
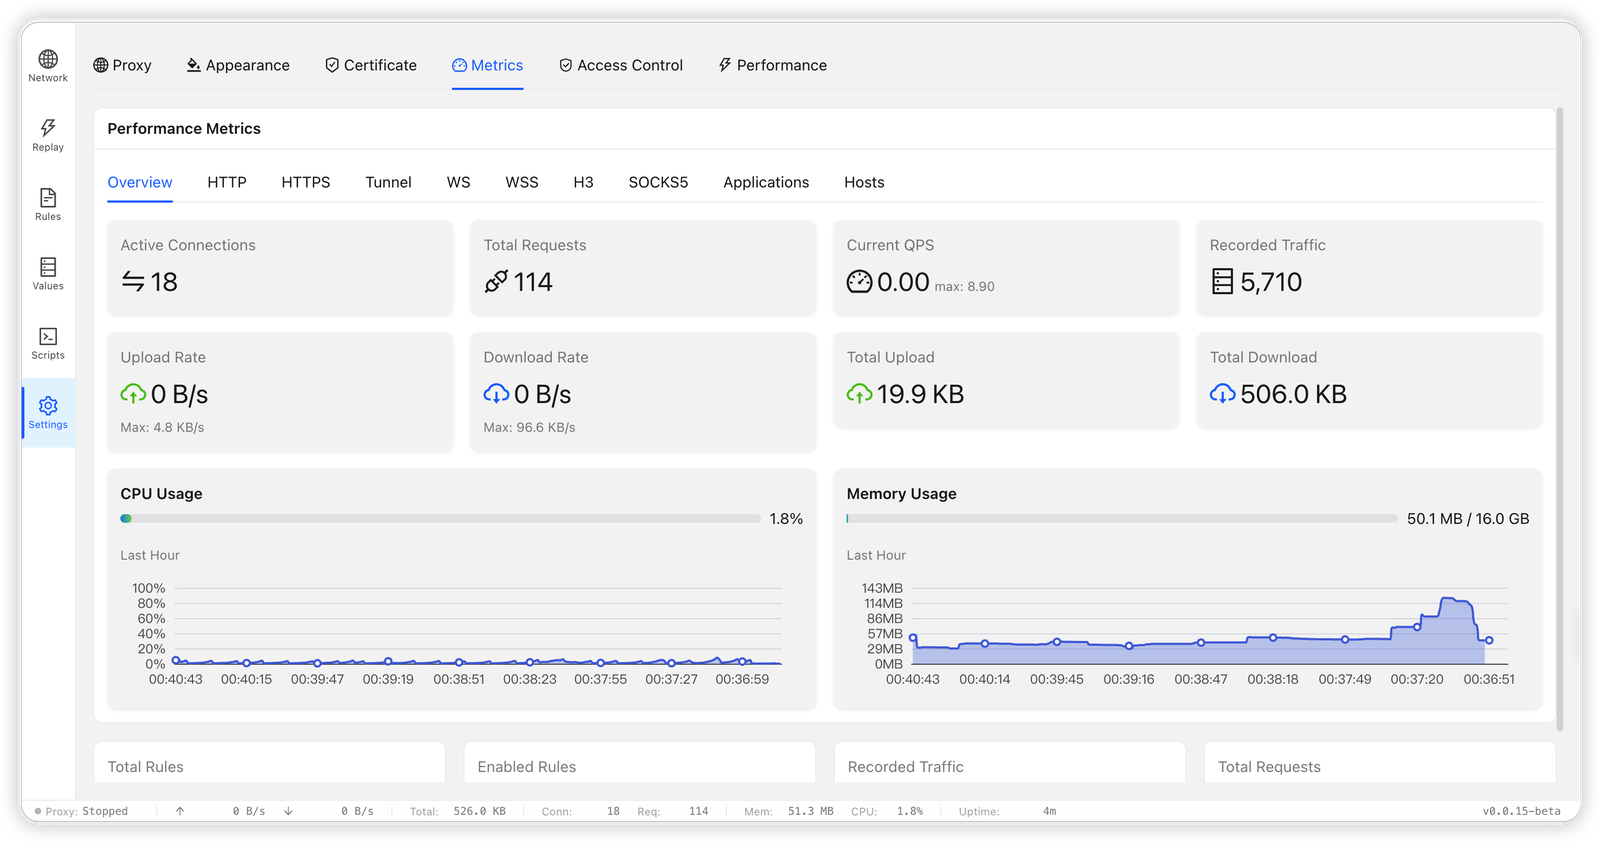
bifrost
 bifrost-proxy/bifrost
High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
api-security-testingnetwork-securitypacket-sniffing-analysis+6
160
bifrost-proxy/bifrostHigh-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
 droe/sslsplit
Transparent man-in-the-middle proxy that terminates SSL/TLS connections, forges certificates on-the-fly, and logs decrypted traffic for network…
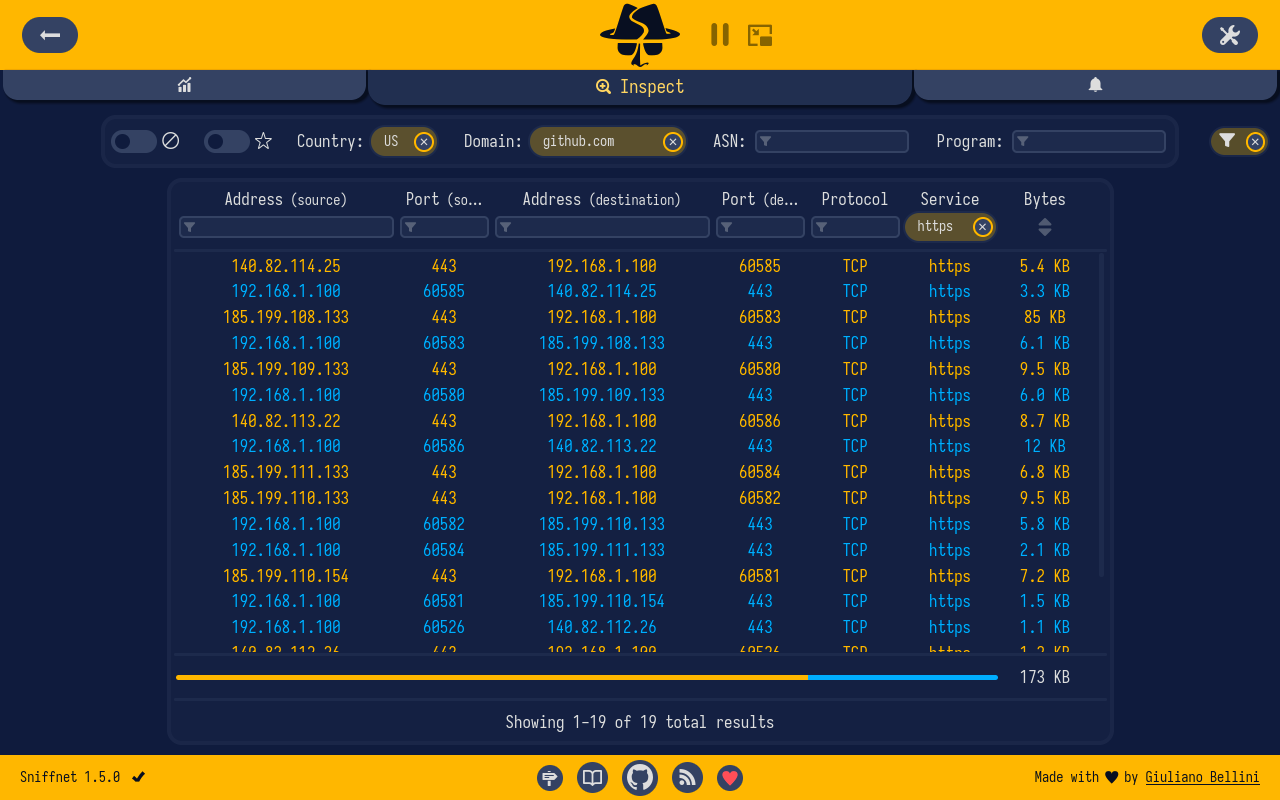 gyulyvgc/sniffnet
Comfortably monitor your network traffic 🕵️♂️
 davidhavoc/ayaflow
A high-performance, eBPF-based network traffic analyzer written in Rust.
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…

 jpr5/ngrep
ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…
 telekom-security/tpotce
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 robertdavidgraham/masscan
TCP port scanner, spews SYN packets asynchronously, scanning entire Internet in under 5 minutes.
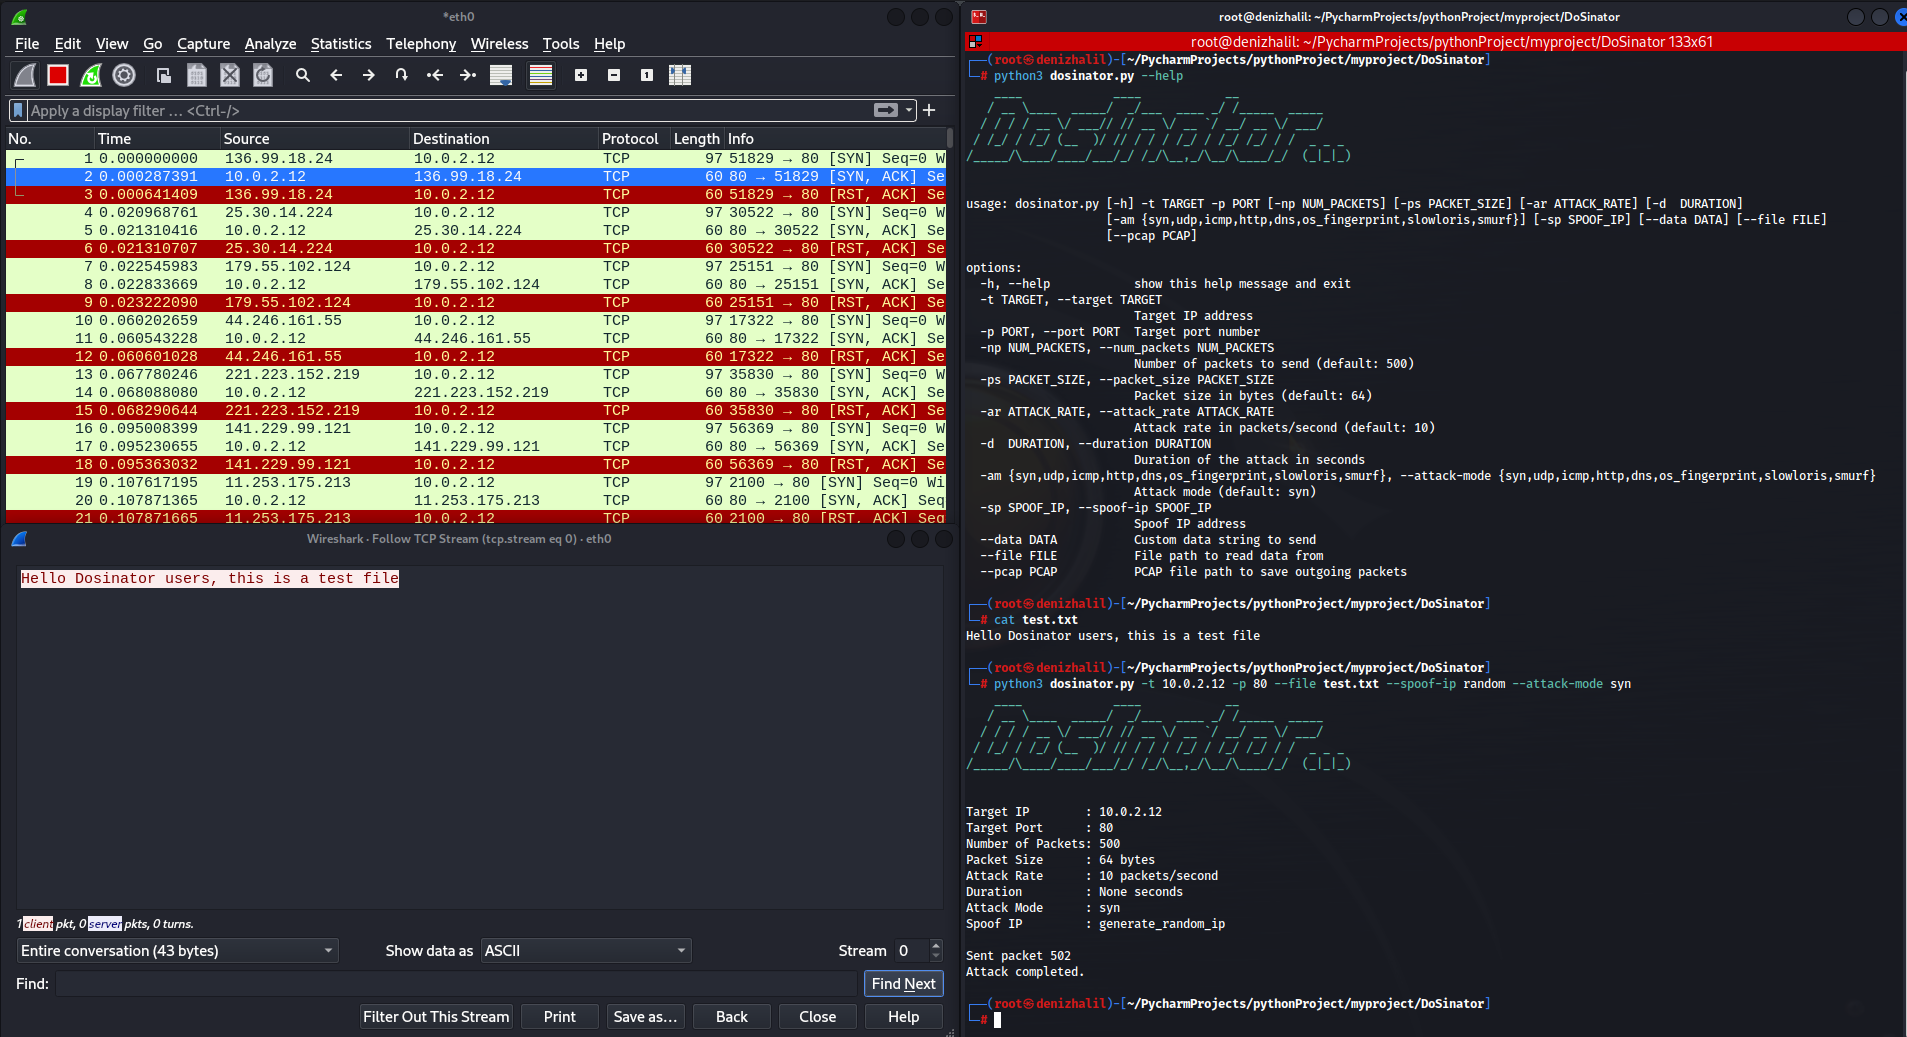 halildeniz/dosinator
DoSinator is a powerful Denial of Service (DoS) testing tool developed in Python.
 aircrack-ng/aircrack-ng
Complete suite for WiFi network security auditing, including packet capture, injection attacks, deauthentication, fake AP creation, and WEP/WPA PSK…
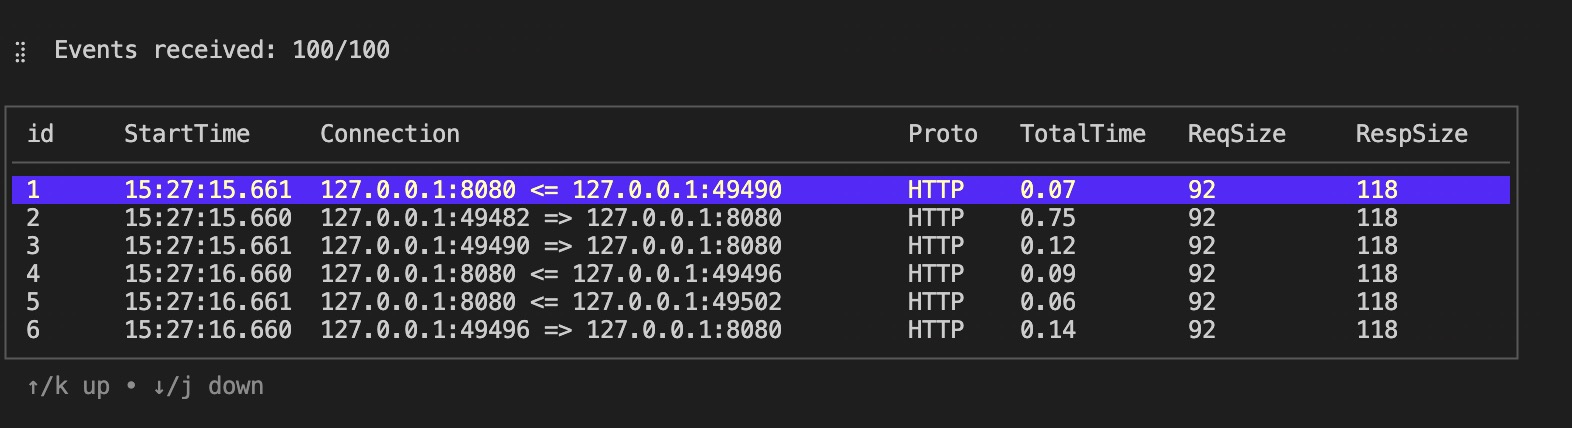 hengyoush/kyanos
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…
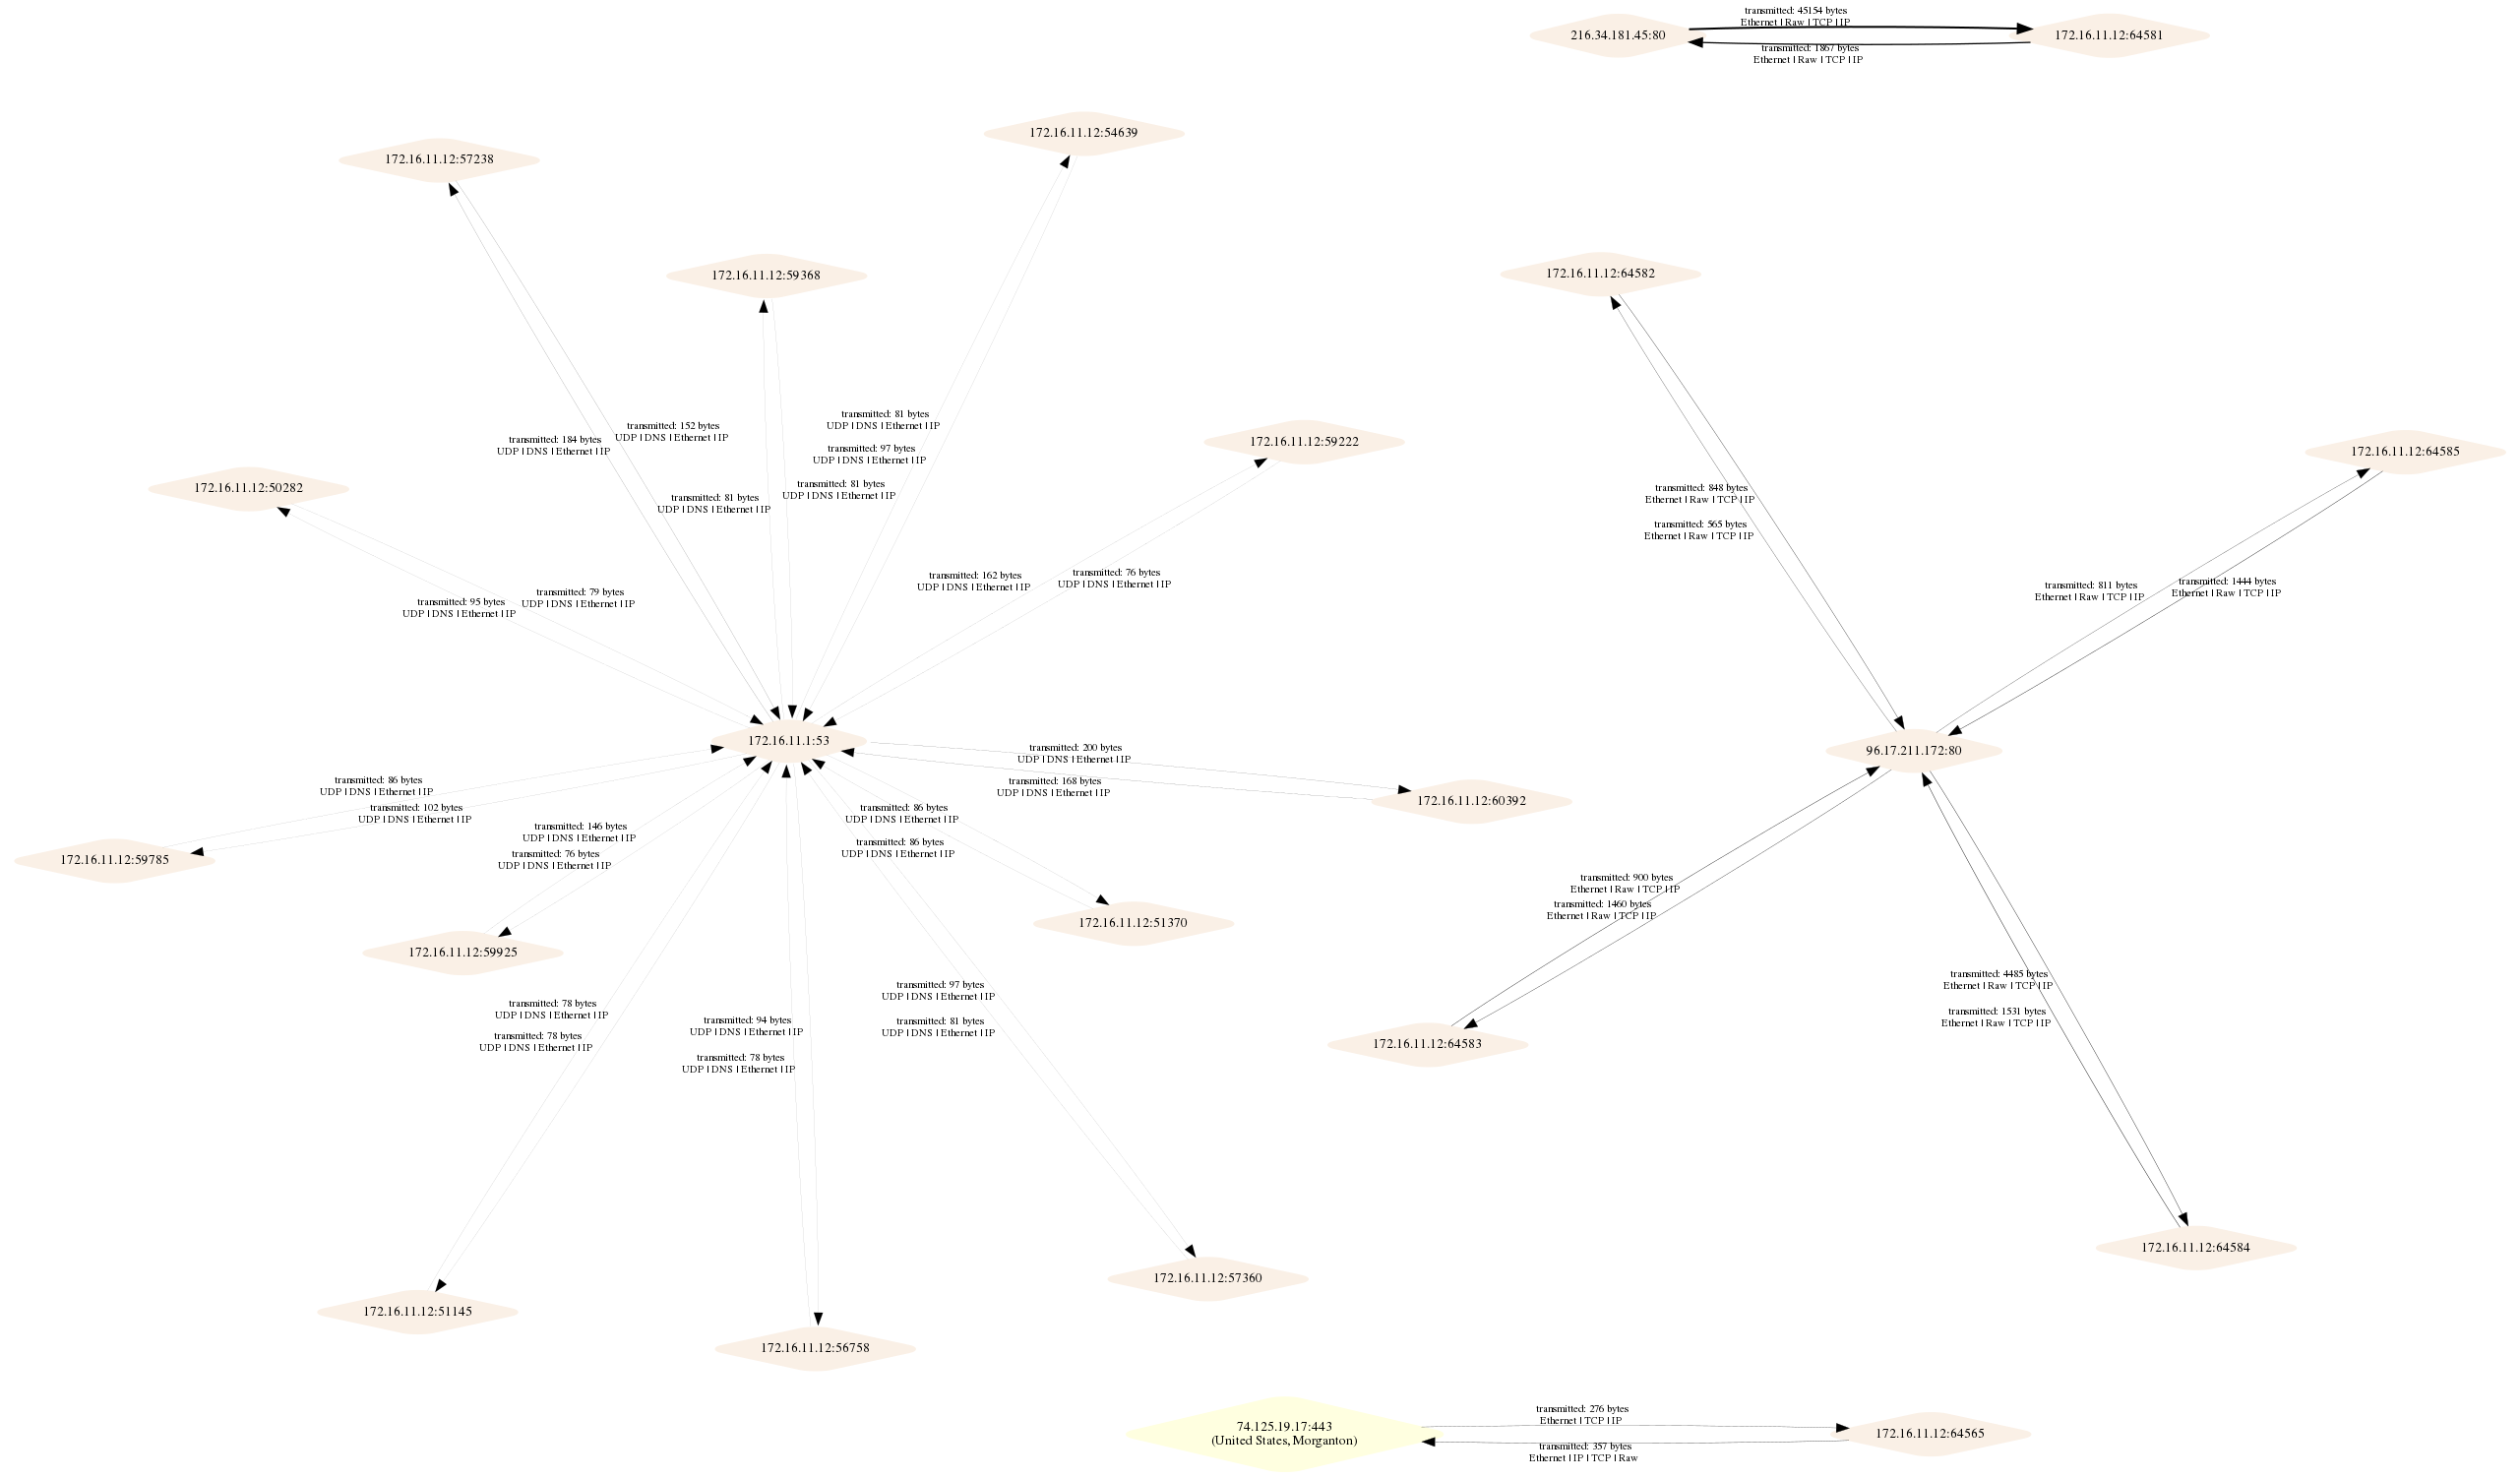 1ultimat3/pcapviz
Visualize network topologies and collect graph statistics based on pcap files
 phaethon/kamene
Network packet and pcap file crafting/sniffing/manipulation/visualization security tool. Originally forked from scapy in 2015 and providing python3…
 shramos/polymorph
Polymorph is a real-time network packet manipulation framework with support for almost all existing protocols
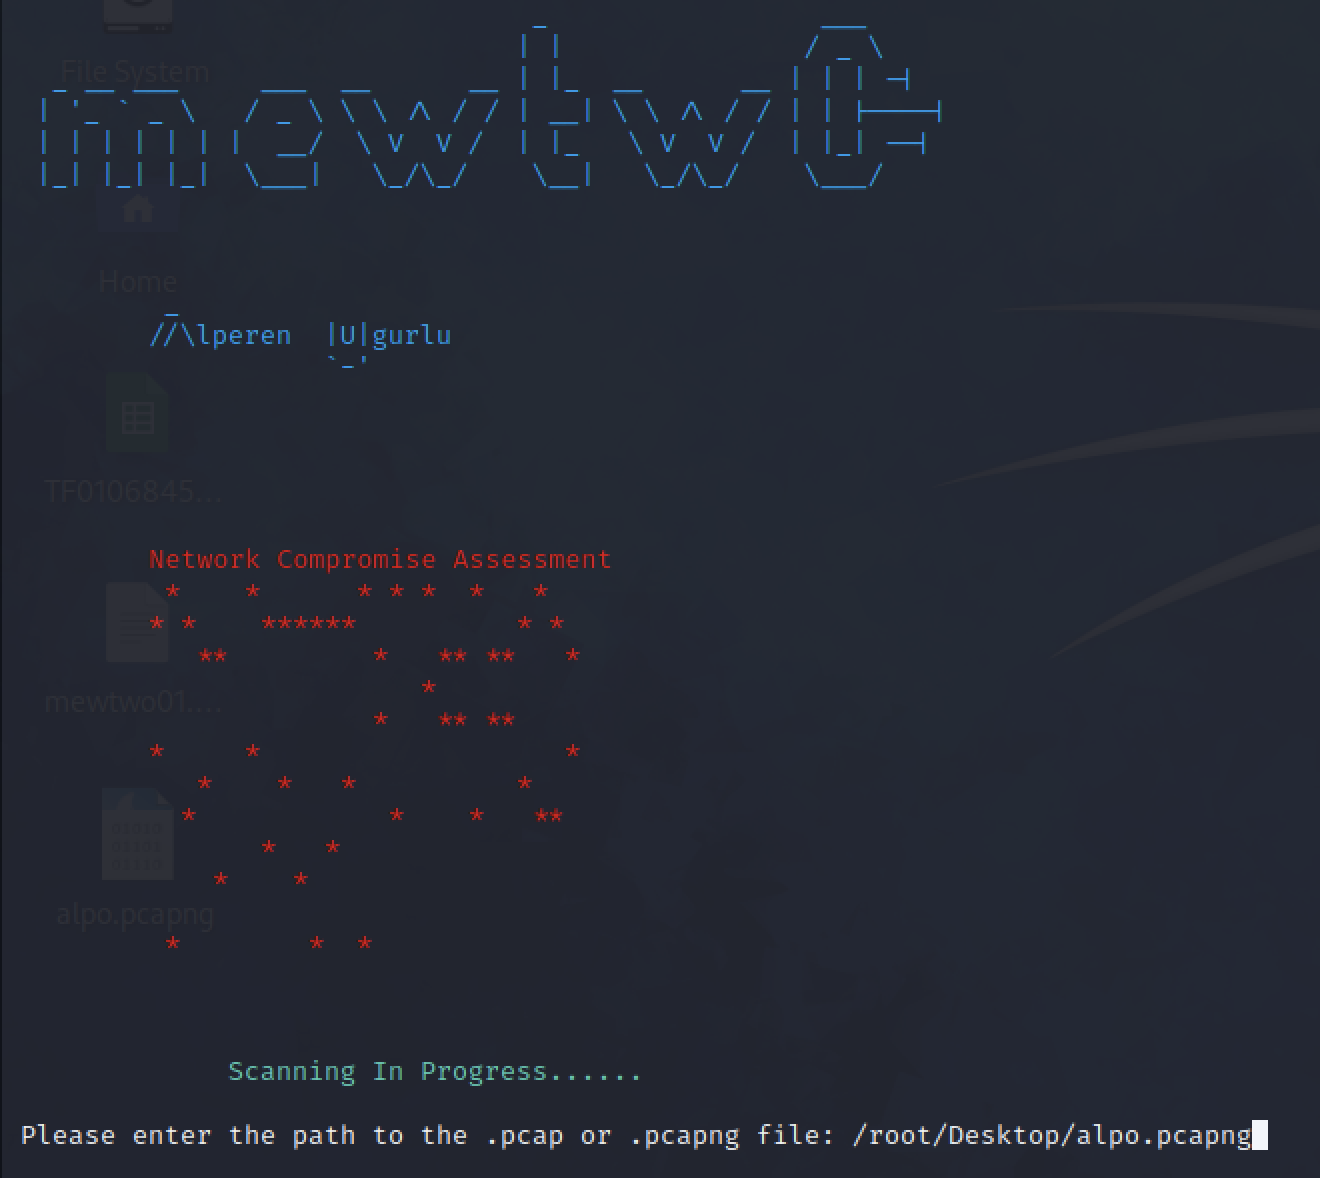 alperenugurlu/network_assessment
With Wireshark or TCPdump, you can determine whether there is harmful activity on your network traffic that you have recorded on the network you…