
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
18 results
wireshark preview

wireshark

GitHubwireshark/wireshark

Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…

bluetooth-securitydata-exfiltrationdigital-forensics+11
9.9k
3 days ago
kubeshark preview

kubeshark

GitHubkubeshark/kubeshark

eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
ai-securitycloud-infrastructure-securitycloud-security+9
12.1k2 days ago
ecapture preview

ecapture

GitHubgojue/ecapture

Capturing SSL/TLS plaintext without a CA certificate using eBPF. Supported on Linux/Android kernels for amd64/arm64.
android-securitydatabase-securitydynamic-analysis-sandboxing+3
15.5k21h 26m ago
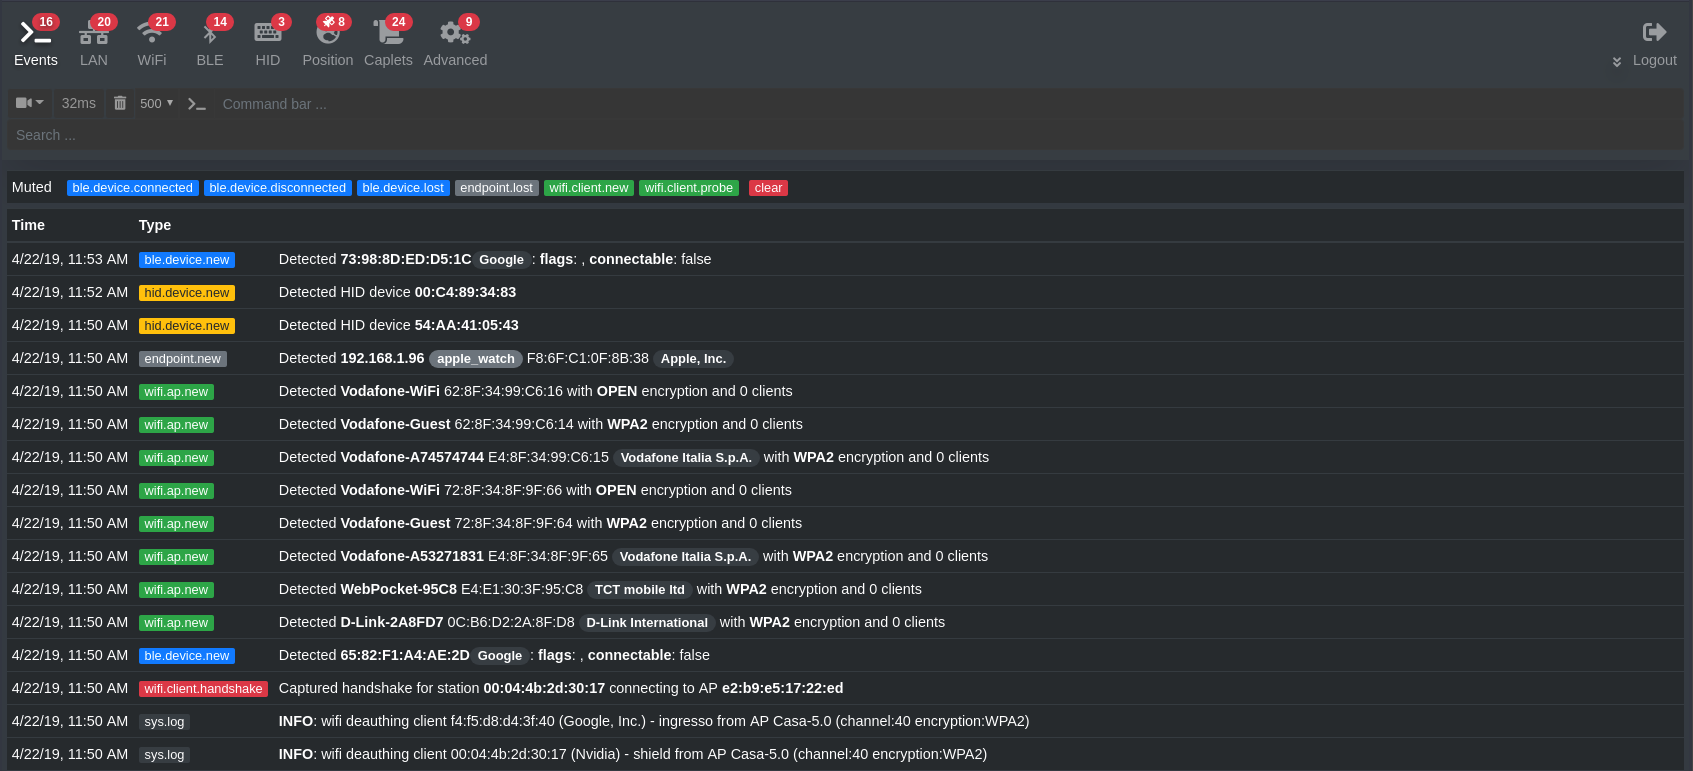
bettercap preview

bettercap

GitHubbettercap/bettercap

The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
bluetooth-securitydata-exfiltrationfingerprint-spoofing+16
20.0k1 month ago
ByeDPIAndroid preview

ByeDPIAndroid

GitHubdovecoteescapee/byedpiandroid

Android VPN-based local proxy that bypasses Deep Packet Inspection (DPI) and censorship by redirecting all traffic through a SOCKS5 tunnel without…

dns-analysisids-ips-evasionnetwork-security+2
5.5k2 years ago
USBArmyKnife preview

USBArmyKnife

GitHubi-am-shodan/usbarmyknife

USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
bluetooth-securitydata-exfiltrationhardware-hacking+8
2.9k22 days ago
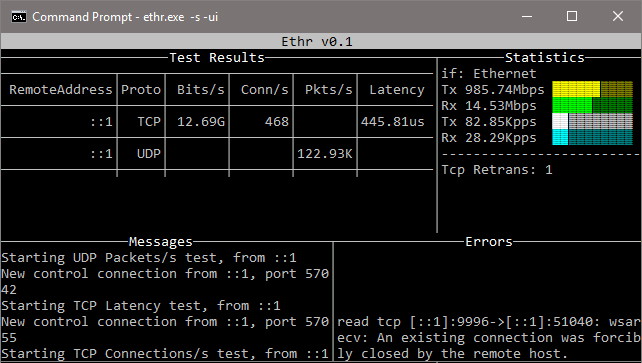
ethr preview

ethr

GitHubmicrosoft/ethr

Cross-platform CLI for network performance testing over TCP, UDP, HTTP, HTTPS, and ICMP: bandwidth, connections/s, packets/s, latency, loss, jitter,…
data-exfiltrationgeneral-purpose-utilitiesinformation-gathering+3
5.9k9 months ago
SpectralCovert preview

SpectralCovert

GitHubprox0959/spectralcovert

Detects network covert channels using Shannon entropy and Sarle's bimodality coefficient to flag encrypted ICMP/TCP payload exfiltration and…
anomaly-detectioncryptographydata-exfiltration+7
1 day ago
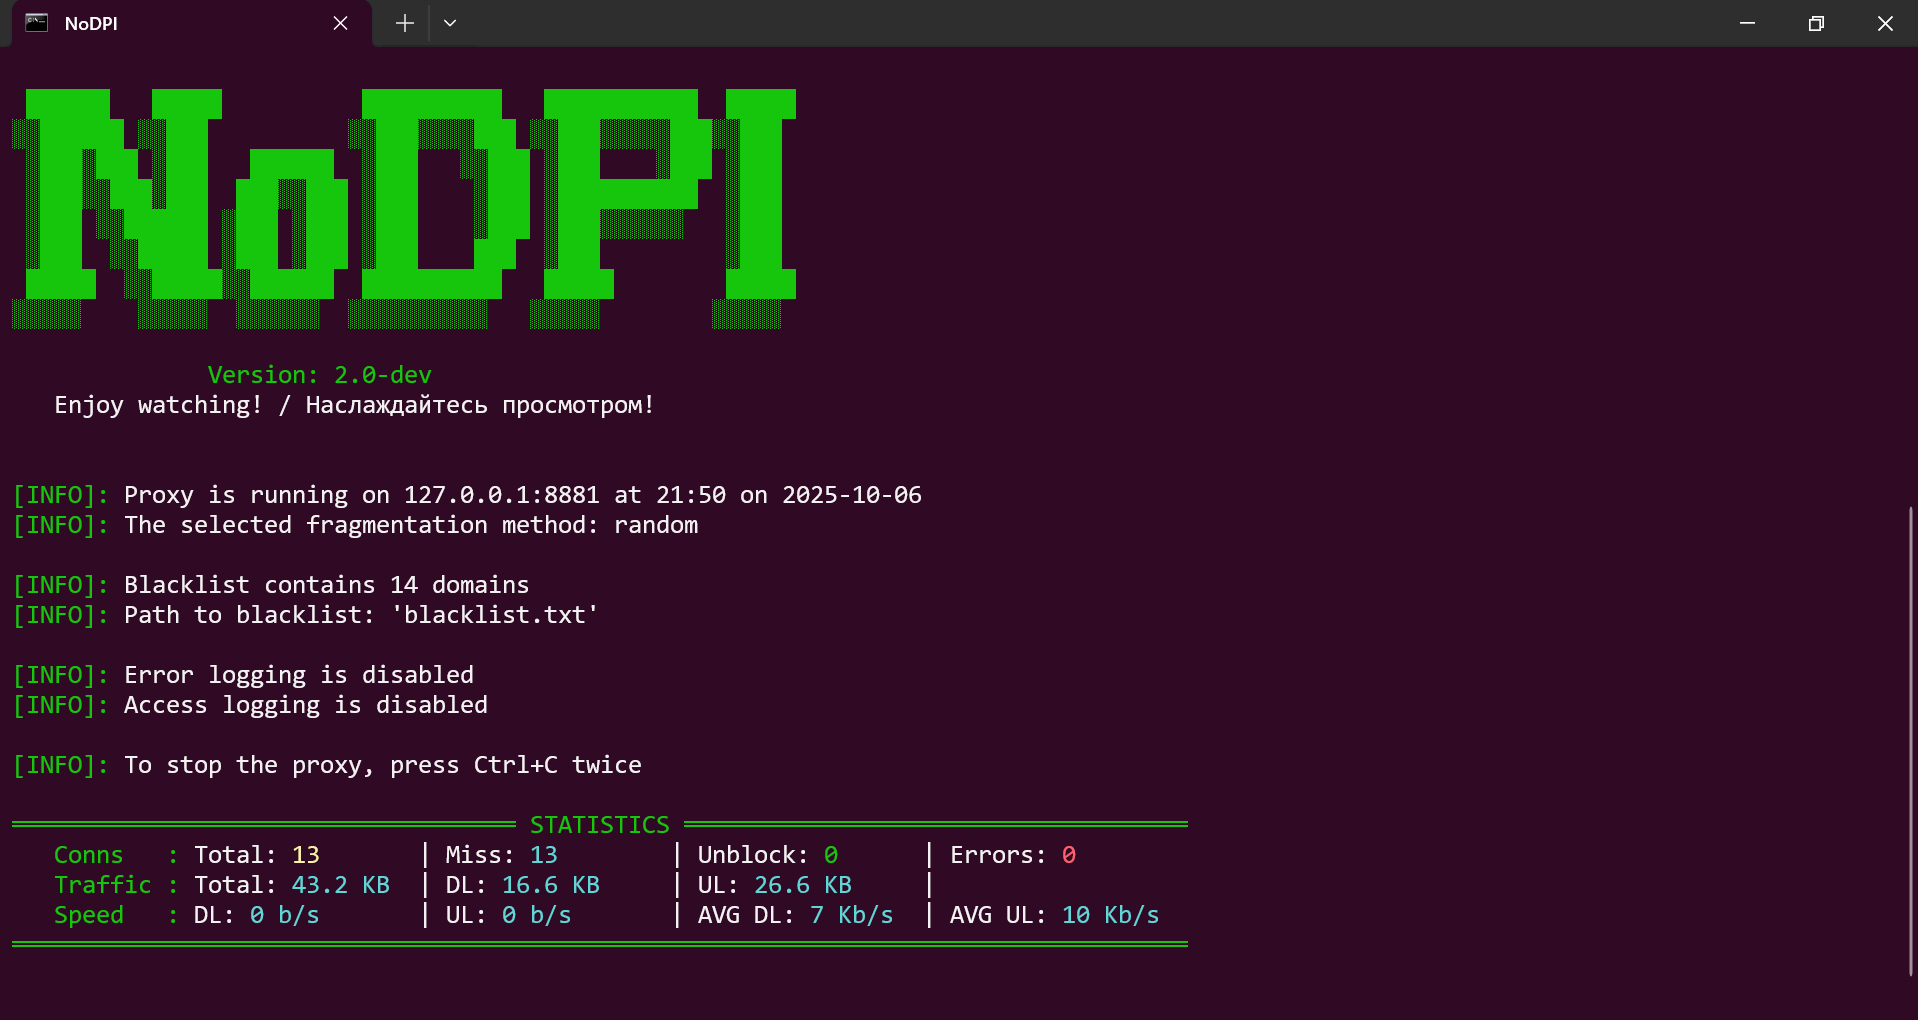
NoDPI preview

NoDPI

GitHubgvcoder09/nodpi

Local proxy that bypasses Deep Packet Inspection by fragmenting TLS ClientHello packets, enabling access to blocked websites without requiring…

ids-ips-evasionnetwork-securitypacket-sniffing-analysis+1
1.7k1 month ago
Solitude preview

Solitude

GitHubnccgroup/solitude

Solitude is a privacy analysis tool that enables anyone to conduct their own privacy investigations. Whether a curious novice or a more advanced…
data-exfiltrationinformation-gatheringmobile-security+4
3765 years ago
phantomprint preview

phantomprint

GitHubharuu77g/phantomprint

Passive hybrid fingerprinting engine — identify hosts without sending a single packet
digital-forensicsinformation-gatheringnetwork-mapping+7
41 month ago
keepass-exfil-forensics preview

keepass-exfil-forensics

GitHubpugazhendii22/keepass-exfil-forensics

Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…
ctfdata-exfiltrationdigital-forensics+6
1 month ago
keysweeper preview

keysweeper

GitHubsamyk/keysweeper

KeySweeper is a stealthy Arduino-based device, camouflaged as a functioning USB wall charger, that wirelessly and passively sniffs, decrypts, logs…
data-exfiltrationembedded-systems-securityhardware-hacking+4
1.1k9 years ago
loki-parse preview

loki-parse

GitHubr3mrum/loki-parse

A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…
data-exfiltrationdigital-forensicsforensics+5
139 years ago
Above preview

Above

GitHubcaster0x00/above

Passive network security sniffer that analyzes 28 protocols (ARP, STP, OSPF, VLAN, SCADA) to detect vulnerabilities in network equipment without…
network-securitypacket-sniffing-analysispenetration-testing+2
8728 months ago
CVE-2025-32433-LAB preview

CVE-2025-32433-LAB

GitHubdamnkrishna/cve-2025-32433-lab

A Flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without…
container-securityeducationexploitation+6
7 days ago
CVE-2025-4679-SecureOAuth-Demo---Enfoque-educativo preview

CVE-2025-4679-SecureOAuth-Demo---Enfoque-educativo

GitHubfevar54/cve-2025-4679-secureoauth-demo---enfoque-educativo

Isolated educational lab simulating CVE-2025-4679 OAuth credential exposure. Learn offensive and defensive security through hands-on exercises,…

api-securityauthenticationctf+6
9 months ago
Woeful preview

Woeful

GitHubmercuryworkshop/woeful

Woeful is a tool that lets web apps to safely and securely connect to the outside internet without a complex backend.

dns-analysisnetwork-securitypacket-sniffing-analysis+2
141 year ago