
fileintel
 keithjjones/fileintel
A modular Python application to pull intelligence about malicious files
hash-analysisinformation-gatheringmalware-analysis+2
1235 years ago
keithjjones/fileintelA modular Python application to pull intelligence about malicious files

 theresafewconors/sooty
The SOC Analysts all-in-one CLI tool to automate and speed up workflow.
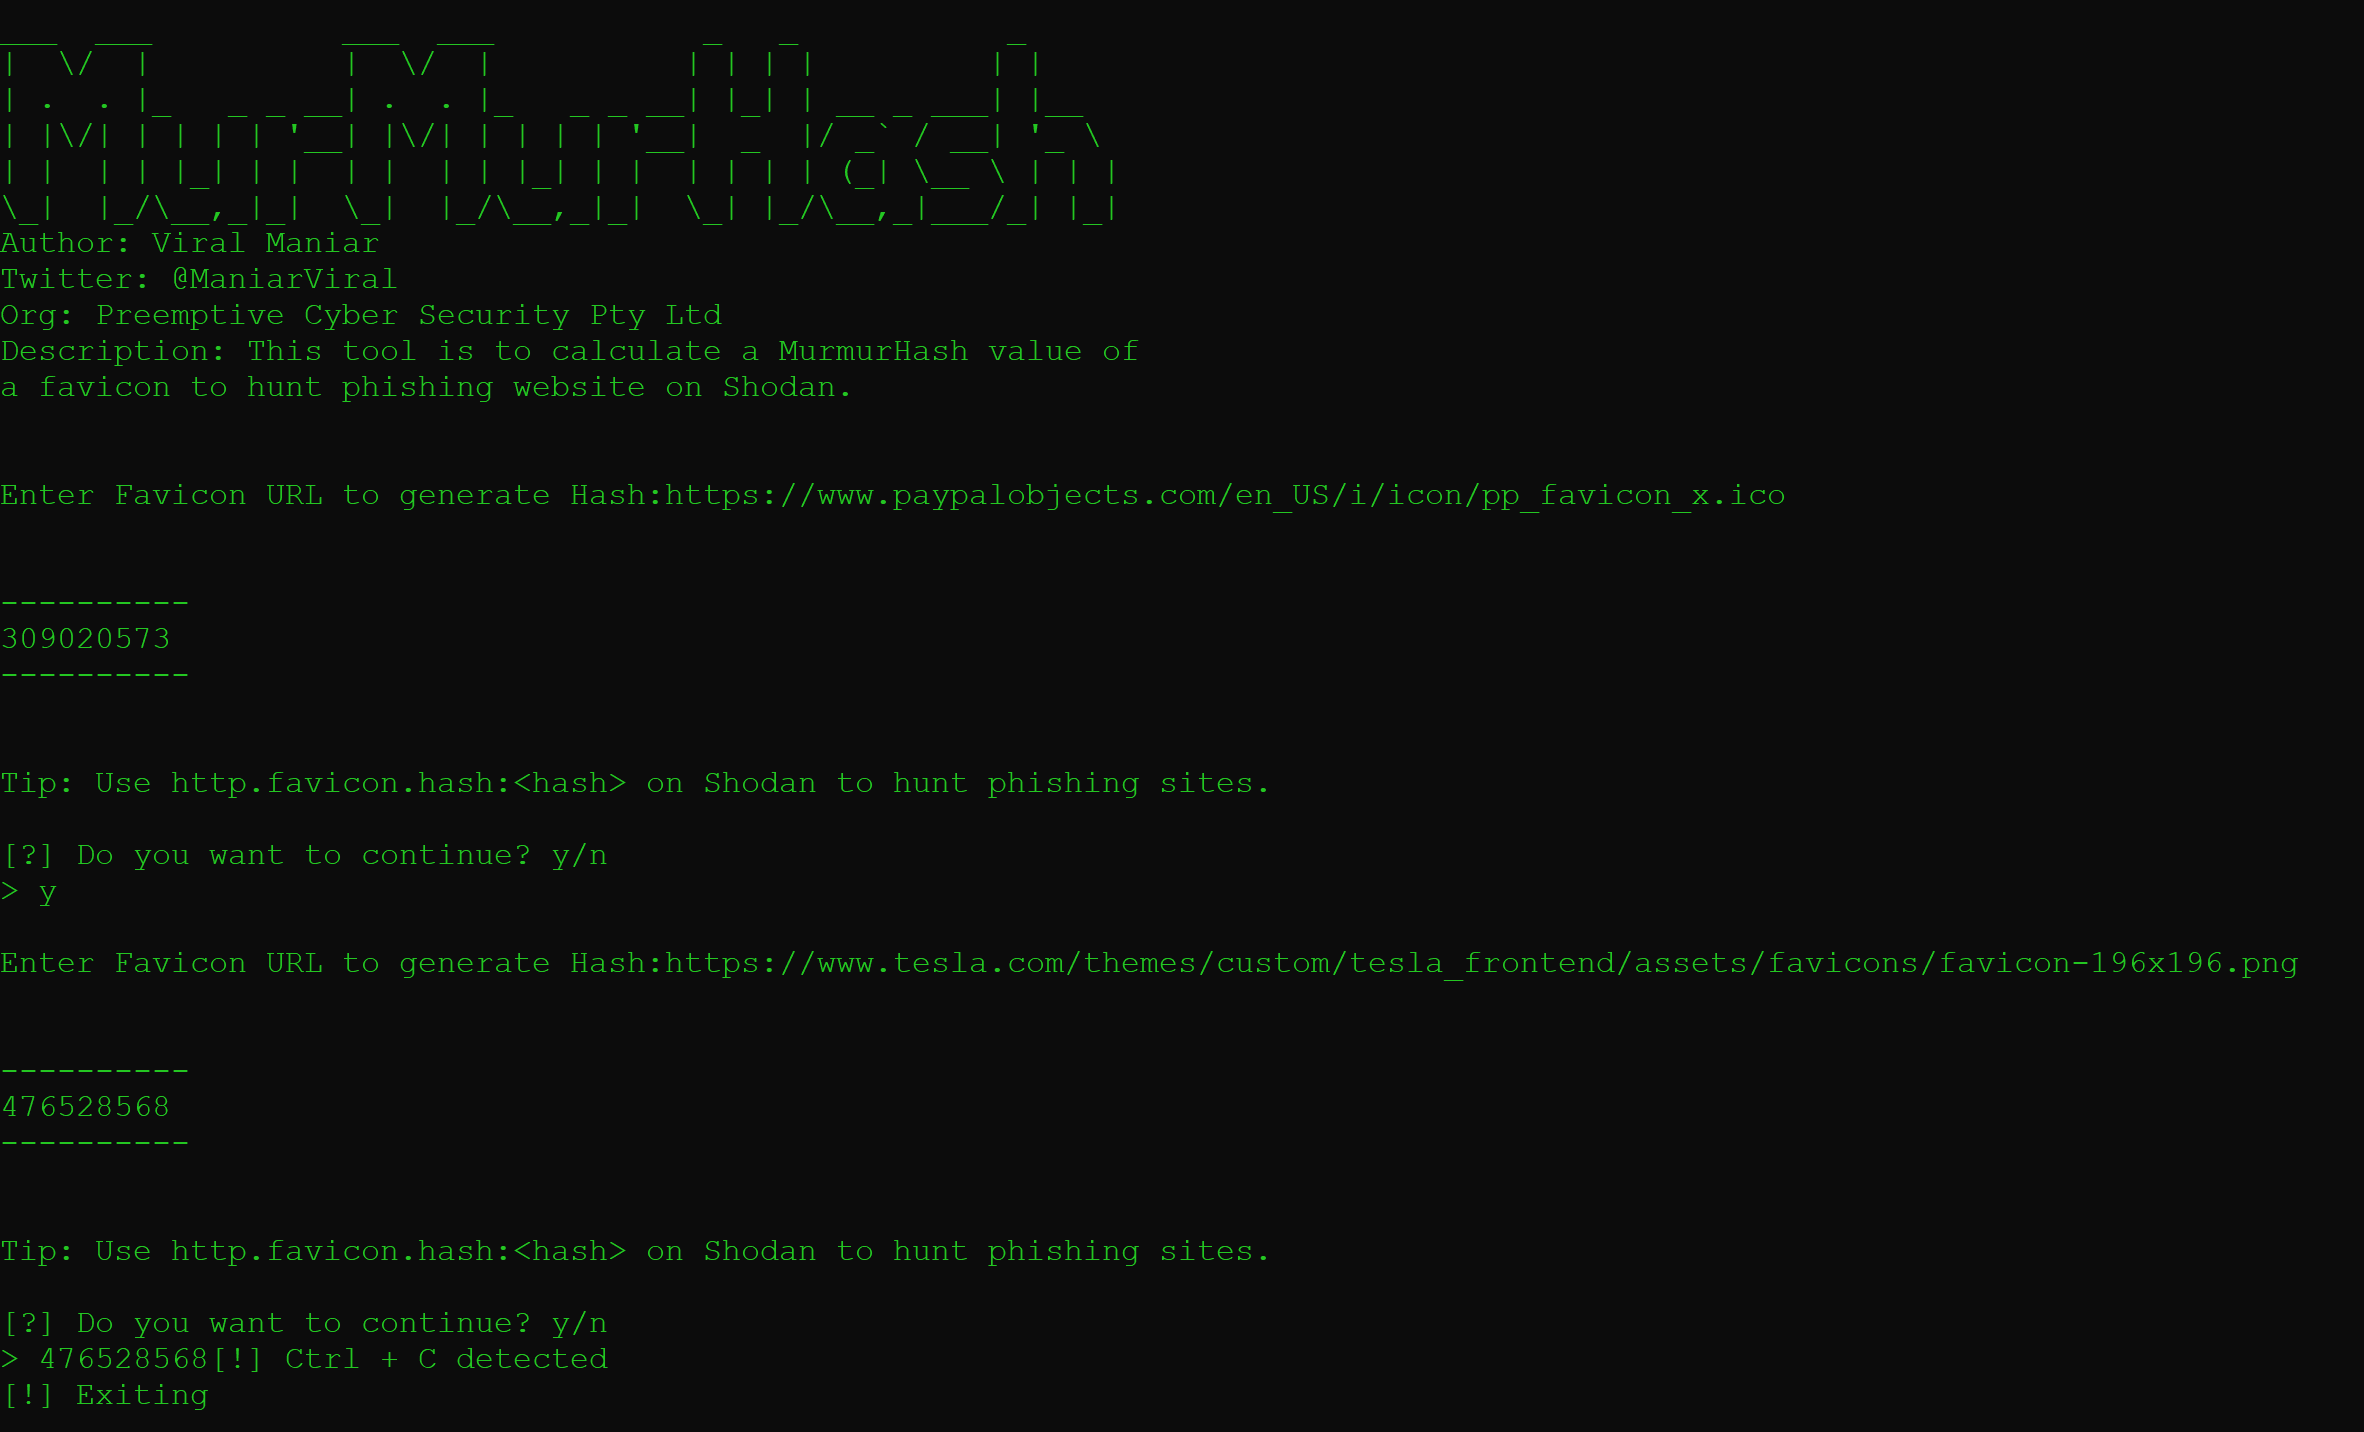 viralmaniar/murmurhash
This little tool is to calculate a MurmurHash value of a favicon to hunt phishing websites on the Shodan platform.
 1an0rmus/tekdefense-automater
Automater - IP URL and MD5 OSINT Analysis
 ktzgraph/sarenka
OSINT tool - gets data from services like shodan, censys etc. in one app
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 viralmaniar/ddwpasterecon
DDWPasteRecon tool will help you identify code leak, sensitive files, plaintext passwords, password hashes. It also allow member of SOC & Blue Team…
 ranguli/ioccheck
A tool for simplifying the process of researching IOCs.
 star-sg/random-scripts
Collection of DFIR and OSINT Python scripts for parsing malicious LNK samples, extracting OLE objects from MHTML, and hashing favicons to hunt…
 jayy001/search-that-hash
🔎Searches Hash APIs to crack your hash quickly🔎 If hash is not found, automatically pipes into HashCat⚡
 inquest/python-inquestlabs
A Pythonic interface and command line tool for interacting with the InQuest Labs API.
 00gxd14g/misp-extractor
Extracts selected MISP attributes, including IP addresses, URLs, and hashes, into reusable output files.

 jankoboy88/higernes
a passive OSINT toolkit in python - usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 vqkro/higernes
a passive OSINT toolkit in python usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 artemcyberlab/project-ntlm-hash-capture-and-phishing-email-exploitation-for-cve-2024-21413
Demonstrates capturing NTLM hashes via Responder and executing phishing emails exploiting CVE-2024-21413 to compromise systems.
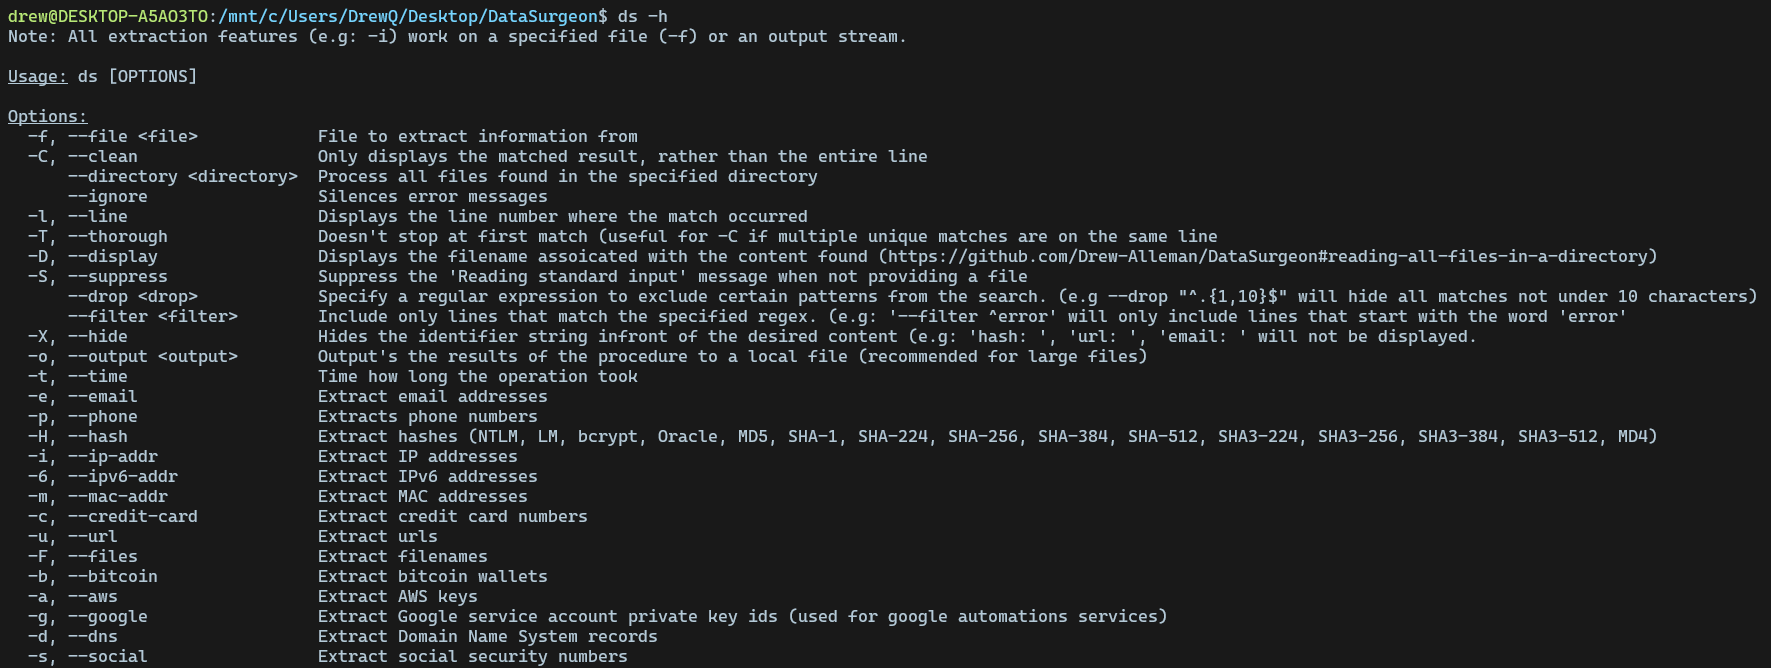 drew-alleman/datasurgeon
Quickly Extracts IP's, Email Addresses, Hashes, Files, Credit Cards, Social Security Numbers and a lot More From Text