
BinGoo
 hood3drob1n/bingoo
BinGoo! A Linux bash based Bing and Google Dorking Tool
dns-subdomain-enumerationinformation-gatheringosint+5
240
hood3drob1n/bingooBinGoo! A Linux bash based Bing and Google Dorking Tool
 ustayready/python-pentesting
Just a repo of random Python scripts to get pentesters started with the Python language on engagements.
 silverpoision/rock-on
Rock-On is a all in one Recon tool that will just get a single entry of the Domain name and do all of the work alone.
 owasp/d4n155
OWASP D4N155 - Intelligent and dynamic wordlist using OSINT
 sowdust/tafferugli
Web-based framework for filtering, collecting, and analyzing tweets to detect coordinated behavior, automated posting, and propaganda operations with…
 zyn3rgy/clickoncehunter
Golang search engine scraper intended for identification of published ClickOnce deployments
 msadministrator/czds
A Python package to download Zone Files from the Centralized Zone Data Service hosted by ICAAN.
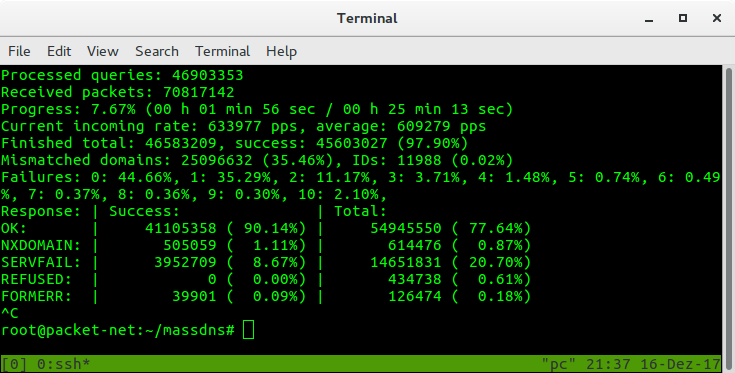 blechschmidt/massdns
A high-performance DNS stub resolver for bulk lookups and reconnaissance (subdomain enumeration)
 therook/subbrute
A DNS meta-query spider that enumerates DNS records, and subdomains.
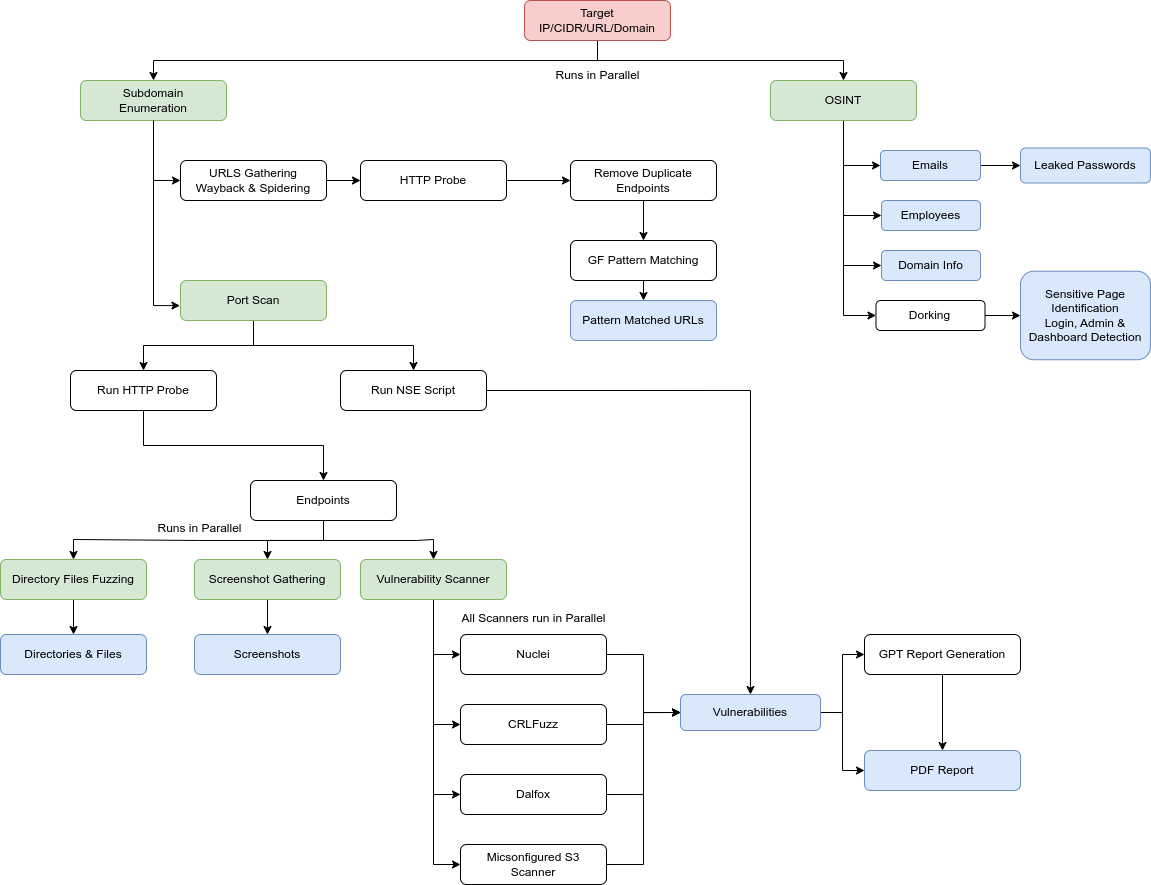 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 dhotrey/awesome-cybersec
A collection of awesome platforms, blogs, documents, books, resources and cool stuff about security
 busindre/dumpzilla
Extract all forensic interesting information of Firefox, Iceweasel and Seamonkey browsers
 tnkr/poc_monitor
A short scraper looking for a POC of CVE-2024-49112
 crocodyli/threatactors-ttps
Repository created to share information about tactics, techniques and procedures used by threat actors. Initially with ransomware groups and evolving…
 hackplayers/iptodomain
This tool extract domains from IP address based in the information saved in virustotal.
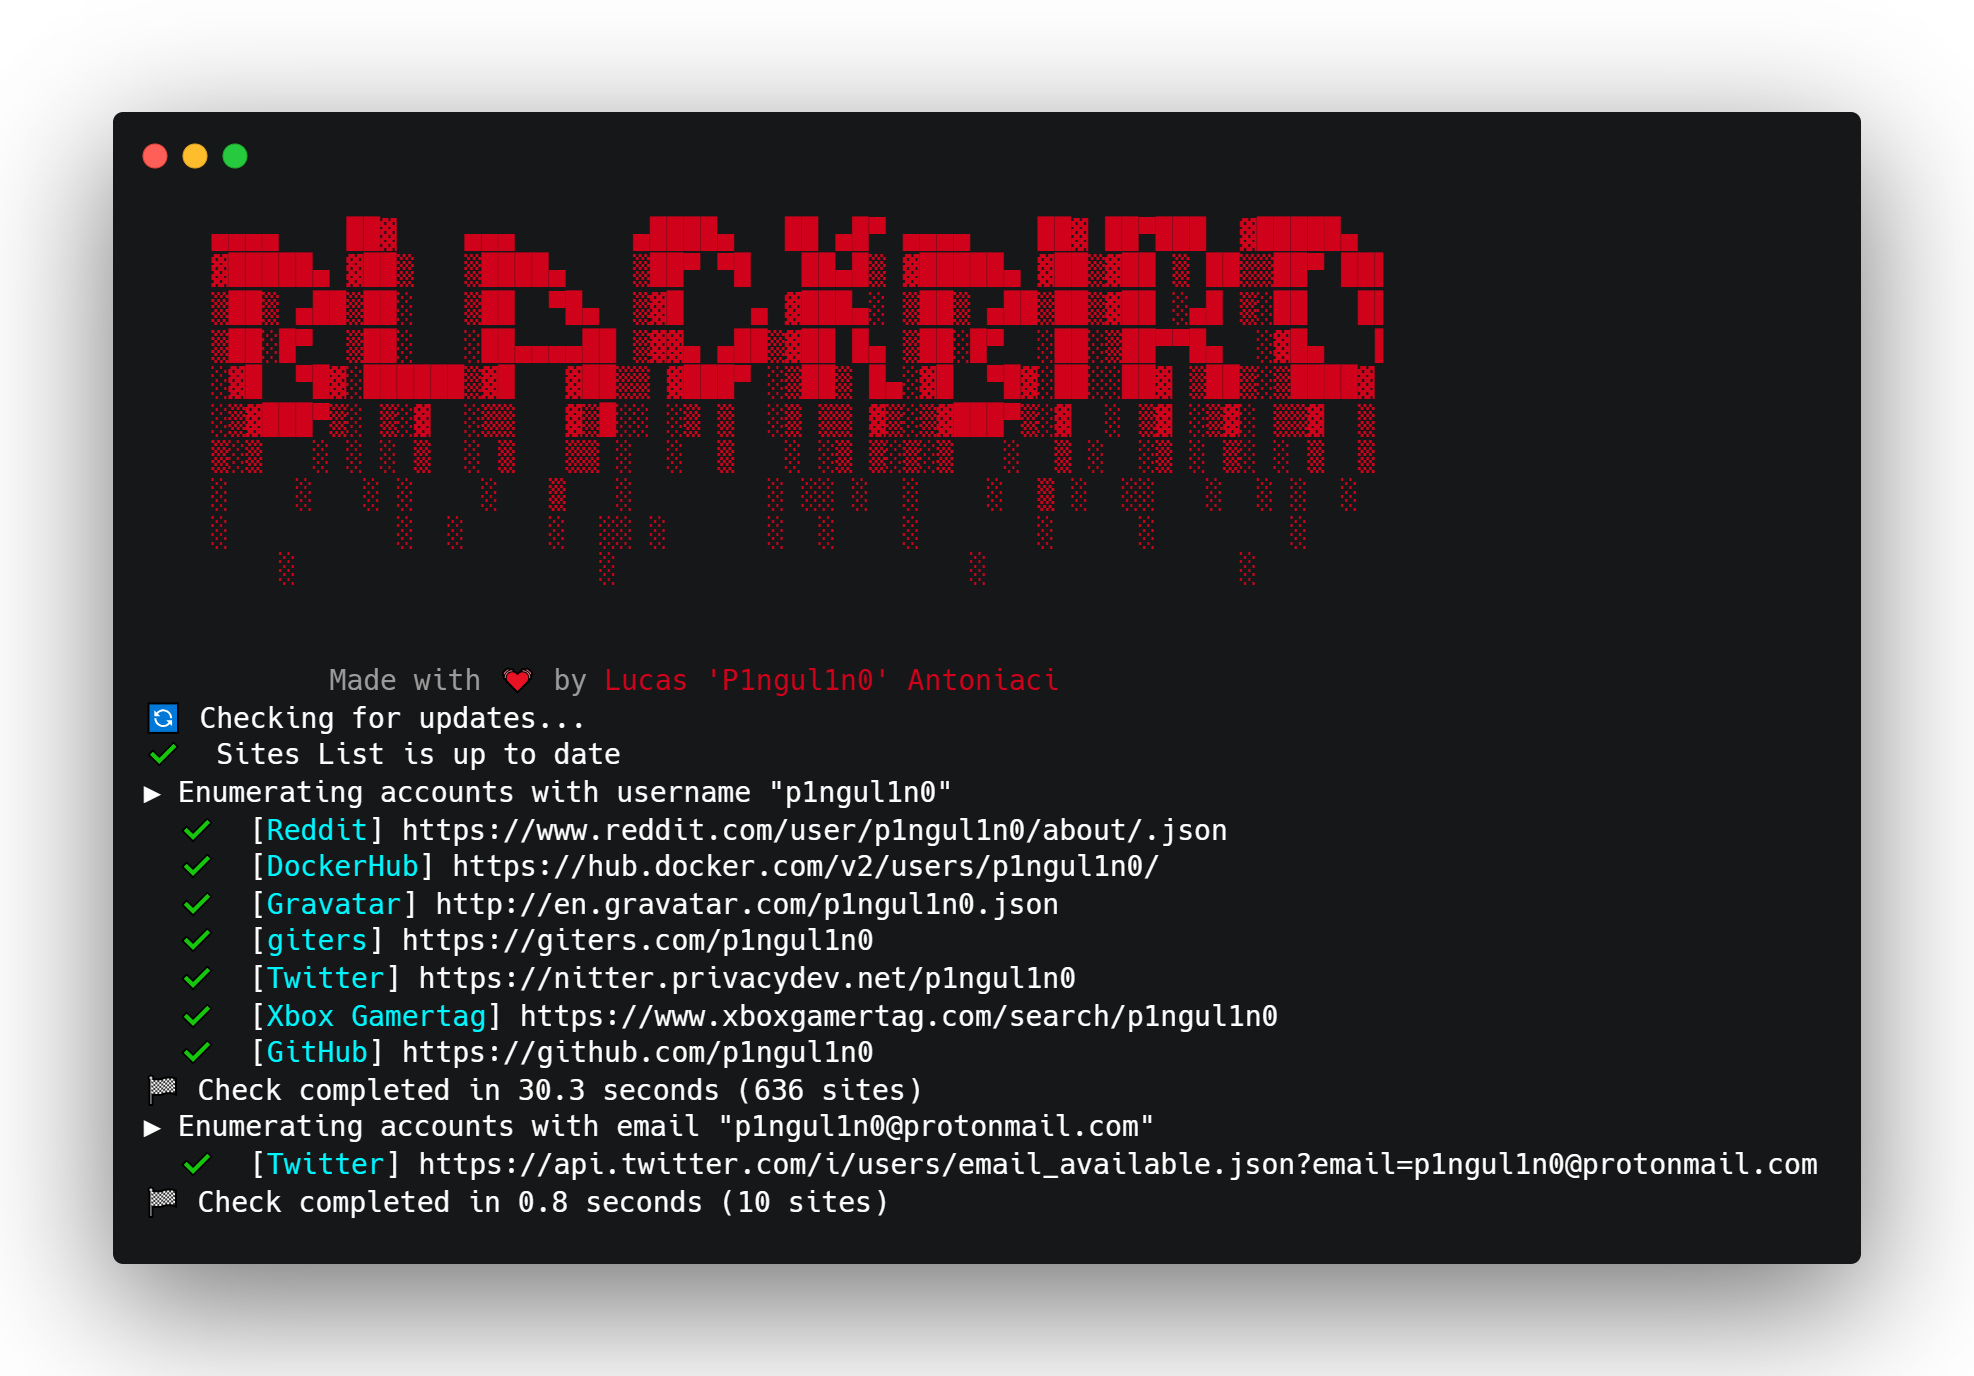
 gcabc123/blackbird
An OSINT tool to search for accounts by username in social networks.
 vanyasem/vk-scraper
Command-line tool to scrape and download media (photos, videos, stories) from VKontakte users and communities using the VK API. Supports multiple…
 tjnull/tj-osint-notebook
This OSINT Notebook provides an overview of the tools, techniques, and resources that I use for a variety of situations when it comes to performing…