SOC274---Palo-Alto-Networks-PAN-OS-Command-Injection-Vulnerability-Exploitation-CVE-2024-3400-

Step-by-step SOC analyst walkthrough for investigating and remediating CVE-2024-3400 (PAN-OS command injection). Covers detection, log analysis,…

Step-by-step SOC analyst walkthrough for investigating and remediating CVE-2024-3400 (PAN-OS command injection). Covers detection, log analysis,…

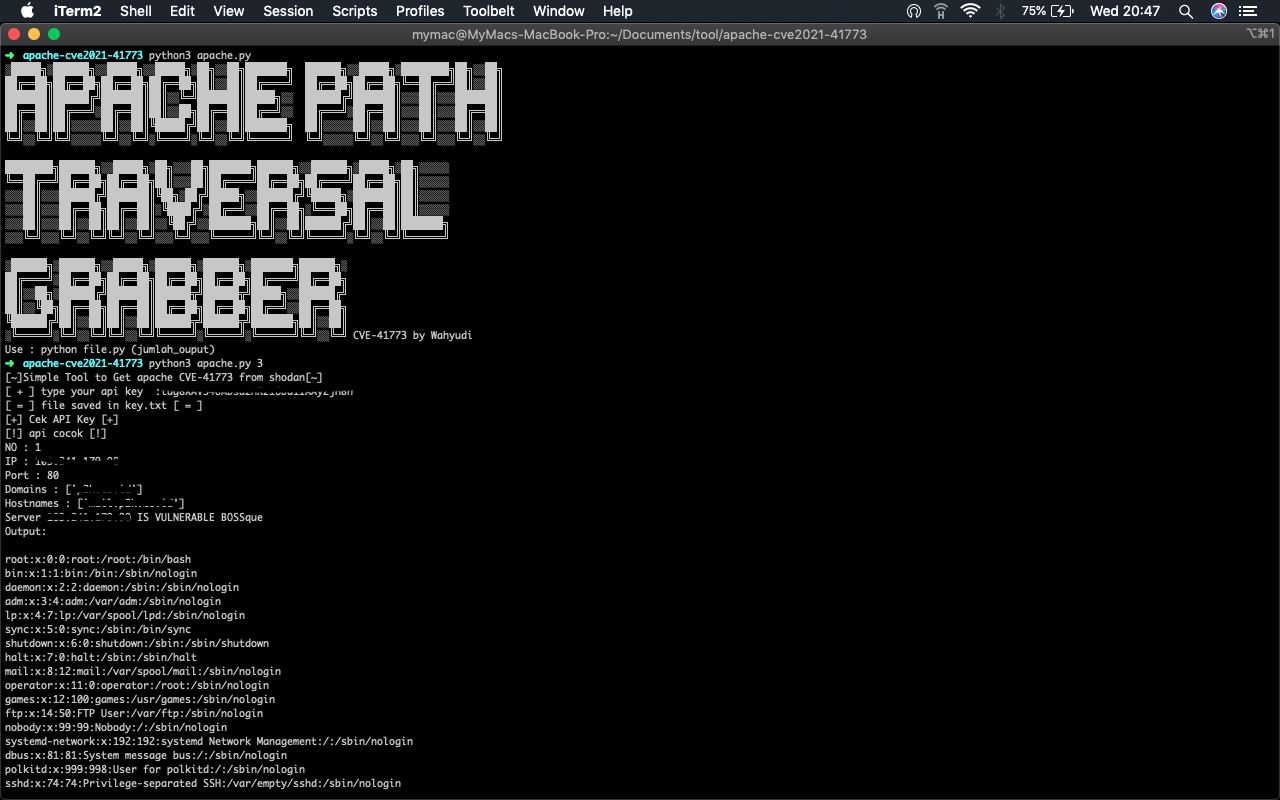
Python script that uses Shodan to discover Apache HTTP Server 2.4.49 instances vulnerable to CVE-2021-41773 path traversal and file disclosure.

Panthera(P.)uncia - Official CLI utility for Subdomain Center & Exploit Observer.

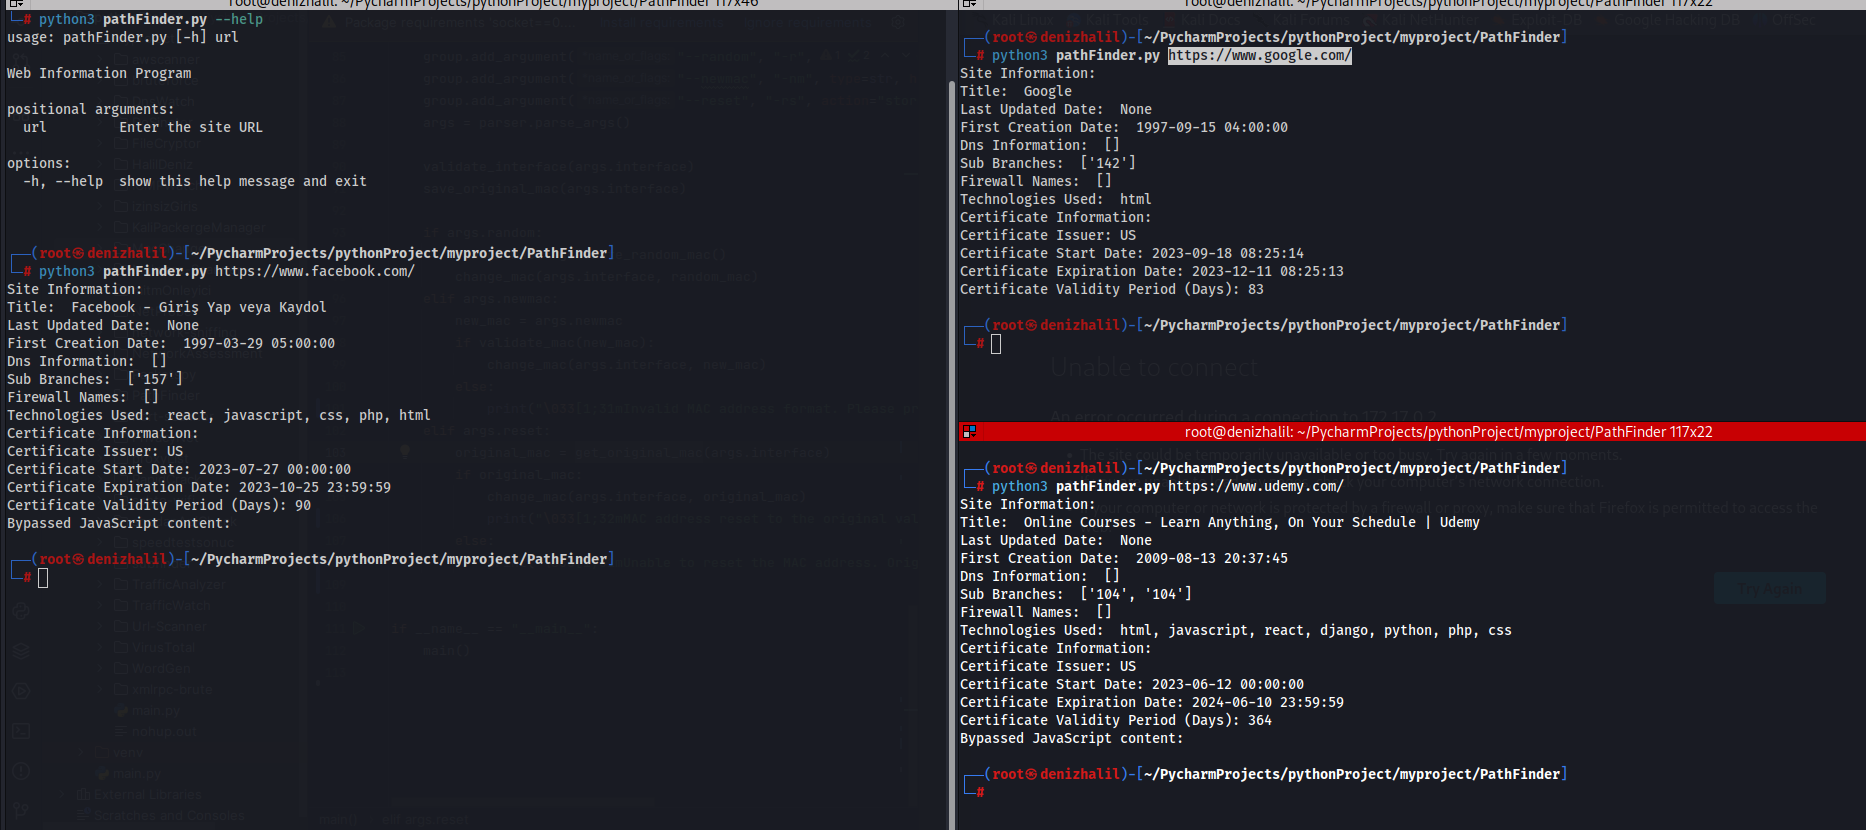
Python-based web reconnaissance tool that extracts site metadata, DNS records, subdomains, firewall names, technologies, and certificate details for…

Exploit for CVE-2018-20555: automated discovery and takeover of Twitter accounts via leaked API keys in vulnerable Social Network Tabs WordPress…

WhatsApp Intelligence & Resource Exhaustion Tool. Features real-time device tracking, silent RTT probing, and protocol stress testing for security…

A curated list of awesome search engines useful during Penetration testing, Vulnerability assessments, Red/Blue Team operations, Bug Bounty and more

📡 PoC auto collect from GitHub. ⚠️ Be careful Malware.

Offensive security platform that automates attack surface discovery and vulnerability management

PAVELOW Exploit Toolbox is a BASH script that corresponds with your KALI distro to better help your vulnerability hunting and exploiting proccess…

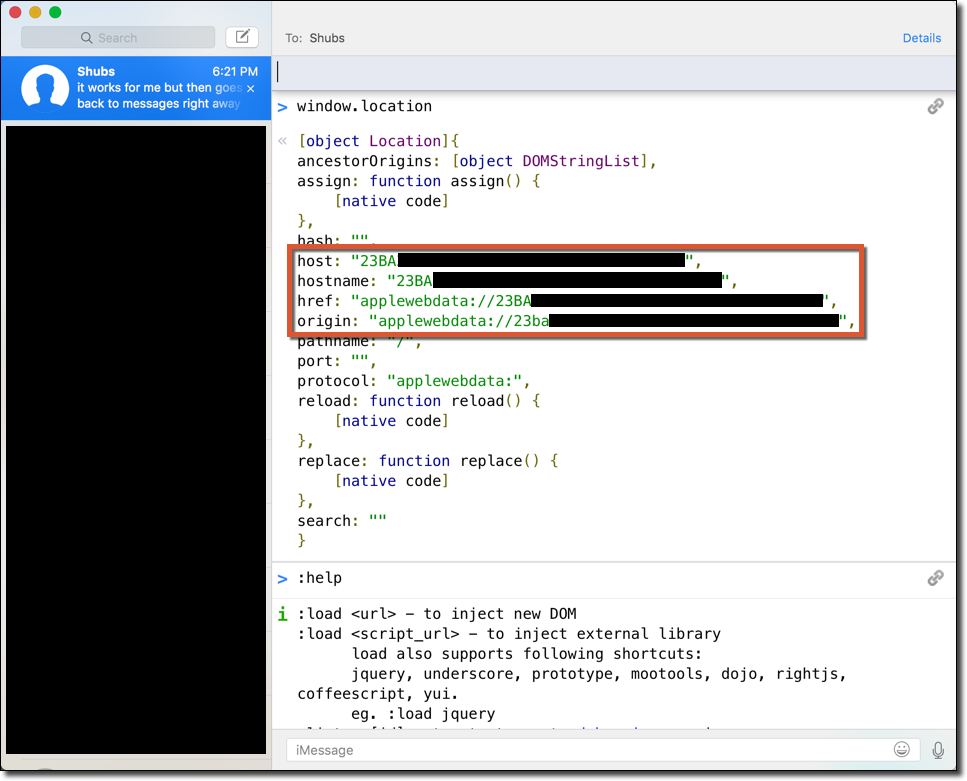
Extraction of iMessage Data via XSS

User Enumeration vulnerability in Kaiten (workflow management system)

This repository documents the process of identifying, analyzing, and gathering Open Source Intelligence (OSINT) on a specific security vulnerability…

This Proof of Concept (PoC) demonstrates the exploitation of the CVE-2024-4367 vulnerability, which involves Cross-Site Scripting (XSS) attacks.

Demonstrates an unauthenticated enumeration vulnerability in a public certificate lookup endpoint, exposing personal data such as CPF and RG.…

CVE-2022-26134, an OGNL injection vulnerability exists that would allow an unauthenticated attacker to execute arbitrary code on a Confluence Server…

Search public CVE proof-of-concept exploits from GitHub, Nuclei, ExploitDB, Metasploit and Vulhub, with CVSS, EPSS and CISA KEV context.