


 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 yukselberkay/asnap
Automates reconnaissance by mapping IPv4/IPv6 addresses to organizations using GeoLite2 databases, with integrated nmap port scanning and batch…
 morpheuslord/nmap-api
RESTful API wrapping Nmap for automated network scanning, port detection, service enumeration, and vulnerability analysis with optional AI-powered…
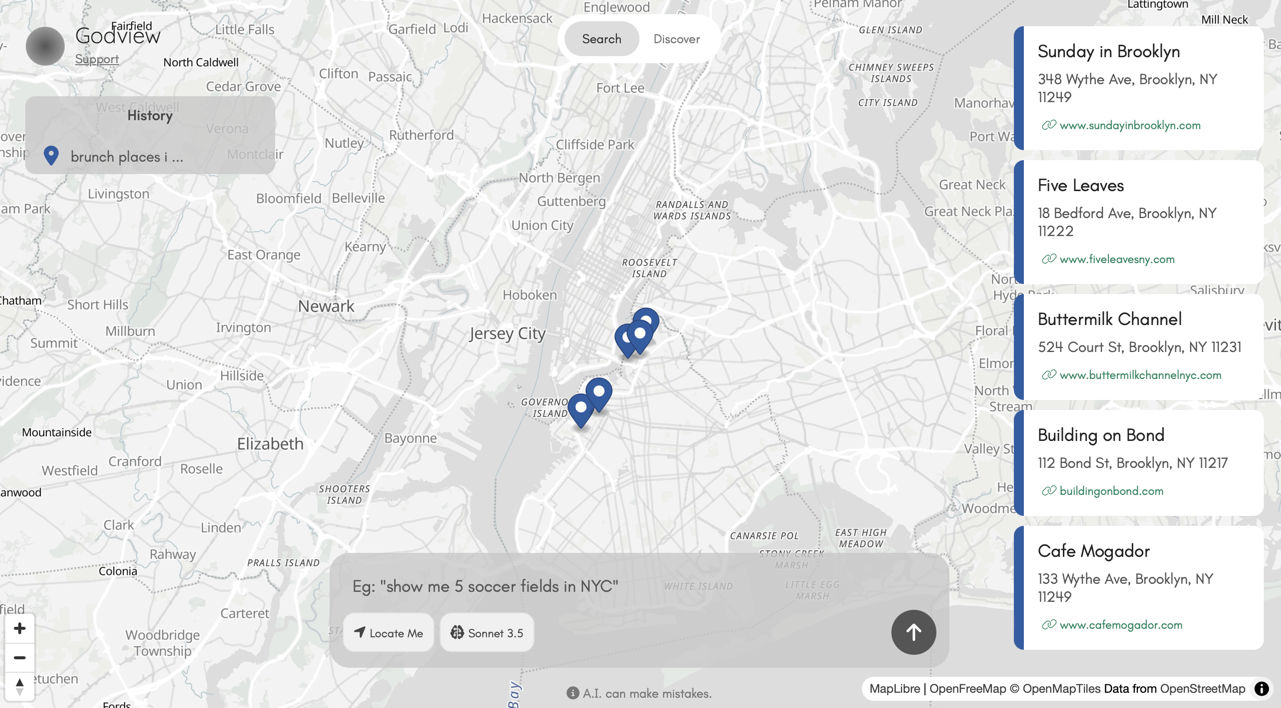 space0blaster/smartmap
LLM based map for research, exploration and discovery.
 nu11secur1ty/nmap-cheat-sheet
Curated cheat sheet for Nmap, covering target selection, port scanning, service/OS detection, NSE scripts, and output formats for network…
 ivre/ivre
Network recon framework. Build your own, self-hosted and fully-controlled alternatives to Shodan / ZoomEye / Censys and GreyNoise, run your Passive…
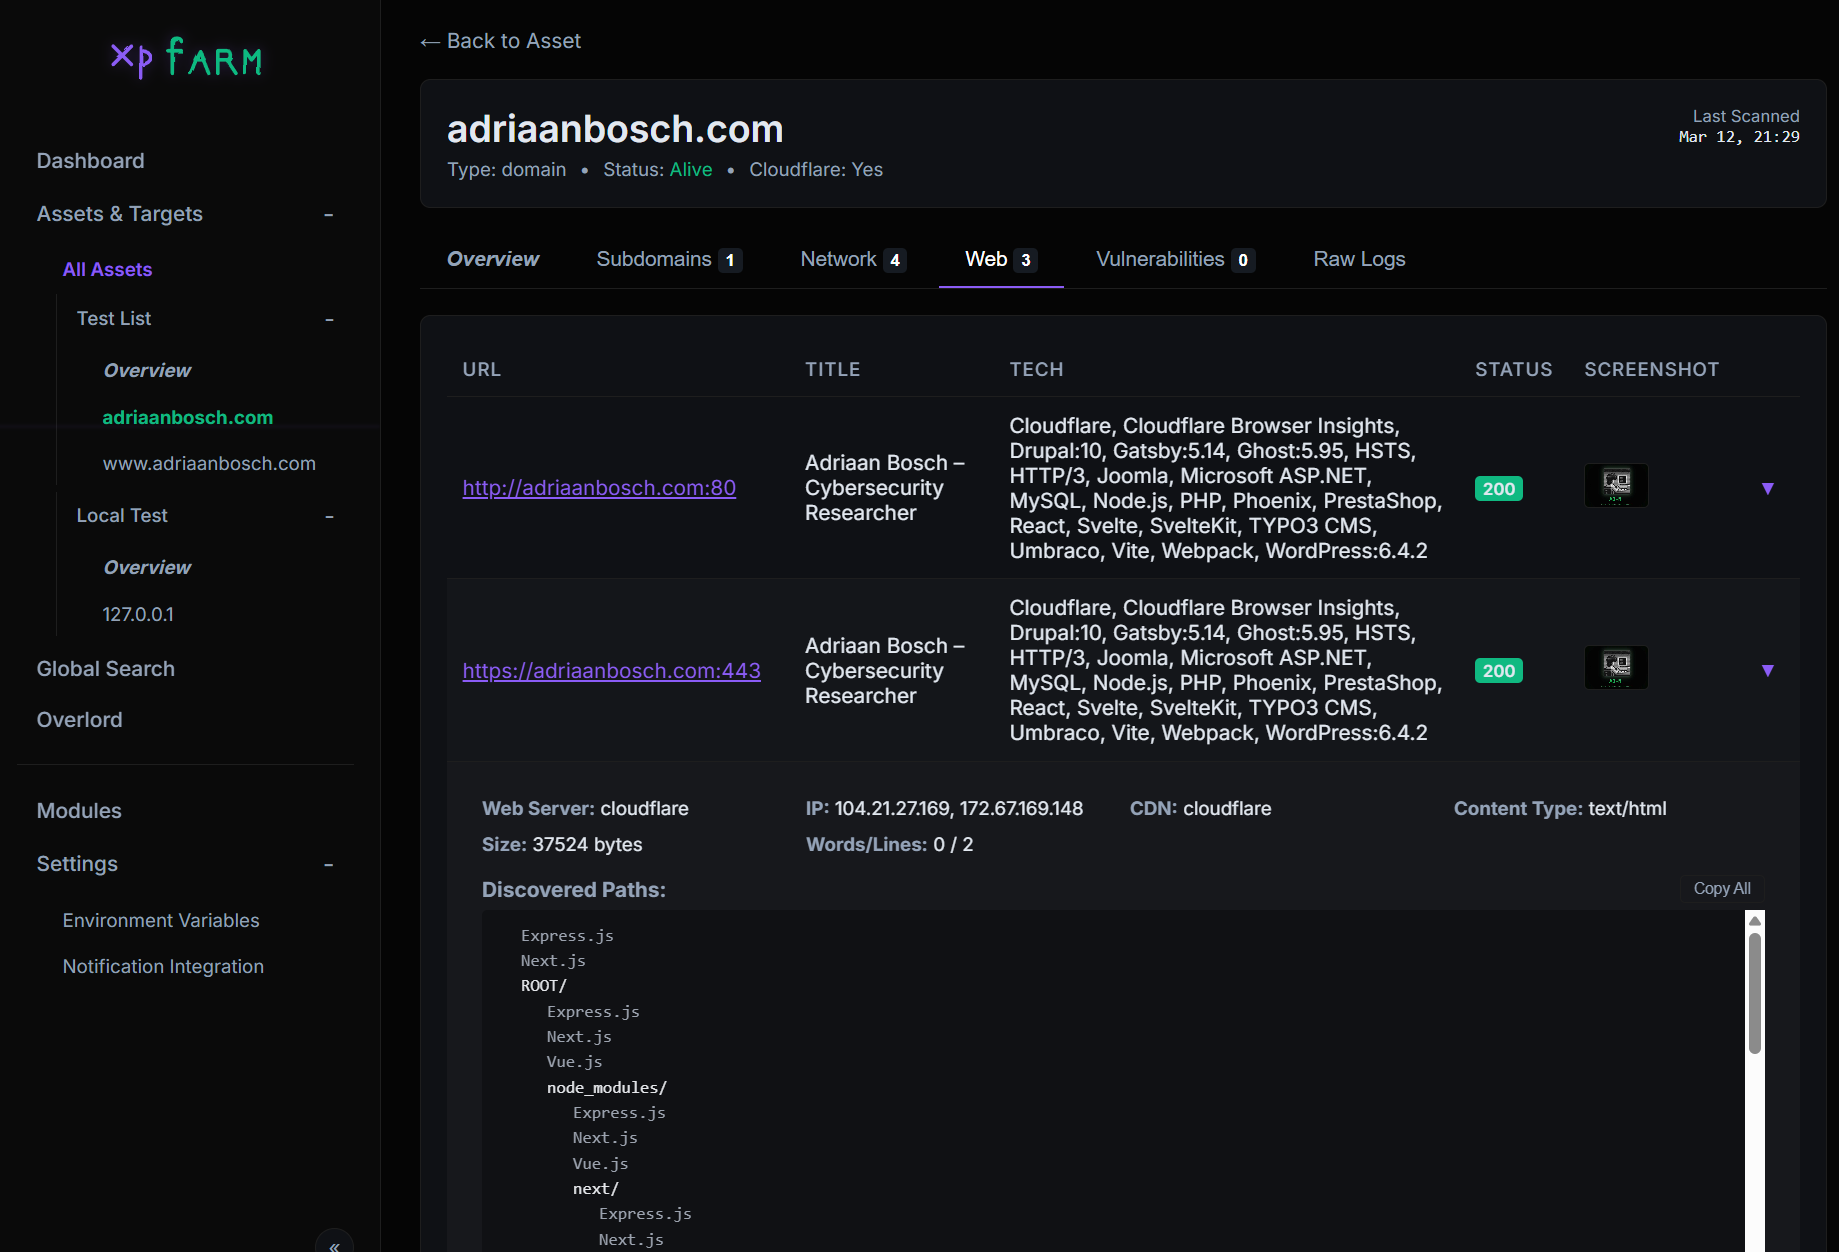 canuk40/xpfarm
Automated bug bounty & recon framework — wraps Subfinder, Naabu, Httpx, Nuclei, Nmap, CVEMap, Gowitness, Katana & more behind a unified web UI
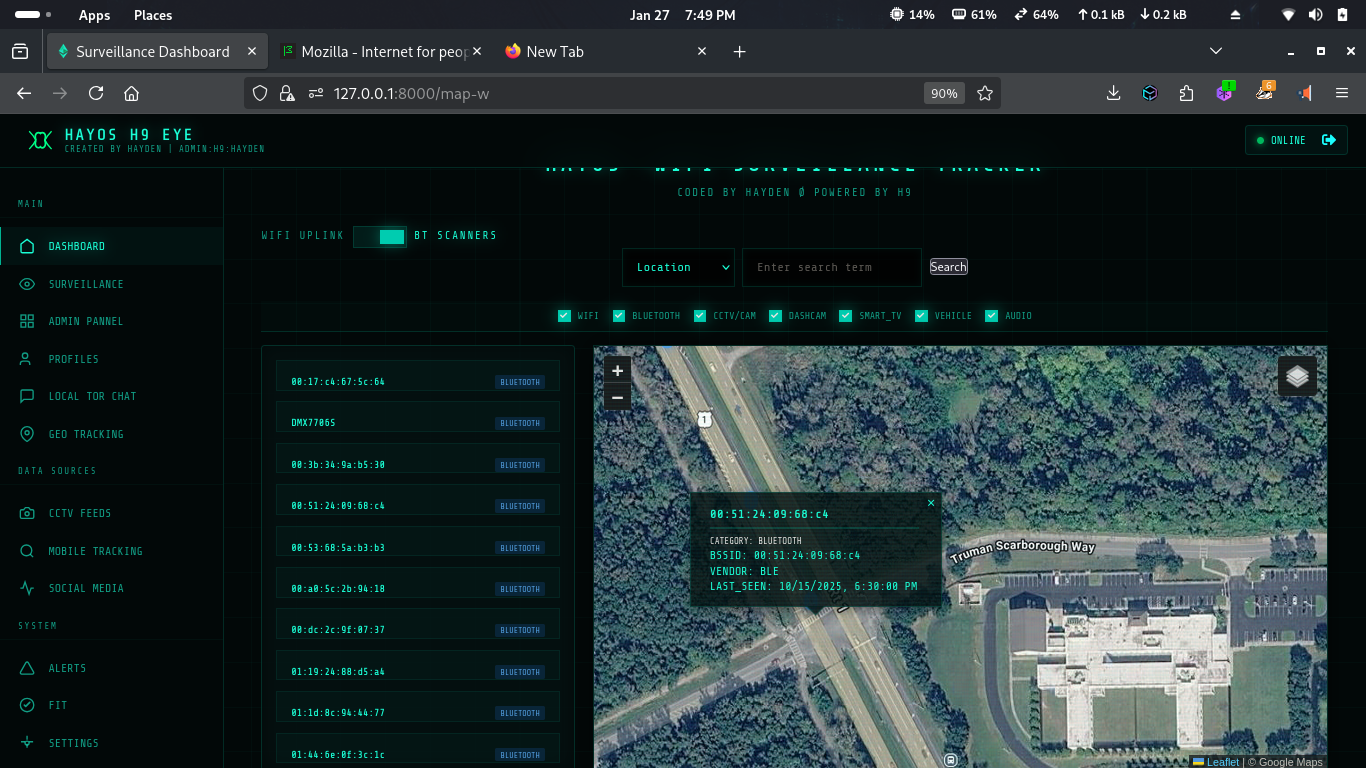 h9zdev/wiretapper
Passive wireless OSINT platform that detects and maps Wi-Fi, Bluetooth, CCTV, IoT devices, and cell towers using radio signal intelligence for…
 milesrichardson/docker-onion-nmap
Scan .onion hidden services with nmap using Tor, proxychains and dnsmasq in a minimal alpine Docker container.
 j3ssie/metabigor
OSINT reconnaissance tool for network discovery, subdomain enumeration, IP enrichment, and secret detection via certificate logs, Shodan, and GitHub…
 chrismaddalena/odin
Automated network asset, email, and social media profile discovery and cataloguing.
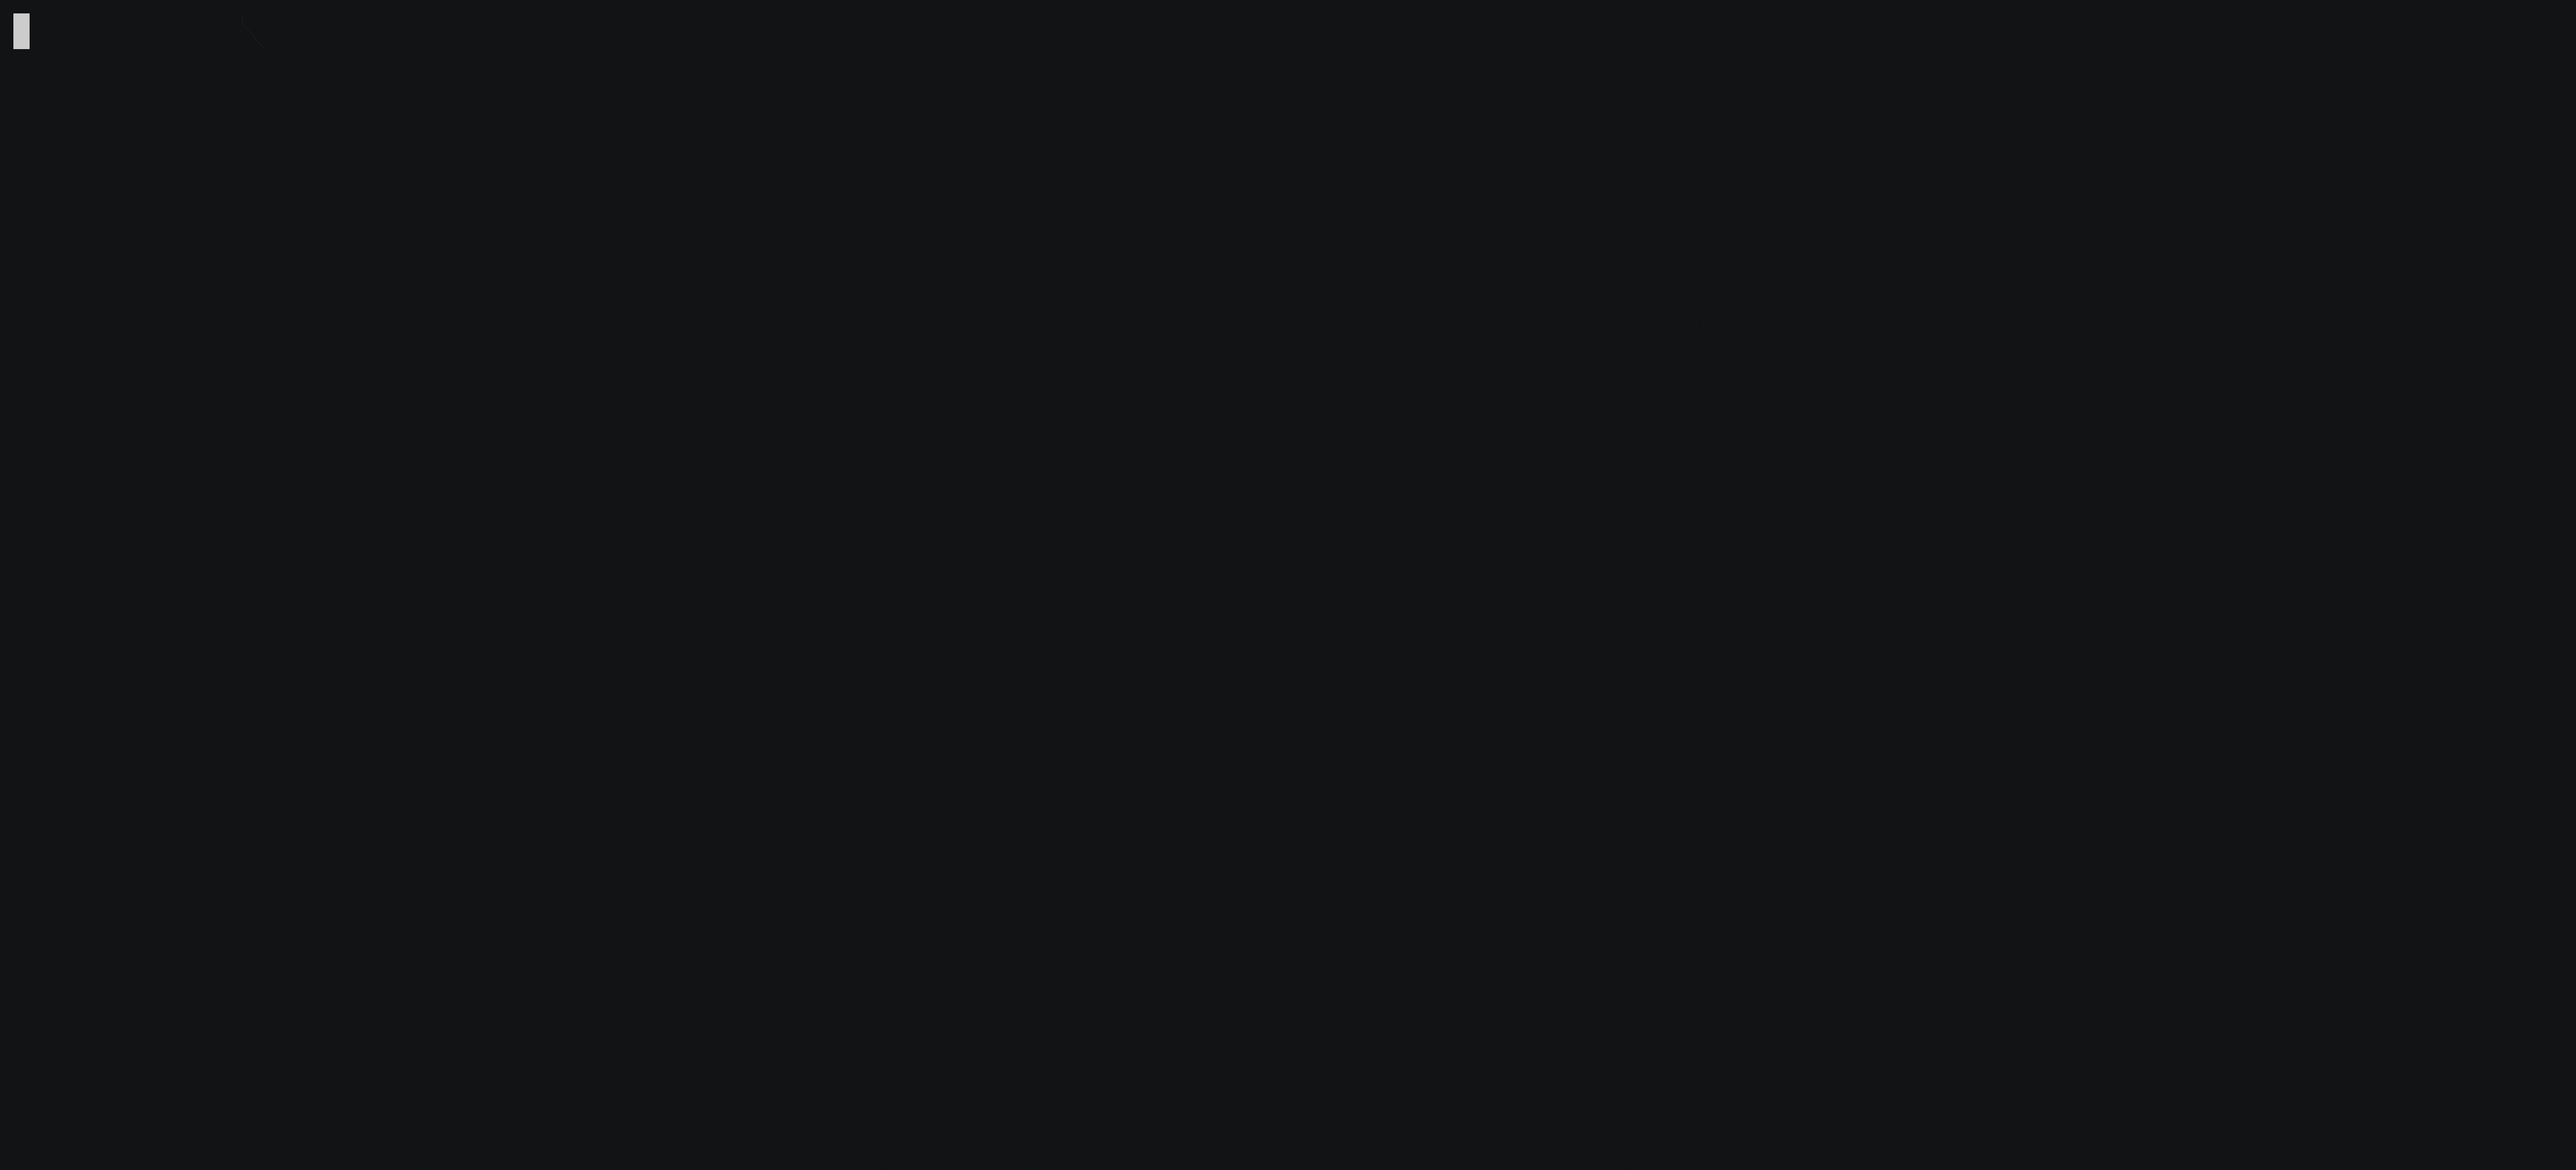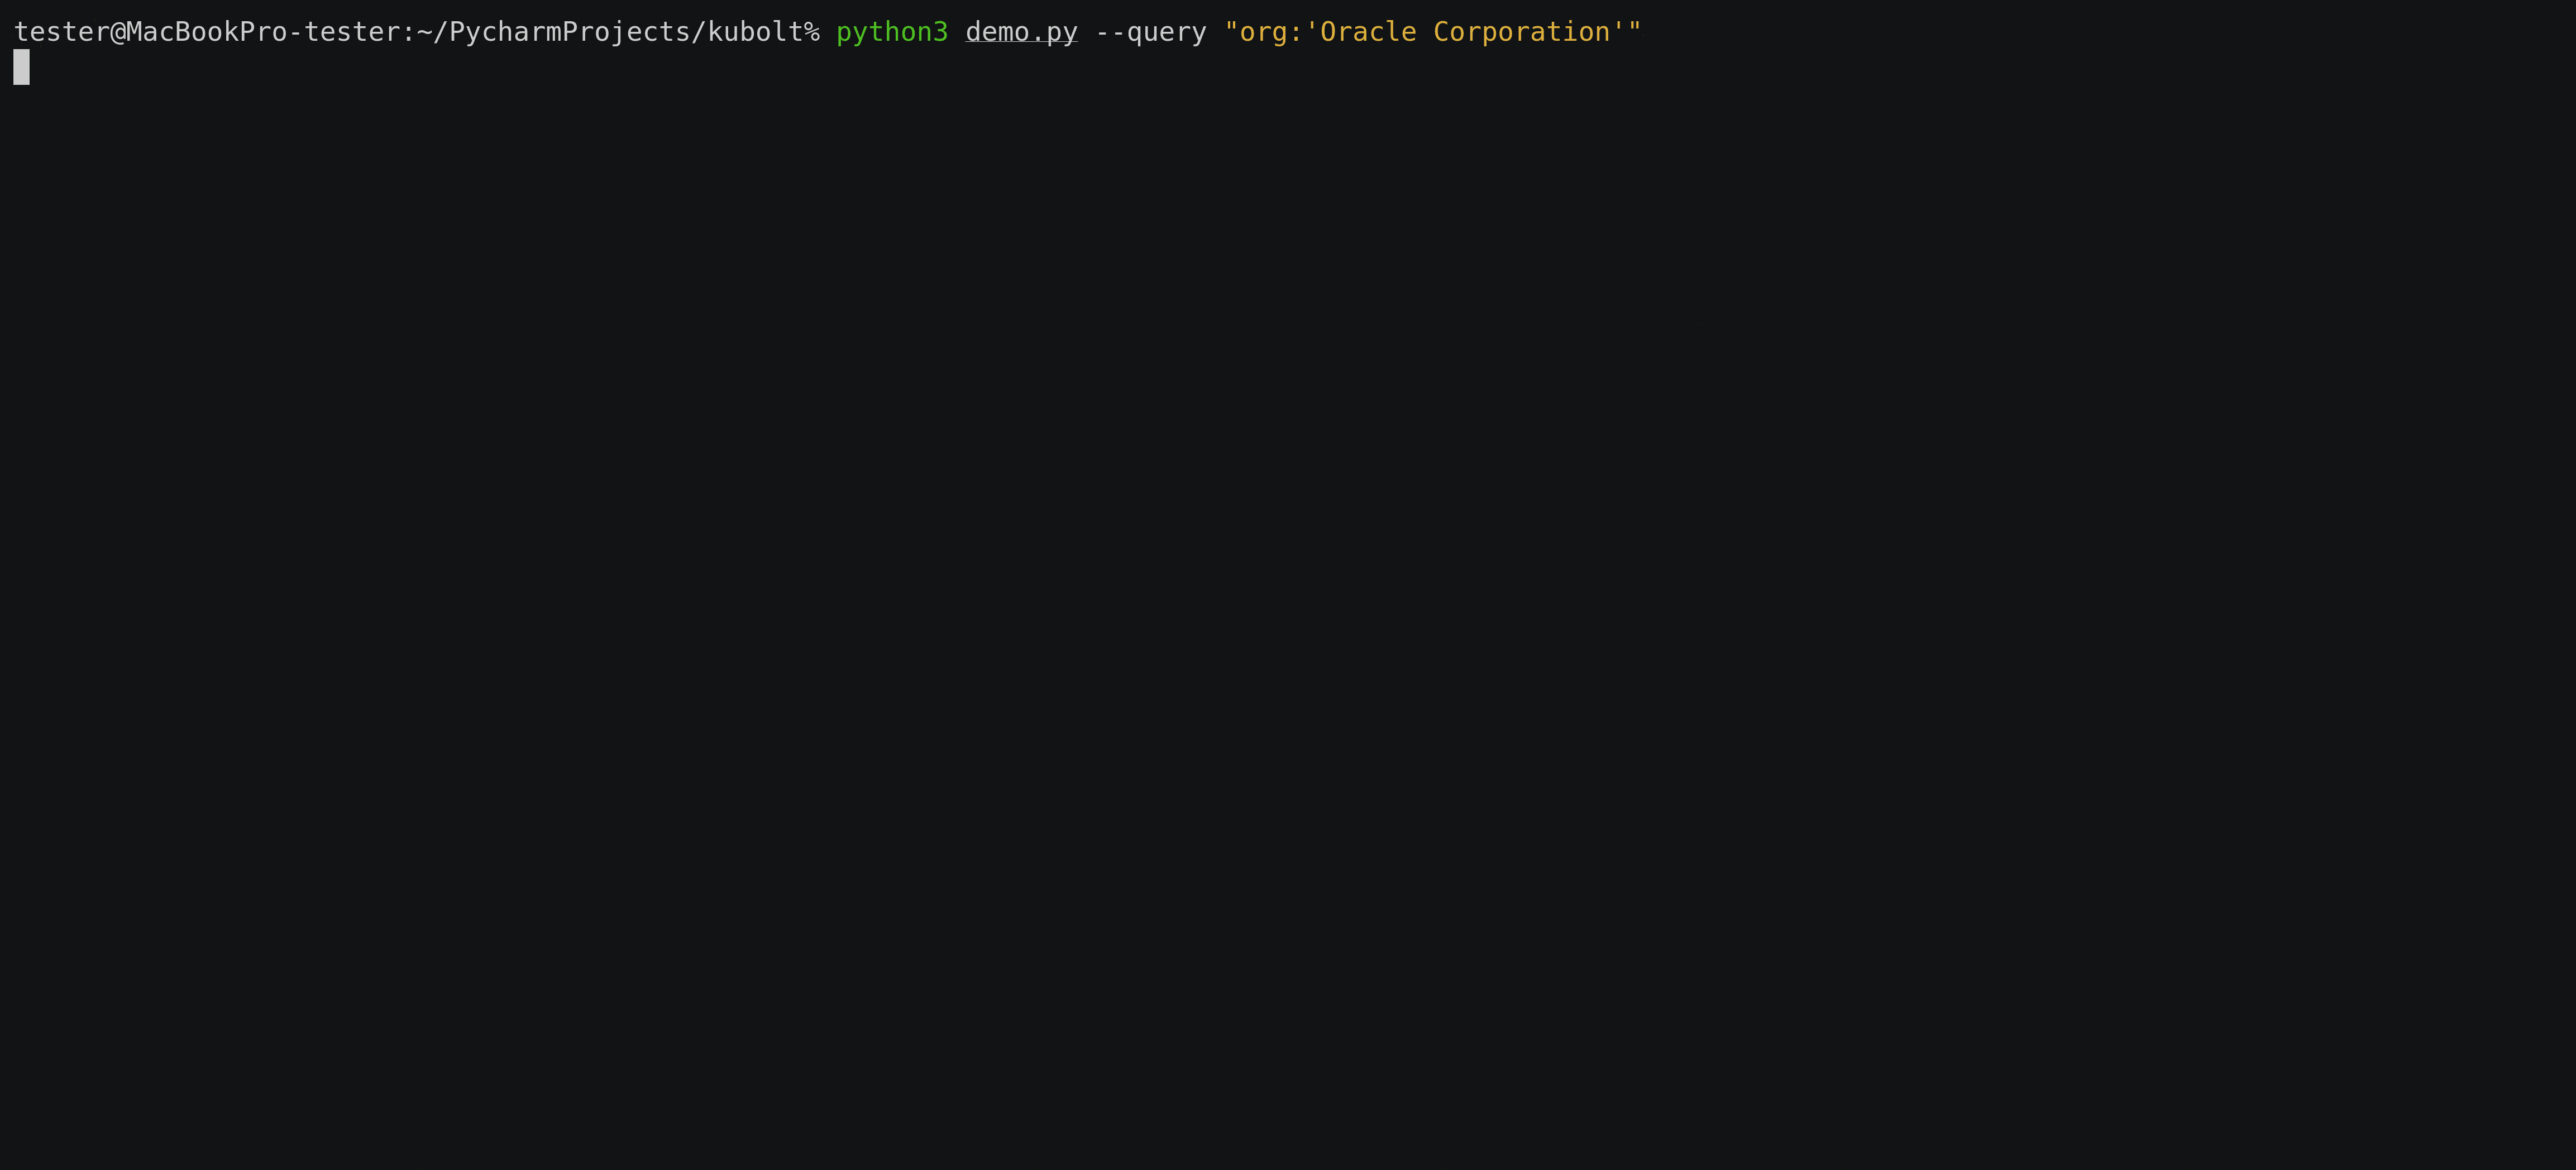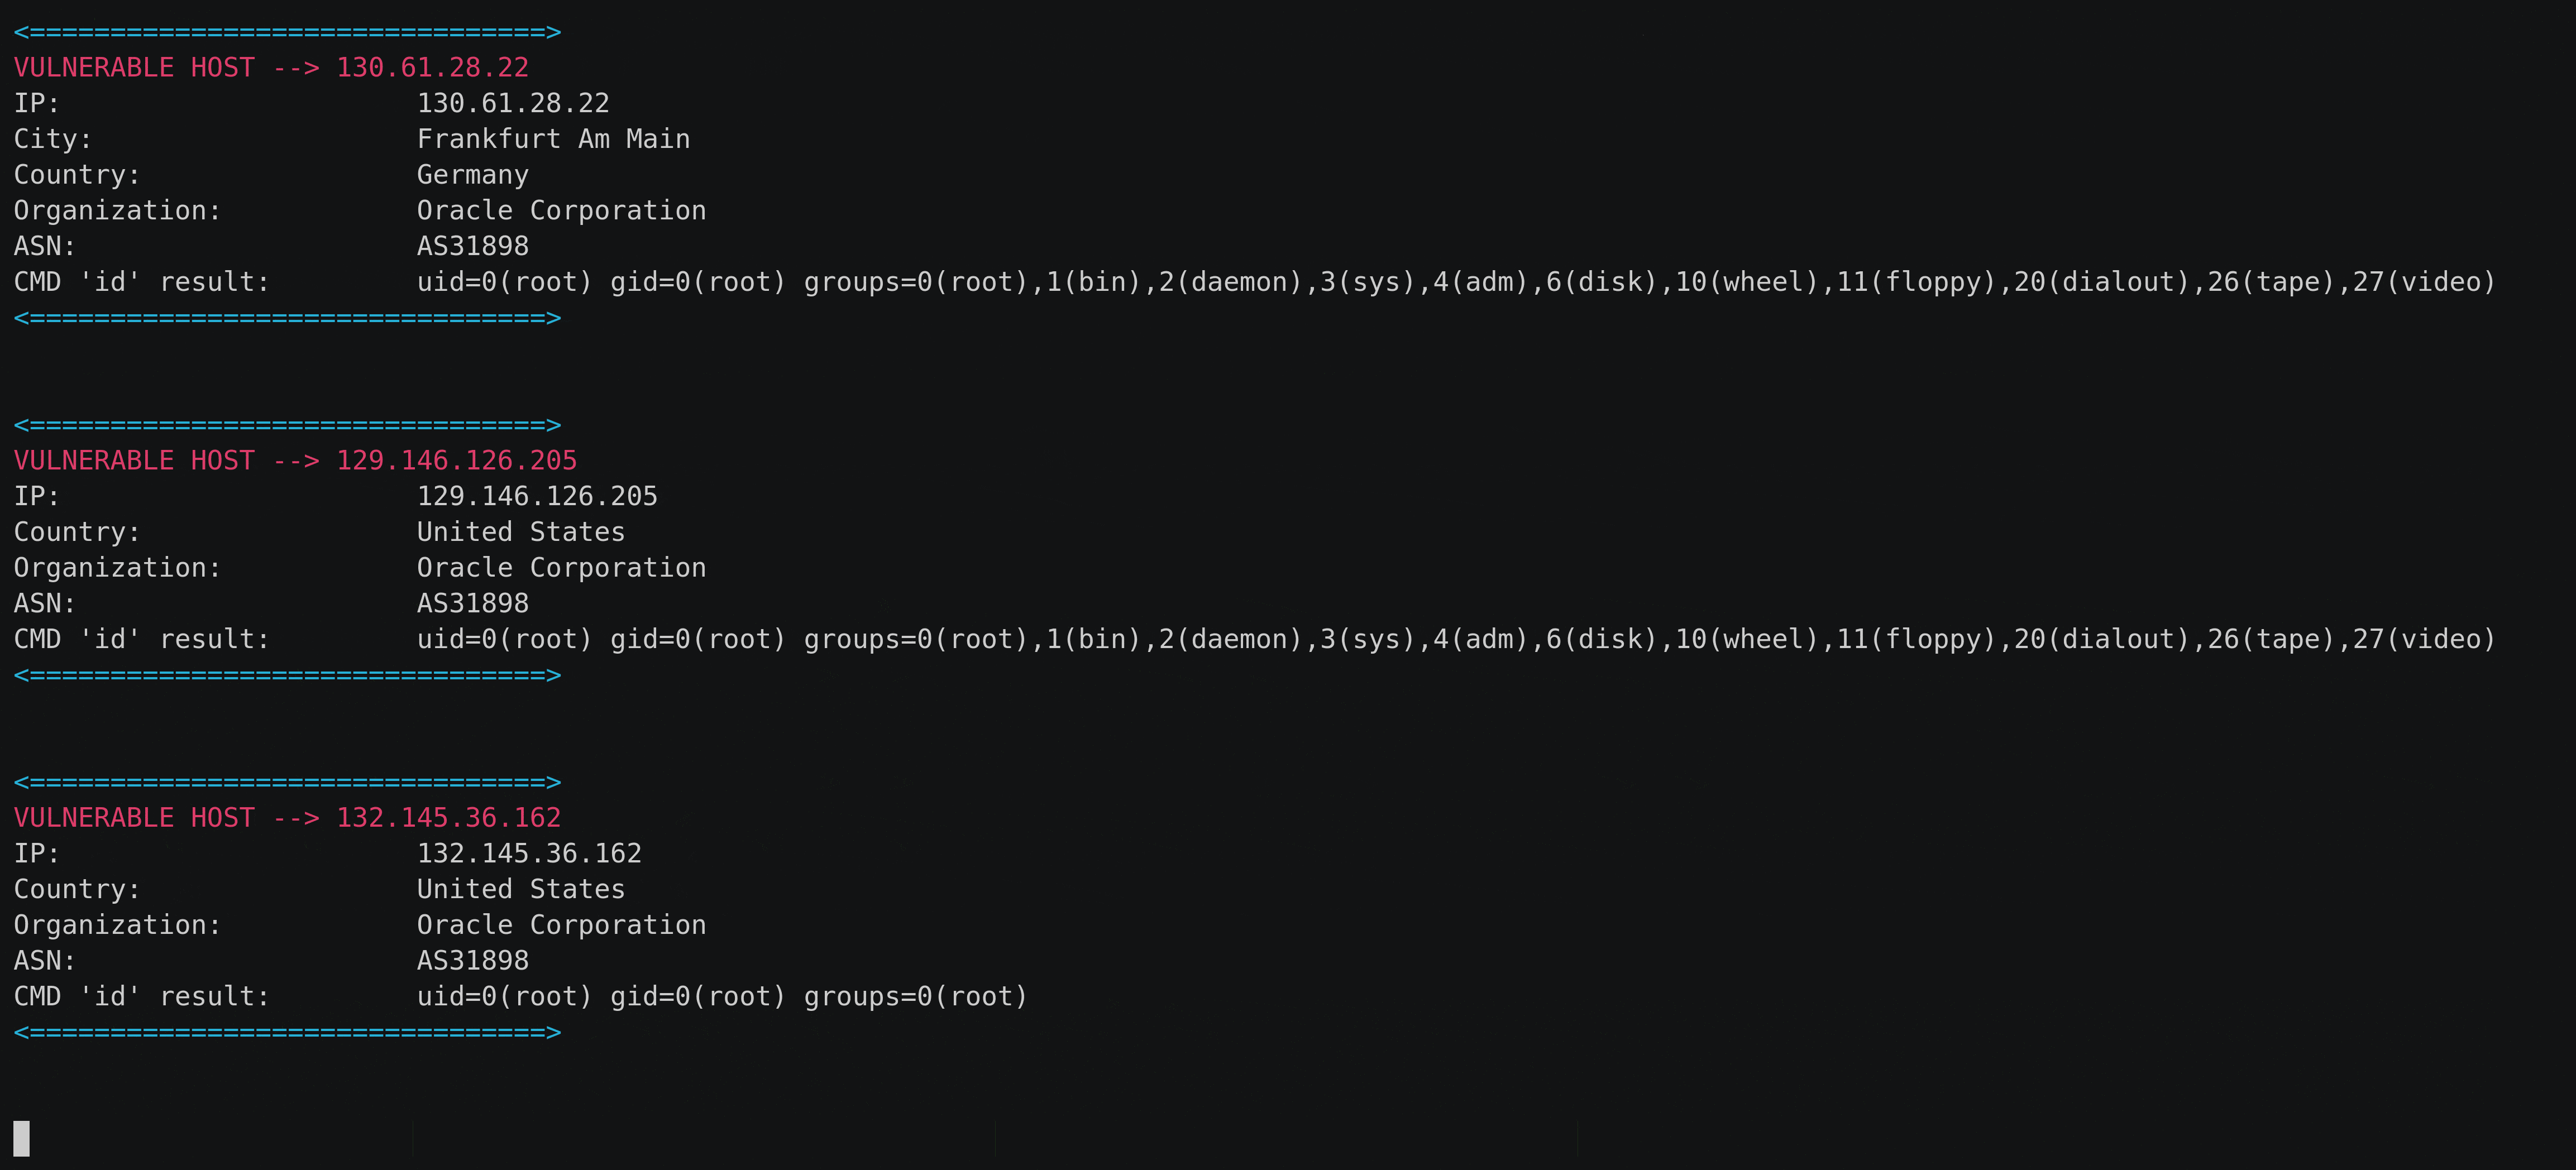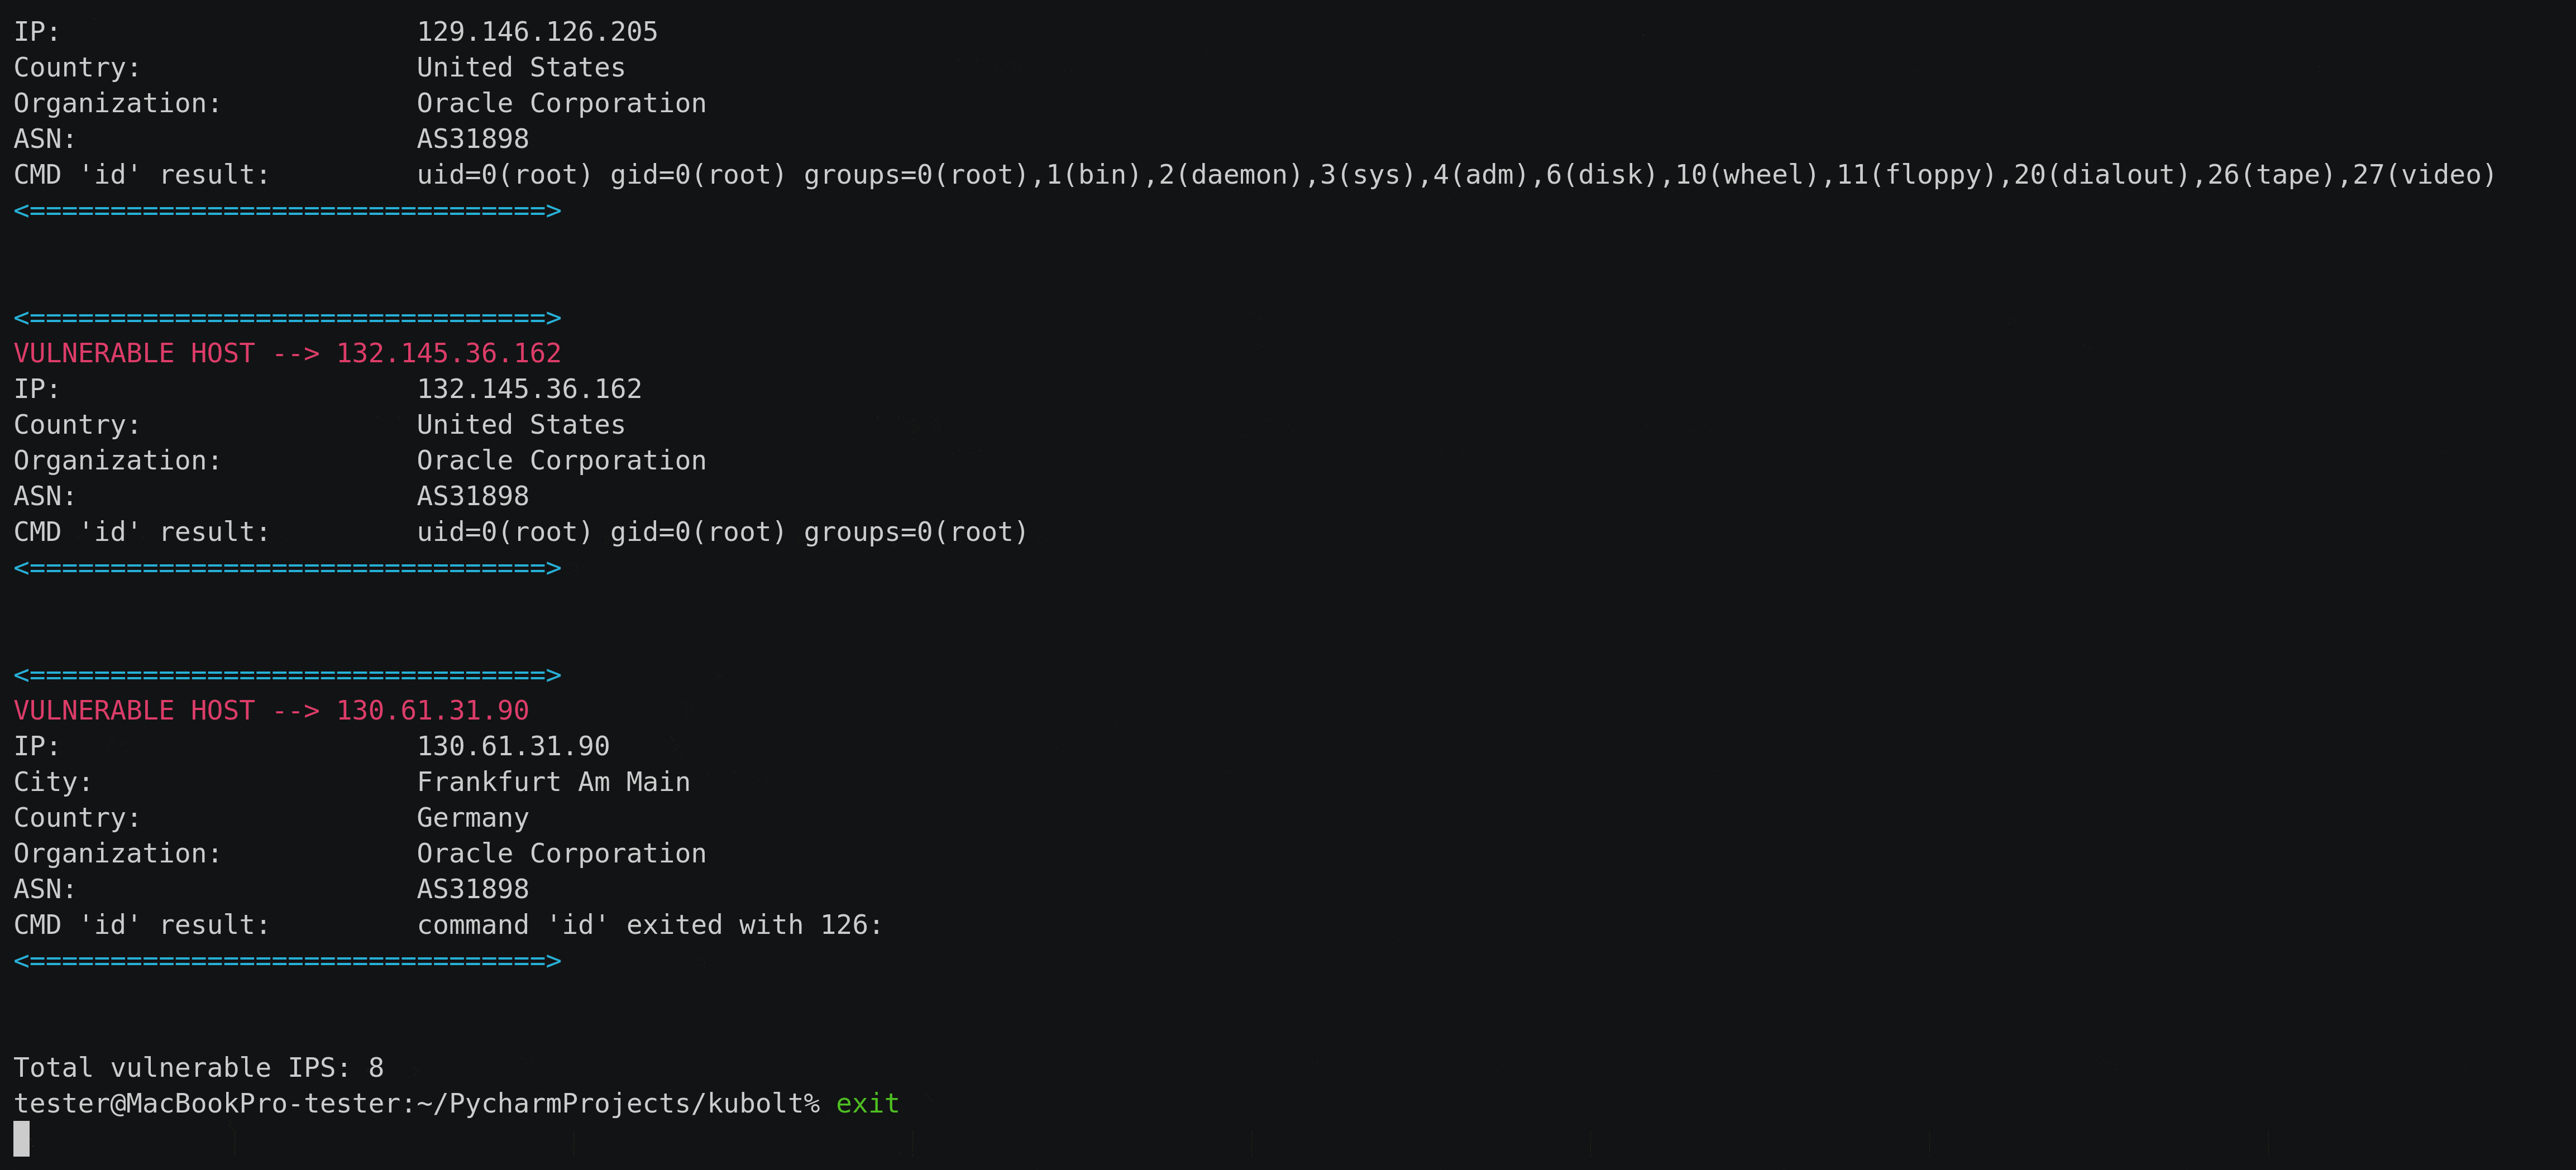 averonesis/kubolt
Kubolt utility for scanning public kubernetes clusters
 offxec/samurai
Bash-based email discovery framework that extracts email addresses using Google dork queries, company names, or domain names for OSINT reconnaissance.
 a3h1nt/sububy
Modular subdomain enumeration suite with certificate transparency, DNS brute-force, and API-based discovery. Includes post-enumeration modules for…
 rix4uni/wordlist
Curated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…
 laramies/theharvester
E-mails, subdomains and names Harvester - OSINT
 gwen001/pentest-tools
A collection of custom security tools for quick needs.