

msticpy
 microsoft/msticpy
Microsoft Threat Intelligence Security Tools
anomaly-detectioncloud-securityeducation+6
microsoft/msticpyMicrosoft Threat Intelligence Security Tools
 redbyte1337/credspy
Entra ID user enumeration and auth method discovery via the public GetCredentialType API
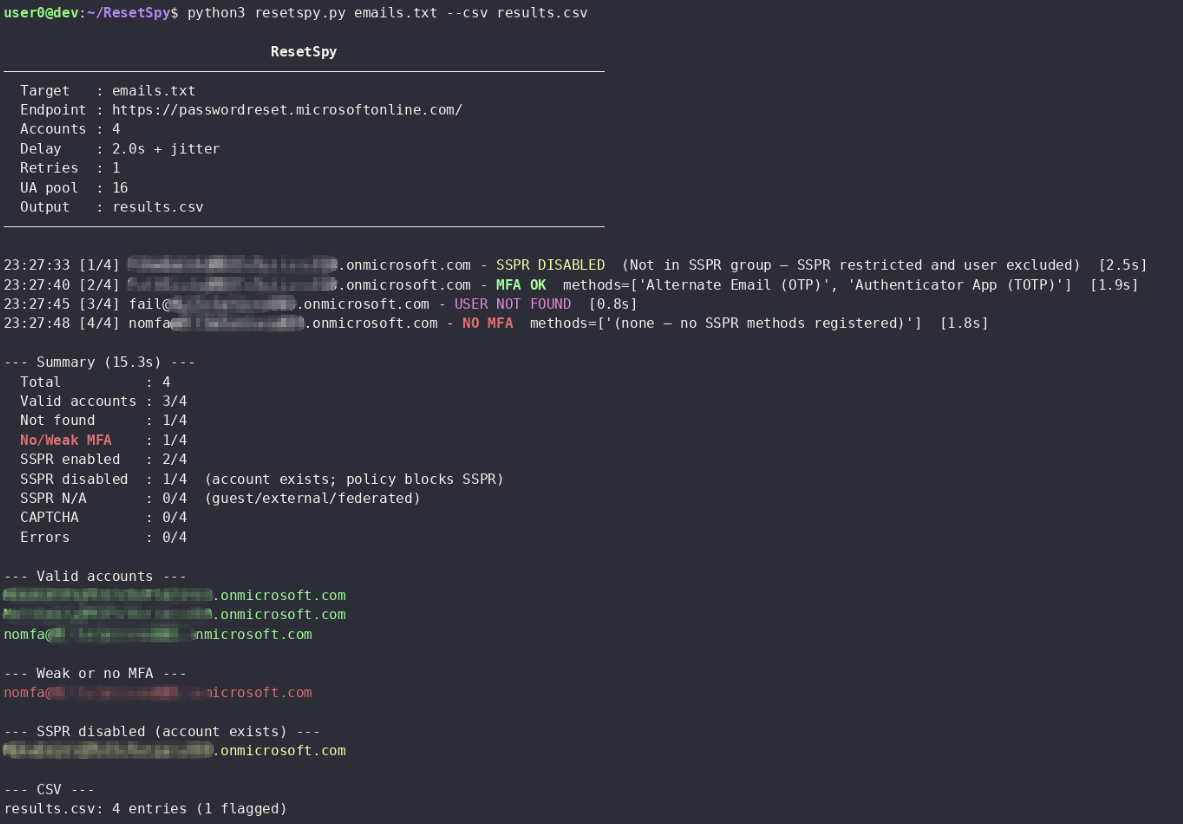 mlcsec/resetspy
Enumerate user accounts and registered authentication methods via the Microsoft Self-Service Password Reset (SSPR) portal
 logisek/azureadenumeration
Microsoft Entra ID (Azure AD) Unauthenticated Enumeration
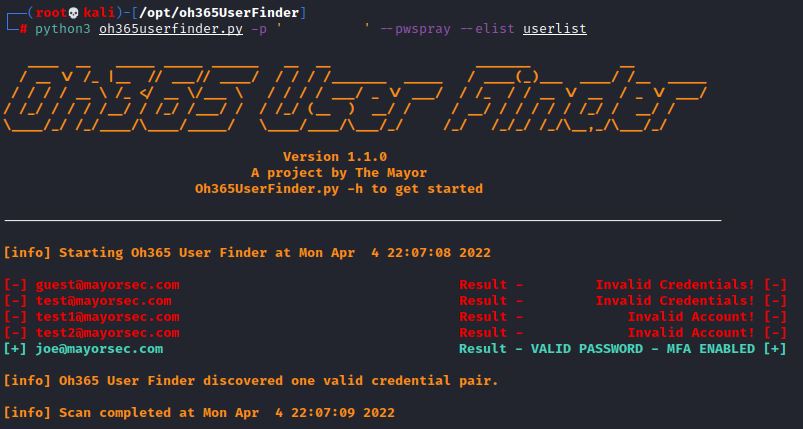 dievus/oh365userfinder
Enumerates valid Microsoft 365 accounts and domains via response analysis, with password spraying support and throttling detection to avoid lockouts.
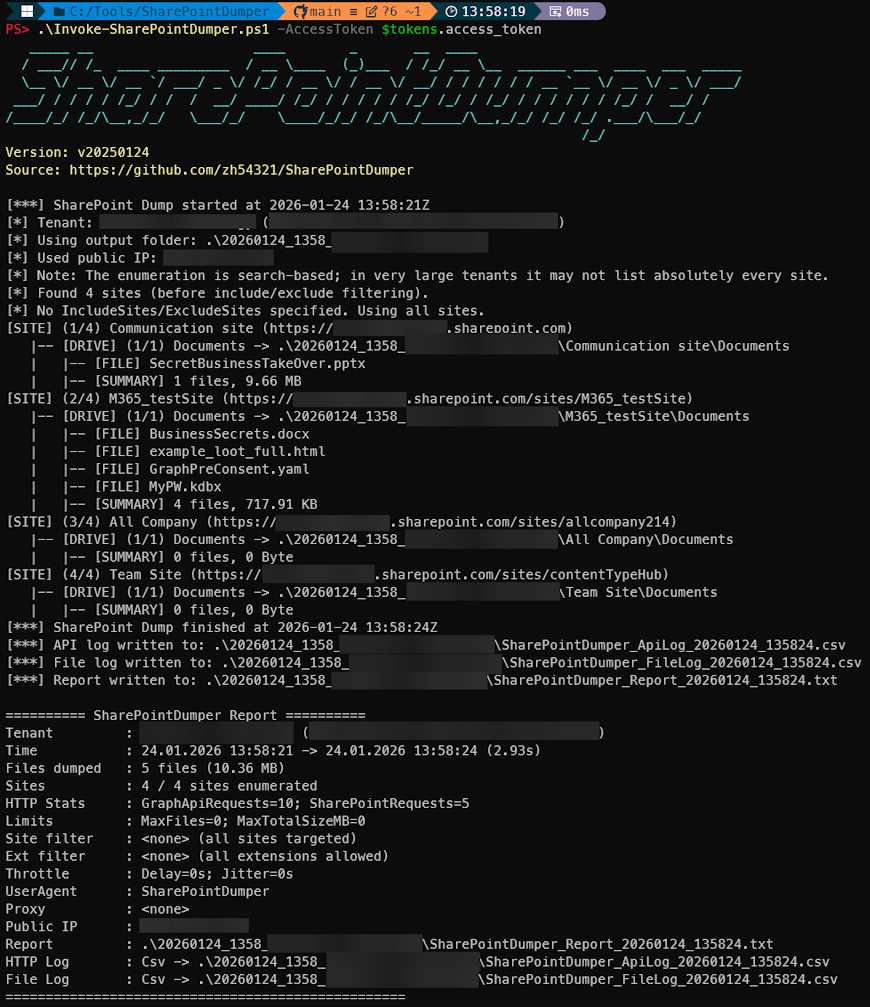 zh54321/sharepointdumper
PowerShell SharePoint extraction + auditing tool for red/blue/purple teams. Enumerates all SharePoint sites/drives a user can access via Microsoft…
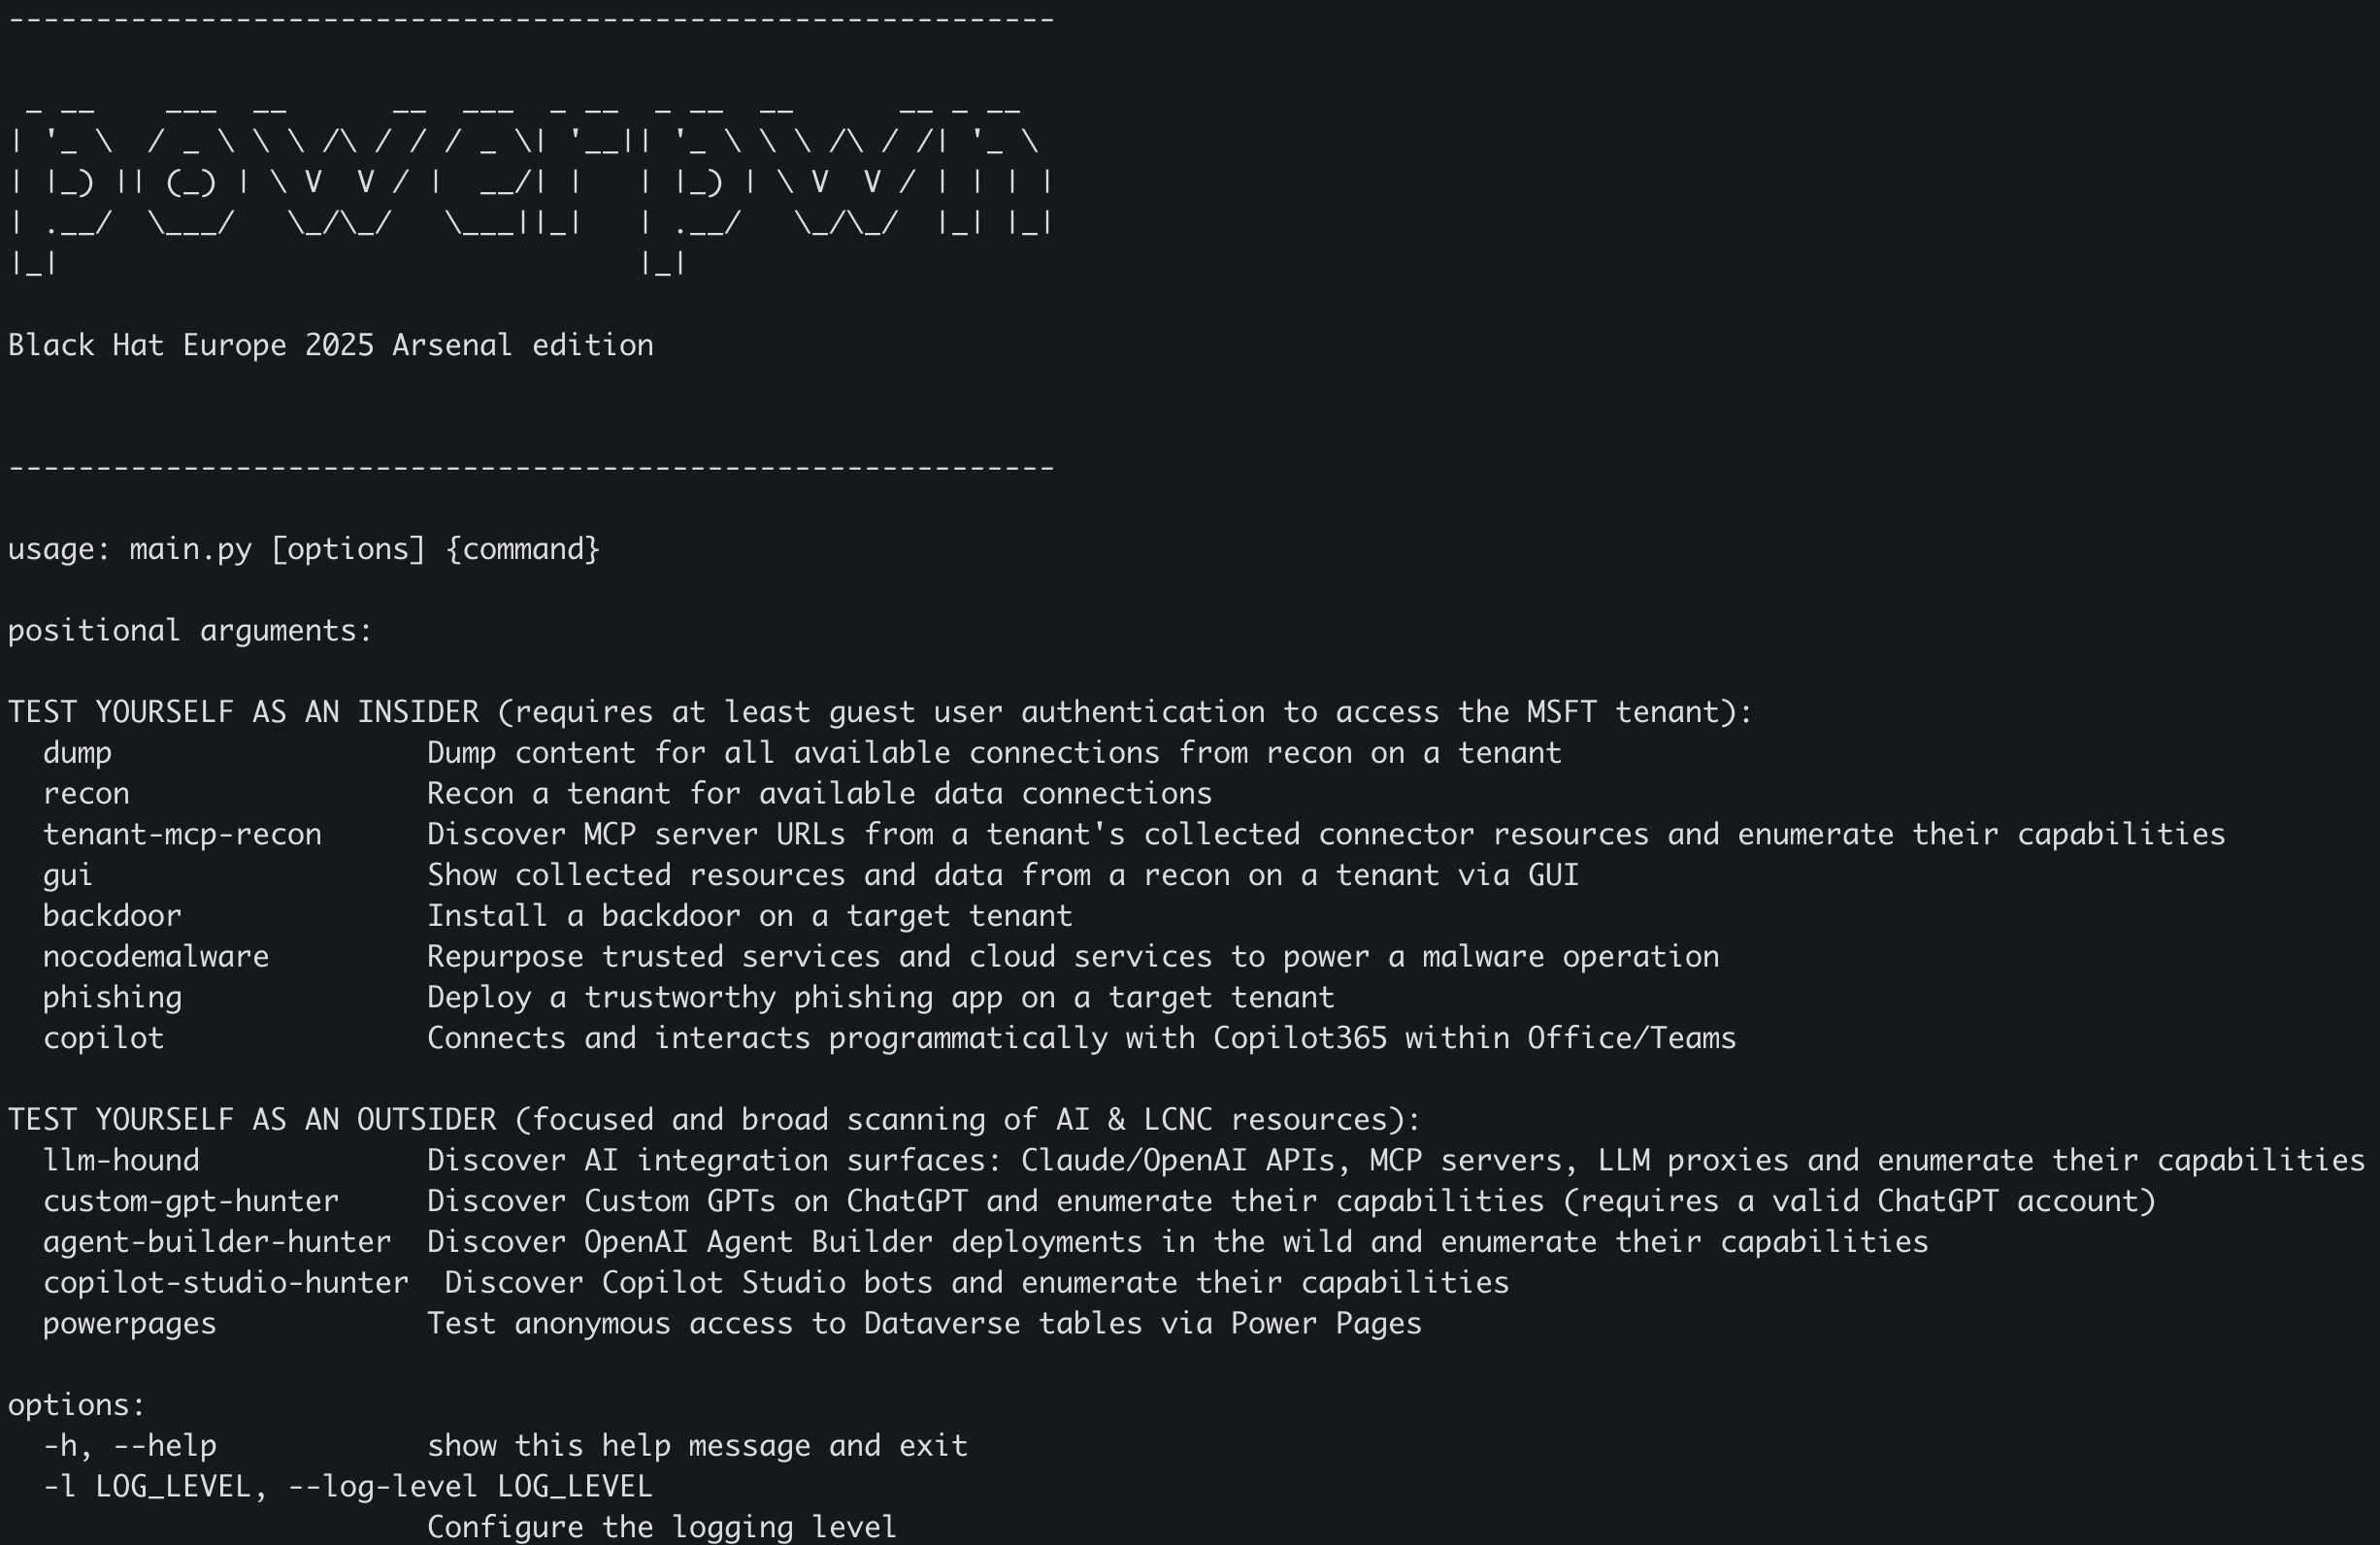 mbrg/power-pwn
An offensive/defense security toolset for discovery, recon and ethical assessment of AI Agents
 0xsha/cloudbrute
Uncover a target's cloud infrastructure, files, and apps across major providers (AWS, Azure, GCP) using unauthenticated enumeration with concurrent…
 optiv/knockknock
Enumerate valid users within Microsoft Teams and OneDrive with clean output.
 expl0itabl3/check_mdi
Python script to enumerate valid Microsoft 365 domains, retrieve tenant name, and check for an MDI instance.
 nccgroup/metadataplus
A tool to use novel locations to extract metadata from Office documents.
 joelgmsec/azuregraph
PowerShell tool for enumerating Azure AD users, devices, applications, and domains via Microsoft Graph API, with offline data export capability.
 dafthack/msolspray
A password spraying tool for Microsoft Online accounts (Azure/O365). The script logs if a user cred is valid, if MFA is enabled on the account, if a…
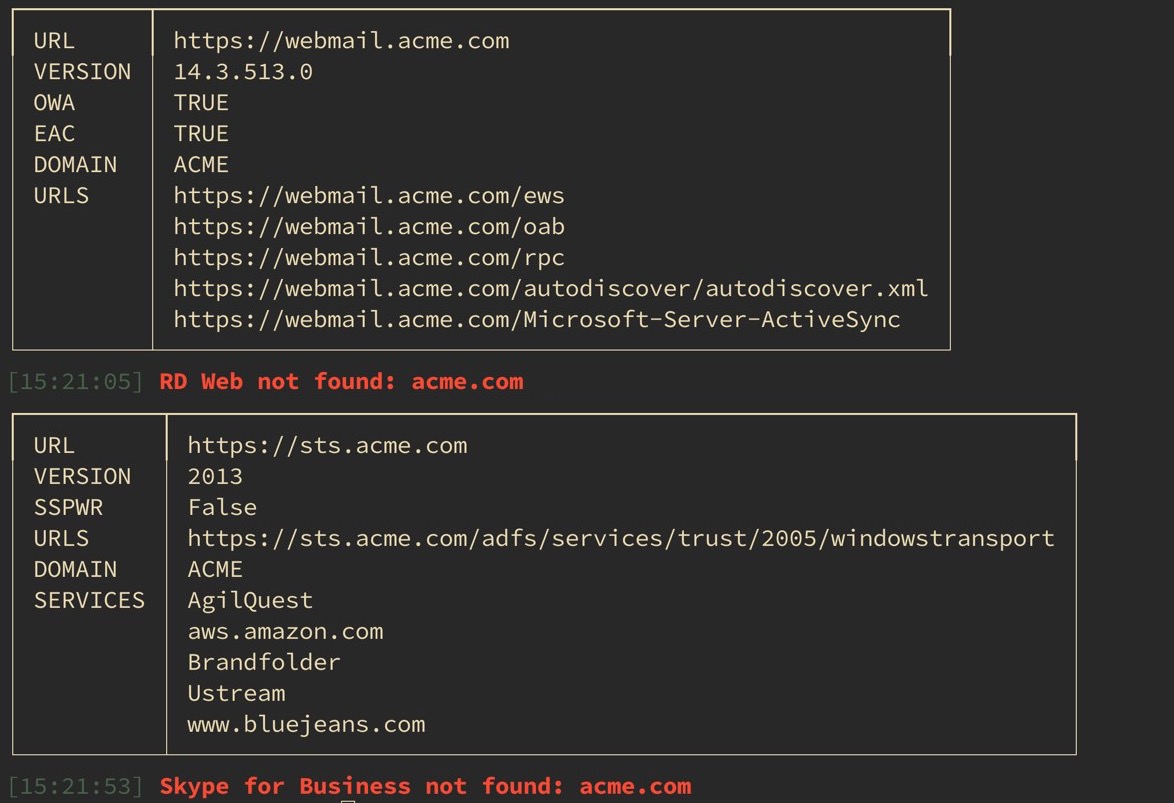 puzzlepeaches/msprobe
Finding all things on-prem Microsoft for password spraying and enumeration.
 immunit/teamsuserenum
User enumeration with Microsoft Teams API
 cnotin/m365_groups_enum
Enumerate Microsoft 365 Groups in a tenant with their metadata