
Shadowbroker
 bigbodycobain/shadowbroker
Real-time geospatial OSINT platform aggregating 60+ public telemetry feeds (ADS-B, AIS, satellites, CCTV) into a unified map with server-side recon…
command-and-controlcrawlerdns-analysis+7
11.4k
bigbodycobain/shadowbrokerReal-time geospatial OSINT platform aggregating 60+ public telemetry feeds (ADS-B, AIS, satellites, CCTV) into a unified map with server-side recon…
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 princessauroraj/chinese-cybercrime-research
Resources to learn more about Chinese-language cybercrime actors.
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 m4elstr0m/gophoner
Check simultaneously if a phone number is registered on popular apps & websites, without any prerequisite 📞
 here_forawhile/terminalphone
Encrypted push-to-talk voice and text communication over Tor hidden services with end-to-end encryption, configurable ciphers, relay mode for group…
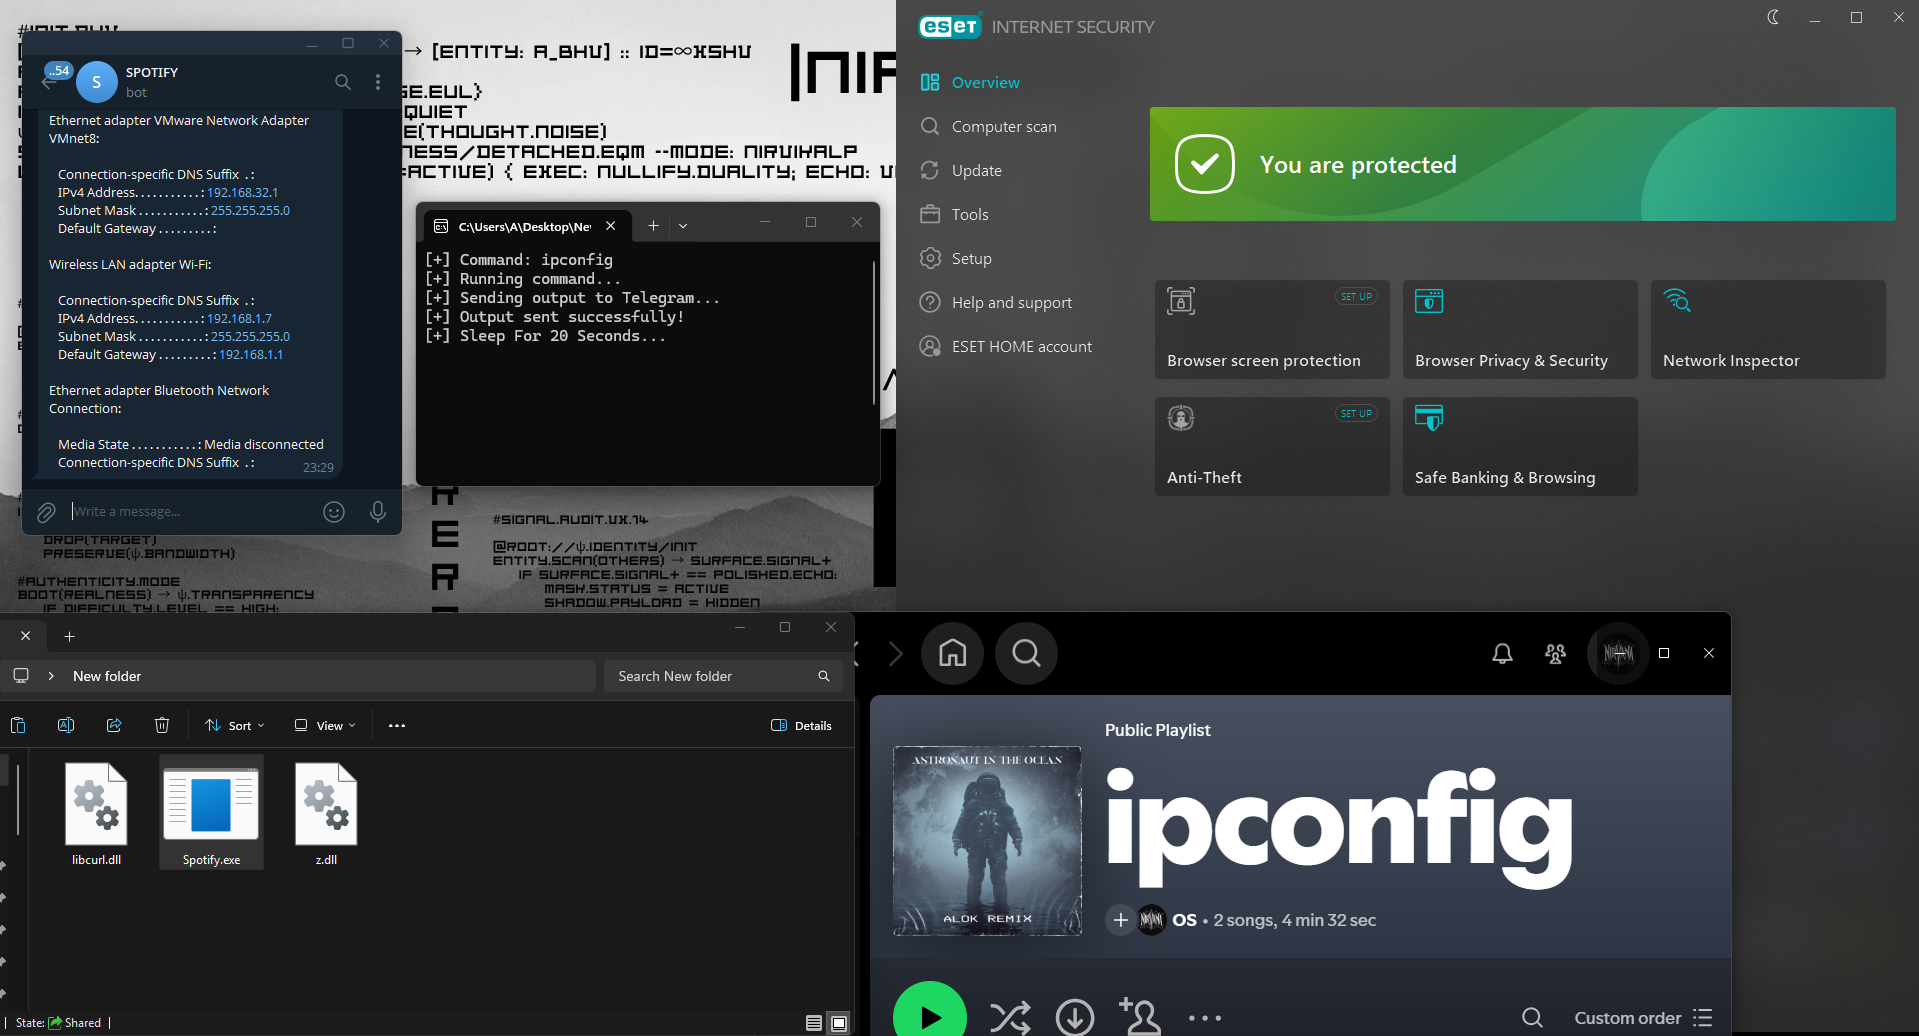 nirvanaon/spotifyc2
Windows-based C2 research tool that uses Spotify playlists as a command channel and Telegram for output delivery, demonstrating cloud-assisted…
 cogensec/gideon
Autonomous security operations agent for threat intelligence, vulnerability research, IOC analysis, and red teaming. Supports dual-mode operations…
 askhatov21/best-practices-cybersecurity-otanata-project
CVE-2024-3273 — Authorized Penetration Test Report D-Link DNS-320L NAS | Client: Otonata
 montysecurity/c2-tracker
Live Feed of C2 servers, tools, and botnets
 shadowopcode/desckvb-rat
Full analysis of a never documented before Remote Access Trojan linked to Pjoao1578 toolchain
 7h30th3r0n3/ollamahound
Mass reconnaissance, version fingerprinting, CVE tester and live exploitation framework for Ollama open instances.
 matthewwiese/hinge-command-control-c2
A proof of concept demonstrating how to use the Hinge dating app as a C2.
 hotpotcookie/cve-2022-44877-white-box
Red Team utilities for setting up CWP CentOS 7 payload & reverse shell (Red Team 9 - CW2023)
 threatexpress/domainhunter
Checks expired domains for categorization/reputation and Archive.org history to determine good candidates for phishing and C2 domain names
 splunk/melting-cobalt
A Cobalt Strike Scanner that retrieves detected Team Server beacons into a JSON object
 pjlantz/hale
Botnet command & control monitor