

dddd
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
fingerprint-spoofinginformation-gatheringnetwork-mapping+9
1.9k
sleepingbag945/ddddBatch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 qyvora/qyvora-anansi
Terminal-first attack surface intelligence engine. Built for speed, portability, and raw technical signal.
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 strategic-automation/violin
Agentic pentest profile for Hermes: 31 playbooks for authorised recon, web/access-control attacks, safe exploit validation, and evidence-driven…
 0xdea/tactical-exploitation
Modern tactical exploitation toolkit.
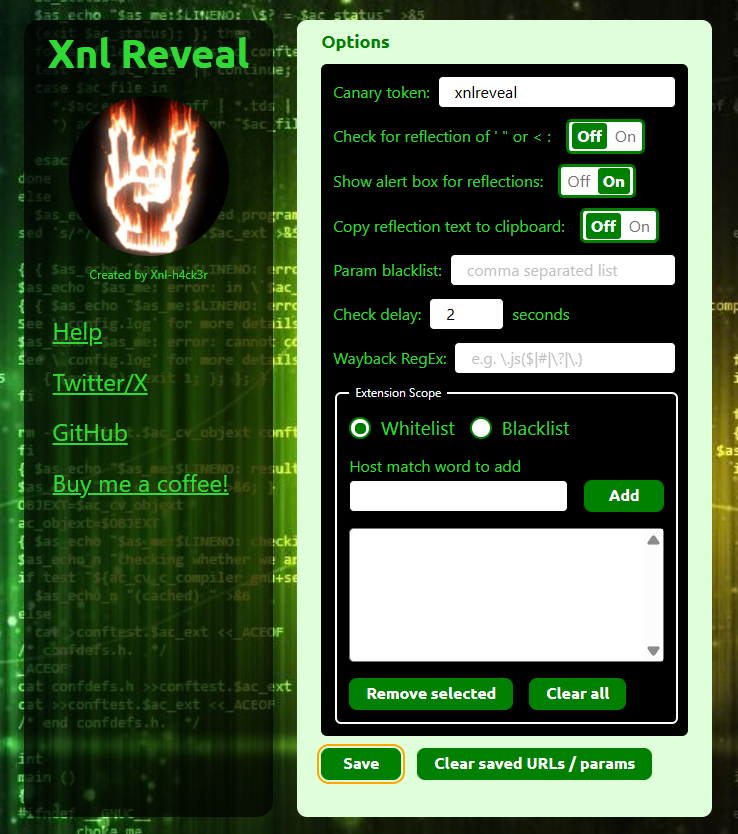 xnl-h4ck3r/xnlreveal
A Chrome/Firefox browser extension to show alerts for reflected query params, show Wayback archive links for the current path, show hidden elements…
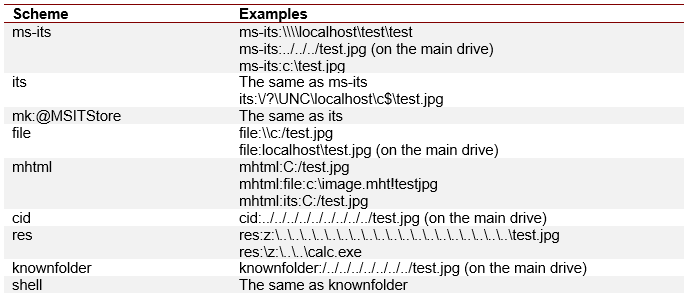 nccgroup/outlookleaktest
The Outlook HTML Leak Test Project
 jenderal92/alfa-perl-rce-zoneh-grabber-python
Python2.7
 ef3tr/cve-2026-4106
WordPress HTMega Unauthenticated PII Disclosure Exploit (CVE-2026-4106)
 pilfer/idictpy
A salty-ass 100% verified hacker status python script to turn apple id's into apple crisp #nicememe
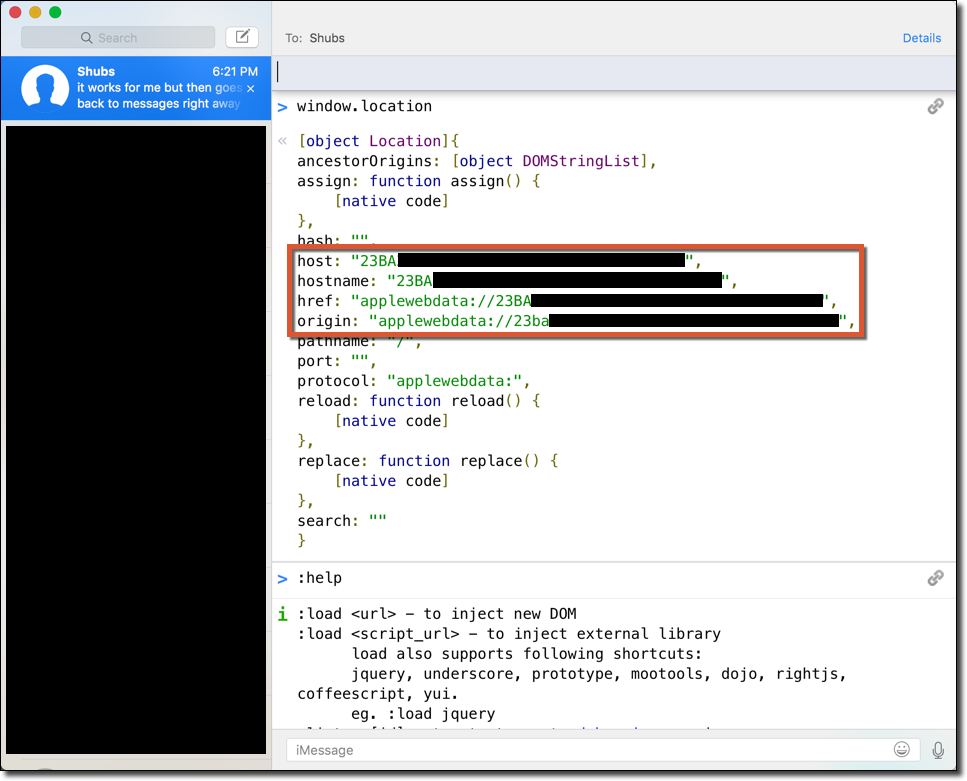 moloch--/cve-2016-1764
Extraction of iMessage Data via XSS
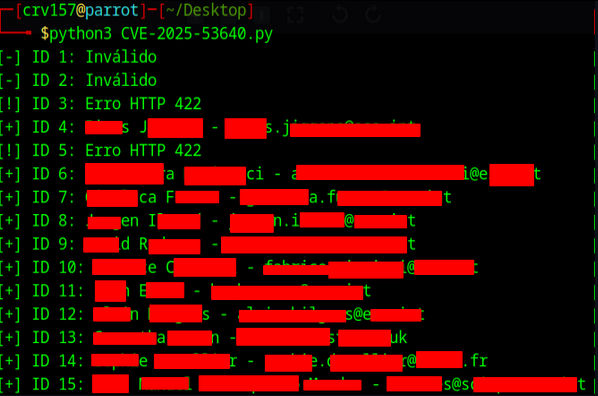 rafaelcorvino1/cve-2025-53640
Broken Object Level Authorization (BOLA) in CERN's Indico leads to authenticated user enumeration.
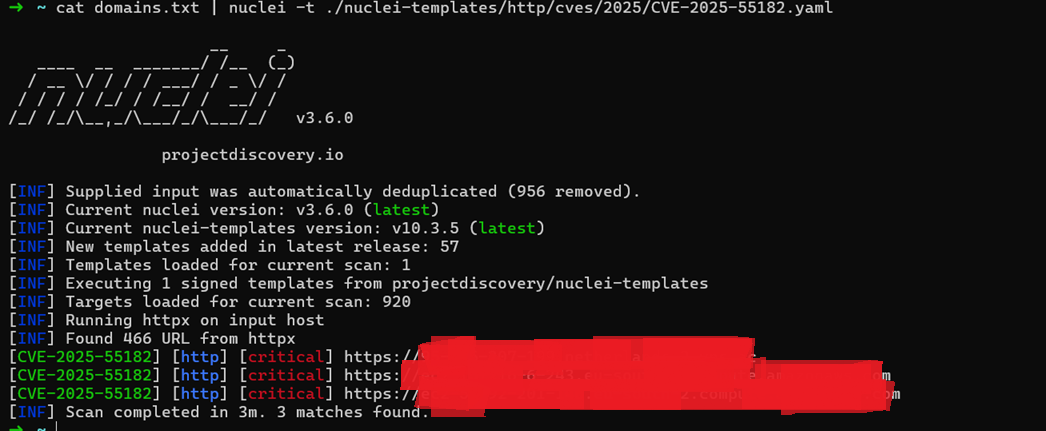 jaycelation/cve-2025-55182
PoC, Hunting React2Shell about CVE-2025-55182
 mmoobbeeiidat-design/hack-the-box-enigma-findings-report
HTB_Enigma Security Assessment – Full pentest completed, chaining NFS disclosure, IMAPS password reuse, and OS Command Injection in OpenSTAManager…
 sunny-kathuria/exploit_cve-2022-26134
CVE-2022-26134, an OGNL injection vulnerability exists that would allow an unauthenticated attacker to execute arbitrary code on a Confluence Server…