

disclosure-check
 gmh5225/disclosure-check
Tool to identify the best mechanisms for privately disclosing a security vulnerability for a package/project.
defensive-toolsinformation-gatheringosint+4
gmh5225/disclosure-checkTool to identify the best mechanisms for privately disclosing a security vulnerability for a package/project.
 0xmarcio/pocindex
Search 82,000+ public CVE proof-of-concept exploits from GitHub, Nuclei, ExploitDB, Metasploit and Vulhub.
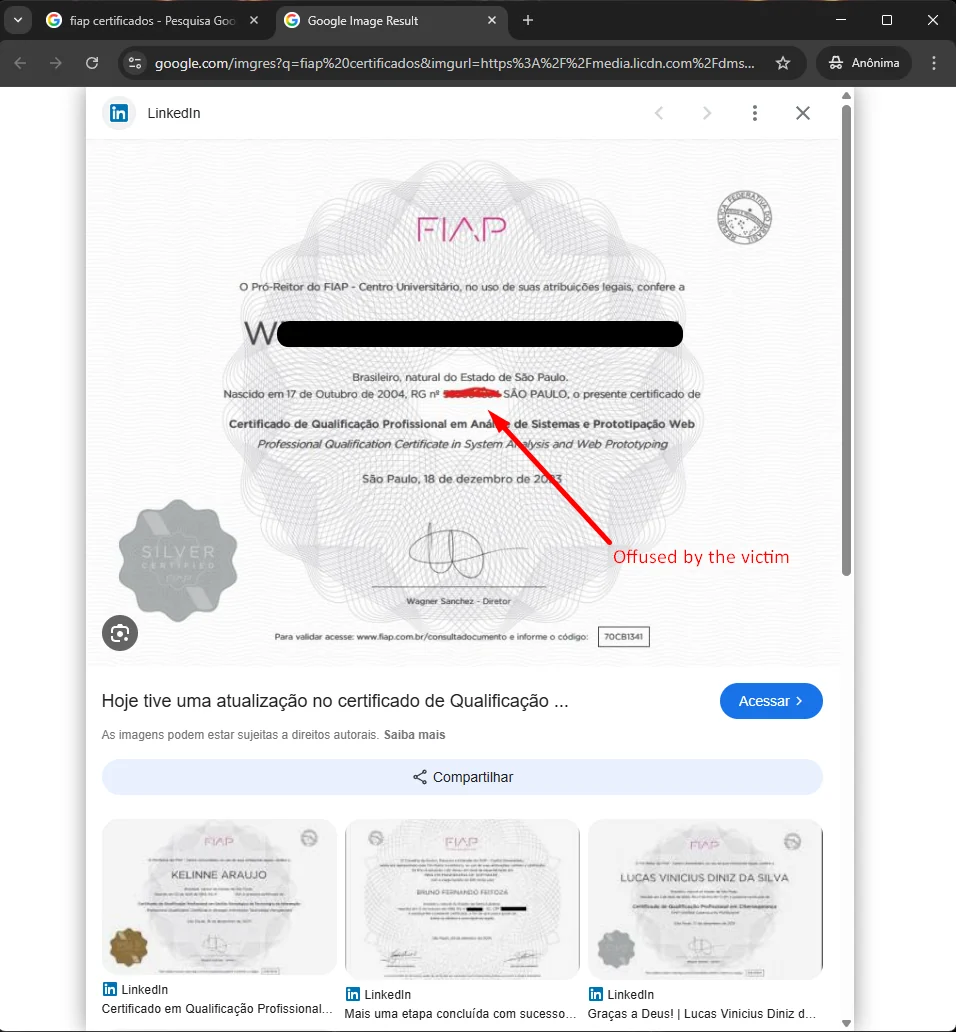 rrespxwnss/cve-2026-36374
Demonstrates an unauthenticated enumeration vulnerability in a public certificate lookup endpoint, exposing personal data such as CPF and RG.…
 enriquenegri-cyberlaw/boa-cve-2009-4496-analysis
Defensive analysis of CVE-2009-4496 in Boa 0.94.14rc21, including source-code review, patch analysis, severity assessment, and ethical scope.
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 rxerium/responsible-disclosure-email-gathering
A workflow to gather responsible disclosure emails from a given host(s).
 zavikhttak/follina-msdt-threat-investigation
🔵 Threat analysis writeup for Follina (CVE-2022-30190) — Microsoft MSDT RCE zero-day exploited in the wild. Covers static analysis, VirusTotal,…
 projectdiscovery/vulnx
Modern CLI for exploring vulnerability data with powerful search, filtering, and analysis capabilities.
 tanasescualexandrugabriel/vulnerability-assessment-and-osint-cve-2012-1823
This repository documents the process of identifying, analyzing, and gathering Open Source Intelligence (OSINT) on a specific security vulnerability…
 mohwahyudi/cve-2021-41773
Python script that uses Shodan to discover Apache HTTP Server 2.4.49 instances vulnerable to CVE-2021-41773 path traversal and file disclosure.
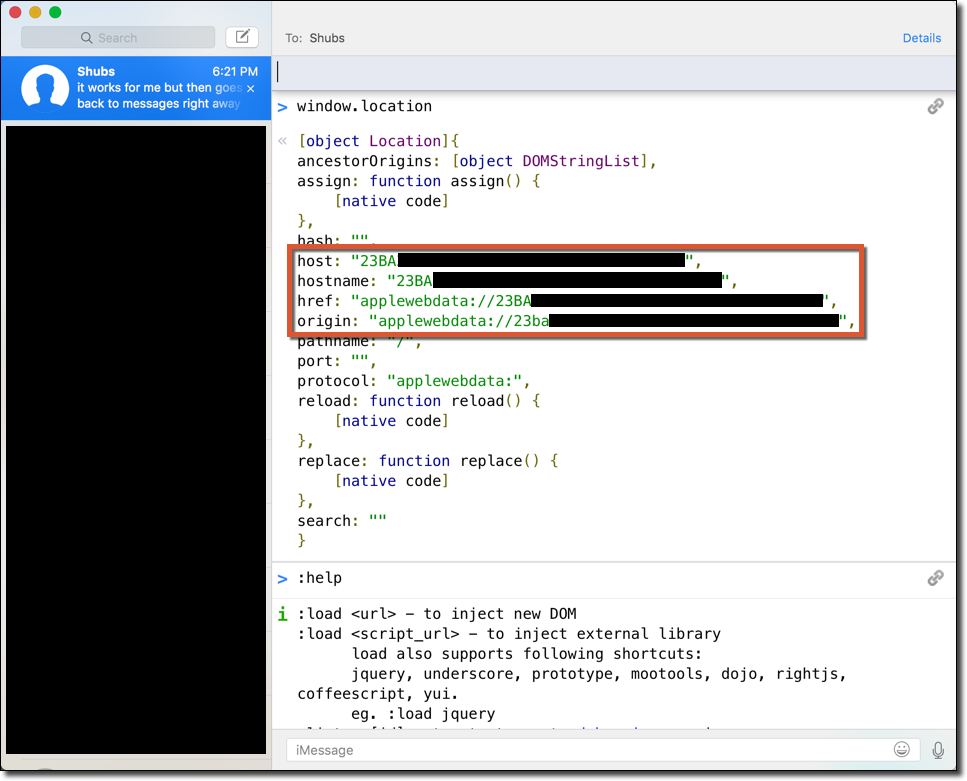 moloch--/cve-2016-1764
Extraction of iMessage Data via XSS
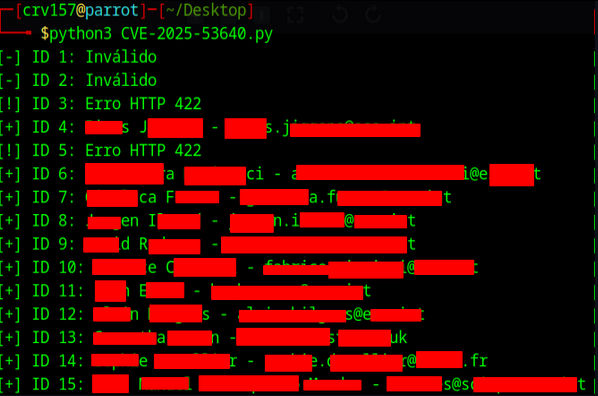 rafaelcorvino1/cve-2025-53640
Broken Object Level Authorization (BOLA) in CERN's Indico leads to authenticated user enumeration.
 cyberbibs/soc274---palo-alto-networks-pan-os-command-injection-vulnerability-exploitation-cve-2024-3400-
Step-by-step SOC analyst walkthrough for investigating and remediating CVE-2024-3400 (PAN-OS command injection). Covers detection, log analysis,…
 zhazhalove/osquery_cve-2024-23443
Osqery extension HP BIOS WMI
 disk0nn3ct/maltegoheartbleed
Maltego transform to detect the OpenSSL Heartbleed vulnerability (CVE-2014-0160)
 sunny-kathuria/exploit_cve-2022-26134
CVE-2022-26134, an OGNL injection vulnerability exists that would allow an unauthenticated attacker to execute arbitrary code on a Confluence Server…
 tadash10/detect-cve-2024-0762
Detecting vulnerabilities like CVE-2024-0762, particularly in UEFI firmware, is quite challenging due to the low-level nature
 manyaigdtuw/cve-2025-68613_scanner
GUI Shodan-powered scanner to identify n8n instances exposed to CVE-2025-68613 (version range 0.211.0–1.122.0)