
qyvora-toha3ee
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
exploitationnetwork-securityosint+9
4
qyvora/qyvora-toha3eeGo-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
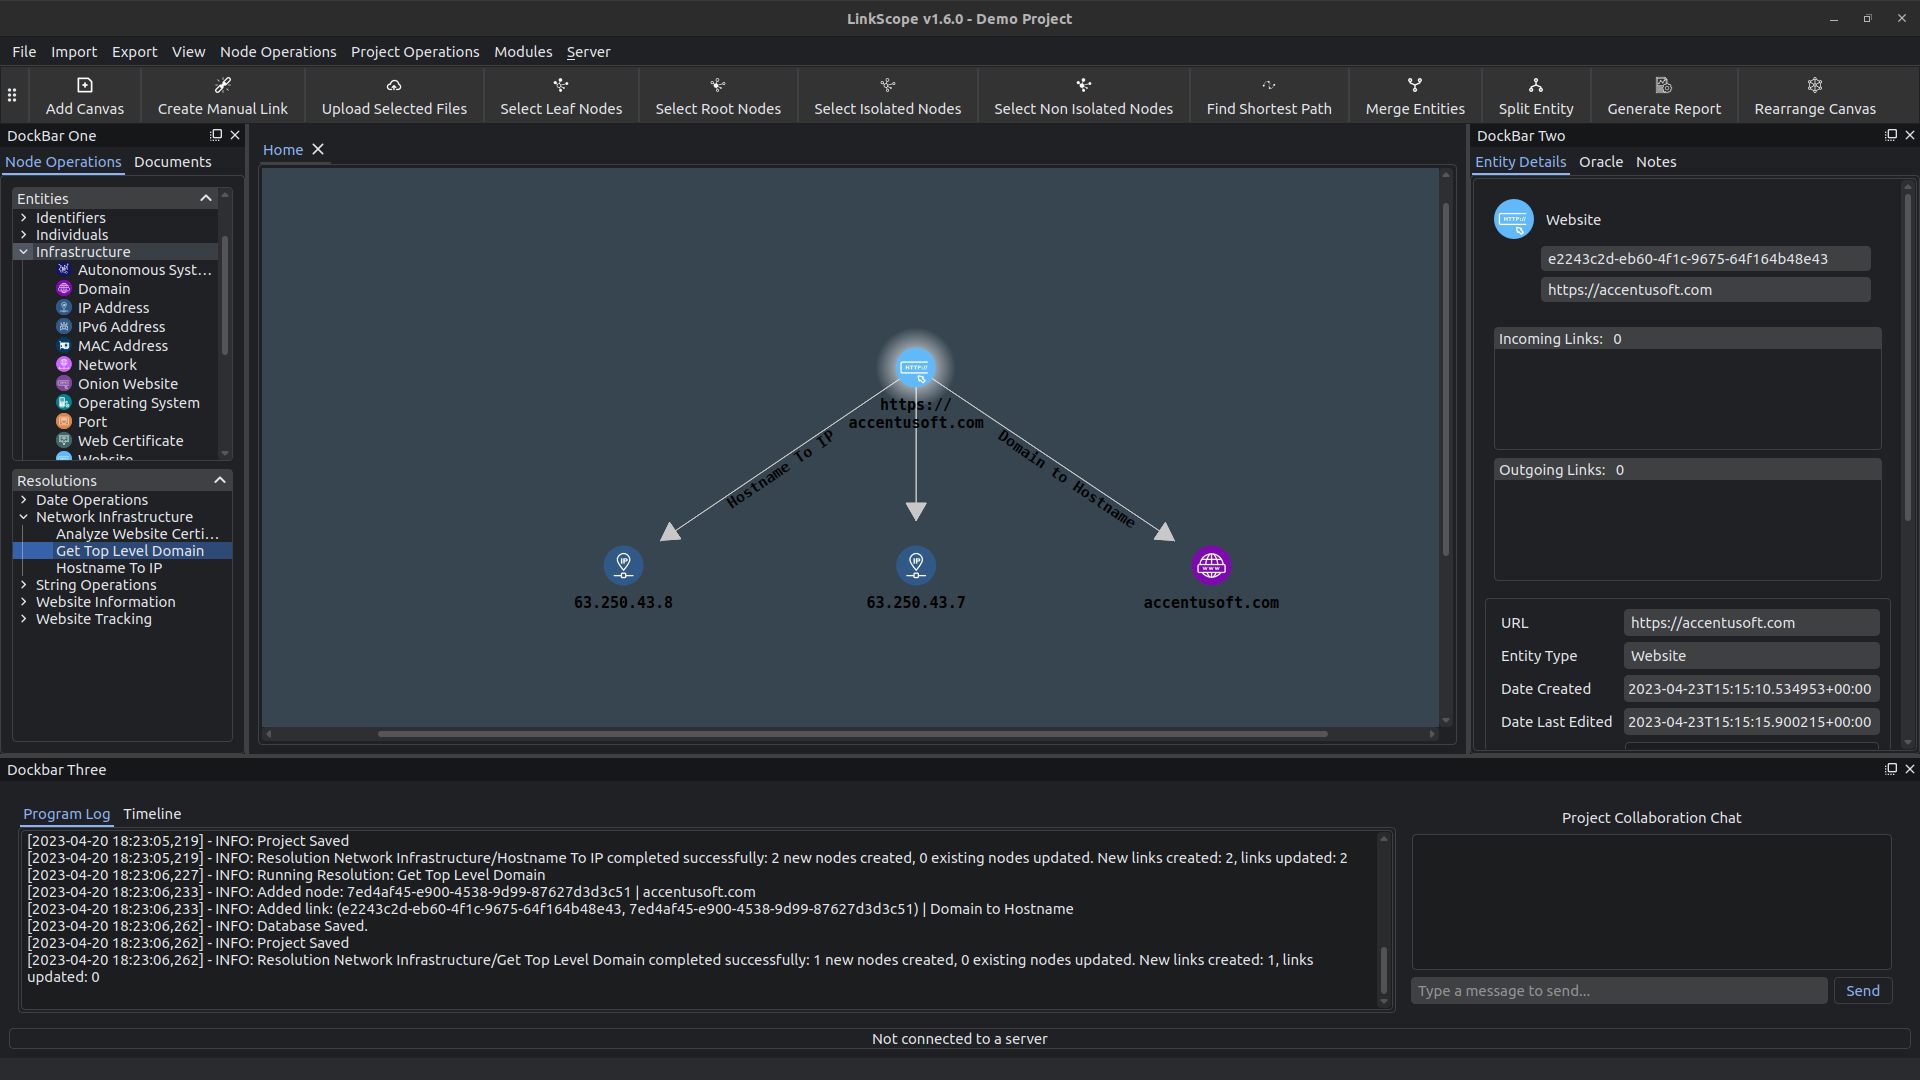 accentusoft/linkscope_client
Repository for the LinkScope Client software.
 firefart/hijagger
Checks all maintainers of all NPM and Pypi packages for hijackable packages through domain re-registration
 synacktiv/depfuzzer
Scans project dependencies for dependency confusion vulnerabilities and checks package owner email takeover risks across multiple registries (npm,…

 jenderal92/reverse_ip_multithreading1
Multithreaded reverse IP lookup tool for discovering domains hosted on the same IP address.
 cyeezy08/kimai-cve-2026-49865-poc
PoC exploits for CVE-2026-52824 (GHSA-jr9p-4h4j-6c58) — Kimai time-tracking default APP_SECRET authentication bypass affecting versions ≤ 2.57.0
 lukebob-zz/c2-pwn
Uses Shodan API to pull down C2 servers to run known exploits on them.
 staaldraad/fastfluxanalysis
Scripts to detect Fast-Flux and DGA using DNS query responses
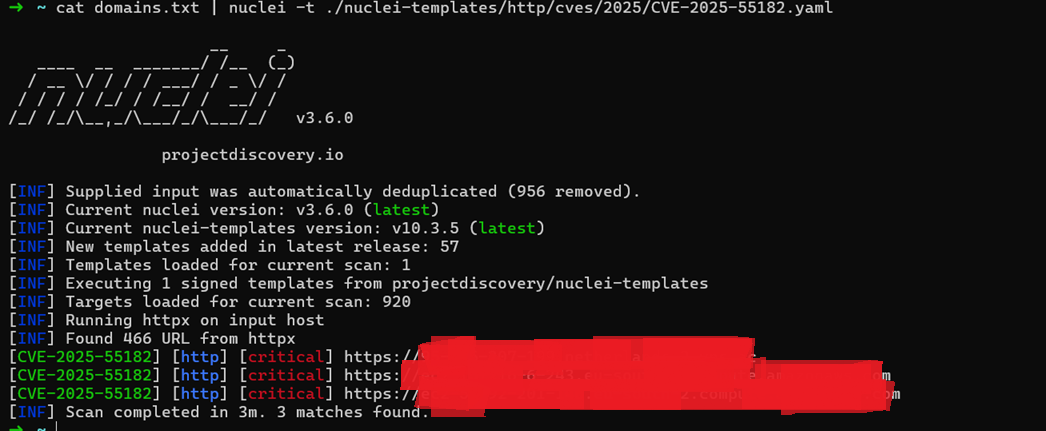 jaycelation/cve-2025-55182
PoC, Hunting React2Shell about CVE-2025-55182
 sunny-kathuria/exploit_cve-2022-26134
CVE-2022-26134, an OGNL injection vulnerability exists that would allow an unauthenticated attacker to execute arbitrary code on a Confluence Server…
 rdoix/cve-2024-21762-checker
Shodan-based scanner that discovers FortiGate SSL VPN devices and tests them for CVE-2024-21762 vulnerability, displaying organization and country…
 projectdiscovery/subfinder
Fast passive subdomain enumeration tool.
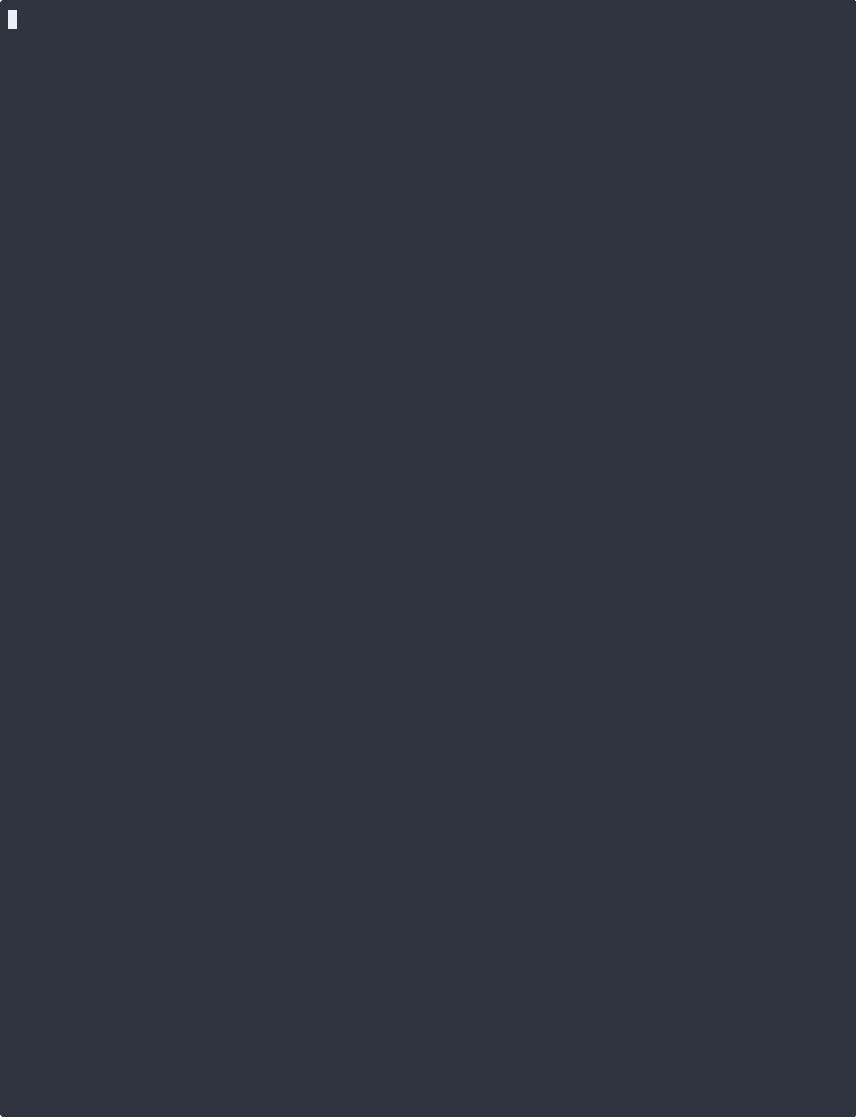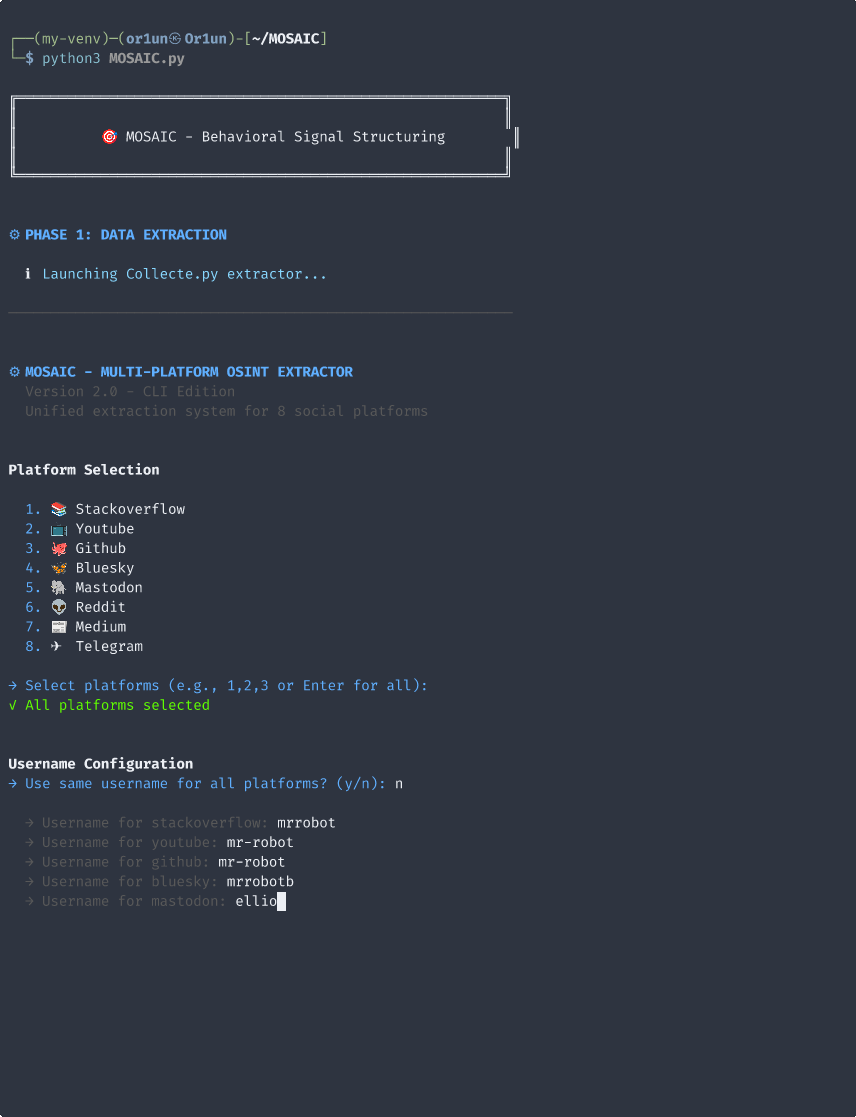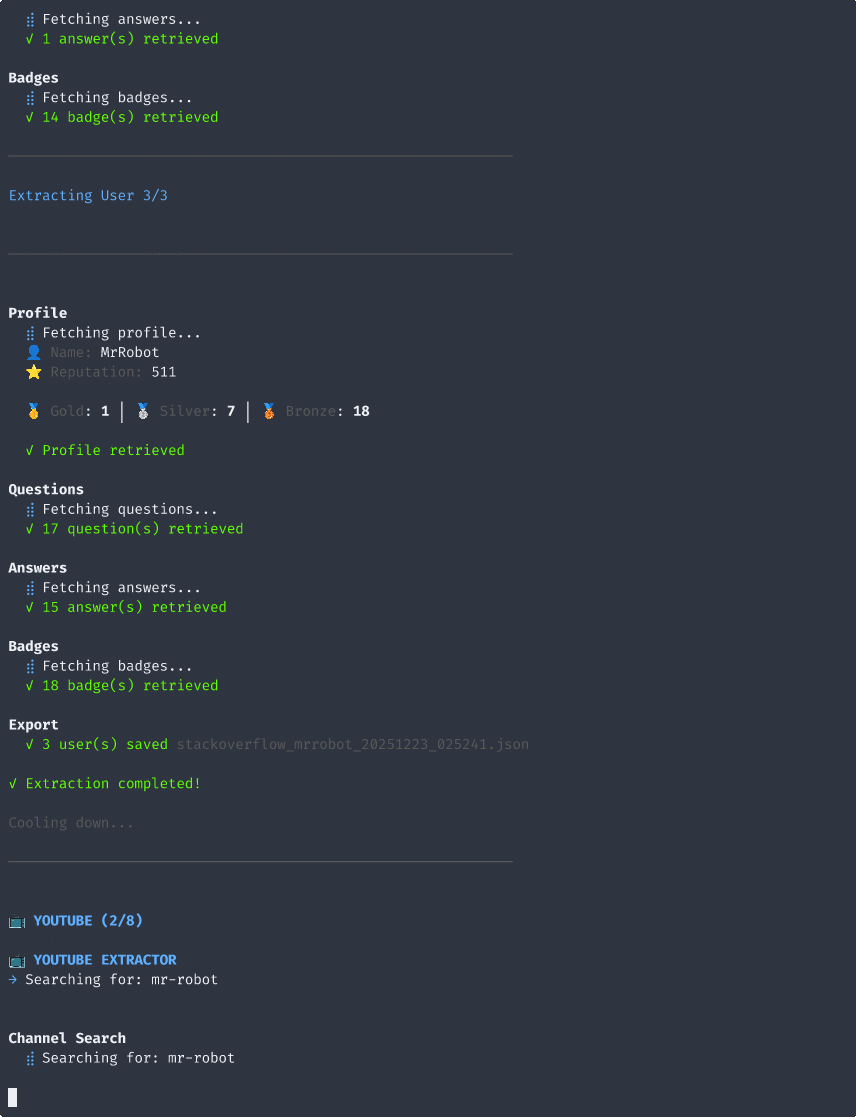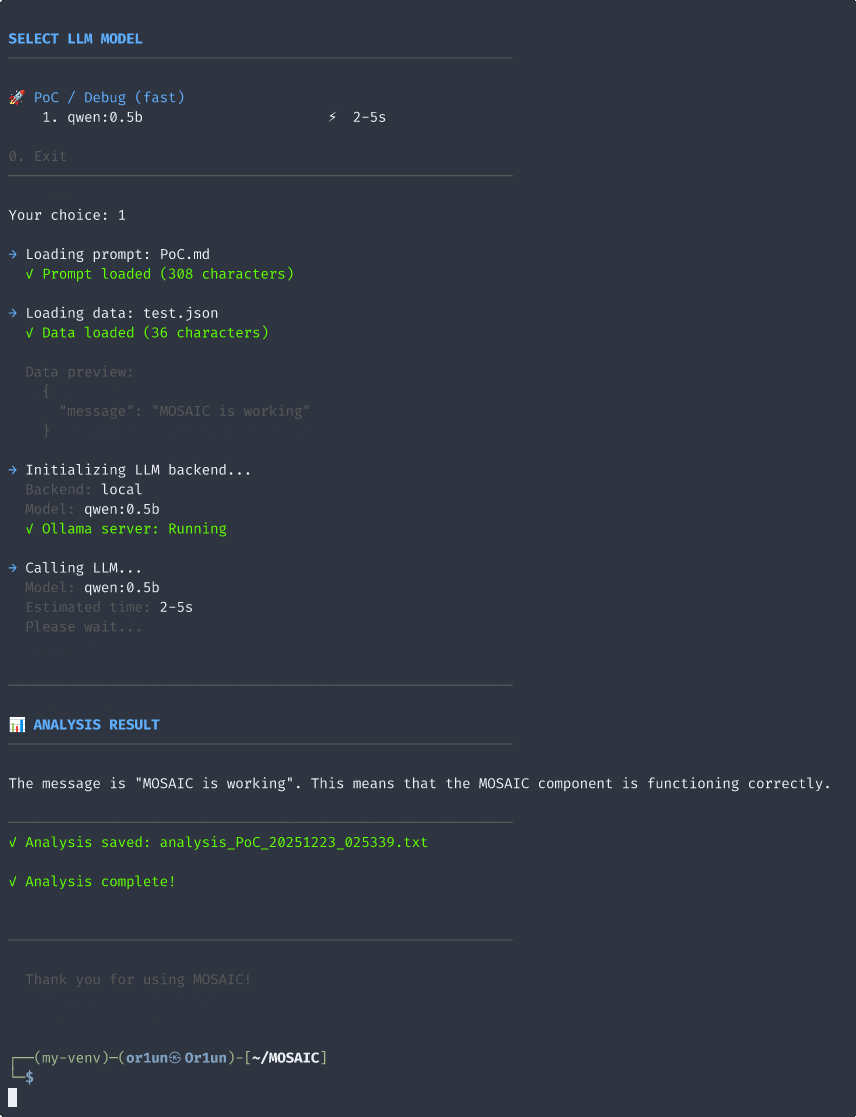 or1un/mosaic
Privacy-first behavioral intelligence framework for multi-platform analysis and sociodynamic research.
 matthewwiese/hinge-command-control-c2
A proof of concept demonstrating how to use the Hinge dating app as a C2.
 andripwn/pulse-exploit
Pulse Secure SSL VPN exploit (CVE-2019-11510) using hosts retrieved from Shodan API.
 yaelwrites/big-ass-data-broker-opt-out-list
Curated, community-maintained directory of data broker opt-out instructions to help individuals remove personal information from people-search sites…