

LBFH
 naimkowshik/lbfh
About All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
educationexploitationhash-analysis+9
725 years ago
naimkowshik/lbfhAbout All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
 ahmadhassan-bted/silentsniffer
A professional, high-fidelity de-anonymization and vulnerability diagnostic framework. Features a zero-coupling modular architecture for…
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 gmh5225/disclosure-check
Tool to identify the best mechanisms for privately disclosing a security vulnerability for a package/project.
 0xmarcio/pocindex
Search public CVE proof-of-concept exploits from GitHub, Nuclei, ExploitDB, Metasploit and Vulhub, with CVSS, EPSS and CISA KEV context.
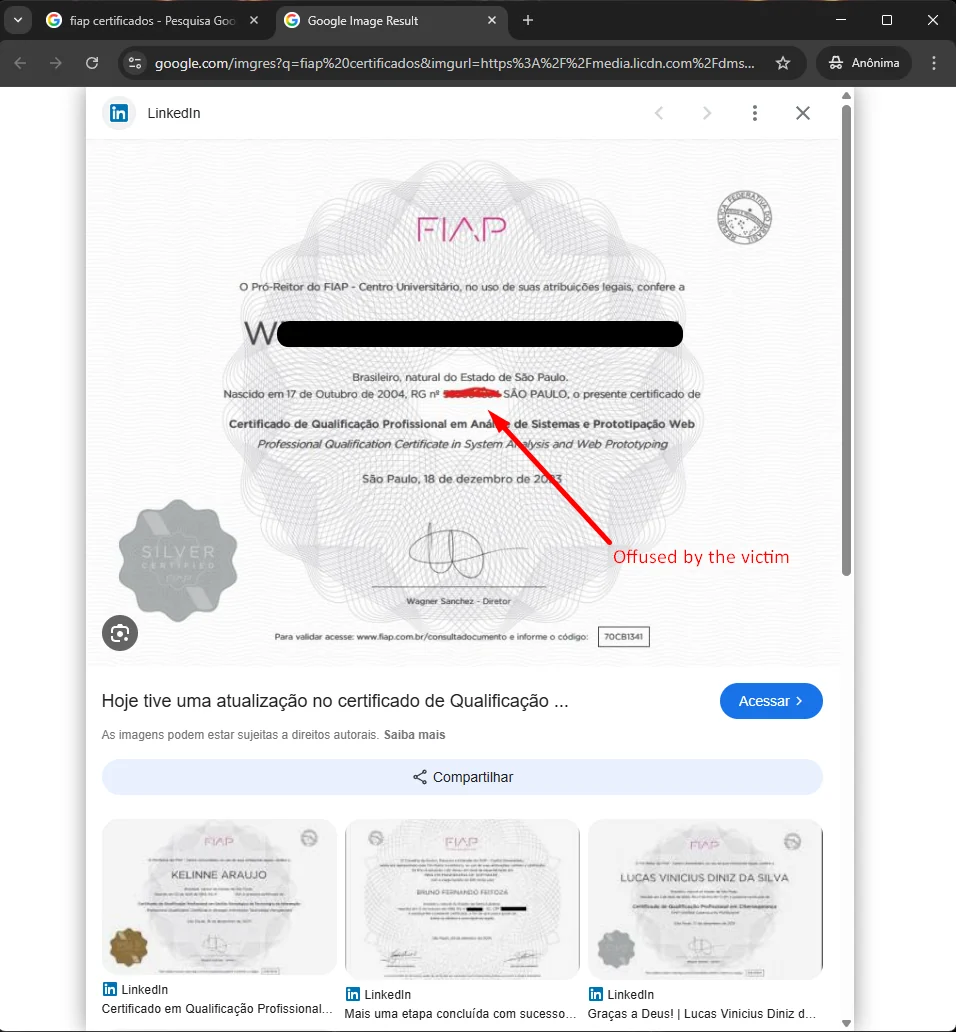 rrespxwnss/cve-2026-36374
Demonstrates an unauthenticated enumeration vulnerability in a public certificate lookup endpoint, exposing personal data such as CPF and RG.…
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 rxerium/responsible-disclosure-email-gathering
A workflow to gather responsible disclosure emails from a given host(s).
 projectdiscovery/vulnx
Modern CLI for exploring vulnerability data with powerful search, filtering, and analysis capabilities.
 tanasescualexandrugabriel/vulnerability-assessment-and-osint-cve-2012-1823
This repository documents the process of identifying, analyzing, and gathering Open Source Intelligence (OSINT) on a specific security vulnerability…
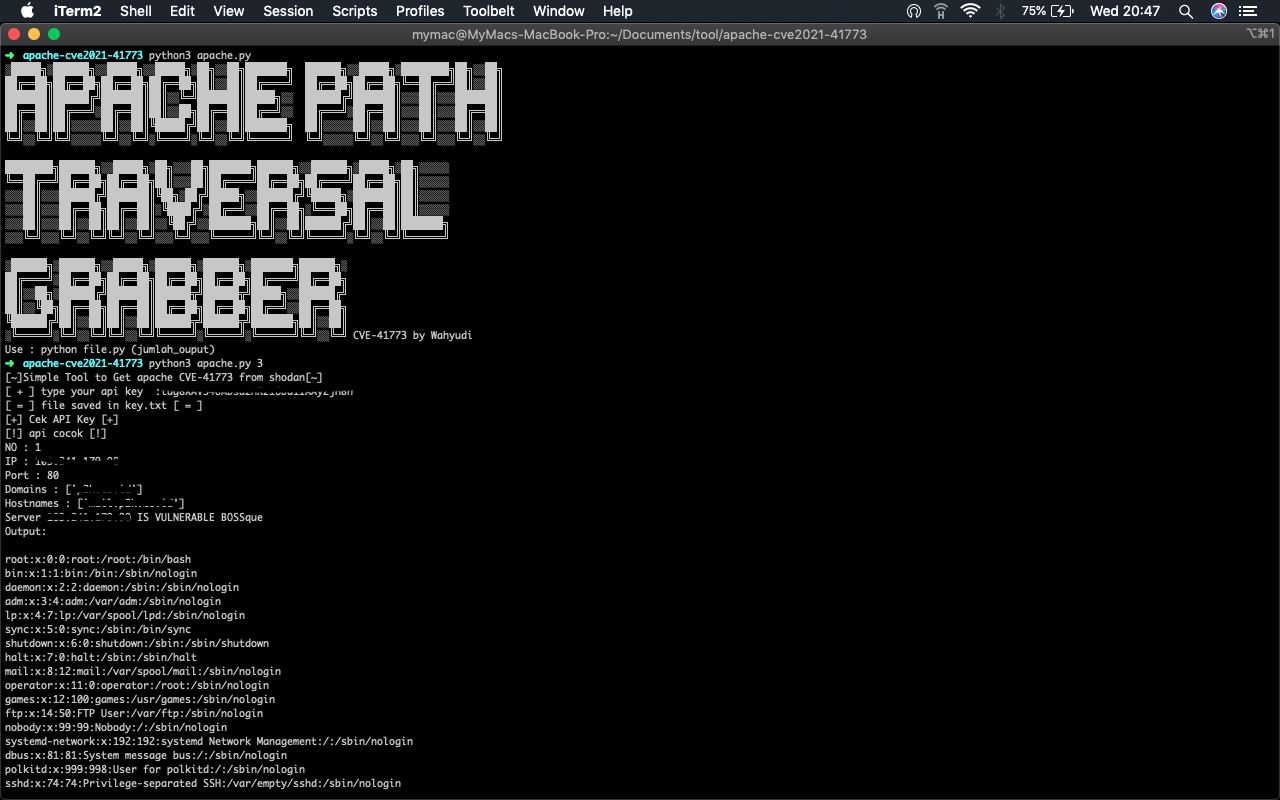 mohwahyudi/cve-2021-41773
Python script that uses Shodan to discover Apache HTTP Server 2.4.49 instances vulnerable to CVE-2021-41773 path traversal and file disclosure.
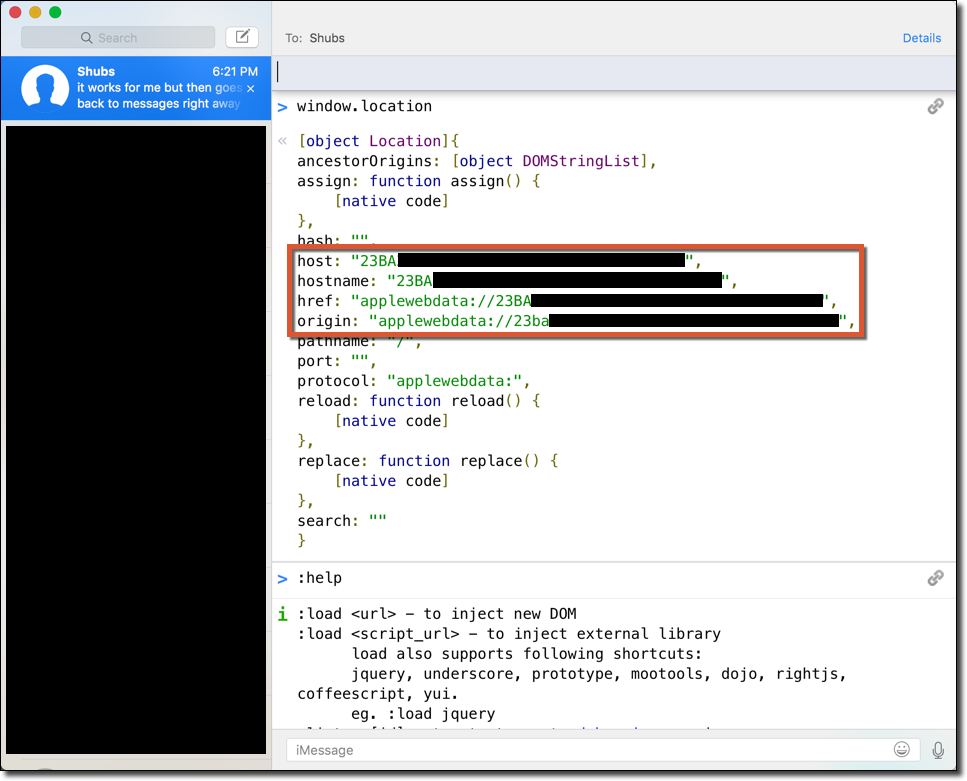 moloch--/cve-2016-1764
Extraction of iMessage Data via XSS
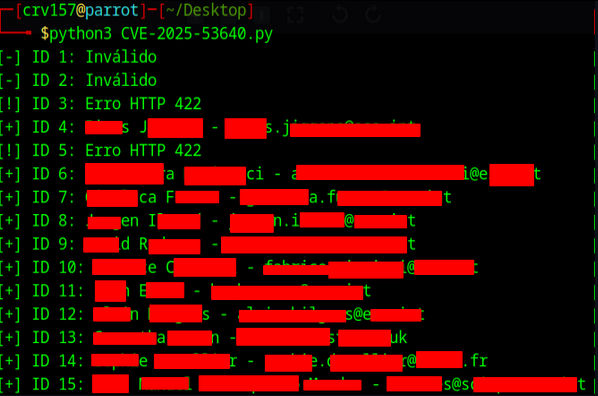 rafaelcorvino1/cve-2025-53640
Broken Object Level Authorization (BOLA) in CERN's Indico leads to authenticated user enumeration.
 cyberbibs/soc274---palo-alto-networks-pan-os-command-injection-vulnerability-exploitation-cve-2024-3400-
Step-by-step SOC analyst walkthrough for investigating and remediating CVE-2024-3400 (PAN-OS command injection). Covers detection, log analysis,…
 zhazhalove/osquery_cve-2024-23443
Osqery extension HP BIOS WMI
 disk0nn3ct/maltegoheartbleed
Maltego transform to detect the OpenSSL Heartbleed vulnerability (CVE-2014-0160)
 sunny-kathuria/exploit_cve-2022-26134
CVE-2022-26134, an OGNL injection vulnerability exists that would allow an unauthenticated attacker to execute arbitrary code on a Confluence Server…
 manyaigdtuw/cve-2025-68613_scanner
GUI Shodan-powered scanner to identify n8n instances exposed to CVE-2025-68613 (version range 0.211.0–1.122.0)