
OmniSec-Hex
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
ai-securitybinary-analysisfuzzing+9
1
vighnesh91/omnisec-hexBrowser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
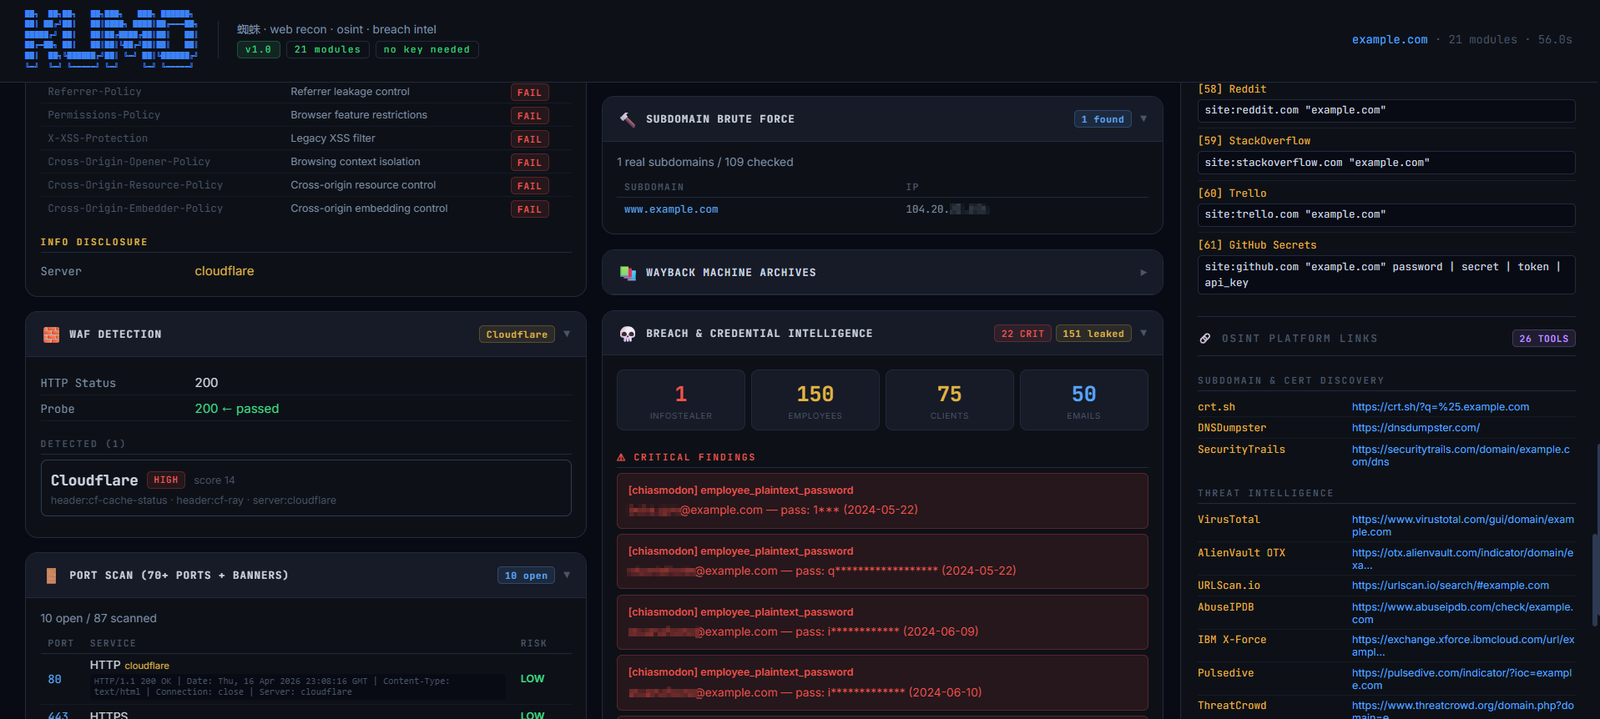 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 badchars/darknet-mcp-server
66-tool MCP server for dark web intelligence — breach data, ransomware tracking, Tor .onion access, malware analysis, blockchain intel, exploit…
 svdwi/bluebox
Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
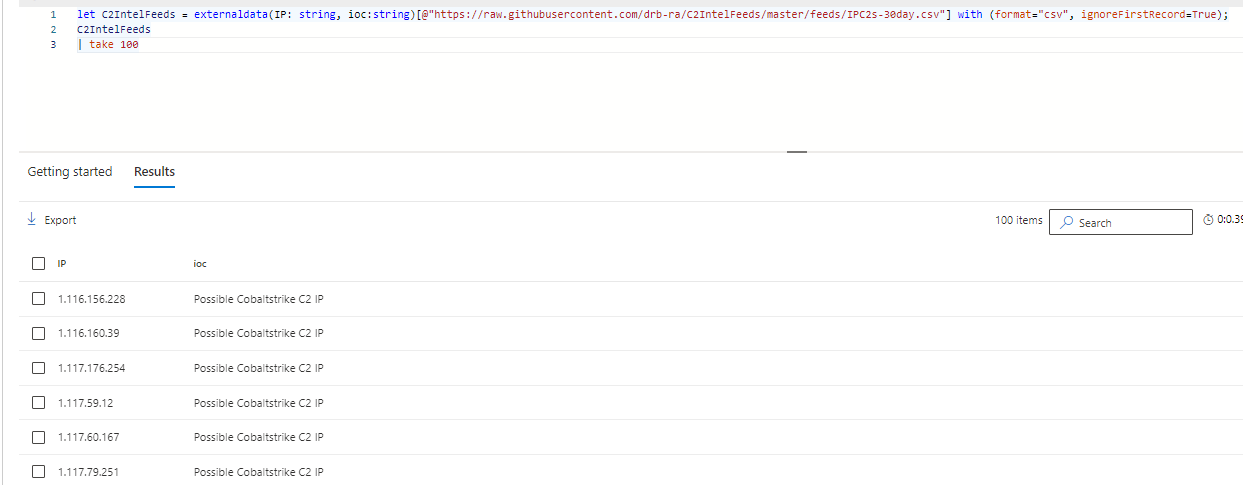 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
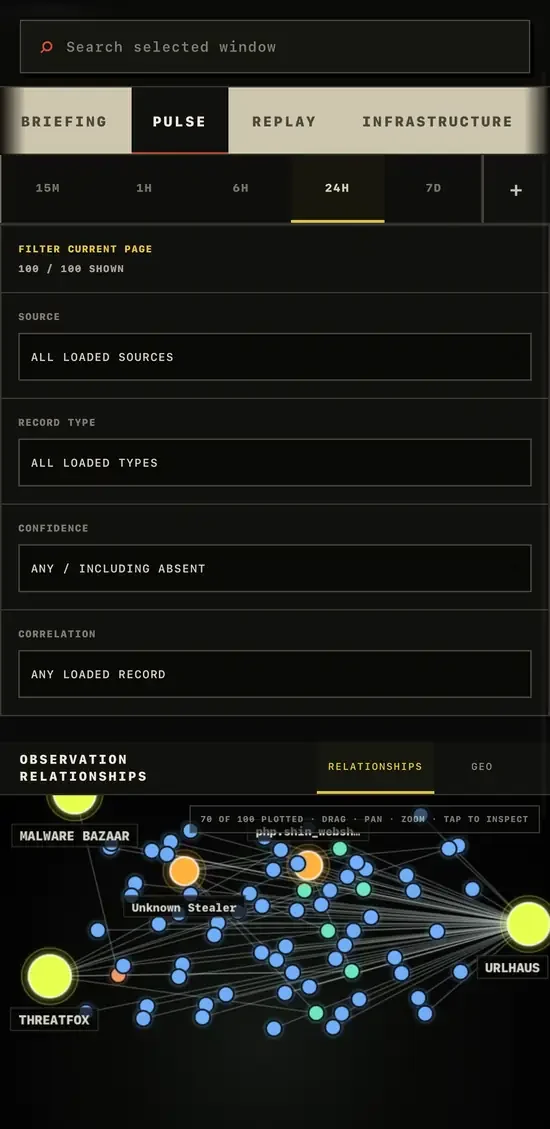
 gnomeman/badbanana-threat-observatory
Threat intel observatory aggregating CISA KEV, ThreatFox, URLhaus, and MalwareBazaar feeds with search, change tracking, and STIX/CSV/JSONL export.
 ph4l4nx/ctf-s-tools
Repository to index useful tools for CTF's
 hslatman/awesome-threat-intelligence
Curated directory of threat intelligence sources, feeds, frameworks, tools, and research for SOC/CTI teams—covering IOCs, STIX/TAXII formats, and…
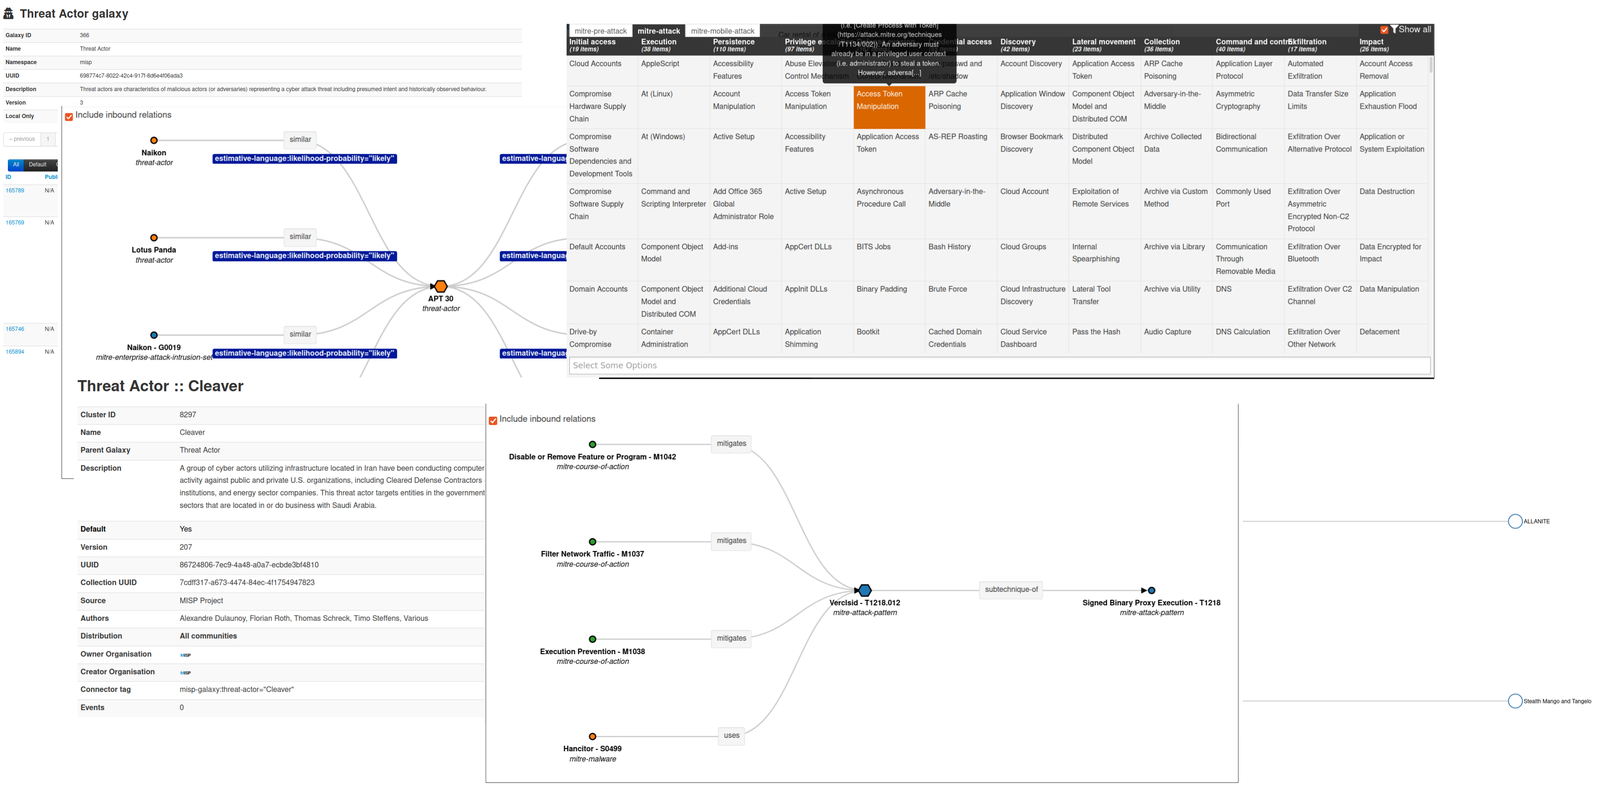 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
 enriquenegri-cyberlaw/boa-cve-2009-4496-analysis
Defensive analysis of CVE-2009-4496 in Boa 0.94.14rc21, including source-code review, patch analysis, severity assessment, and ethical scope.
 olivierlaflamme/cheatsheet-god
Penetration Testing Reference Bank - OSCP / PTP & PTX Cheatsheet
 vxunderground/threatintelligencediscordbot
Gets updates from various clearnet domains and ransomware threat actor domains
 3xp0rt/lockbit-tattoo
Structured OSINT dataset of LockBit ransomware-linked identities, including usernames, IDs, join dates, Bitcoin addresses, and media artifacts for…
 strangerealintel/eternalliberty
Curated repository of threat actor aliases and naming schemes used by major threat intelligence vendors, enabling cross-vendor search, attribution,…
 ransomlook/ransomlook
Yet another Ransomware gang tracker
 inquest/python-inquestlabs
A Pythonic interface and command line tool for interacting with the InQuest Labs API.
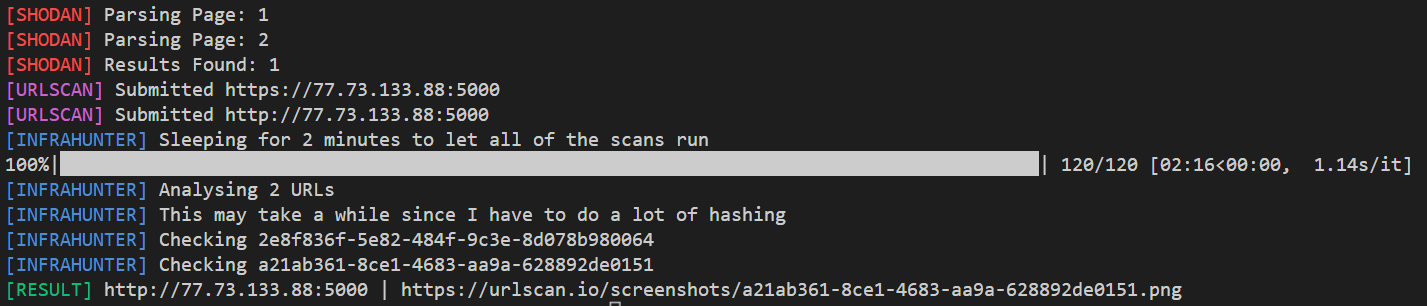 montysecurity/infrahunter
Actively hunt for attacker infrastructure by filtering Shodan results with URLScan data.