
fyp
 talha1112/fyp
Desktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…
authenticationexploitationnetwork-security+4
talha1112/fypDesktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…
 hrsman/samba-cve-2021-44142
Python tool to check Samba servers for CVE-2021-44142 by leaking heap cookies and pointers via a single SMB connection, demonstrating exploitability.
 abacus-group-rto/legion
Legion is an open source, easy-to-use, super-extensible and semi-automated network penetration testing tool that aids in discovery, reconnaissance…
 open-flaw/cve-2026-56848
Exploit PoC for CVE-2026-56848, a Node.js HTTP/2 heap-use-after-free that allows remote unauthenticated DoS. Includes raw-socket trigger, ASan build…
 exfil0/cve-2024-55591-poc
A comprehensive all-in-one Python-based Proof of Concept script to discover and exploit a critical authentication bypass vulnerability…
 aytackalinci/cve-2024-47176
Vulnerability Scanner for CUPS: CVE-2024-47176
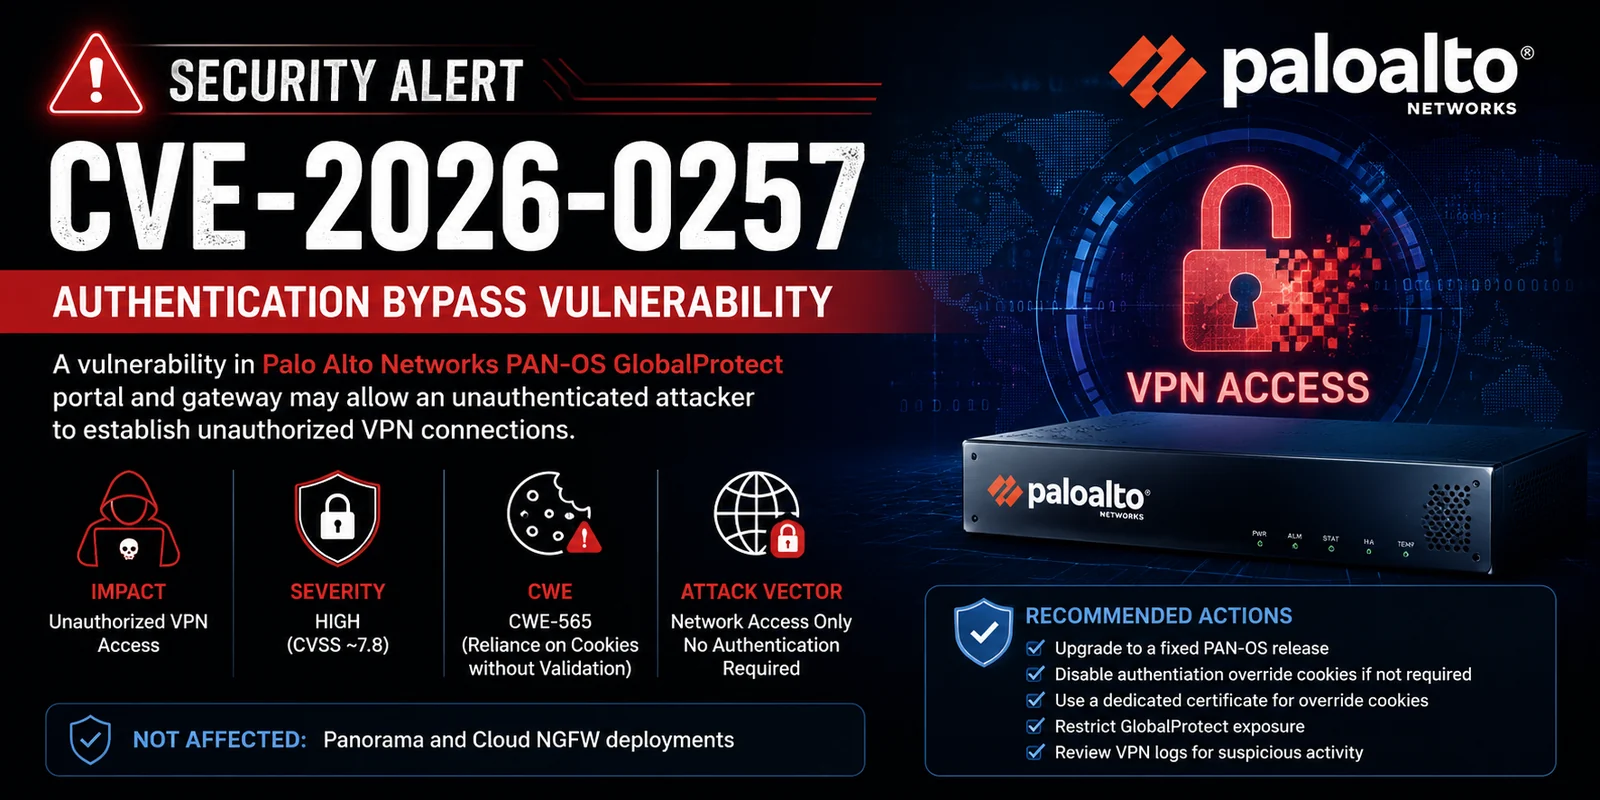 0xredash/cve-2026-0257
Python exploit for CVE-2026-0257 that forges GlobalProtect authentication override cookies to bypass PAN-OS portal and gateway authentication and…
 bishopfox/sparkplugfuzzer
Fuzzer for the Sparkplug B IIoT protocol
 arrhenius975/cve-2024-38063-exploit-refactoring
Python-based exploit for CVE-2024-38063 targeting Windows IPv6 vulnerability. Automates network interface detection, packet crafting, and…
 madhusudhan-in/cve_2023_44487-rapid_reset
A comprehensive Python testing tool for CVE-2023-44487, the HTTP/2 Rapid Reset vulnerability. This enhanced version provides granular control over…
 jsongmax/fortinet-cve-2022-40684
Go-based exploit tool for CVE-2022-40684 (Fortinet authentication bypass). Automates SSH key injection for authorized penetration testing and…
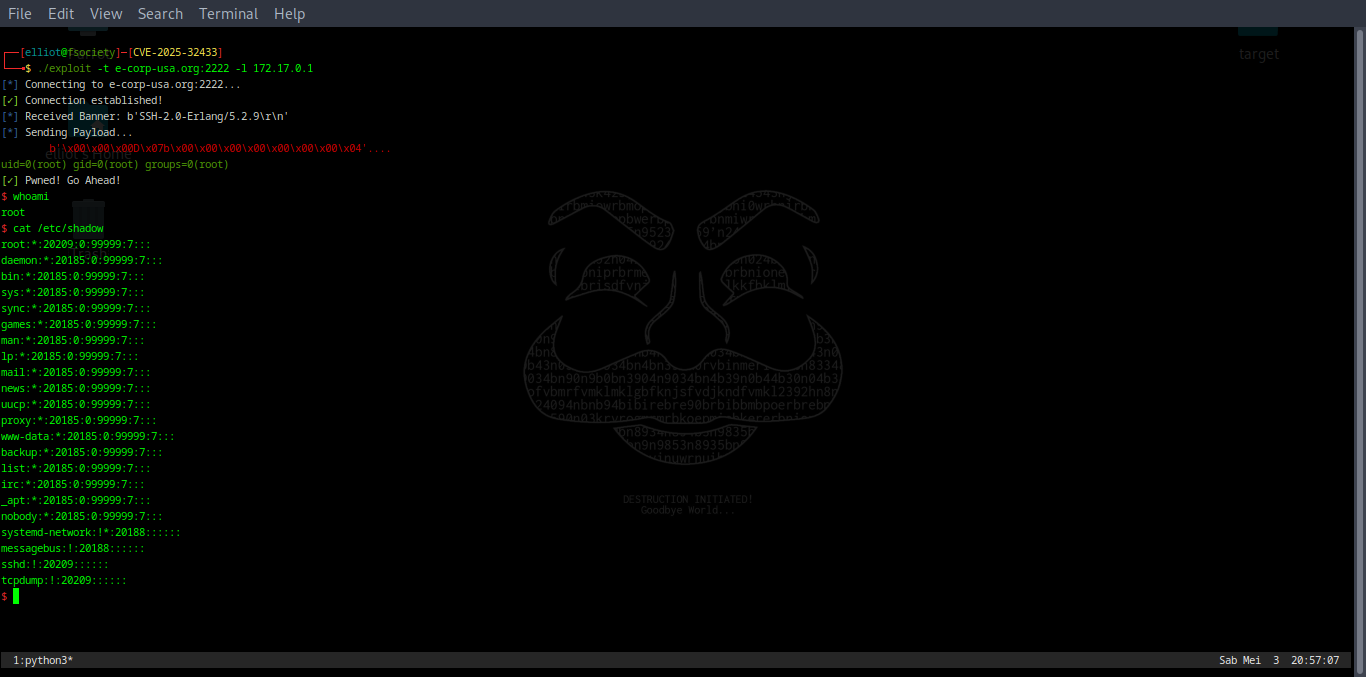 vigilante-1337/cve-2025-32433
A critical flaw has been discovered in Erlang/OTP's SSH server allows unauthenticated attackers to gain remote code execution. One malformed SSH…
 r00t-3xp10it/morpheus
Morpheus - Automating Ettercap TCP/IP (MITM-hijacking Tool)
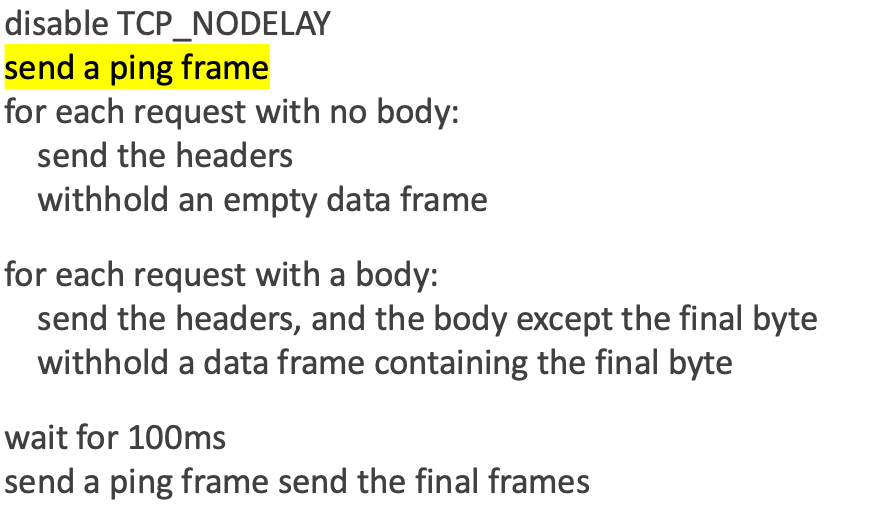 nxenon/h2spacex
HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks
 watchtowrlabs/watchtowr-vs-citrix-netscaler-cve-2026-88772
Detection artifact generator for Citrix NetScaler CVE-2026-88772 that builds a DTLS pre-auth buffer overflow payload to verify remote code execution.
 sugib3o/check-vuln-cve-2019-0708
Check vuln CVE 2019-0708
 minhpham123456789/poc-cve-2024-23113
A proof of concept for CVE 2024 23113 inspired by WatchTowr's article.
 klairmanraj/vulnerability-risk-assessment-tvra-enterprise-network
Qualitative TVRA for multi-VLAN enterprise lab scoring stored XSS and EternalBlue via CVSS v3.0 with ZAP, Nessus, and Wireshark evidence.