OVSwrap-CVE-2026-64531-Mitigation-Tool

Shell script that detects vulnerable Open vSwitch kernel modules, blocks automatic loading, removes the affected module, and verifies mitigation…

Shell script that detects vulnerable Open vSwitch kernel modules, blocks automatic loading, removes the affected module, and verifies mitigation…

Transparent proxy through Tor for Kali Linux OS

Automate stopping bad bots from accessing your server

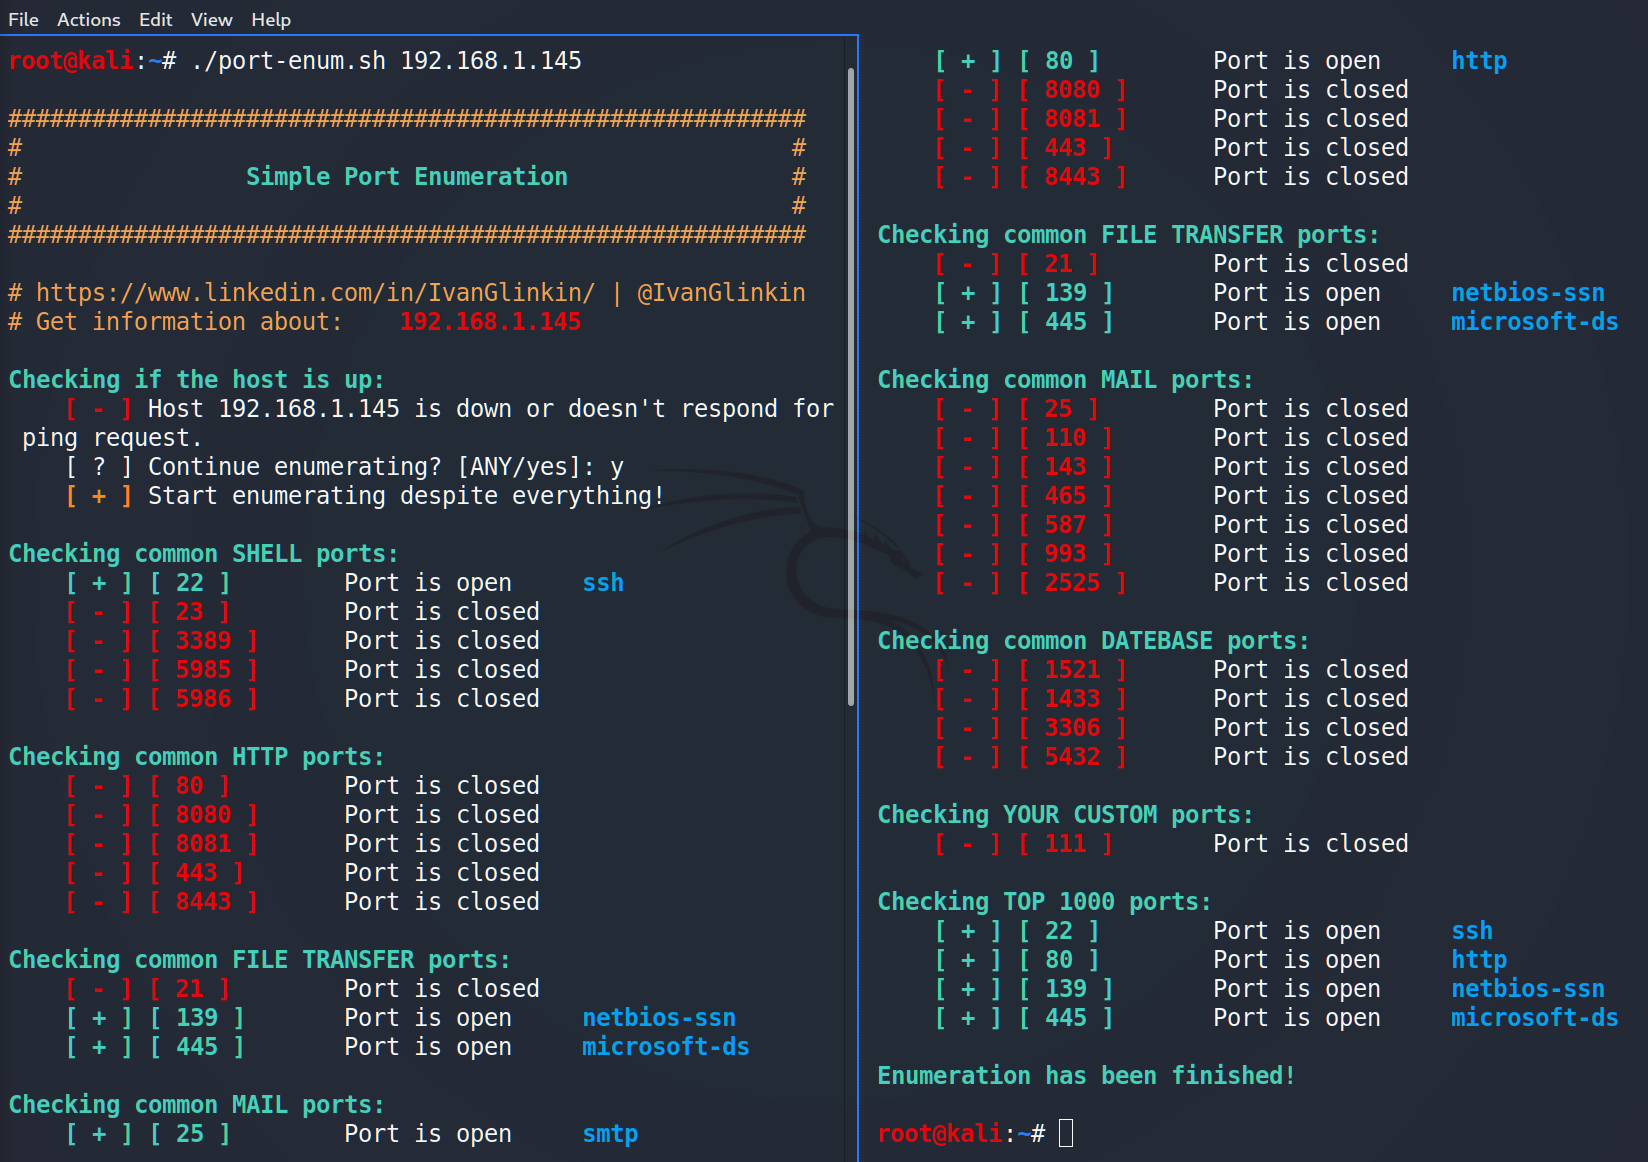
Have you ever faced with the lack of possibility of using NMap? For instance if you have reverse shell as an unprivileged user and there are no…

Basic BASH Script to Automate OpenSSL based testing for FREAK Attack (CVE-2015-0204) as advised by Akamai.


Establish secure remote access to a machine with interactive shell, file transfer, and web proxy over end-to-end encrypted peer-to-peer WebRTC, using…

Fast, secure shell protocol built on HTTP/3, QUIC, and TLS 1.3. Supports OAuth2, OpenID Connect, and classical SSH authentication with UDP port…

Netcat with automated NAT traversal, secure P2P, and advanced features for shell access, file transfer, and network proxying.

Egressbuster is a method to check egress filtering and identify if ports are allowed. If they are, you can automatically spawn a shell.

Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.

Proof-of-concept exploit for CVE-2026-24061, a critical remote authentication bypass in GNU inetutils-telnetd via crafted NEW_ENVIRON USER variable,…

Source code for a BPFDoor backdoor controller supporting TCP, UDP, ICMP, and HTTPS covert communication channels with magic packet activation,…

Modular penetration testing framework with a Metasploit-like interactive shell, pre-built CVE exploit modules, and cloud/network reconnaissance…

Python toolkit for the MikroTrick MikroTik RouterOS SSH pre-auth takeover chain: exploit.py performs rekey bypass and fd-2 policy swap for admin…

Proof-of-concept exploit for GNU Inetutils telnetd authentication bypass (CVE-2026-24061) with Docker lab setup and Go PoC. Exploits NEW-ENVIRON…

Detection and exploitation toolkit for the FreeSWITCH SIP MESSAGE command injection (CVE-2026-116779), with API execution, DNS OAST shell output,…

Python exploit for CVE-2026-76504, a Cisco Catalyst SD-WAN Manager authentication bypass via percent-encoded j_security_check, with token theft, API…