
gopassivedns
 phillipmartin/gopassivedns
Network-based passive DNS logger capturing and logging DNS queries from live traffic or pcap files, outputting JSON for integration with SIEM and…
dns-analysisinformation-gatheringnetwork-security+2
phillipmartin/gopassivednsNetwork-based passive DNS logger capturing and logging DNS queries from live traffic or pcap files, outputting JSON for integration with SIEM and…
 siddharth2440/network-detection-engine
Lightweight network intrusion detection engine capturing live traffic with libpcap. Detects SYN/ICMP floods, port scans, and signature-based web…
 basil00/tallow
Tallow - Transparent Tor for Windows
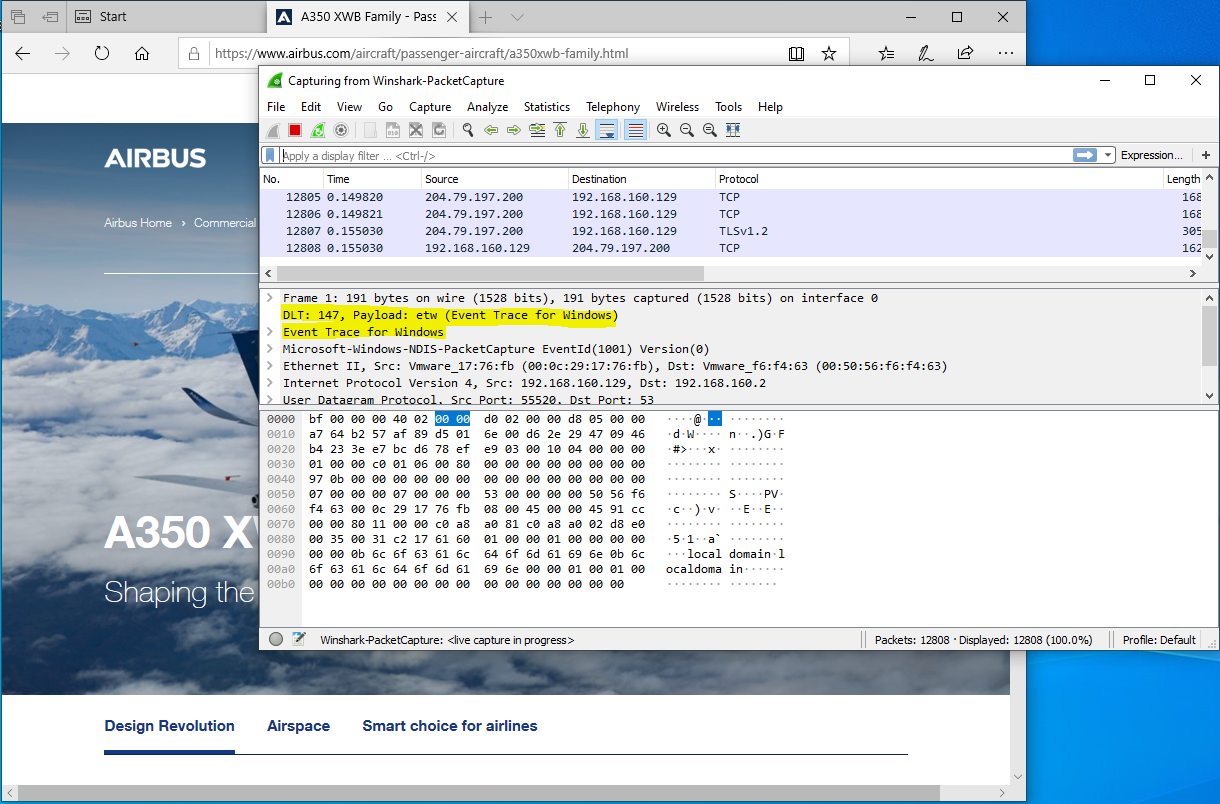 airbus-cert/winshark
A wireshark plugin to instrument ETW
 alt3kx/airdecloak-ng
My Aircrack-ng contribution with Thomas d'Otreppe
 aircrack-ng/aircrack-ng
Complete suite for WiFi network security auditing, including packet capture, injection attacks, deauthentication, fake AP creation, and WEP/WPA PSK…
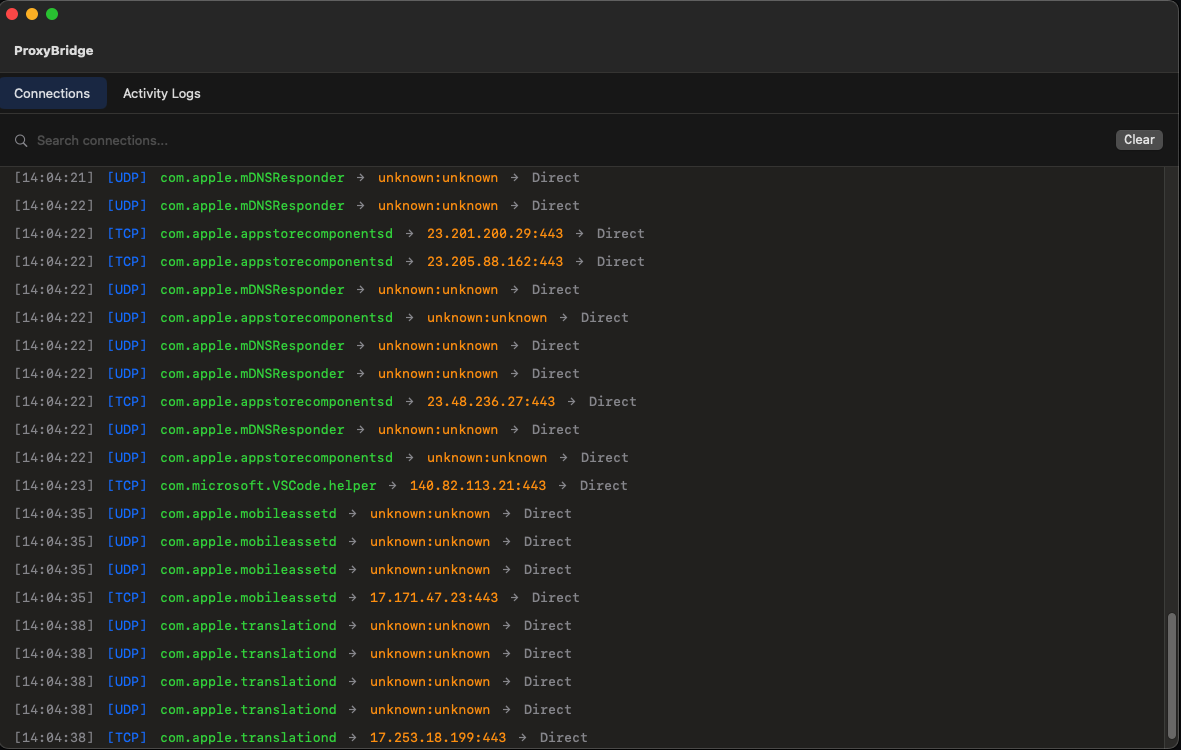 interceptsuite/proxybridge
Force Proxy to any Windows/MacOS/Linux Application TCP and UDP traffic
 nmap/npcap
Nmap Project's Windows packet capture and transmission library
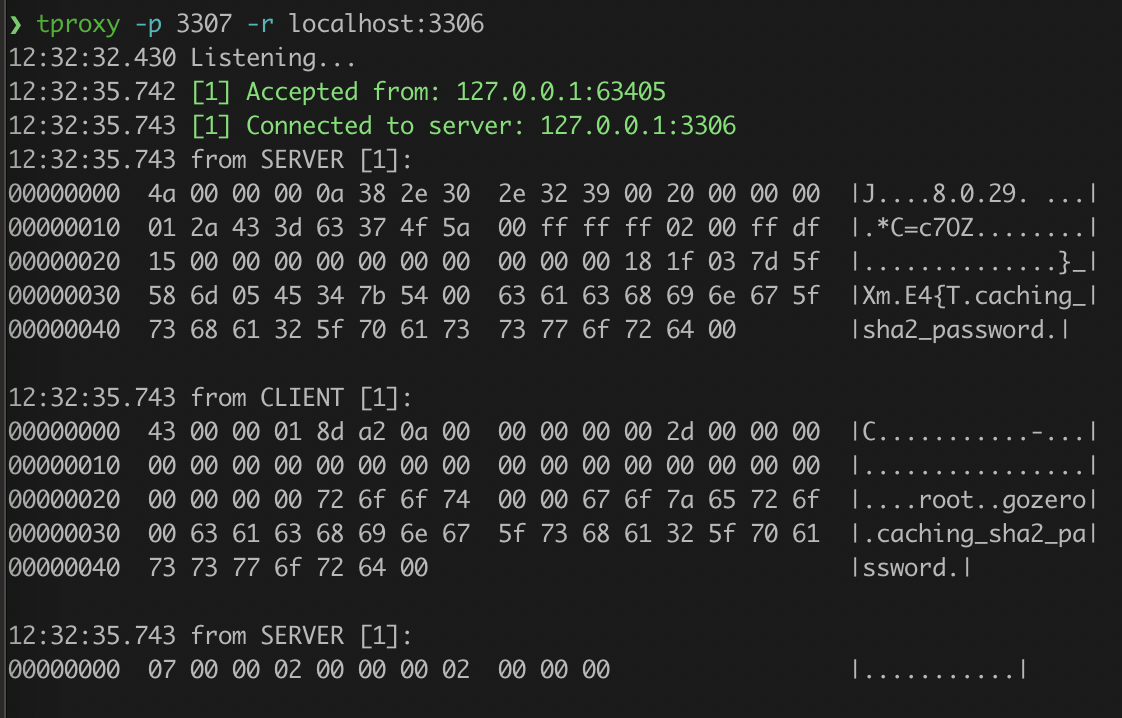 kevwan/tproxy
A cli tool to proxy and analyze TCP connections.

 caster0x00/above
Passive network security sniffer that analyzes 28 protocols (ARP, STP, OSPF, VLAN, SCADA) to detect vulnerabilities in network equipment without…
 libnet/nemesis
A command-line network packet crafting and injection utility
 nccgroup/upnp-pentest-toolkit
UPnP Pentest Toolkit for Windows
 josh0xa/espionage
A Linux Packet Sniffing Suite for Automated MiTM Attacks
 nccgroup/binproxy
BinProxy is a proxy for arbitrary TCP connections. You can define custom message formats using the BinData gem.
 mhils/honeyproxy
This project is now part of @mitmproxy.
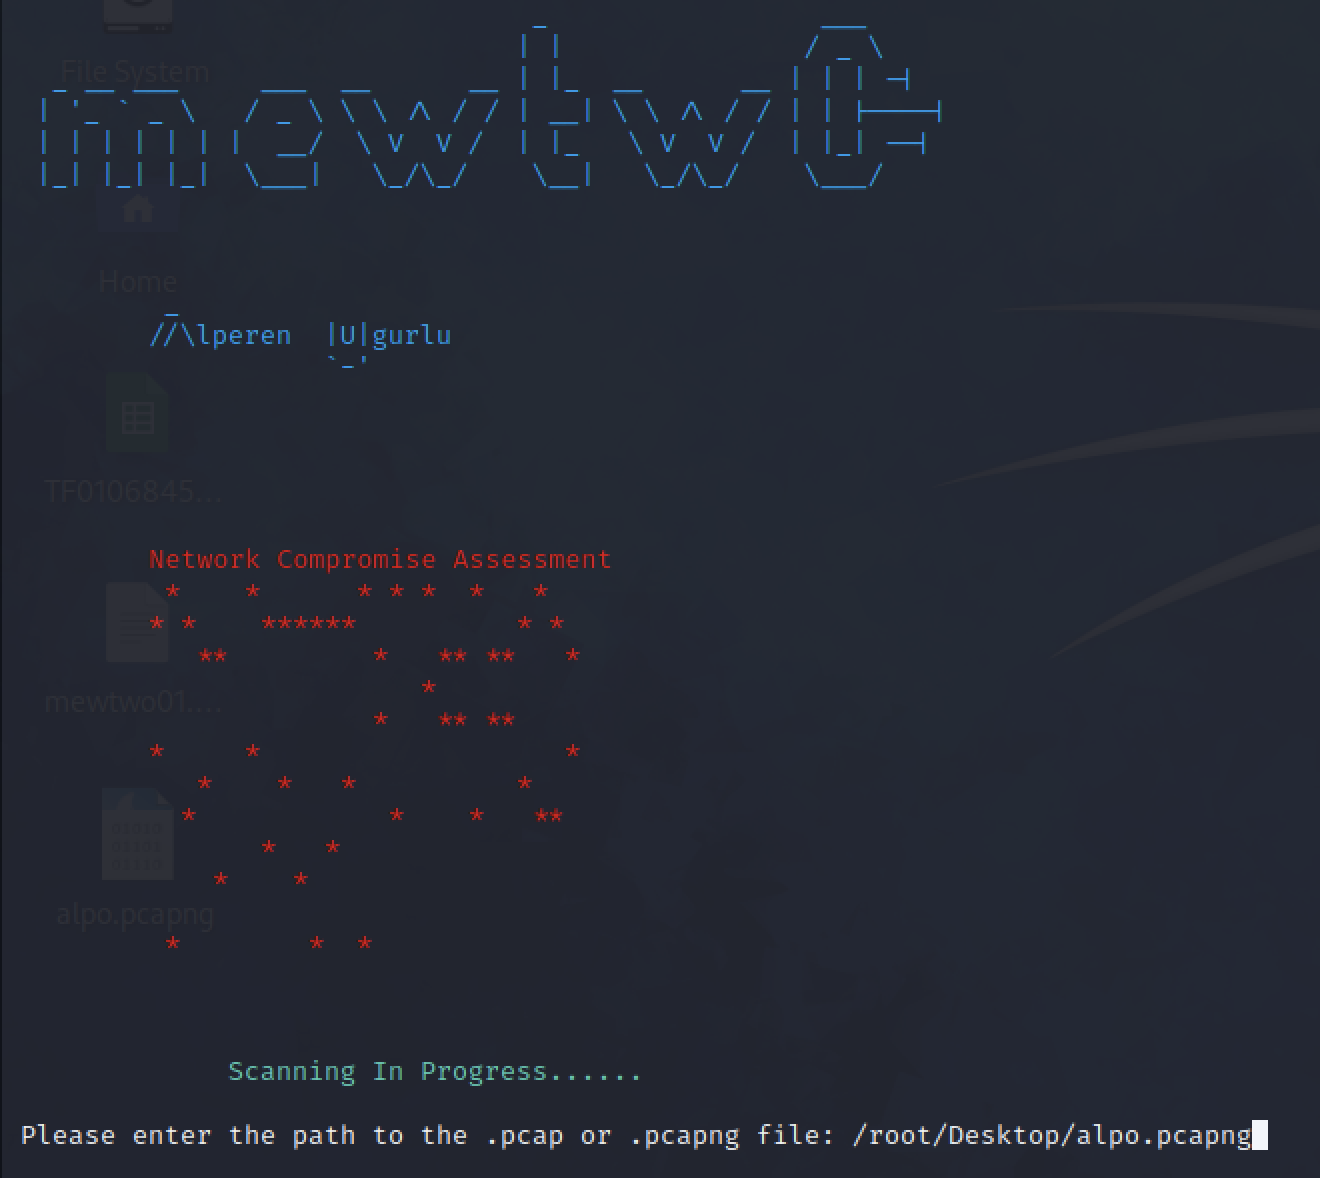 alperenugurlu/network_assessment
With Wireshark or TCPdump, you can determine whether there is harmful activity on your network traffic that you have recorded on the network you…