

Nettacker
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
api-securityapi-security-testingdynamic-code-analysis+14
5.6k
owasp/nettackerAutomated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 m0nad/hellraiser
Vulnerability scanner using Nmap for scanning and correlating found CPEs with CVEs.
 daryllundy/cve-2025-53770
Network-based vulnerability scanner for detecting systems vulnerable to CVE-2025-53770 (unsafe deserialization). Includes PowerShell and Python…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
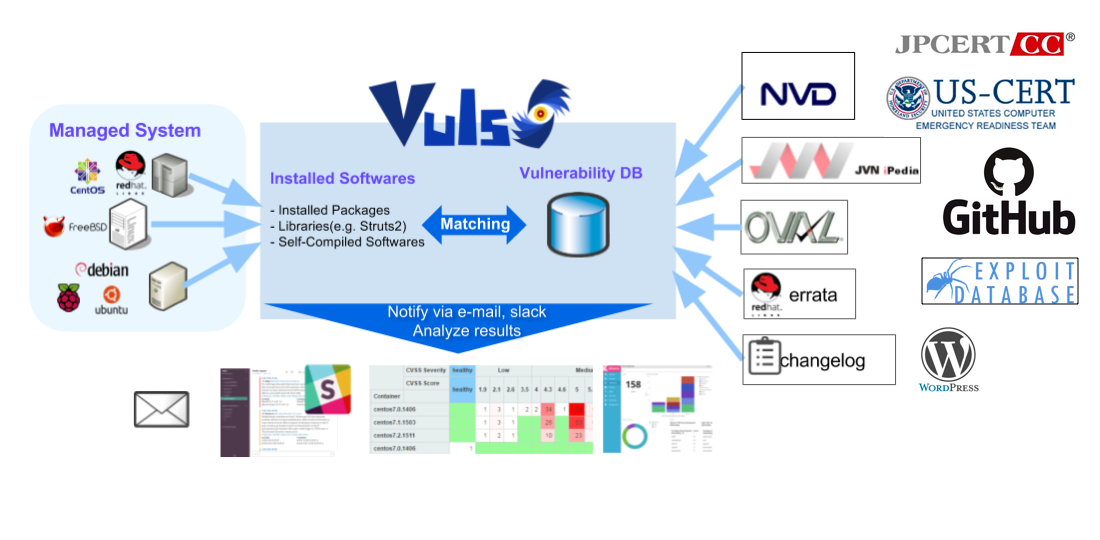 future-architect/vuls
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
 cloudflare/flan
A pretty sweet vulnerability scanner
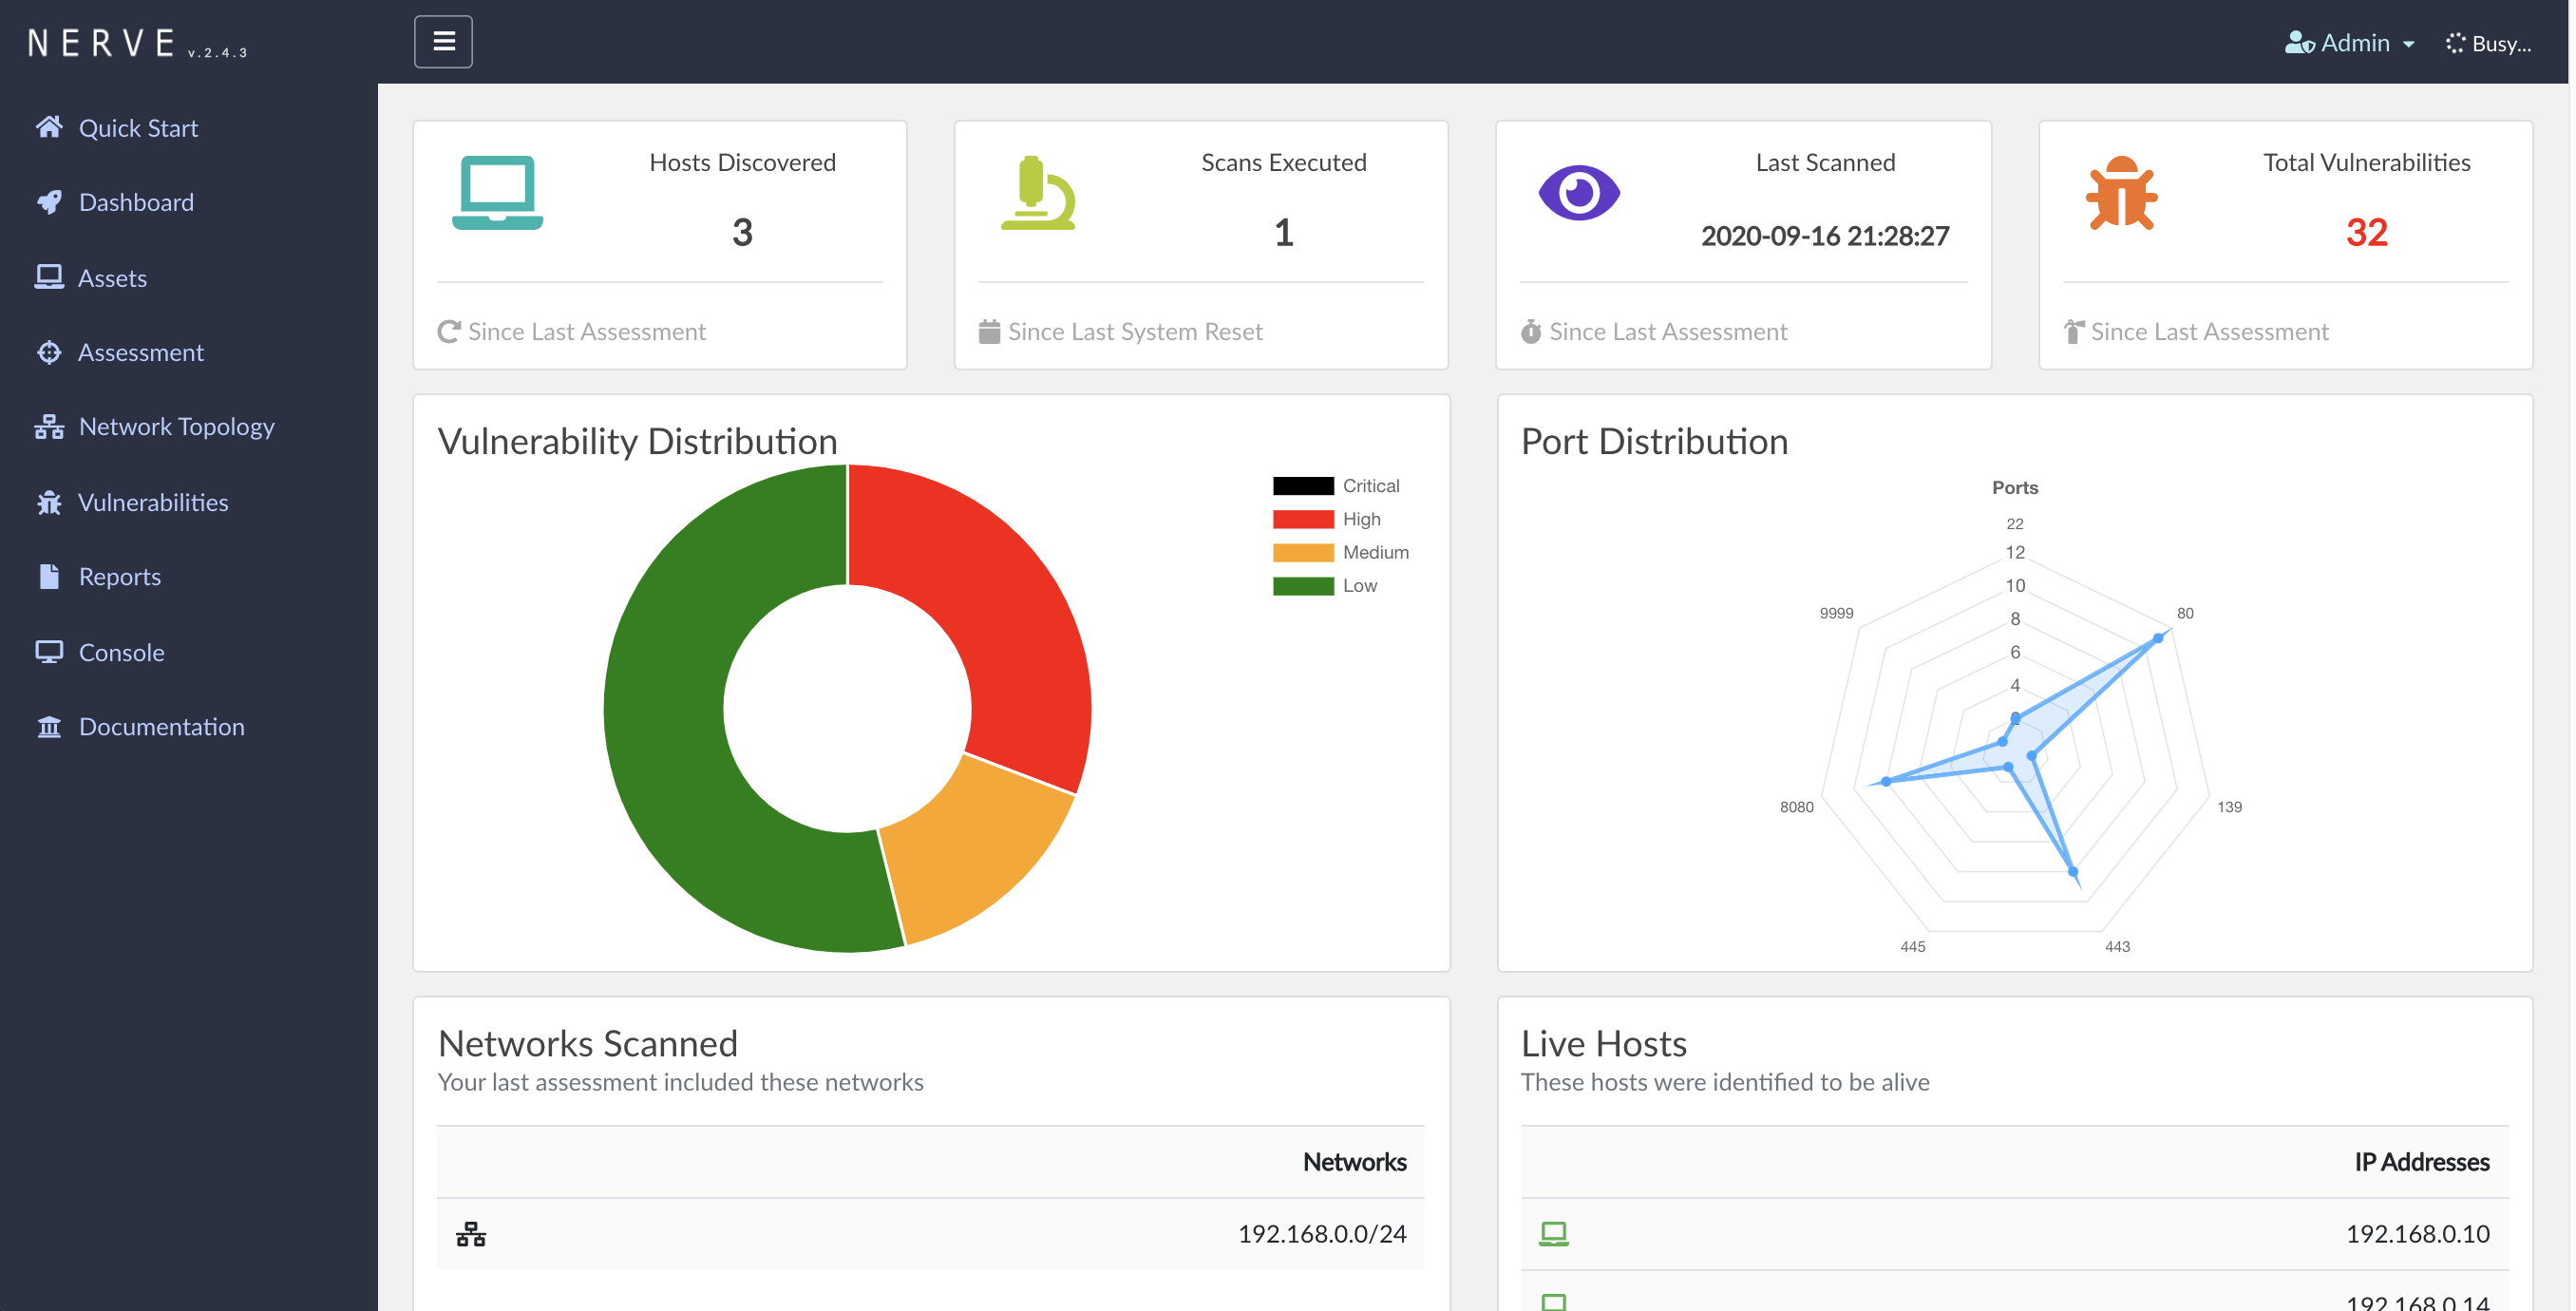 paytmlabs/nerve
NERVE Continuous Vulnerability Scanner
 xen0vas/vscan
vulnerability scanner tool using nmap and nse scripts
 1n3/massbleed
MassBleed SSL Vulnerability Scanner
 fox-it/cve-2019-1040-scanner
SMB vulnerability scanner that detects CVE-2019-1040 by sending invalid NTLM authentication packets, enabling MIC Remove relay attacks for domain…
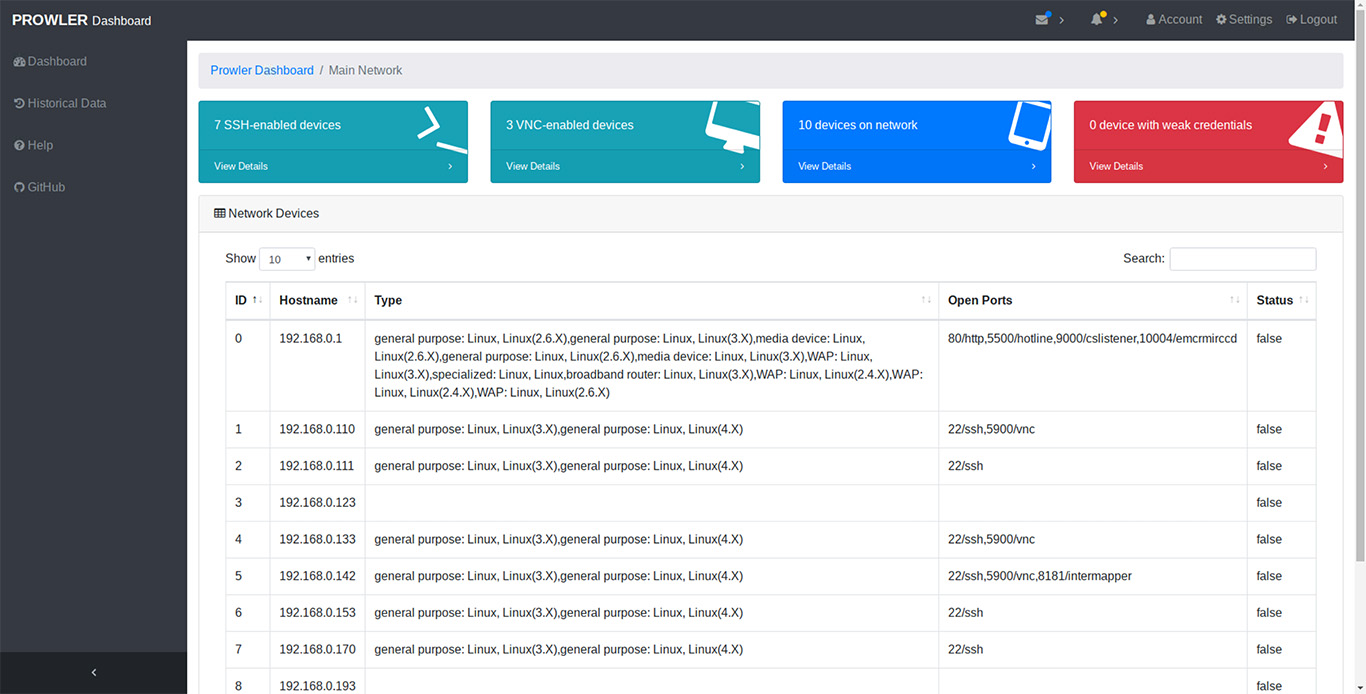 tlkh/prowler
Distributed Network Vulnerability Scanner
 offseq/threat-finder
Runtime vulnerability scanner: finds CVEs in the services actually running on a host and ranks them by network exposure.
 b34mr/zeroscan
Zeroscan is a Domain Controller vulnerability scanner, that currently includes checks for Zerologon (CVE-2020-1472), MS-PAR/MS-RPRN and SMBv2 Signing.
 bytejmp/ms09-050
Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…
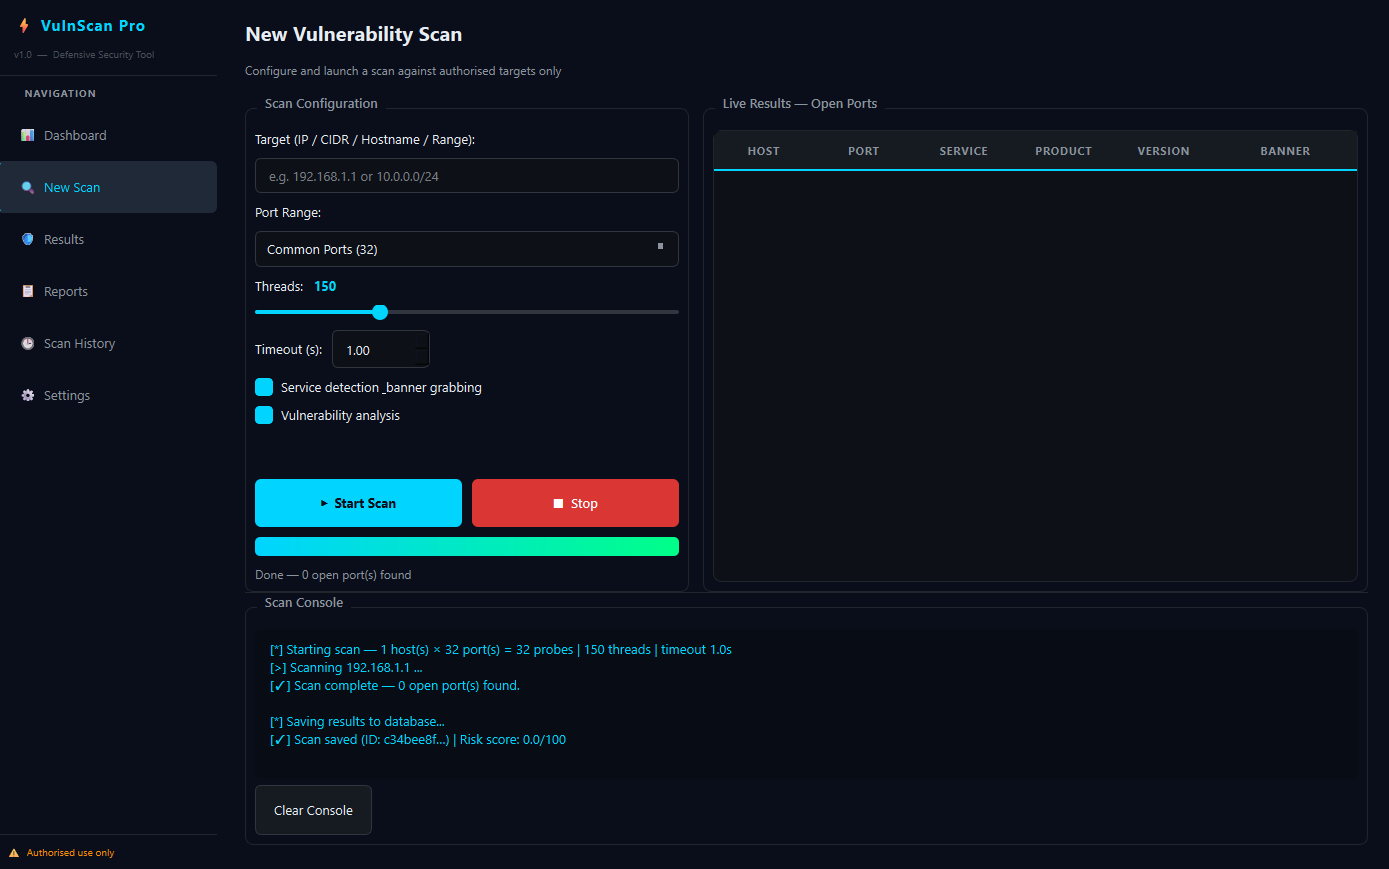 guppss/vulnscan-pro
⚡ Professional vulnerability scanner — port scanning, CVE detection, risk scoring & PDF reports in a dark PyQt6 dashboard
 liamromanis101/dead.letter-cve-2026-45185
Shell-based vulnerability scanner for CVE-2026-45185 (Dead.Letter) in Exim MTA. Detects use-after-free in GnuTLS builds, checks version, TLS library,…
 harshinsecurity/sentinelssh
SentinelSSH is an advanced, high-performance SSH vulnerability scanner written in Go. It's specifically designed to detect the CVE-2024-6387…
 cybrdude/cve-2026-1731-scanner
Passive vulnerability scanner for CVE-2026-1731 — BeyondTrust RS/PRA pre-auth RCE (CVSS 9.9). Educational & defensive use only.