
CVE-2020-15916
 geniuszly/cve-2020-15916
Proof-of-concept exploit for CVE-2020-15916, enabling unauthorized LAN configuration changes via weak authentication bypass and payload injection.
educationexploitationnetwork-security+2
3
geniuszly/cve-2020-15916Proof-of-concept exploit for CVE-2020-15916, enabling unauthorized LAN configuration changes via weak authentication bypass and payload injection.
 exbotanical/brutus
extensible exploitation framework shipped on a modular multi-tasking architecture
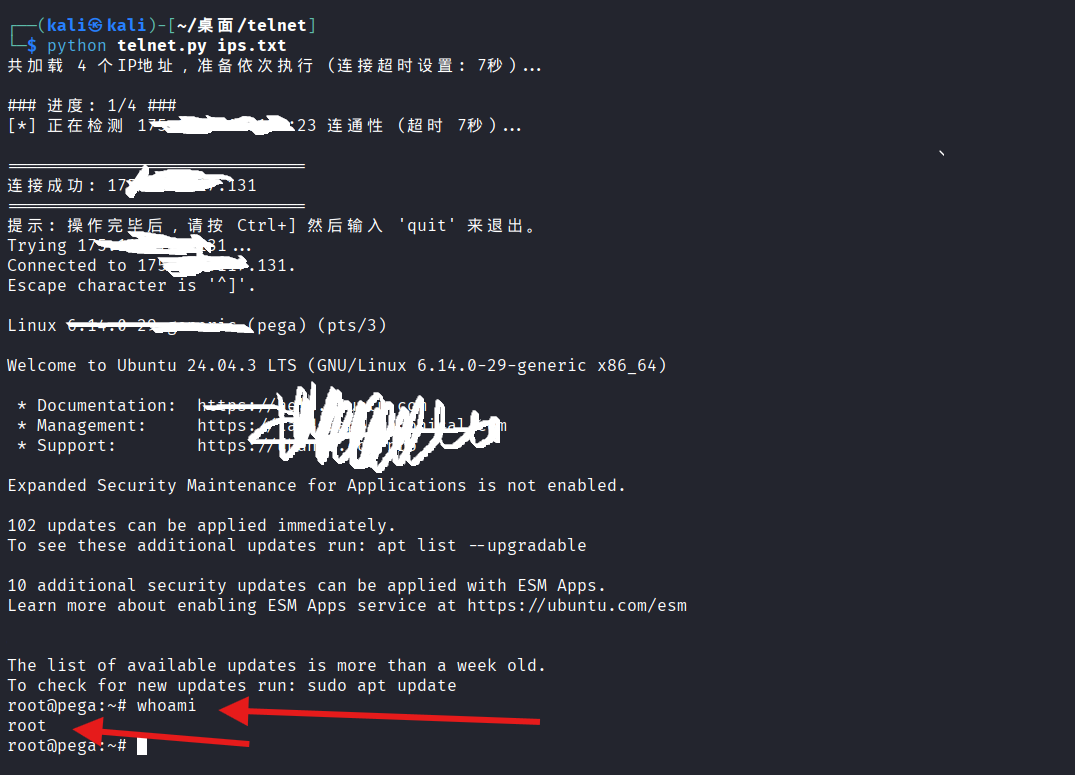 parameciumzhang/tell-me-root
Batch scanner for CVE-2026-24061 Telnet authentication bypass, with port liveness checks and automated payload attempts for authorized penetration…
 watchtowrlabs/watchtowr-vs-watchguard-cve-2025-9242
Python-based detection artifact generator and exploit for WatchGuard Fireware OS CVE-2025-9242, an unauthenticated IKEv2 out-of-bounds write…
 p33d/cve-2024-23113
Python script to detect CVE-2024-23113, a format string vulnerability in FortiGate FGFM service on TCP/541, using SSL connection and crafted payload…
 corelight/cve-2021-41773
Zeek package detecting Apache HTTP Server path traversal/RCE exploits (CVE-2021-41773, CVE-2021-42013) with payload capture and server header…
 l3onkers/fuxios
Modernized Python 3 exploit PoC for CVE-2016-4631 targeting iOS devices. Features network scanning, malformed IP/TCP payload generation, and packet…
 homjxi0e/cve-2017-3881-cisco
Proof-of-concept remote code execution exploit for CVE-2017-3881 affecting Cisco Catalyst switches with telnet enabled, including detailed exploit…
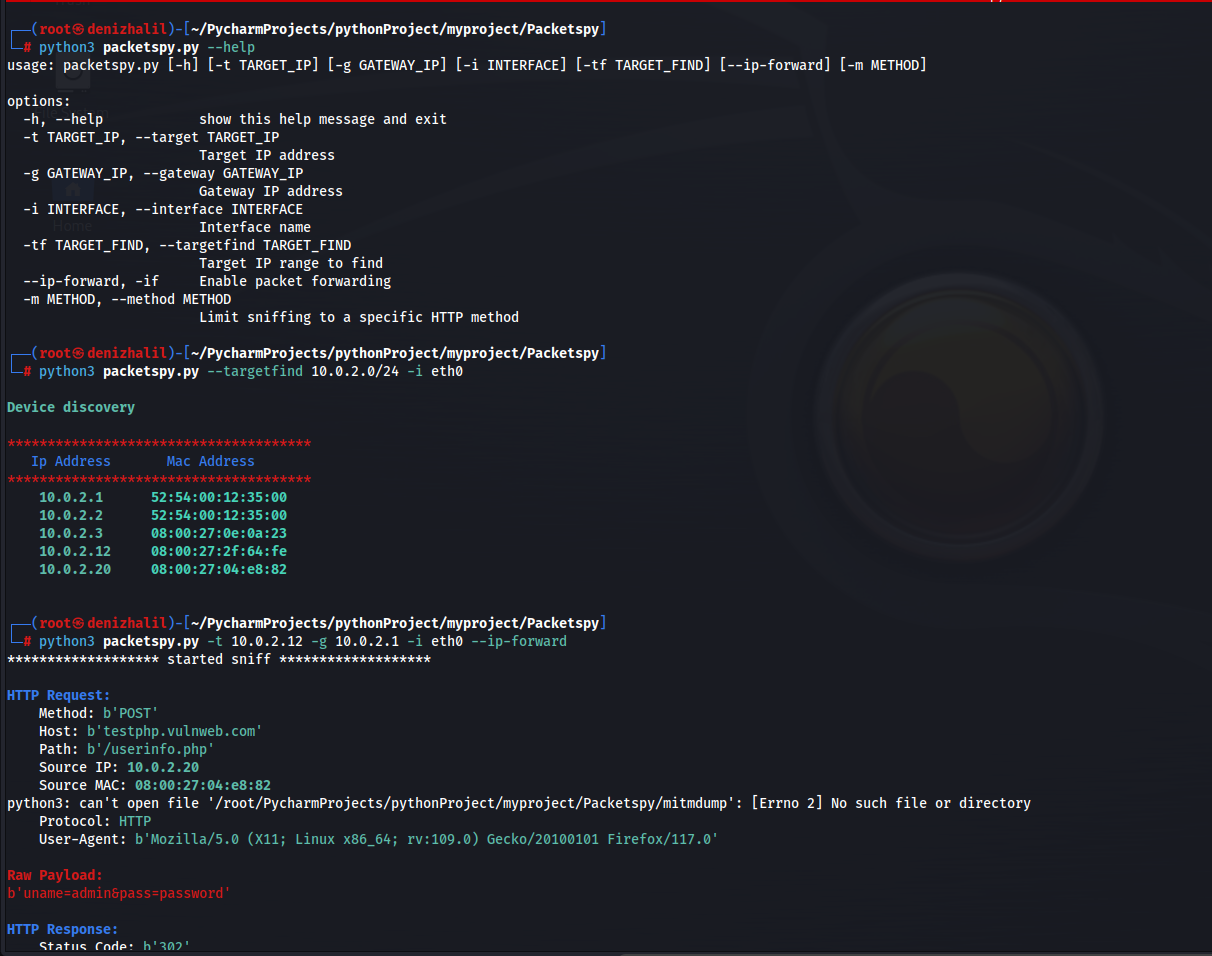 halildeniz/packetspy
Network packet sniffer for real-time traffic capture, HTTP inspection, raw payload analysis, and device discovery with built-in man-in-the-middle…
 hungdnvp/poc-cve-2020-0796
Proof-of-concept exploit for CVE-2020-0796 (SMBGhost) targeting Windows 10/Server SMBv3.1.1. Includes Nmap reconnaissance, vulnerability scanning,…
 nomis/eero-zero-length-ipv6-options-header-dos
eeroOS Ethernet Interface Denial of Service Vulnerability (CVE-2023-5324)
 kimobu/cve-2021-44228
CVE-2021-44228 investigation toolkit with Log4j RCE PoC, JNDIExploit payload runner, Snort detection rules, and PCAP analysis for red and blue team…
 l0n3m4n/cve-2024-6387
PoC - Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (Scanner and Exploit)
 komomon/cve-2020-16898--exp-poc
Proof-of-concept exploit and checker for CVE-2020-16898, a Windows TCP/IP remote code execution vulnerability. Includes Python-based exploit scripts…
 patchpoint/cve-2024-38063
Proof-of-concept exploit for CVE-2024-38063, a Windows TCP/IP remote code execution vulnerability triggered by sending two crafted IPv6 packets with…
 e4zyy/project-cve-2026-50751
IKEv1 VPN scanners, attempts a Check Point authentication-bypass exploit, and includes internal network scanning and reverse-shell features.
 amberwolfcyber/nachovpn
A delicious, but malicious SSL-VPN server 🌮
 kkirsche/cve-2018-1111
Ruby-based exploit for CVE-2018-1111 (DynoRoot) targeting DHCP client vulnerability in Red Hat-based systems to gain root access via malicious DHCP…