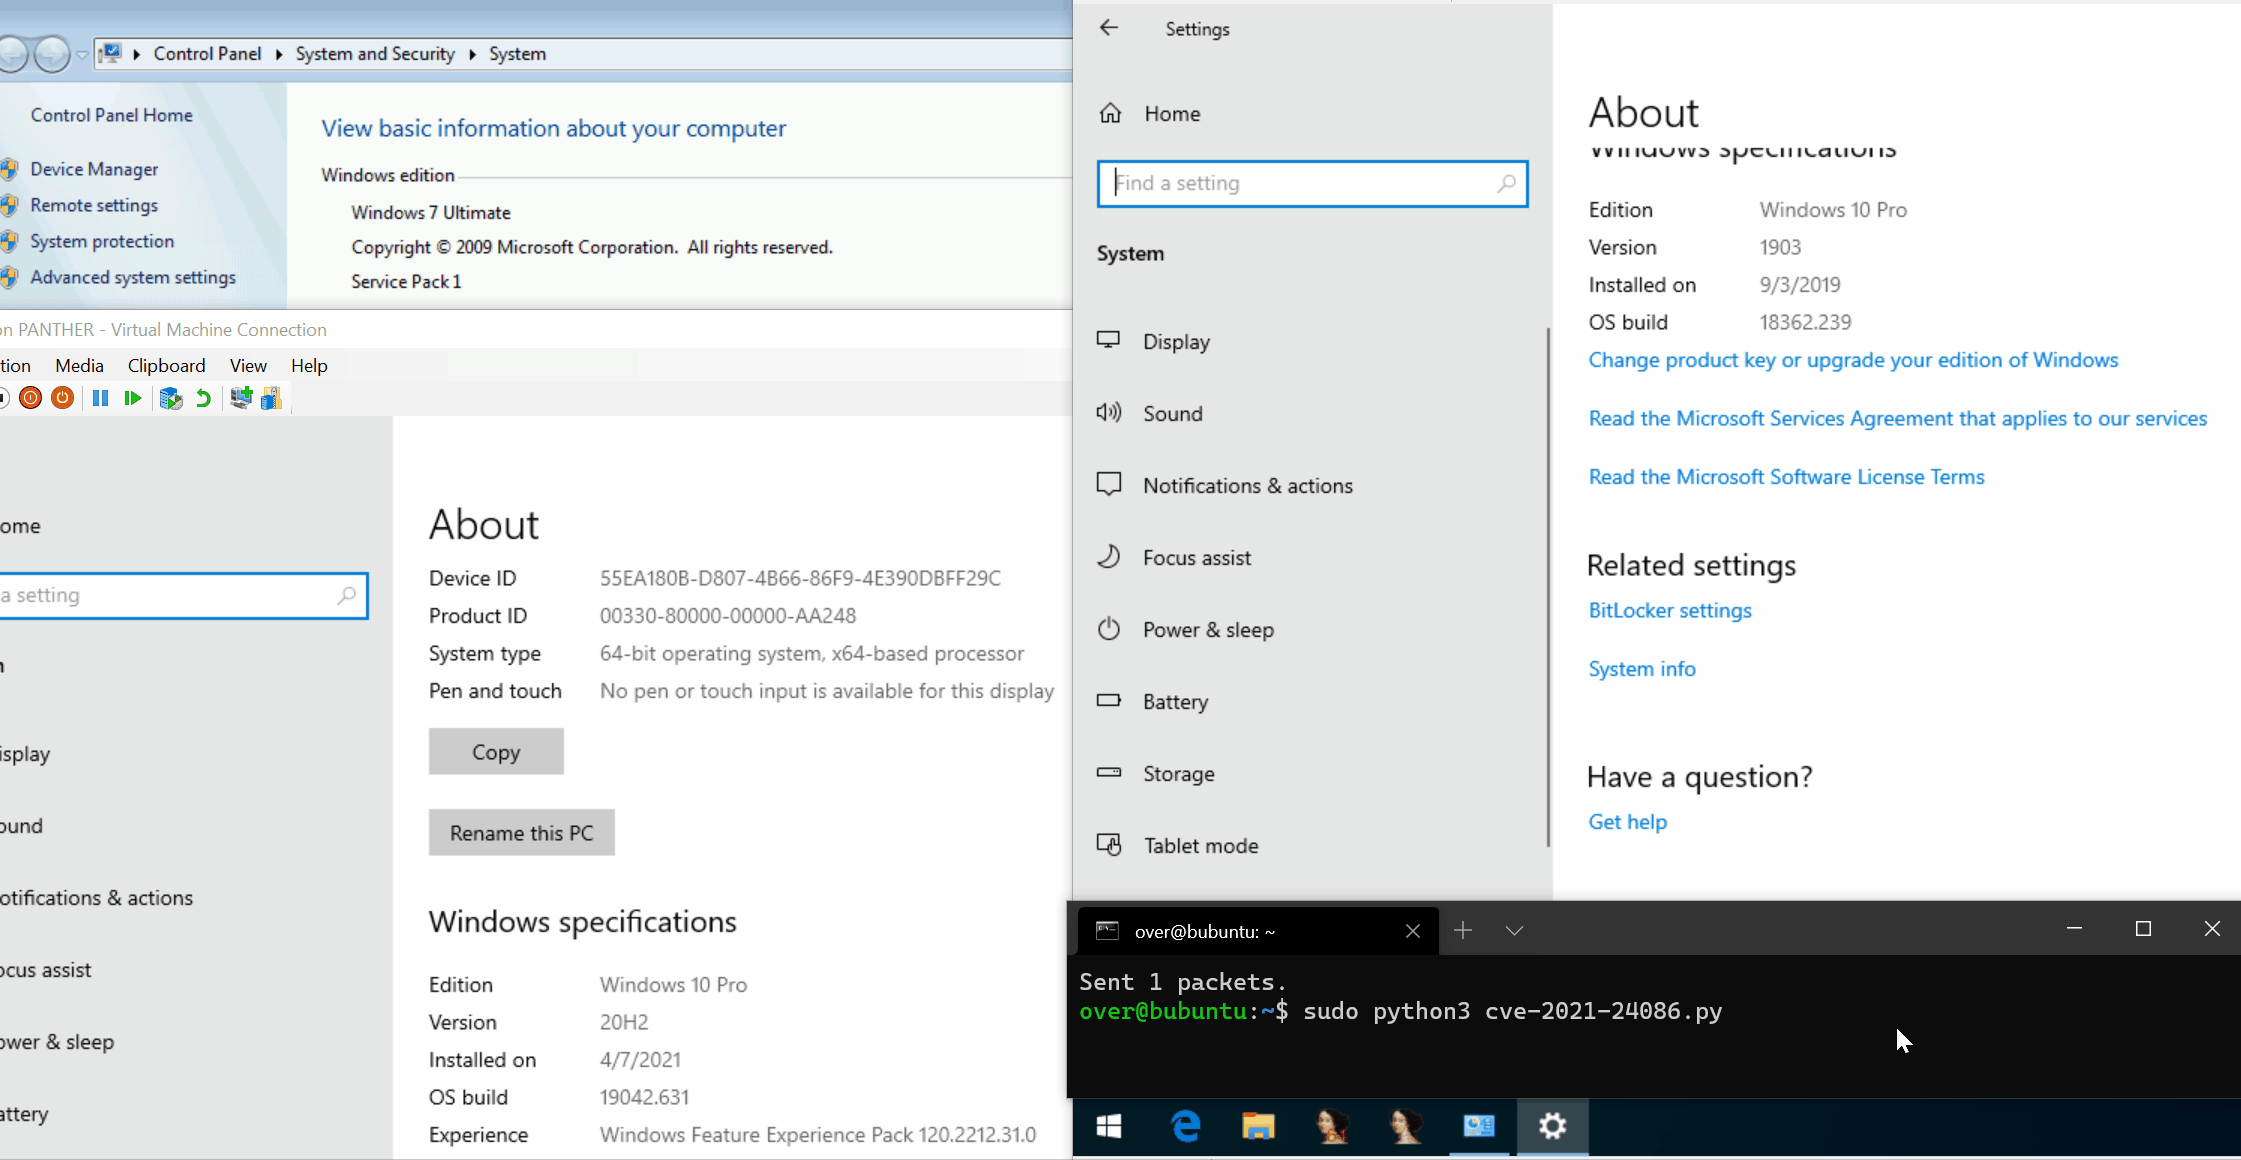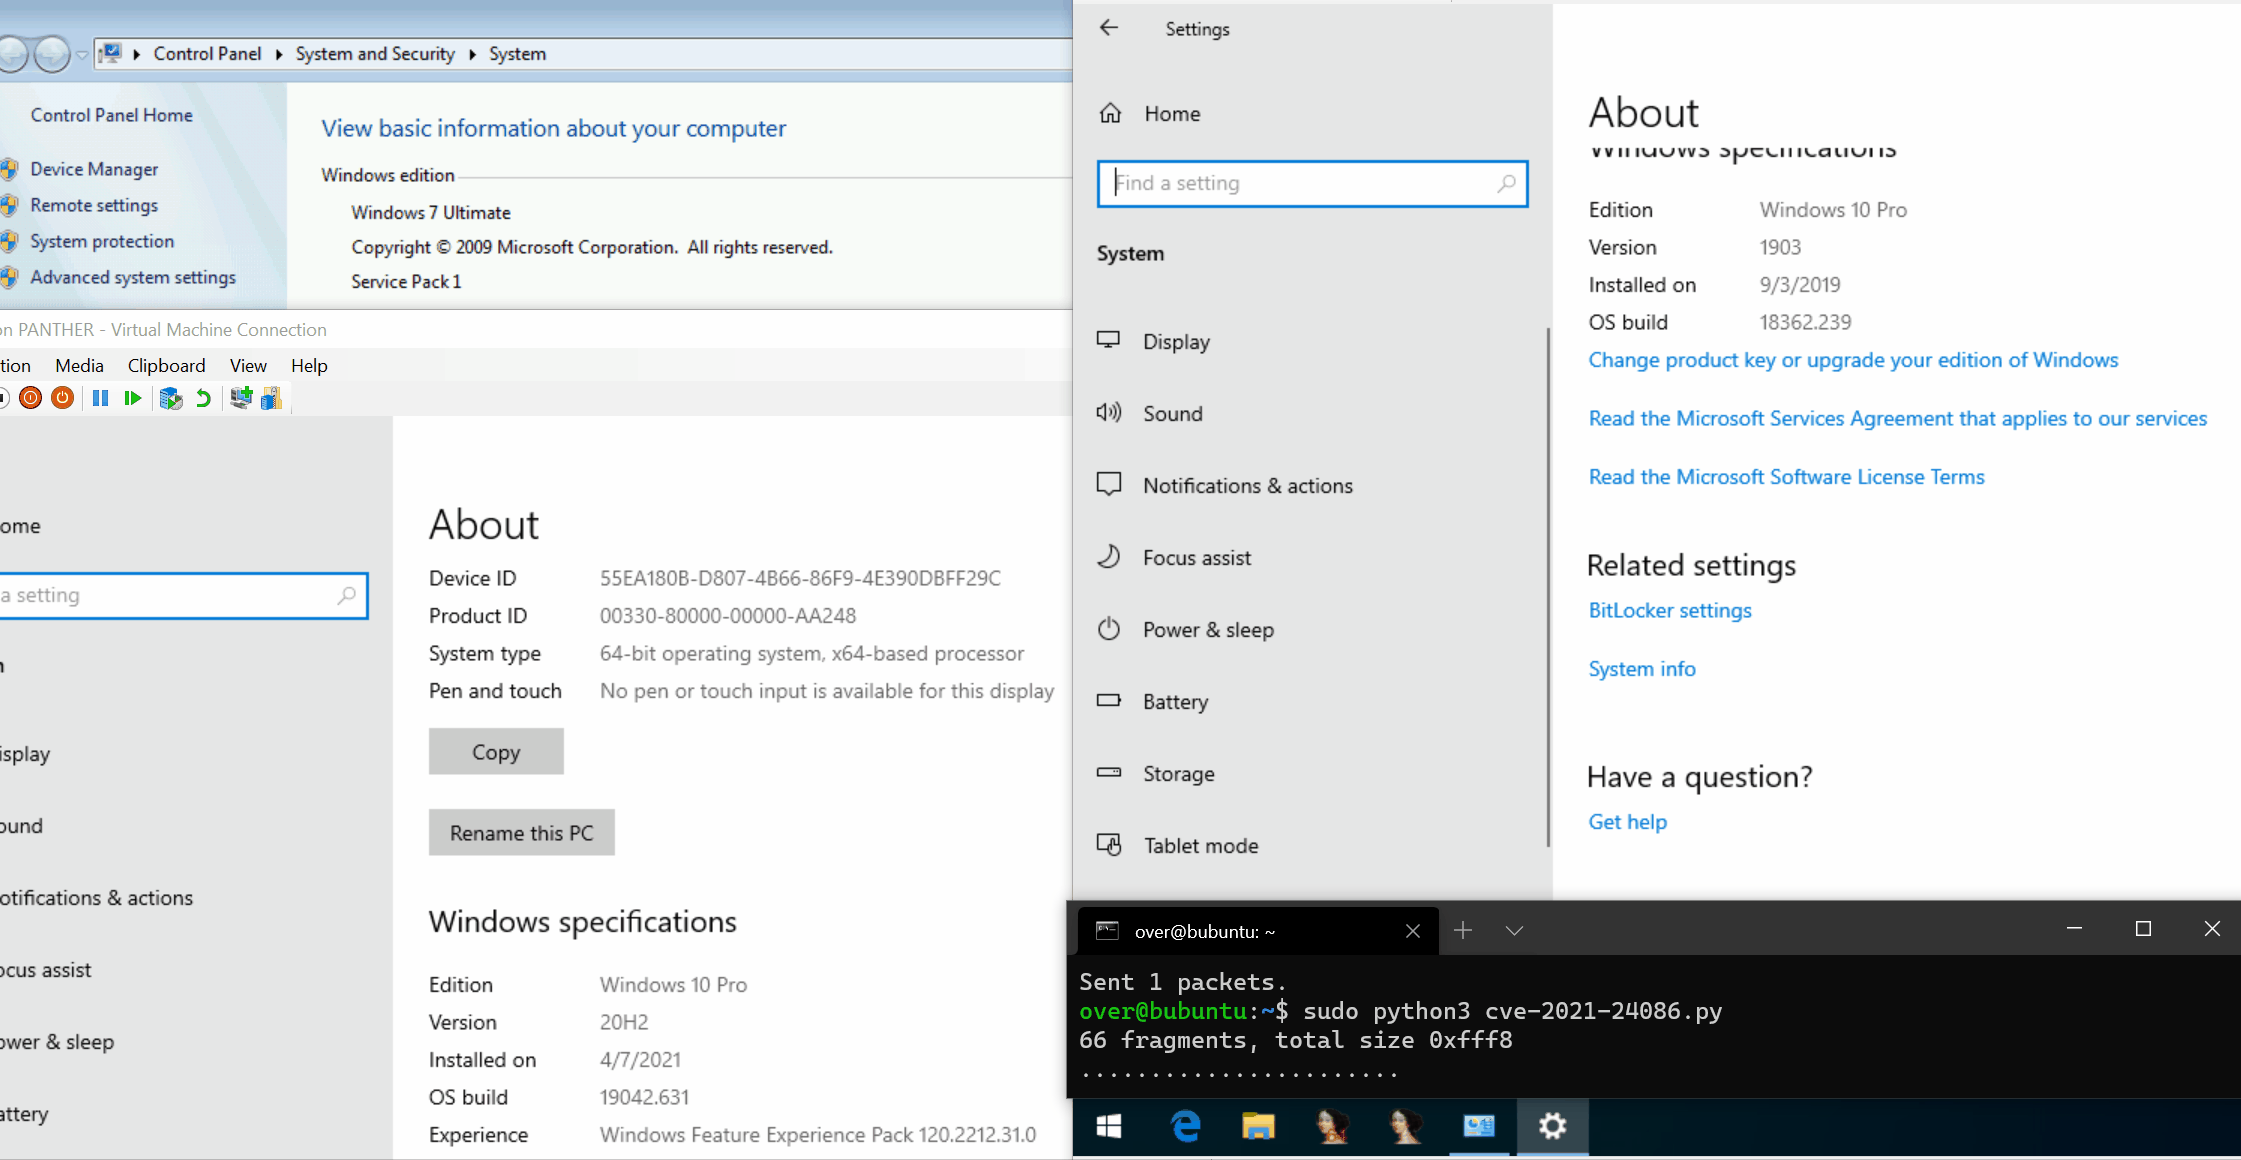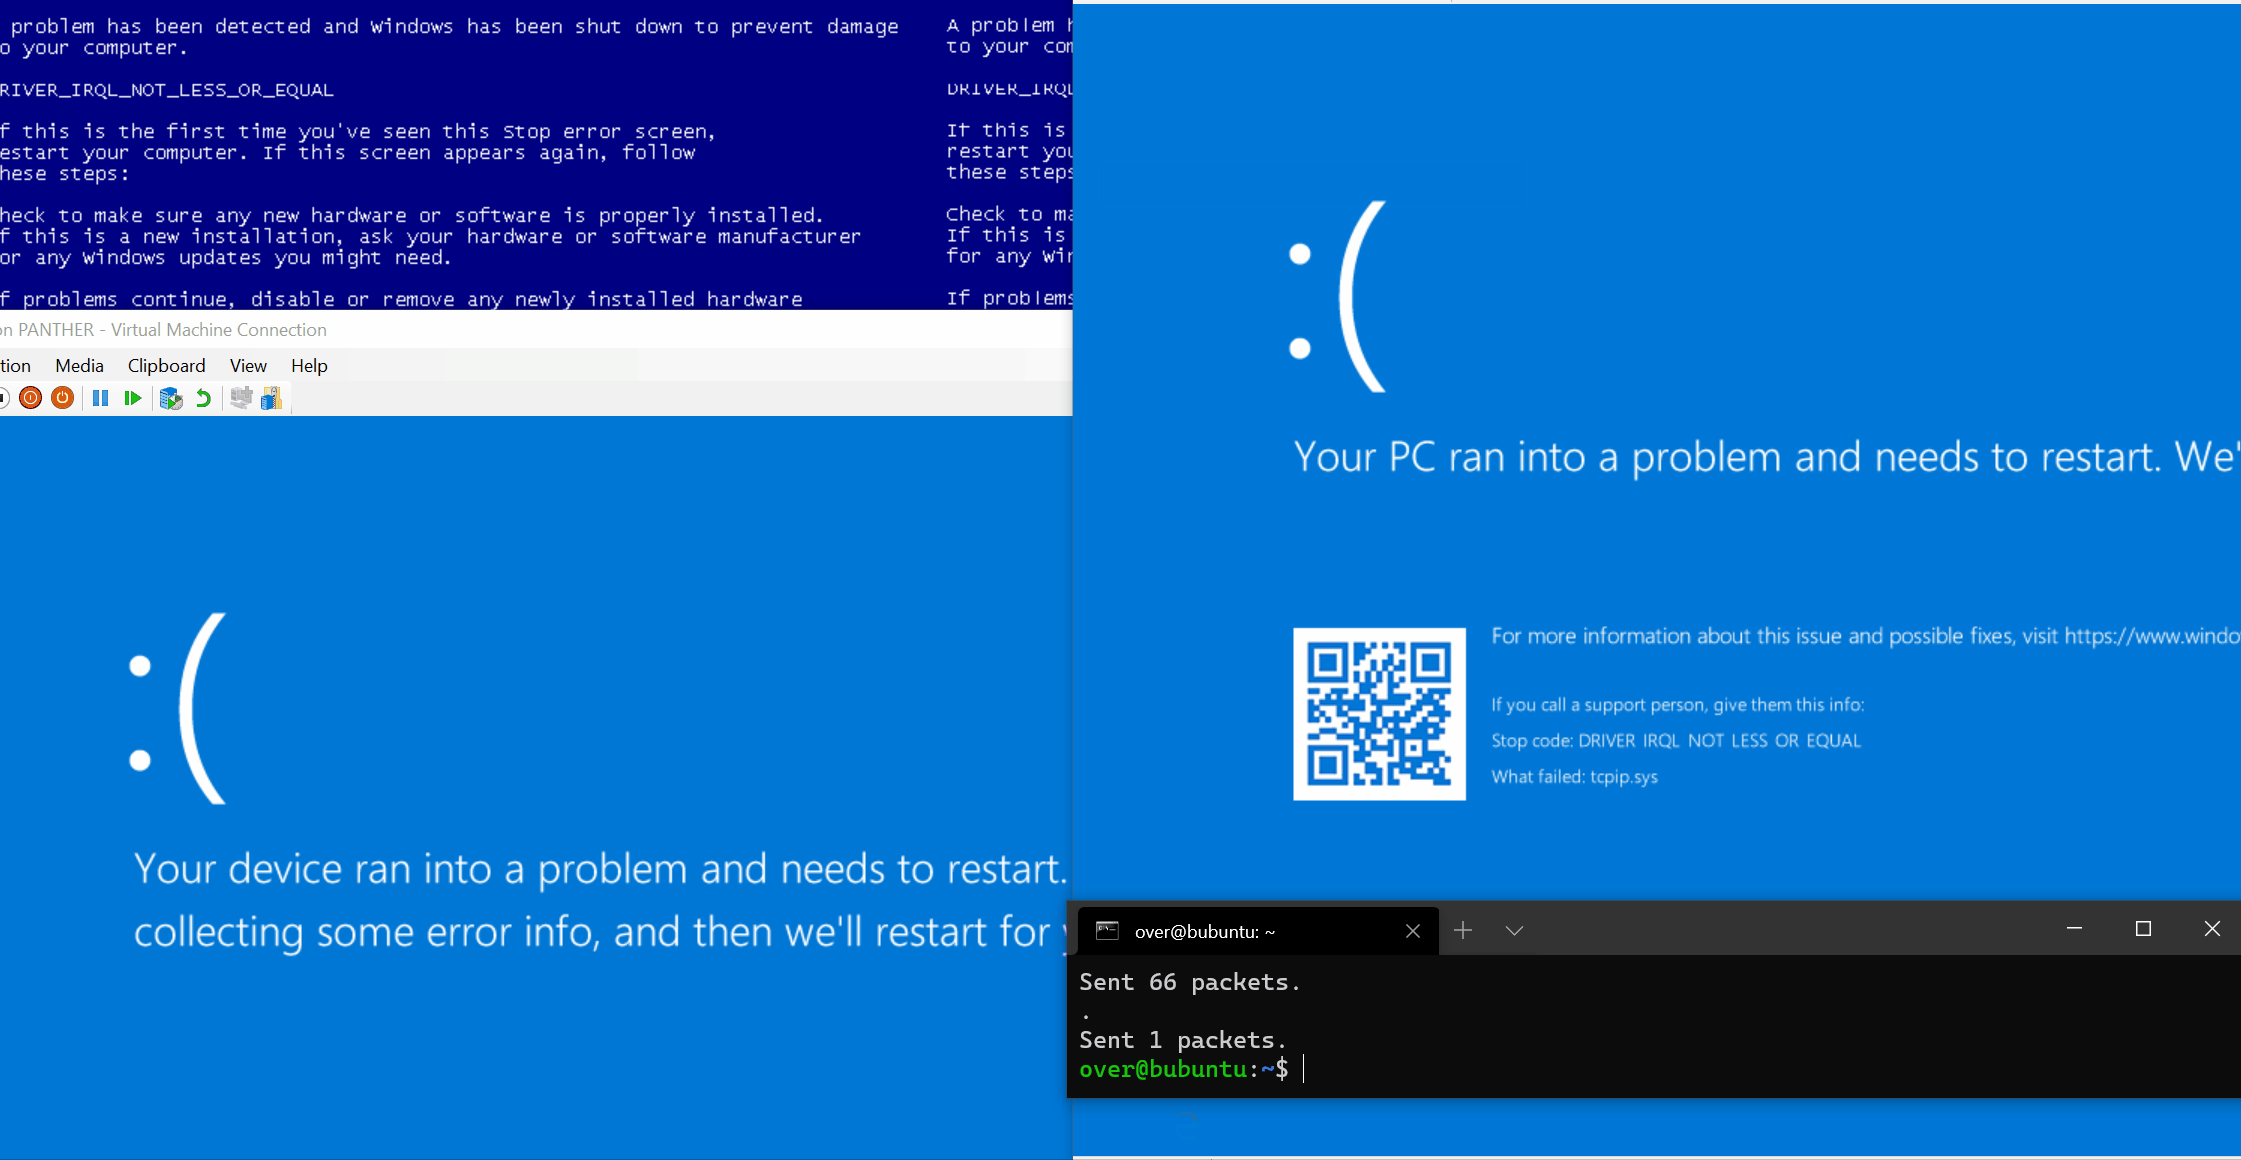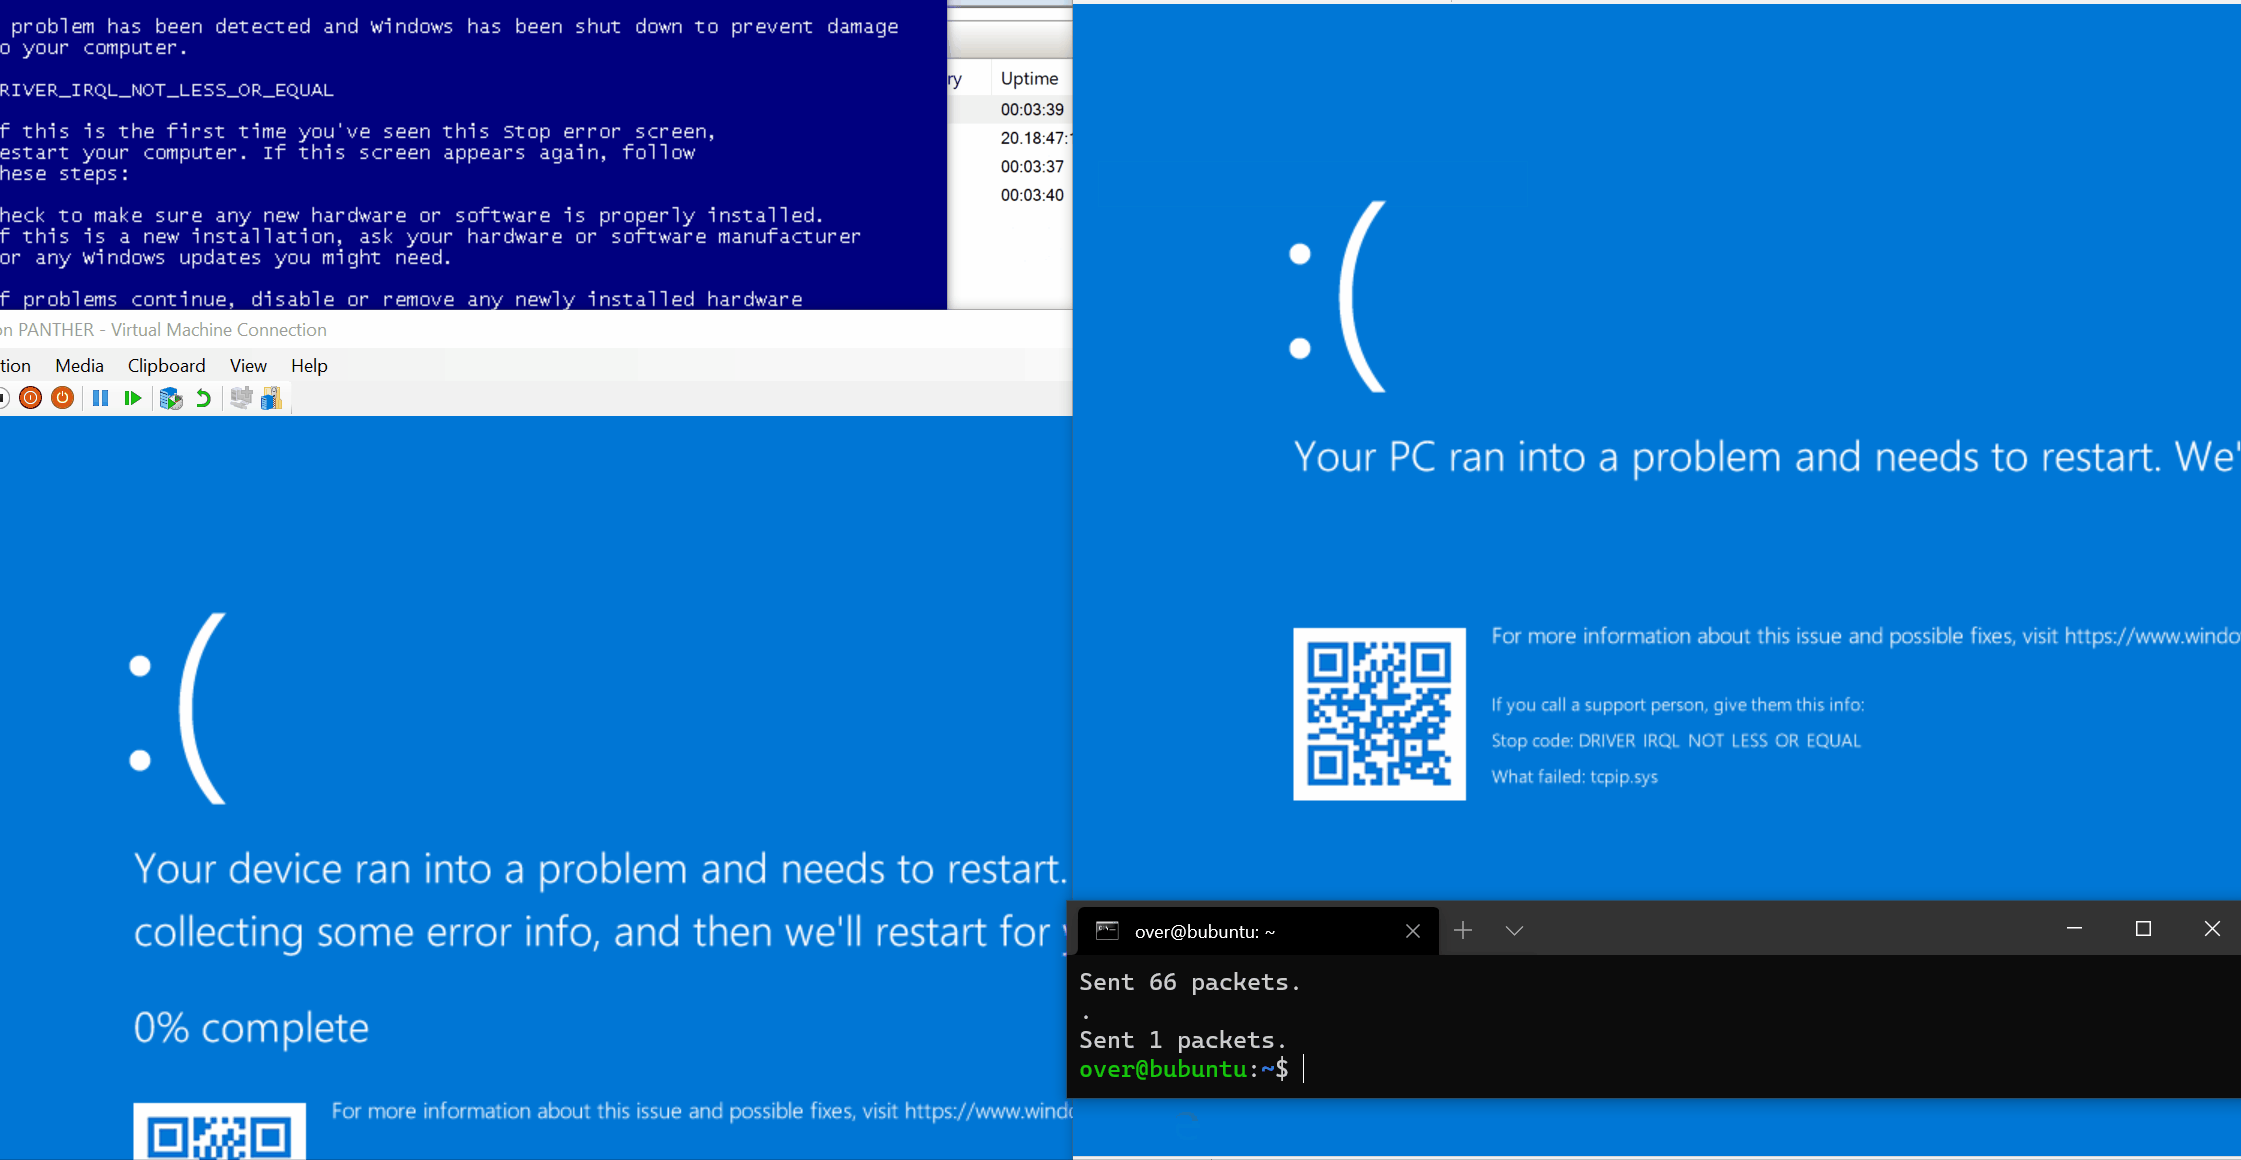

CVE-2021-24086-exp
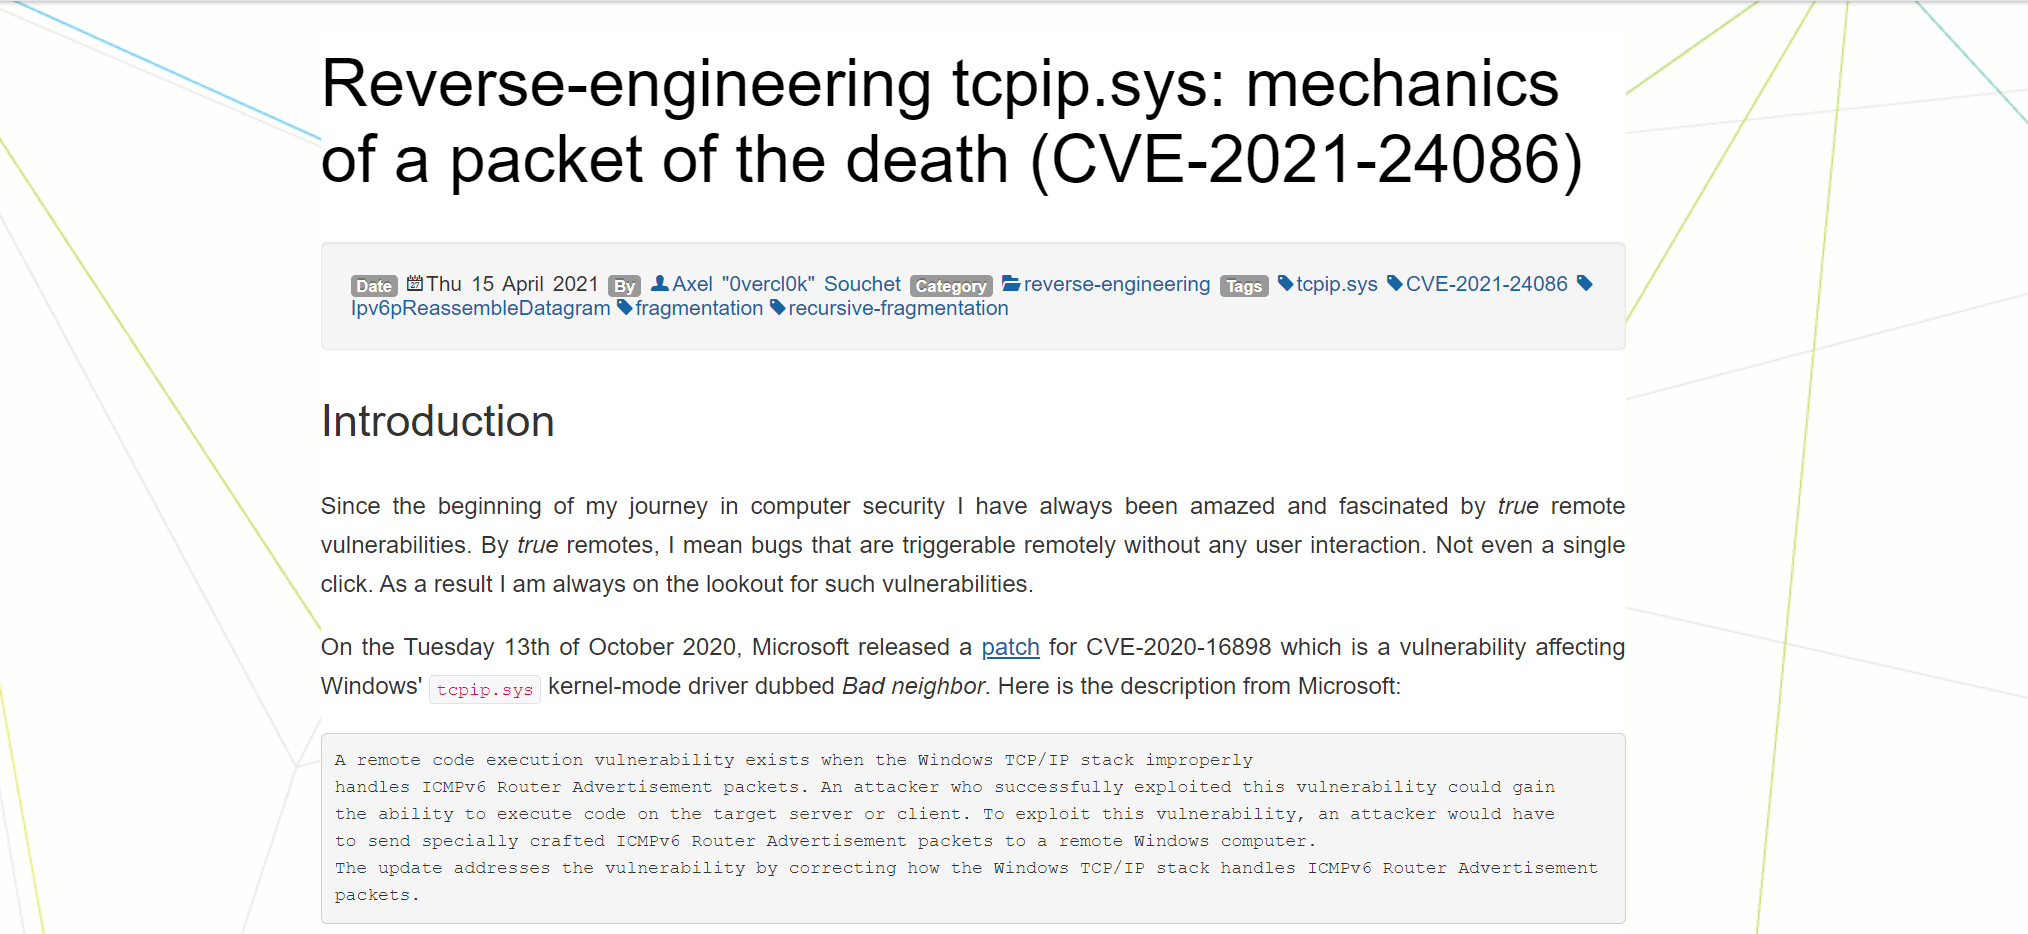
Proof-of-concept exploit for CVE-2021-24086, a NULL dereference in tcpip.sys causing remote denial of service via malicious UDP packets over IPv6.

Proof-of-concept exploit for CVE-2021-24086, a NULL dereference in tcpip.sys causing remote denial of service via malicious UDP packets over IPv6.

Proof of concept for CVE-2021-24086, a NULL dereference in tcpip.sys triggered remotely.

Detection rules (Suricata + Zeek) for CVE-2021-31166 HTTP Protocol Stack vulnerability, providing network-level alerts on exploit attempts against…

Zeek package detecting CVE-2021-42292 Microsoft Excel local privilege escalation exploit via network traffic analysis of spreadsheet downloads.

Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.

Script to scan a list of hosts for CVE-2021-3156 (sudoedit privilege escalation) vulnerability, with configurable passwordless SSH connections for…

Zeek package to detect CVE-2021-1675 (PrintNightmare) by monitoring named pipes and RPC operations for spoolss exploitation attempts.

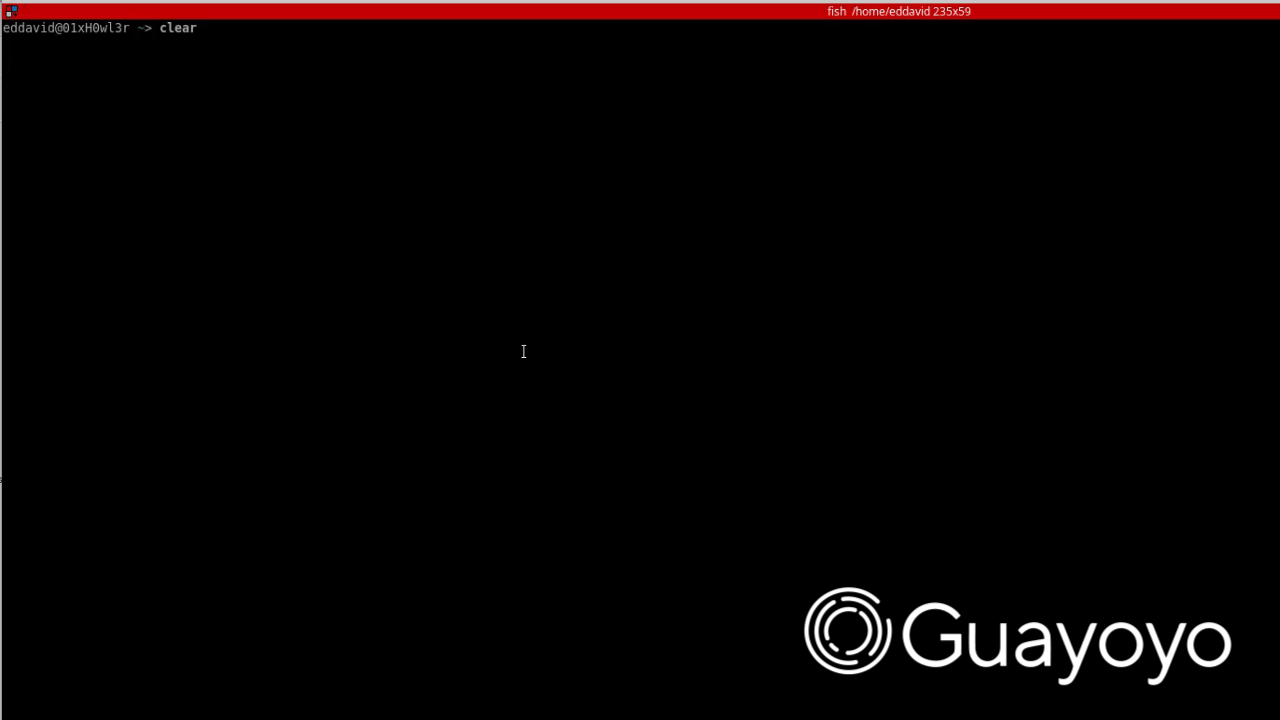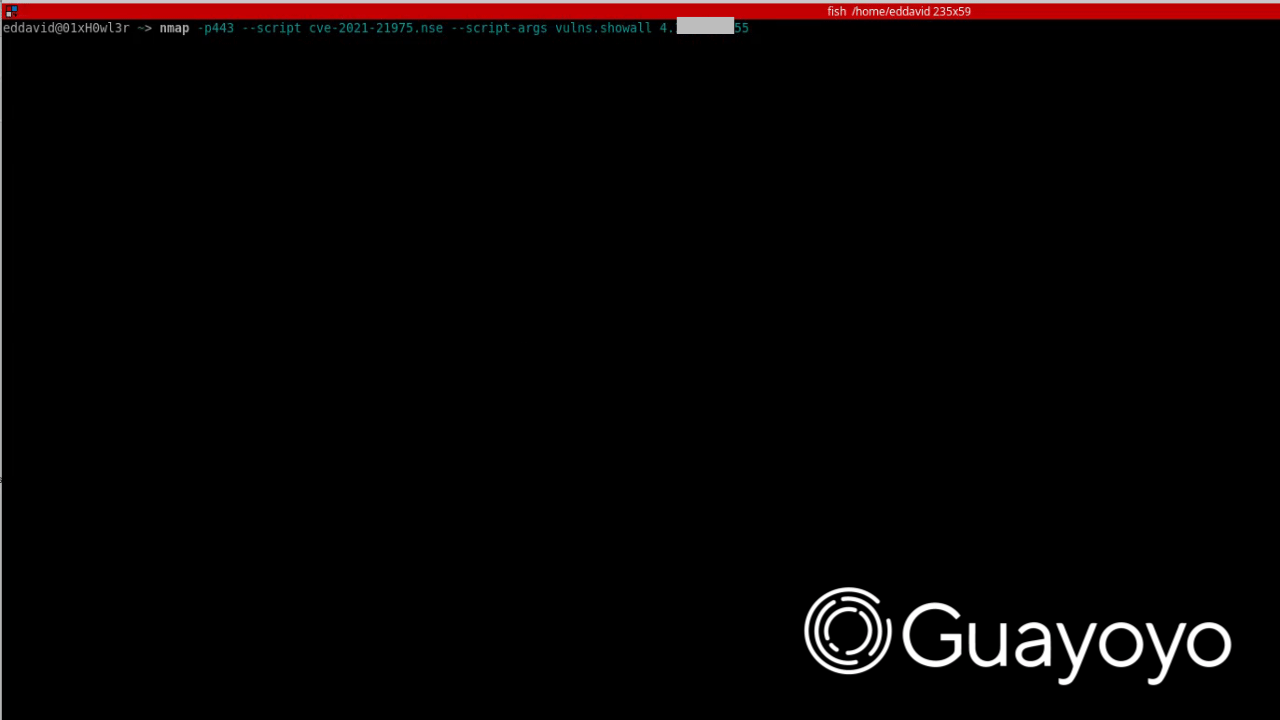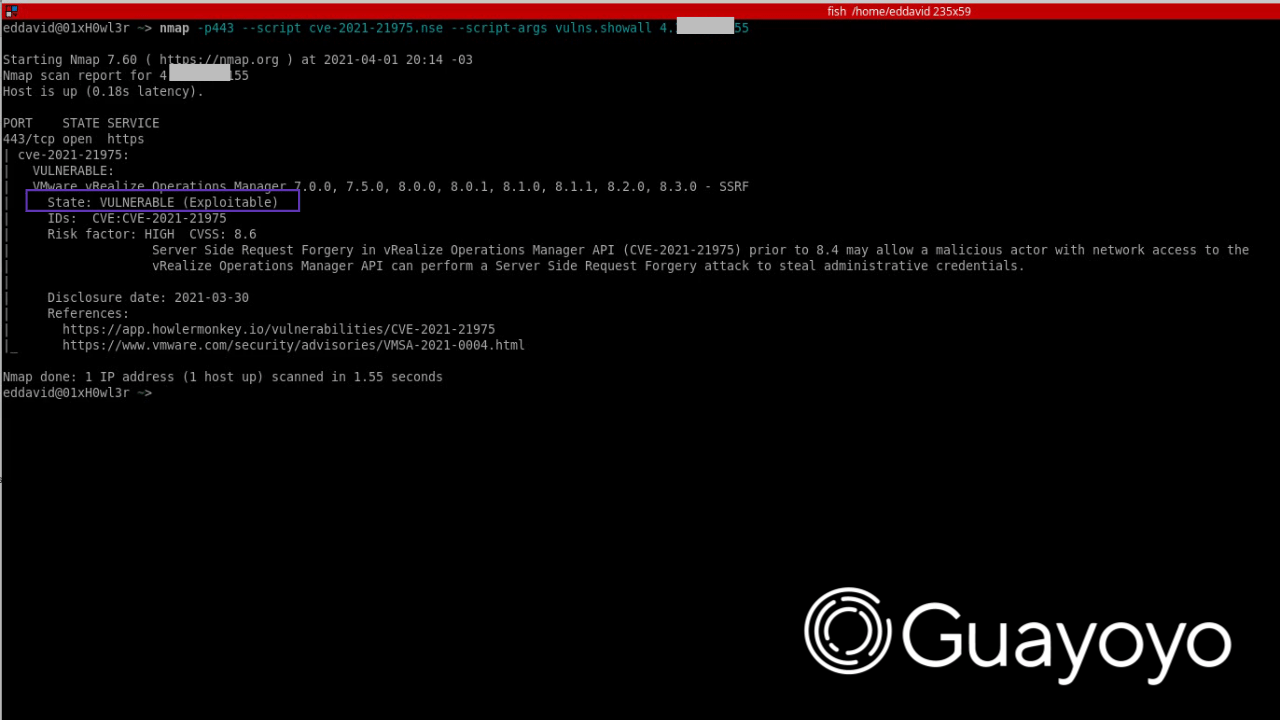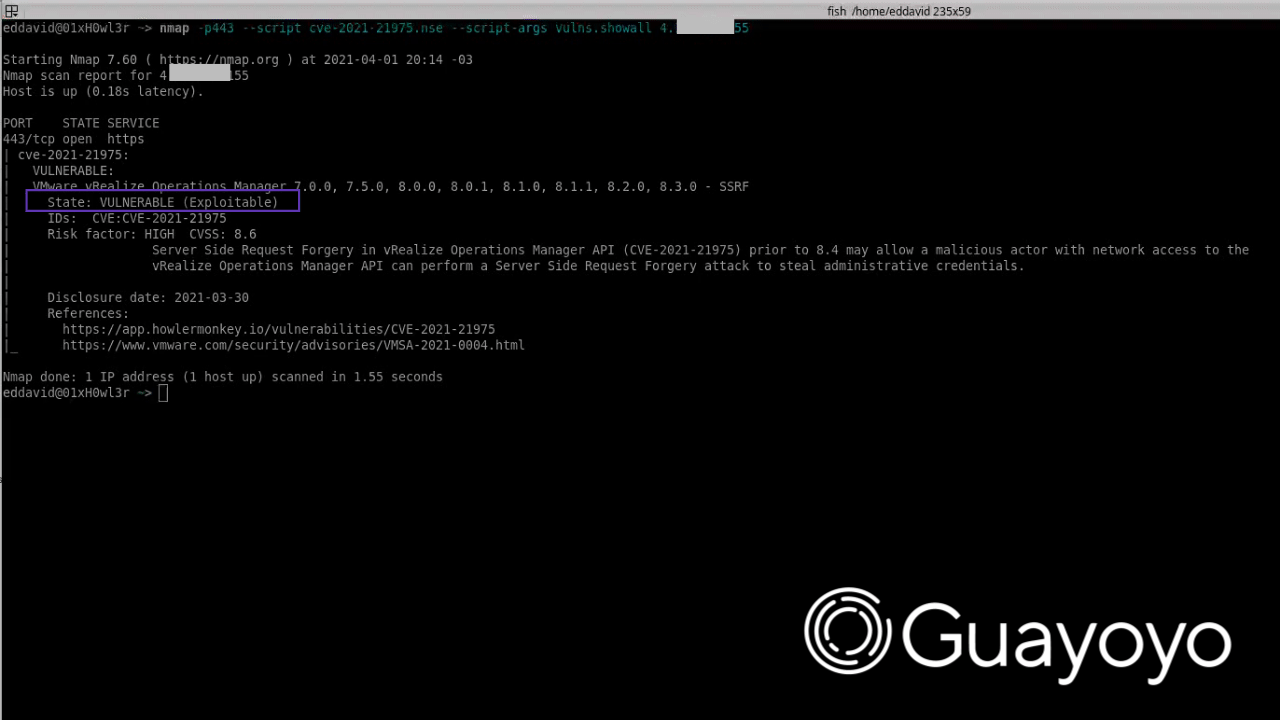
Nmap script to check vulnerability CVE-2021-21975

Different rules to detect if CVE-2021-31166 is being exploited

CVE-2021-21974 Vulnerability Detection Tool Safe PoC that identifies vulnerable SLP implementations without exploitation

Scan your IP network and determine hosts with possible CVE-2021-44228 vulnerability in log4j library.

It is a nmap script for metabase vulnerability (CVE-2021-41277)

CVE-2021-44228 investigation toolkit with Log4j RCE PoC, JNDIExploit payload runner, Snort detection rules, and PCAP analysis for red and blue team…

PoC materials to exploit the CVE-2021-1480 on Cico SD-WAN.

Zeek package detecting CVE-2021-38647 (OMIGOD) exploit attempts by monitoring OMI/WMI traffic for missing Authorization headers and malicious SOAP…

CVE-2021-38647 AKA "OMIGOD" vulnerability in Windows OMI

https://github.com/corelight/CVE-2021-38647 without the bloat

Nmap NSE script for detecting Apache Log4j RCE (CVE-2021-44228) by injecting JNDI exploit payloads via HTTP headers or TCP/UDP sockets across…