
phantom-playbooks
 corelight/phantom-playbooks
Automated security incident response playbooks for Splunk Phantom, integrating Zeek logs, DNS analysis, and VirusTotal threat intelligence to…
defensive-toolsincident-responseintrusion-detection+4
10
corelight/phantom-playbooksAutomated security incident response playbooks for Splunk Phantom, integrating Zeek logs, DNS analysis, and VirusTotal threat intelligence to…
 fox-it/citrix-netscaler-triage
Forensic triage toolkit for Citrix NetScaler devices, featuring a Dissect-based IOC scanner for webshells, timestomping, and suspicious binaries,…
 lupovis/honeypot-for-cve-2025-59287-wsus
Defensive PoC decoy for CVE-2025-59287 (WSUS) - emulates WSUS endpoints, captures request bodies and metadata, saves evidence for forensic analysis,…
 mandiant/citrix-ioc-scanner-cve-2023-3519
Bash-based scanner detecting indicators of compromise from CVE-2023-3519 exploitation on Citrix ADC appliances, supporting live and forensic image…
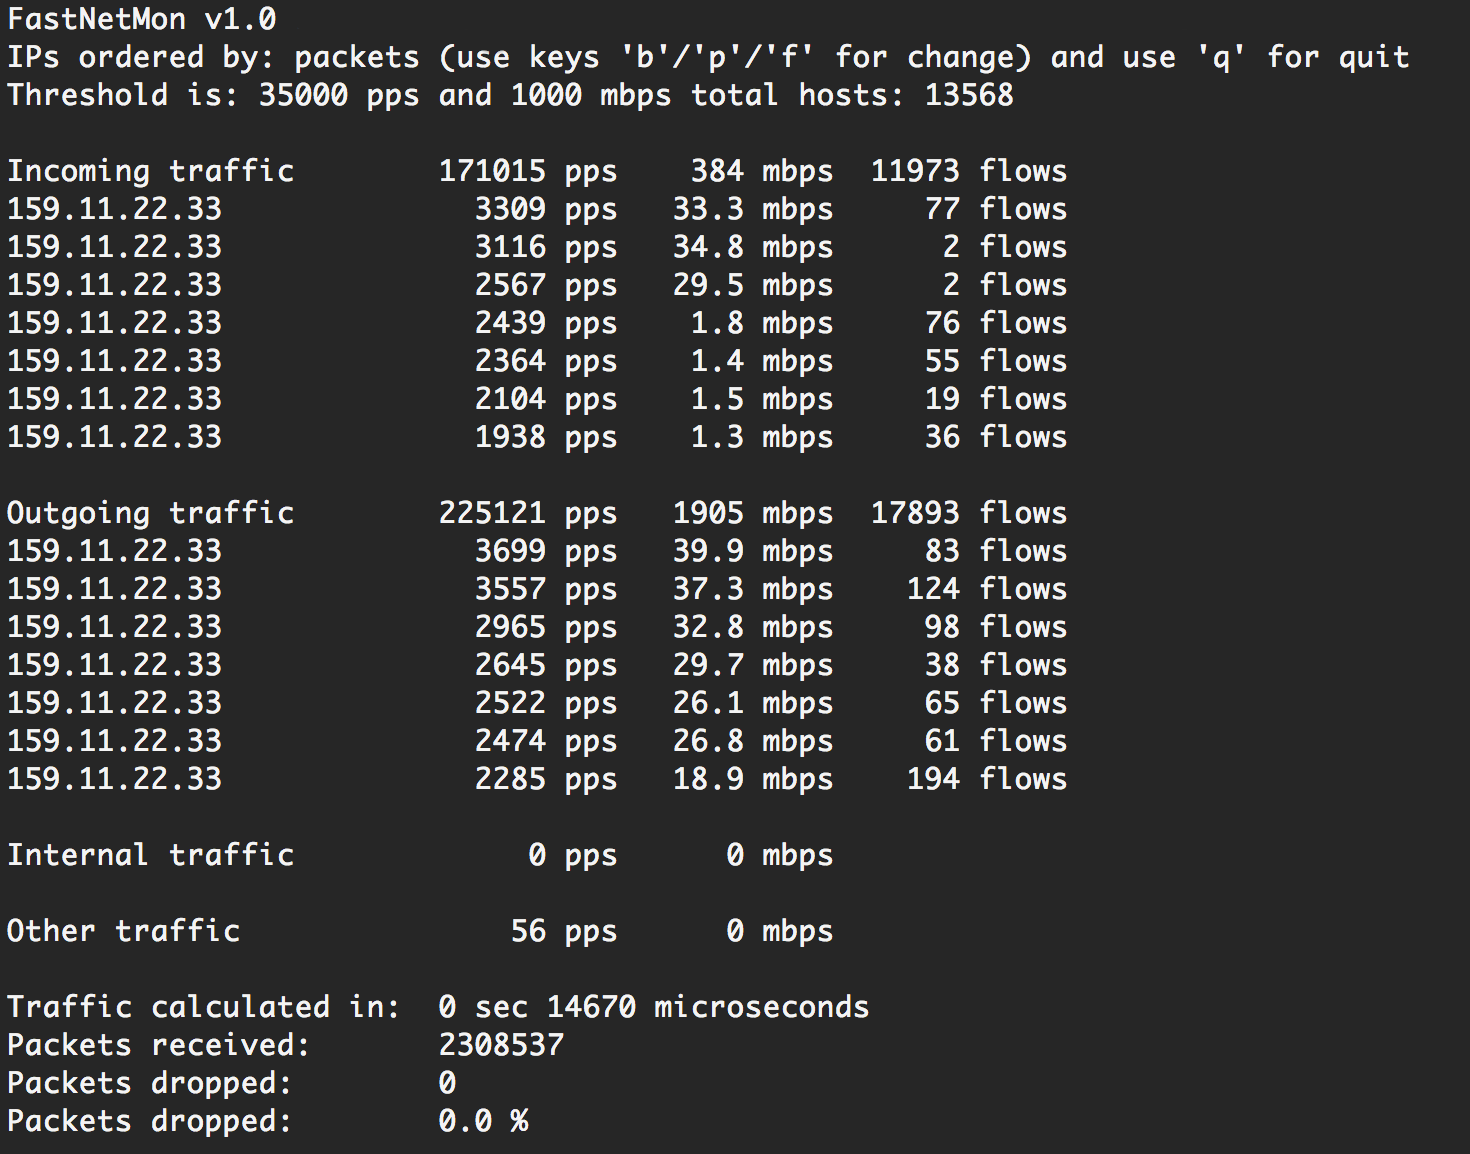 pavel-odintsov/fastnetmon
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
 tenzir/tenzir
Collect, parse, normalize, aggregate, store, query, and route security telemetry data at scale using pipeline-based dataflows for threat detection…
 snorby/snorby
Ruby On Rails Application For Network Security Monitoring
 cyberark/ketshash
A little tool for detecting suspicious privileged NTLM connections, in particular Pass-The-Hash attack, based on event viewer logs.
 corelight/community-id-spec
An open standard for hashing network flows into identifiers, a.k.a "Community IDs".
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 thelightscope/thelightscope
TheLightScope
 aws-alchemy/squidmagic
analyze a web-based network traffic 🕶 to detect central command and control servers
 corelight/ecs-logstash-mappings
Mapping Corelight or Zeek data to Elastic Common Schema logs
 scriptjunkie/fwallower
Analyze Windows Firewall outbound blocks and selectively allow traffic
 withsecurelabs/remotepspy
Live monitoring tool for remote PowerShell sessions using ETW to capture and decode WinRM/PSRP protocol, providing command execution traces and…
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
 corelight/corelightforcrowdstrike
Corelight app for CrowdStrike LogScale and Next-Gen SIEM