Pulsar
 jacopodl/pulsar
Data exfiltration and covert communication tool
command-and-controlcryptographydata-exfiltration+2
jacopodl/pulsarData exfiltration and covert communication tool
 haxrob/bpfdoor-controller-source
Source code for a BPFDoor backdoor controller supporting TCP, UDP, ICMP, and HTTPS covert communication channels with magic packet activation,…
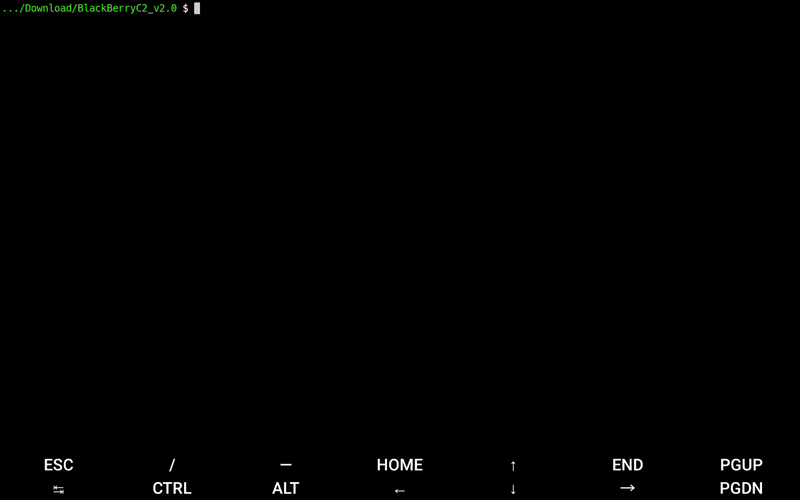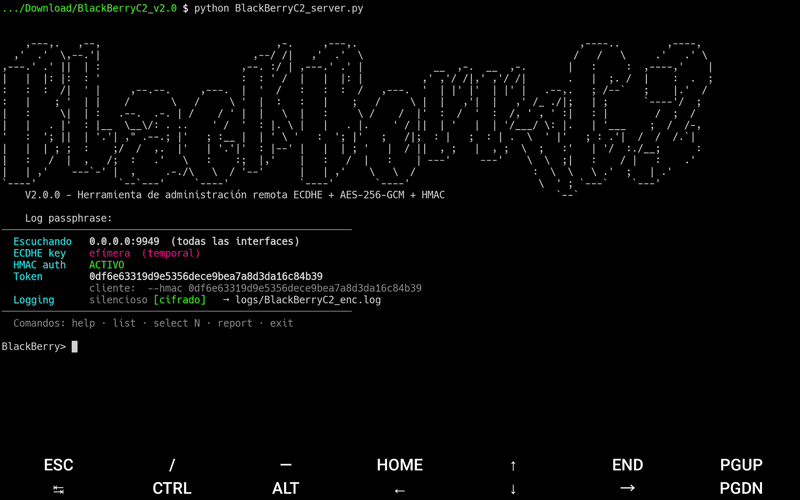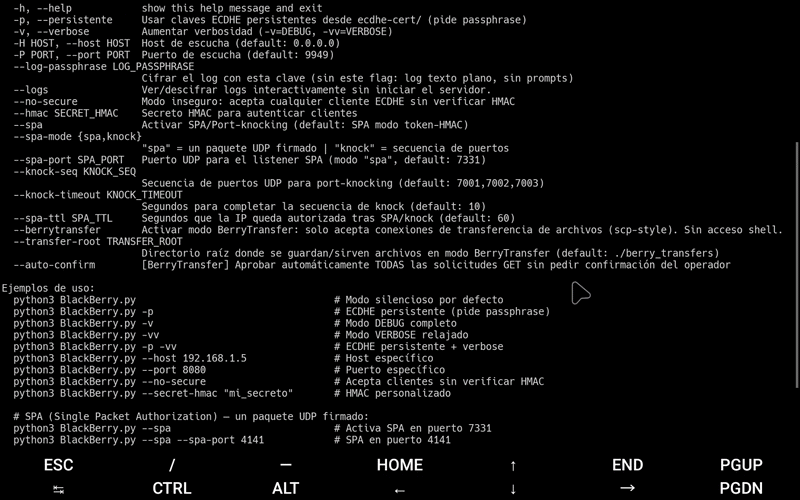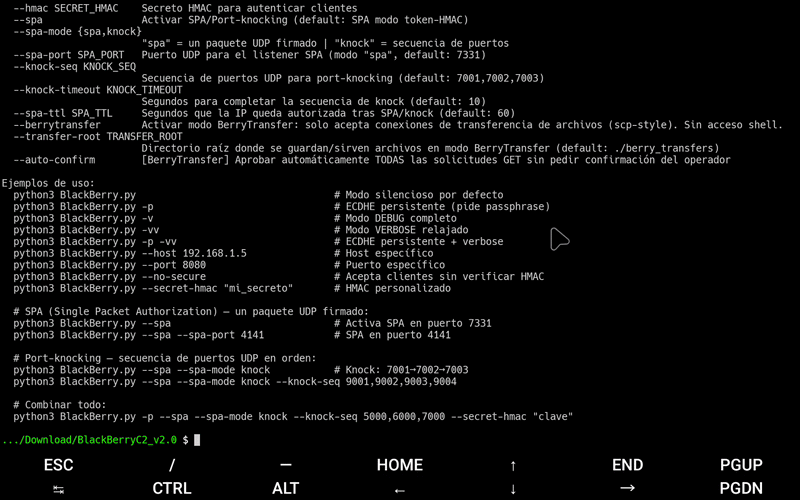 dereeqw/blackberryc2
Encrypted command‑and‑control (C2) research framework for cybersecurity education, red team labs, and secure client‑server communication experiments.
 omer-efe-curkus/cve-2025-32433-erlang-otp-ssh-rce-poc
The vulnerability allows an attacker with network access to an Erlang/OTP SSH server to execute arbitrary code without prior authentication.
 xmco/sdwan-cve-2021-1480
PoC materials to exploit the CVE-2021-1480 on Cico SD-WAN.
 corelight/zeek-netsupport-detector
A Zeek based NetSupport detector. NetSupport is often abused by attackers in malware.
 corelight/zeek-caldera-detector
A Zeek based Mitre Caldera detector.
 abrewer251/cve-2025-32433_erlang-otp_poc
This script is a custom security tool designed to test for a critical pre-authentication vulnerability in systems running Erlang-based SSH servers
 fevar54/cve-2026-20245---cisco-sd-wan-privilege-escalation-exploit
**Este código es SOLO para fines educativos y pruebas de seguridad autorizadas.**
 sastraadiwiguna-purpleeliteteaming/ddos-purple-teaming-offensive-multi-vector-7-tier-defensive-holistic-blueprint-
Replicable Blueprint for advanced DDoS Purple Teaming, engineered for the threat landscape. It integrates a Red Elite Teaming offensive…
 rockmelodies/blackash-cve-2025-14558
CVE-2025-14558
 odst-forge/cve-2025-32433_poc
This script is a custom security tool designed to test for a critical pre-authentication vulnerability in systems running Erlang-based SSH servers
 mgeeky/redwarden
Cobalt Strike C2 Reverse proxy that fends off Blue Teams, AVs, EDRs, scanners through packet inspection and malleable profile correlation
 byt3bl33d3r/mitmf
Framework for Man-In-The-Middle attacks