

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Sources curated into a security tool Repositories, feeds, communities and curated indexes flow through selection, classification, enrichment and translation into an illustrative tool record. ISC License Copyright (c) 2026 Lucide Icons and Contributors Permission to use, copy, modify, and/or distribute this software for any purpose with or without fee is hereby granted, provided that the above copyright notice and this permission notice appear in all copies. THE SOFTWARE IS PROVIDED "AS IS" AND THE AUTHOR DISCLAIMS ALL WARRANTIES WITH REGARD TO THIS SOFTWARE INCLUDING ALL IMPLIED WARRANTIES OF MERCHANTABILITY AND FITNESS. IN NO EVENT SHALL THE AUTHOR BE LIABLE FOR ANY SPECIAL, DIRECT, INDIRECT, OR CONSEQUENTIAL DAMAGES OR ANY DAMAGES WHATSOEVER RESULTING FROM LOSS OF USE, DATA OR PROFITS, WHETHER IN AN ACTION OF CONTRACT, NEGLIGENCE OR OTHER TORTIOUS ACTION, ARISING OUT OF OR IN CONNECTION WITH THE USE OR PERFORMANCE OF THIS SOFTWARE. --- The following Lucide icons are derived from the Feather project: airplay, alert-circle, alert-octagon, alert-triangle, aperture, arrow-down-circle, arrow-down-left, arrow-down-right, arrow-down, arrow-left-circle, arrow-left, arrow-right-circle, arrow-right, arrow-up-circle, arrow-up-left, arrow-up-right, arrow-up, at-sign, calendar, cast, check, chevron-down, chevron-left, chevron-right, chevron-up, chevrons-down, chevrons-left, chevrons-right, chevrons-up, circle, clipboard, clock, code, columns, command, compass, corner-down-left, corner-down-right, corner-left-down, corner-left-up, corner-right-down, corner-right-up, corner-up-left, corner-up-right, crosshair, database, divide-circle, divide-square, dollar-sign, download, external-link, feather, frown, hash, headphones, help-circle, info, italic, key, layout, life-buoy, link-2, link, loader, lock, log-in, log-out, maximize, meh, minimize, minimize-2, minus-circle, minus-square, minus, monitor, moon, more-horizontal, more-vertical, move, music, navigation-2, navigation, octagon, pause-circle, percent, plus-circle, plus-square, plus, power, radio, rss, search, server, share, shopping-bag, sidebar, smartphone, smile, square, table-2, tablet, target, terminal, trash-2, trash, triangle, tv, type, upload, x-circle, x-octagon, x-square, x, zoom-in, zoom-out The MIT License (MIT) (for the icons listed above) Copyright (c) 2013-present Cole Bemis Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction, including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to do so, subject to the following conditions: The above copyright notice and this permission notice shall be included in all copies or substantial portions of the Software. THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.
Repositories
GitHub & GitLab
Security feeds
Blogs, RSS & Atom
Communities
Reddit, X & submissions
Curated indexes
Security lists & trends
Curate & select
Classification
Enrichment
Translation
Fictional tool and repository. The description, categories, stars, forks and views are illustrative examples, not live or verified data. Fictional tool and repository. The description, categories, stars, forks and views are illustrative examples, not live or verified data. {"fictional":true,"name":"Tool","version":"1.0.1","repository":"owner/tool","live_metrics":false,"example_metrics":{"stars":1200,"forks":128,"views":8600}}
Tool
v1.0.1 owner/tool
Discover assets and review
HTTP security headers.
Reconnaissance
Web security
1,200 stars — Fictional example1.2k 128 forks — Fictional example128 8,600 views — Fictional example8.6k

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
2069 results
VULNERAVEL-CVE-2018-14847---CREDENCIAIS-EXTRAIDAS preview

VULNERAVEL-CVE-2018-14847---CREDENCIAIS-EXTRAIDAS

GitHubmourafuseti/vulneravel-cve-2018-14847---credenciais-extraidas

VULNERAVEL CVE-2018-14847 - CREDENCIAIS EXTRAIDAS MIKROTIK EM PYTHON
exploitationiot-securitynetwork-security+3
1
6 months ago
CVE-2026-7473---Arista-EOS-Tunnel-Decapsulation-Bypass preview

CVE-2026-7473---Arista-EOS-Tunnel-Decapsulation-Bypass

GitHubfevar54/cve-2026-7473---arista-eos-tunnel-decapsulation-bypass

Vulnerability: On affected Arista EOS platforms with tunnel decapsulation

configuration-auditingeducationexploitation+3
15 months ago
ssh-honeypot-research preview

ssh-honeypot-research

GitHubliranzoz/ssh-honeypot-research

Medium-interaction SSH honeypot deployment capturing real-world brute-force traffic, malware drops, and attacker behavior. Includes TTY session…
digital-forensicseducationincident-response+4
16 months ago
cpanel2shell-honeypot preview

cpanel2shell-honeypot

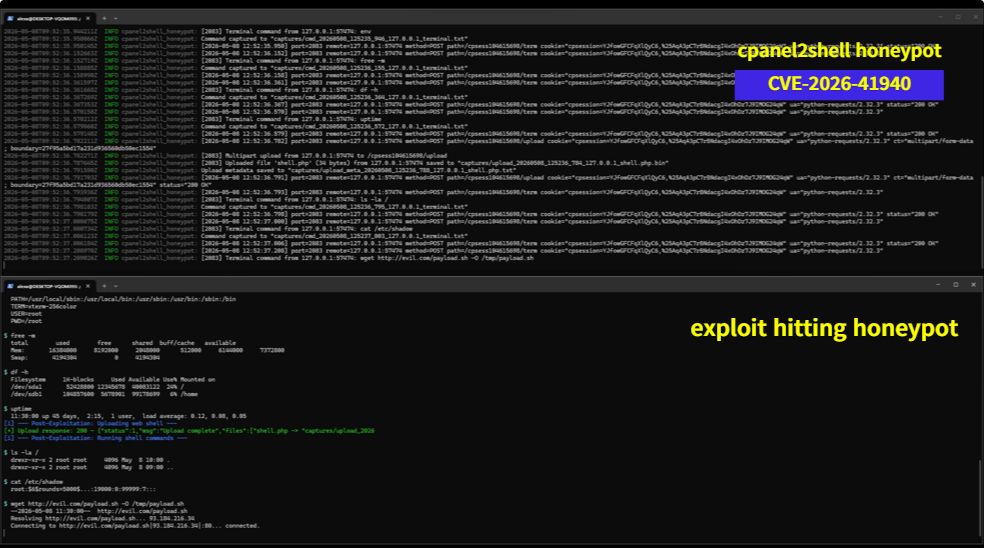
GitHubacuciureanu/cpanel2shell-honeypot

A Rust honeypot that simulates a vulnerable cPanel/WHM instance for CVE-2026-41940

network-securitythreat-intelligencevulnerability-analysis+1
6 months ago
heartbleed-lab preview

heartbleed-lab

GitHubvictoriacfigueiredo/heartbleed-lab

Educational laboratory for studying CVE-2014-0160 (Heartbleed) and framing inconsistencies in TLS heartbeat handling.

binary-exploitationcryptographyeducation+3
5 months ago
PetitPotam preview

PetitPotam

GitHubcorelight/petitpotam

Detects NTLM relay attacks via PetitPotam exploit using Zeek, distinguishing successful and unsuccessful attempts by analyzing DCERPC return codes.

anomaly-detectionauthenticationdefensive-tools+2
15 years ago
cve-2020-6864 preview

cve-2020-6864

GitHubgigachadusers/cve-2020-6864

Lightweight C++ scanner to detect ZTE devices vulnerable to CVE-2020-6864, enabling rapid identification of exploitable network targets.

exploitationinformation-gatheringnetwork-security+2
27 months ago
cve-2026-8697 preview

cve-2026-8697

GitHubitzmetanjim/cve-2026-8697

Detailed CVE-2026-8697 writeup with POC exploit for a login rate-limit bypass on TP-Link Archer C64 routers via a debug SSH service, enabling…

educationexploitationhardware-iot-security+7
15 months ago
network-security-snort preview

network-security-snort

GitHubtaisa456/network-security-snort

Snort 3 IDS → IPS lab on Kali. Custom detection rules + iptables enforcement against ICMP recon, Nmap SYN scans, Hydra FTP brute force, and vsftpd…

defensive-toolseducationexploitation+6
6 months ago
SonicWall-SMA1000-Zero-Day-IoC-Check preview

SonicWall-SMA1000-Zero-Day-IoC-Check

GitHubmrrawbit/sonicwall-sma1000-zero-day-ioc-check

Unofficial Bash IoC checker for SonicWall SMA1000 appliances affected by actively exploited CVE-2026-15409 and CVE-2026-15410.

exploitationforensicsincident-response+5
4 months ago
ioc-cve-2022-42475 preview

ioc-cve-2022-42475

GitHubbryanster/ioc-cve-2022-42475

test for the ioc described for FG-IR-22-398

configuration-auditingincident-responseioc-management+2
13 years ago
Kali-Metasploitable preview

Kali-Metasploitable

GitHubivoalbacete/kali-metasploitable

Escaneo de vulnerabilidades, análisis de tráfico con Wireshark y explotación controlada del CVE-2011-2523 (vsftpd 2.3.4) en entorno de red segura.

ctfeducationexploitation+9
6 months ago
Ripple20 preview

Ripple20

GitHubransc0rp1on/ripple20

This comprehensive package contains everything needed to detect, analyze, and remediate Ripple20 (CVE-2020-11898) vulnerabilities in your…

embedded-systems-securityfirmware-analysisiot-security+3
4 months ago
http2-security-lab preview

http2-security-lab

GitHubmadhantr0/http2-security-lab

HTTP/2 attack simulation & defense lab - Slowloris, Rapid Reset (CVE-2023-44487), HPACK Bomb attacks with 5 layered defenses. Built in pure Python…

defensive-toolseducationlabs-practice+4
5 months ago
Exploiting-a-vulnerability-using-reverse-shell preview

Exploiting-a-vulnerability-using-reverse-shell

GitHubdampedcoast/exploiting-a-vulnerability-using-reverse-shell

This project simulates a real-world attack-and-defend scenario across two virtual machines. You will exploit a critical pre-authentication RCE…
ctfeducationexploitation+5
5 months ago
Zero-day-scanning preview

Zero-day-scanning

GitHubanonymous-family/zero-day-scanning

Zero-day-scanning is a Domain Controller vulnerability scanner, that currently includes checks for Zero-day-scanning (CVE-2020-1472), MS-PAR/MS-RPRN…


exploitationnetwork-securitypenetration-testing+2
14 years ago
CVE-2026-0300 preview

CVE-2026-0300

GitHub0xblackash/cve-2026-0300

CVE-2026-0300

exploitationnetwork-securitypenetration-testing+3
16 months ago
cve-2026-0300-audit preview

cve-2026-0300-audit

GitHubtailwindrg/cve-2026-0300-audit

Read-only audit tooling for CVE-2026-0300 (PAN-OS User-ID Authentication Portal exposure)

cloud-infrastructure-securityconfiguration-auditingdevsecops+3
6 months ago
Previous1…878889…100Next
Sources curated into a security tool Repositories, feeds, communities and curated indexes flow through selection, classification, enrichment and translation into an illustrative tool record. ISC License Copyright (c) 2026 Lucide Icons and Contributors Permission to use, copy, modify, and/or distribute this software for any purpose with or without fee is hereby granted, provided that the above copyright notice and this permission notice appear in all copies. THE SOFTWARE IS PROVIDED "AS IS" AND THE AUTHOR DISCLAIMS ALL WARRANTIES WITH REGARD TO THIS SOFTWARE INCLUDING ALL IMPLIED WARRANTIES OF MERCHANTABILITY AND FITNESS. IN NO EVENT SHALL THE AUTHOR BE LIABLE FOR ANY SPECIAL, DIRECT, INDIRECT, OR CONSEQUENTIAL DAMAGES OR ANY DAMAGES WHATSOEVER RESULTING FROM LOSS OF USE, DATA OR PROFITS, WHETHER IN AN ACTION OF CONTRACT, NEGLIGENCE OR OTHER TORTIOUS ACTION, ARISING OUT OF OR IN CONNECTION WITH THE USE OR PERFORMANCE OF THIS SOFTWARE. --- The following Lucide icons are derived from the Feather project: airplay, alert-circle, alert-octagon, alert-triangle, aperture, arrow-down-circle, arrow-down-left, arrow-down-right, arrow-down, arrow-left-circle, arrow-left, arrow-right-circle, arrow-right, arrow-up-circle, arrow-up-left, arrow-up-right, arrow-up, at-sign, calendar, cast, check, chevron-down, chevron-left, chevron-right, chevron-up, chevrons-down, chevrons-left, chevrons-right, chevrons-up, circle, clipboard, clock, code, columns, command, compass, corner-down-left, corner-down-right, corner-left-down, corner-left-up, corner-right-down, corner-right-up, corner-up-left, corner-up-right, crosshair, database, divide-circle, divide-square, dollar-sign, download, external-link, feather, frown, hash, headphones, help-circle, info, italic, key, layout, life-buoy, link-2, link, loader, lock, log-in, log-out, maximize, meh, minimize, minimize-2, minus-circle, minus-square, minus, monitor, moon, more-horizontal, more-vertical, move, music, navigation-2, navigation, octagon, pause-circle, percent, plus-circle, plus-square, plus, power, radio, rss, search, server, share, shopping-bag, sidebar, smartphone, smile, square, table-2, tablet, target, terminal, trash-2, trash, triangle, tv, type, upload, x-circle, x-octagon, x-square, x, zoom-in, zoom-out The MIT License (MIT) (for the icons listed above) Copyright (c) 2013-present Cole Bemis Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction, including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to do so, subject to the following conditions: The above copyright notice and this permission notice shall be included in all copies or substantial portions of the Software. THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.
Repositories
GitHub & GitLab
Security feeds
Blogs, RSS & Atom
Communities
Social & submissions
Curated indexes
Security lists & trends
Curate & classify
Enrich & translate
Fictional tool and repository. The description, categories, stars, forks and views are illustrative examples, not live or verified data. Fictional tool and repository. The description, categories, stars, forks and views are illustrative examples, not live or verified data. {"fictional":true,"name":"Tool","version":"1.0.1","repository":"owner/tool","live_metrics":false,"example_metrics":{"stars":1200,"forks":128,"views":8600}}
Tool
owner/tool v1.0.1
Discover assets and review HTTP security headers.
Reconnaissance
Web security
1,200 stars — Fictional example1.2k 128 forks — Fictional example128 8,600 views — Fictional example8.6k