

Terrminus-CVE-2026-2406
 ridpath/terrminus-cve-2026-2406
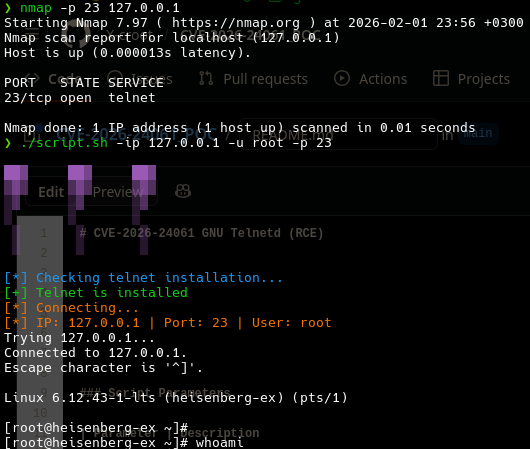
AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…
exploitationinformation-gatheringiot-security+8
2
ridpath/terrminus-cve-2026-2406AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…
 cmaruti/reports
Curated vulnerability disclosure reports with CVE mappings, covering SQLi, XSS, authentication bypass, and DoS in web applications and network…
 abraxas/pfsense-api-enroll-json-ssh
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - Privilege leftover - example-add-devices.py JSON into SSH
 mxypoo/cve-2016-3116-dropbearssh
 varangamin/cve-2017-6206
The DGS-1510 Websmart switch series firmware has been found to have security vulneratiblies. The vulnerabilities include unauthenticated command…
 corelight/zeek-gozi-detector
A Zeek based Gozi banking malware detector.
 abraxas/pfsense-api-example-ssl-verify
pfSense Plus MIM API toolkit b4acd7ca - Medium - Remote - Privilege leftover - official samples verify_ssl=False
 r3verii/cve-2026-33555
One zero-byte QUIC packet is enough to desynchronize HAProxy's backend connection pool and smuggle HTTP requests across unrelated users — even users…
 abraxas/pfsense-api-enroll-autoadd
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - Privilege leftover - Paramiko AutoAddPolicy enroll
 cumakurt/tscan
Python-based scanner that detects and exploits CVE-2026-24061 telnetd authentication bypass, enabling root shell access on vulnerable GNU Inetutils…
 x-croot/cve-2026-24061_poc
POC Script for CVE-2026-24061 (GNU Telnetd Exploit)
 istagmbh/cve-2024-53704
demonstriert, wie mittels missbräuchlicher Nutzung eines Swap-Cookies eine VPN-Session übernommen werden kann. Wichtig: Dieses Projekt dient…
 vinylrider/ivantiunlocker
Prevent CVE-2025-22457 and other security problems with Juniper/Ivanti Secure Connect SSL VPN
 flamebarke/nmap-printer-nse-scripts
NSE port of CVE-2022-1026 exploit for mass identification and exploitation
 bybravehq/ip2
Maintained fork of node-ip with the unpatched SSRF advisory (CVE-2024-29415) fixed
 cybersecuritist/cve-2024-21754-forti-rce
Exploit for CVE-2024-21754 targeting insufficient password hashing in FortiOS and FortiProxy, enabling privileged attackers to decrypt backup files…
 julixsalas/cve-2020-0796
Metasploit Auxiliary module for scanning and detecting CVE-2020-0796 (SMBGhost) vulnerability in Windows SMBv3 implementations.
 keraattin/cve-2026-34197
Detects Apache ActiveMQ Classic RCE (CVE-2026-34197) via Jolokia API with Python and Nmap NSE scripts, checking unauthenticated access and version…