
enum4linux
 ciscocxsecurity/enum4linux
enum4Linux is a Linux alternative to enum.exe for enumerating data from Windows and Samba hosts
information-gatheringnetwork-securityosint+2
1.4k
ciscocxsecurity/enum4linuxenum4Linux is a Linux alternative to enum.exe for enumerating data from Windows and Samba hosts
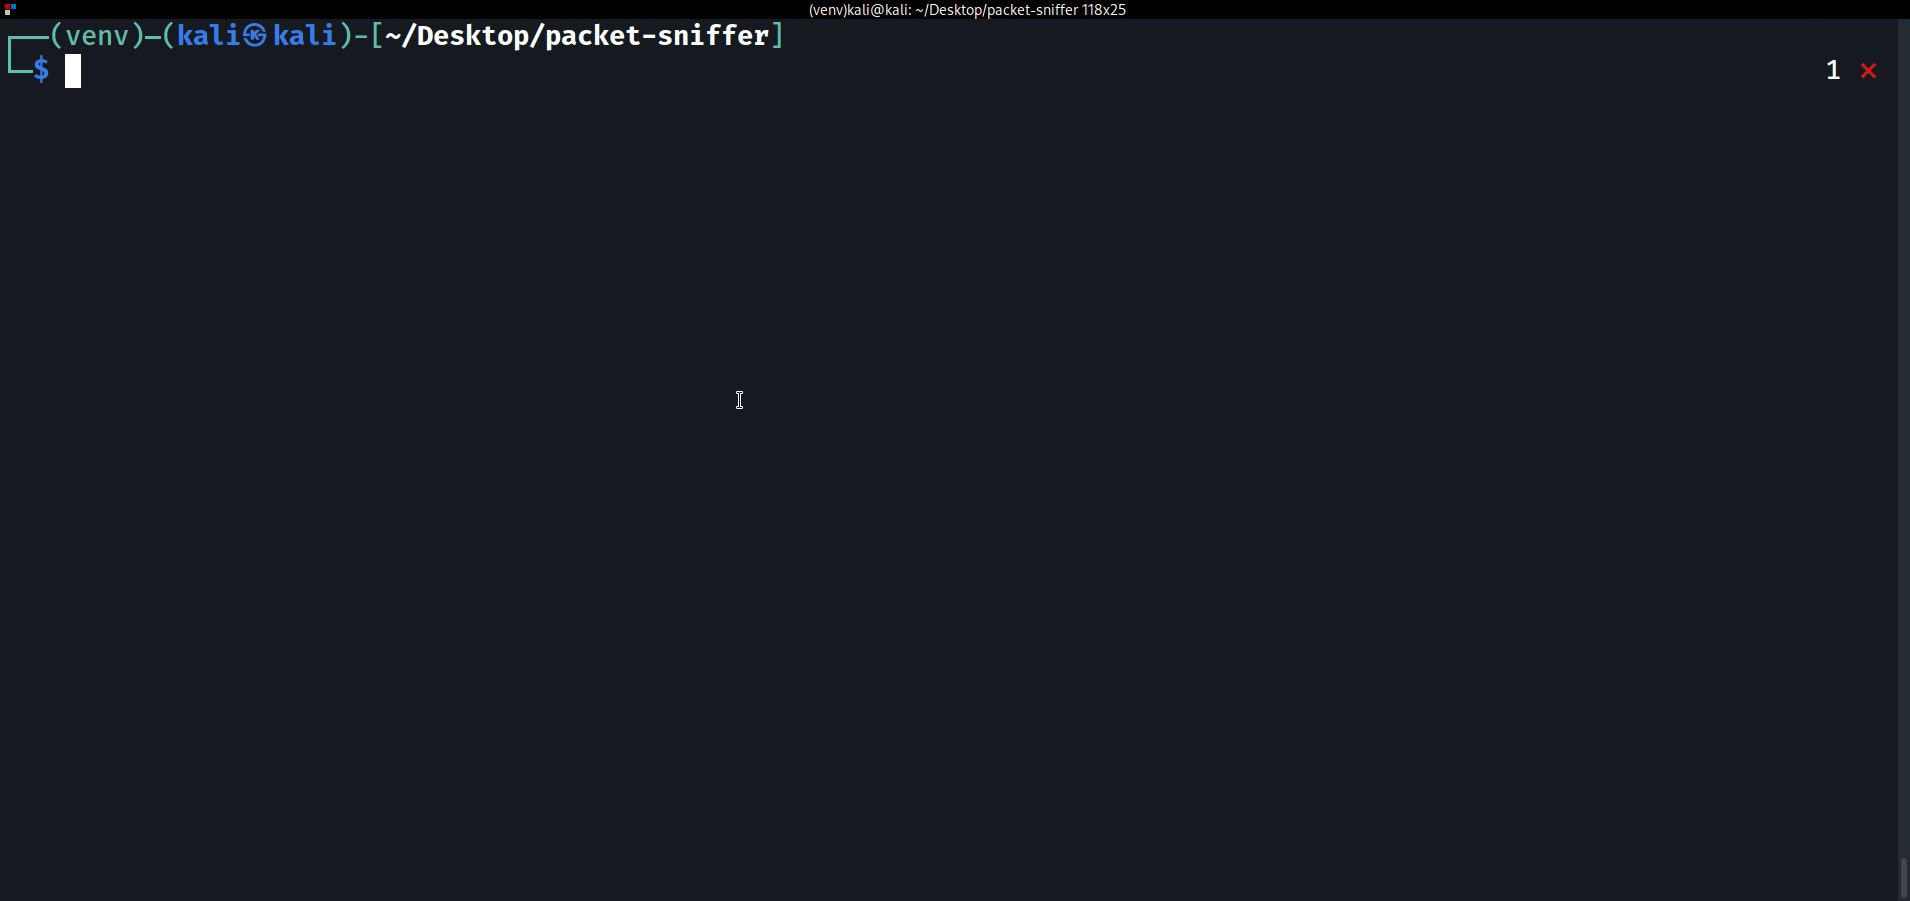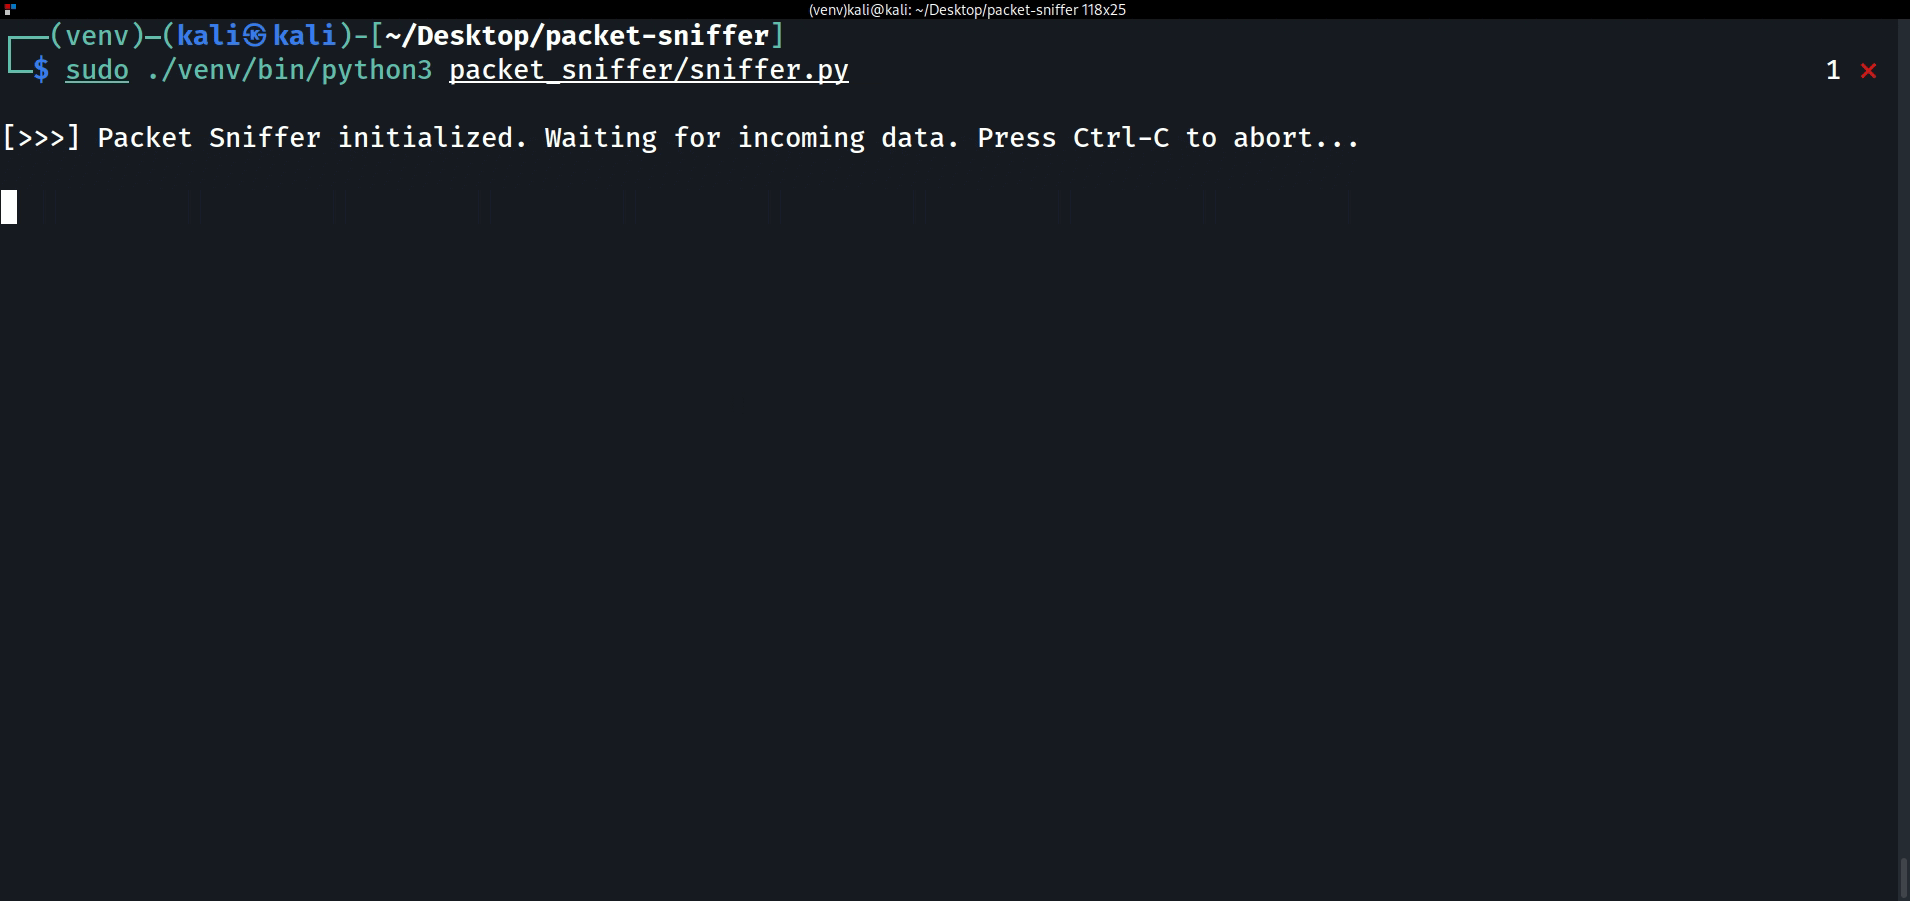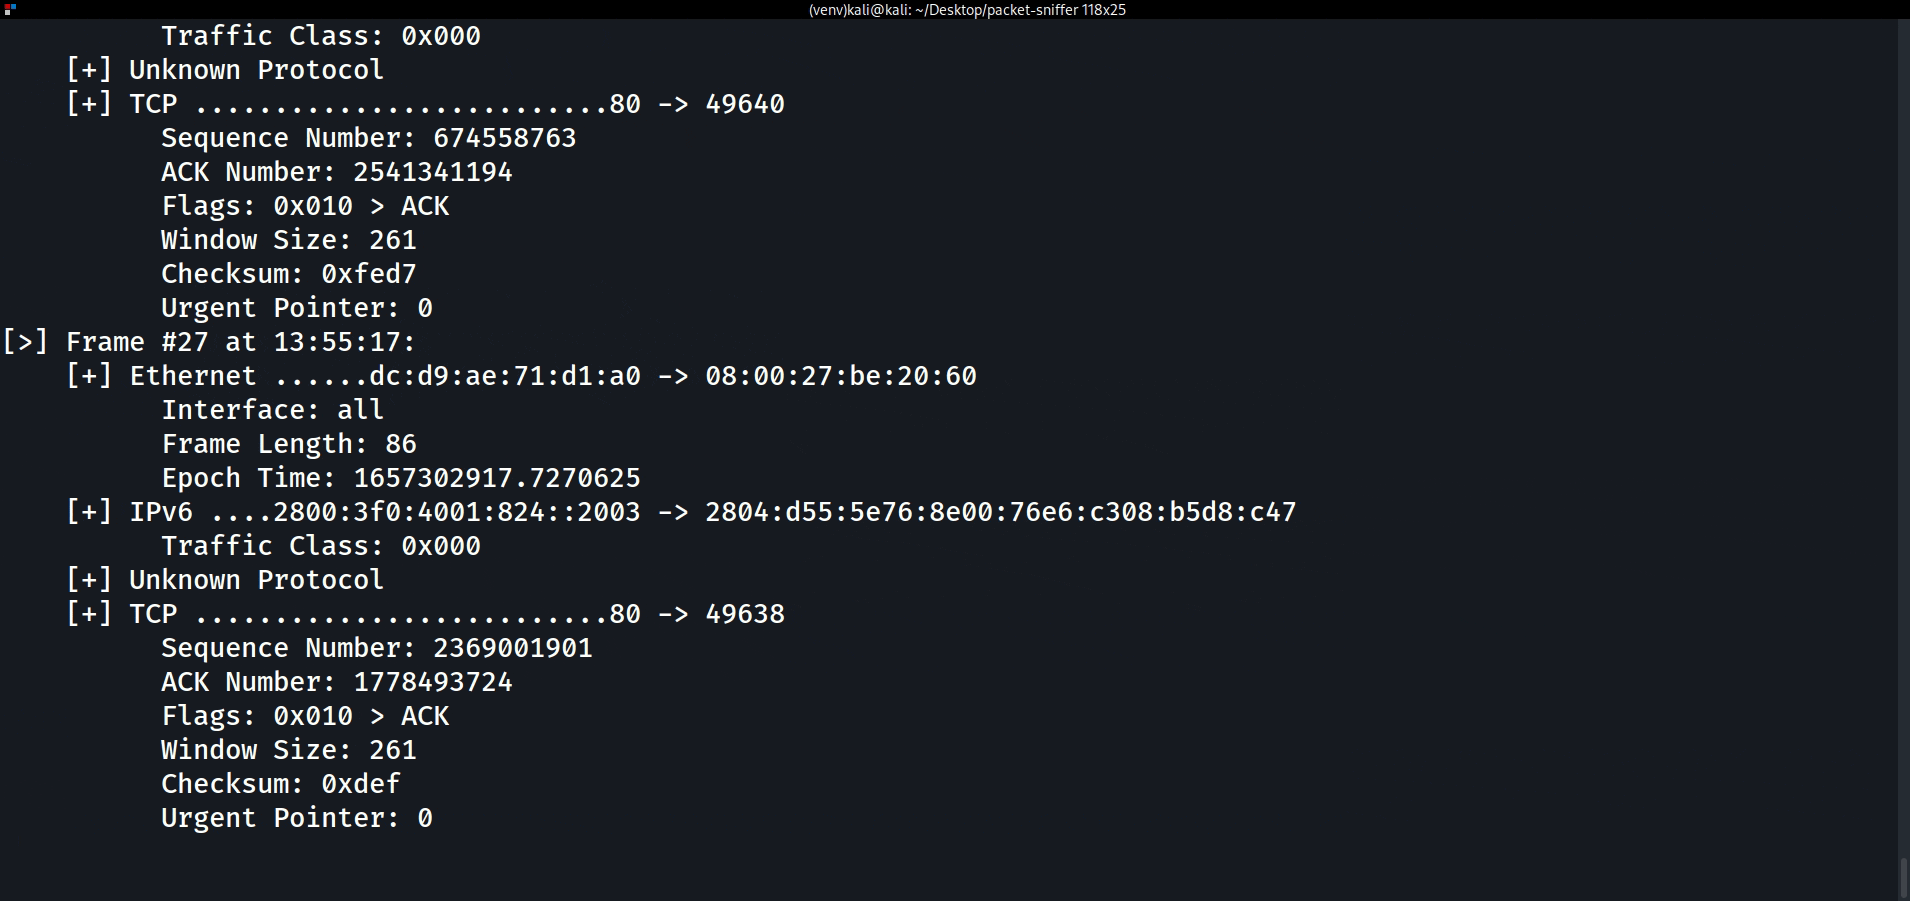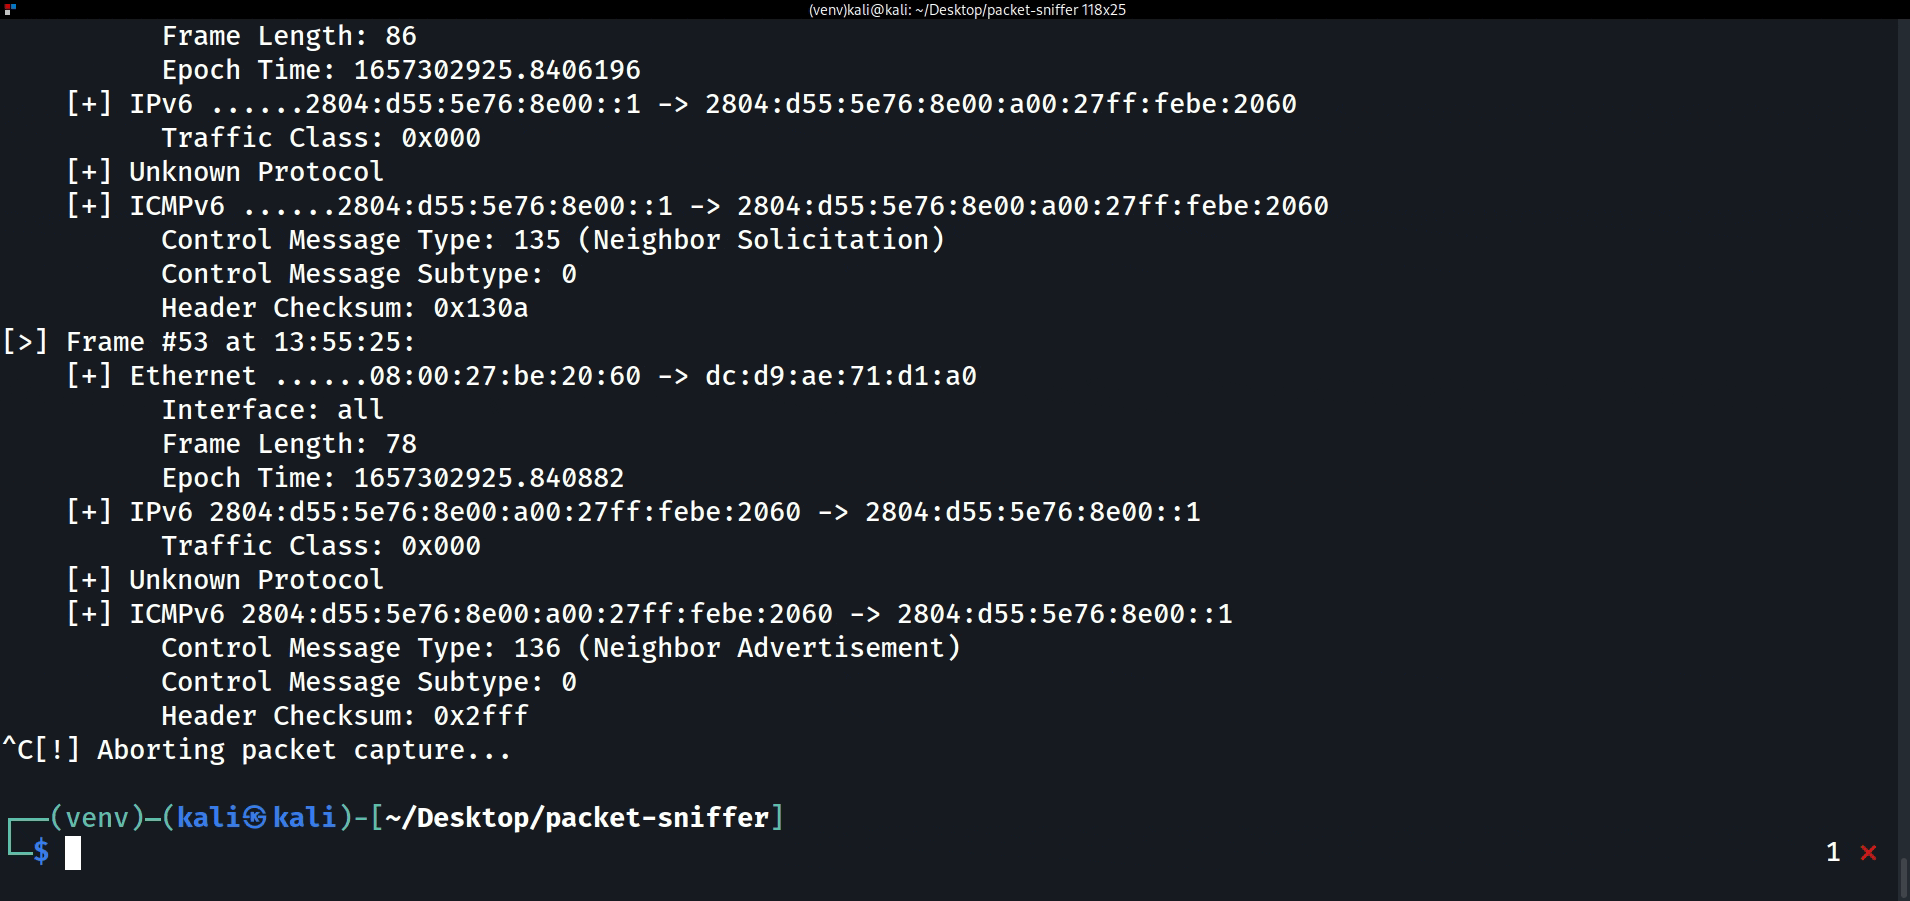 eonraider/packet-sniffer
Raw socket-based network packet sniffer that captures and disassembles TCP/IP packets from network interfaces for security analysis and educational…
 volexity/threat-intel
Signatures and IoCs from public Volexity blog posts.
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
 phaethon/kamene
Network packet and pcap file crafting/sniffing/manipulation/visualization security tool. Originally forked from scapy in 2015 and providing python3…
 netzob/netzob
Open-source toolkit for reverse engineering, modeling, and fuzzing communication protocols. Infers message formats and state machines from network…
 moxie0/chapcrack
Parses and decrypts MS-CHAPv2 handshakes from PPTP VPN and WPA2 Enterprise captures, extracting credentials for offline cracking via CloudCracker.
 aerleon/aerleon
Generate firewall ACLs for Cisco, Juniper, Palo Alto, and more from a single YAML policy language via CLI or Python API.
 batfish/pybatfish
Python client for Batfish, a network configuration analysis tool that validates security, reliability, and compliance by modeling network behavior…
 shirkdog/pulledpork
Pulled Pork for Snort and Suricata rule management (from Google code)
 cryptolok/ghostinthenet
Ultimate Network Stealther that makes Linux a Ghost In The Net and protects from MITM/DOS/scan
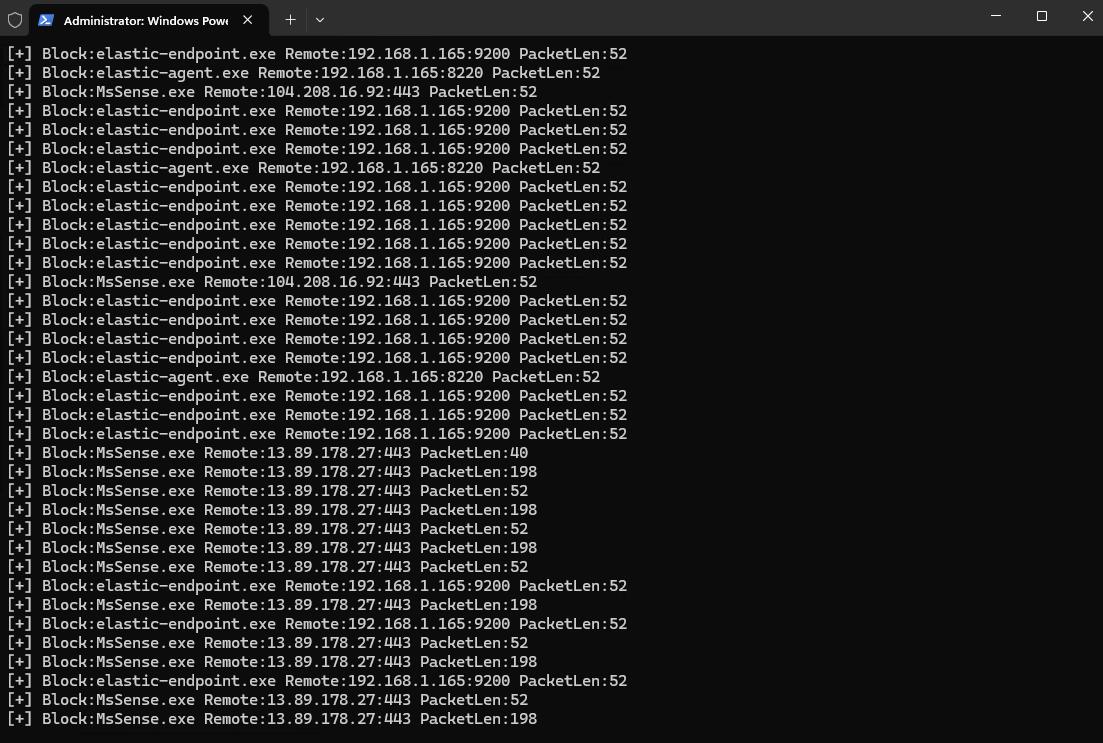 senzee1984/edrprison
Leverage a legitimate WFP callout driver to prevent EDR agents from sending telemetry
 robertdavidgraham/isowall
This is a mini-firewall that completely isolates a target device from the local network.
 pwnfoo/ntlmrecon
Enumerate information from NTLM authentication enabled web endpoints 🔎
 360netlab/dga
Suspicious DGA from PDNS and Sandbox.
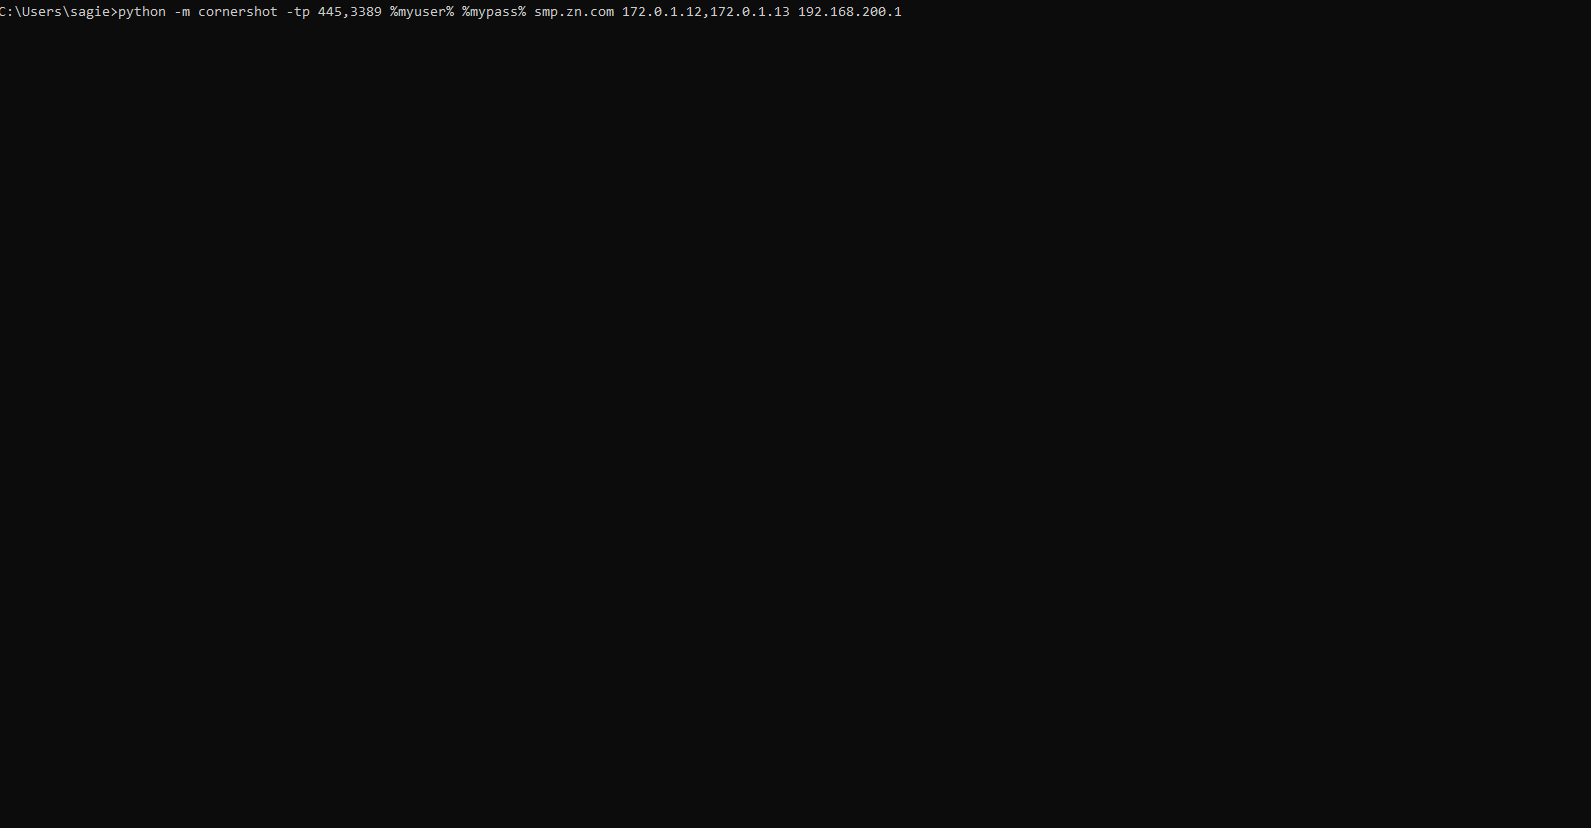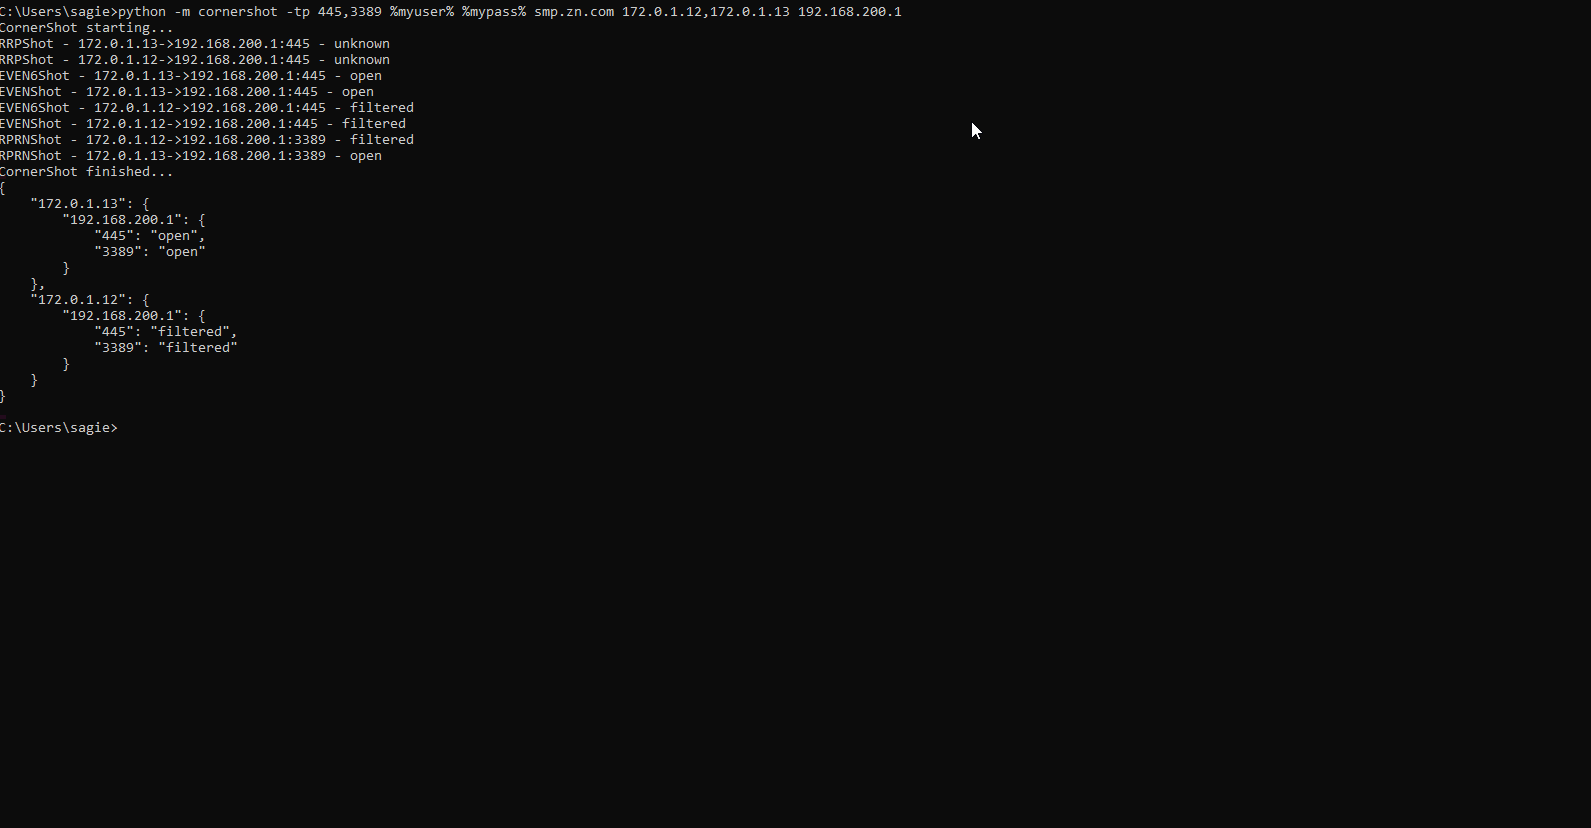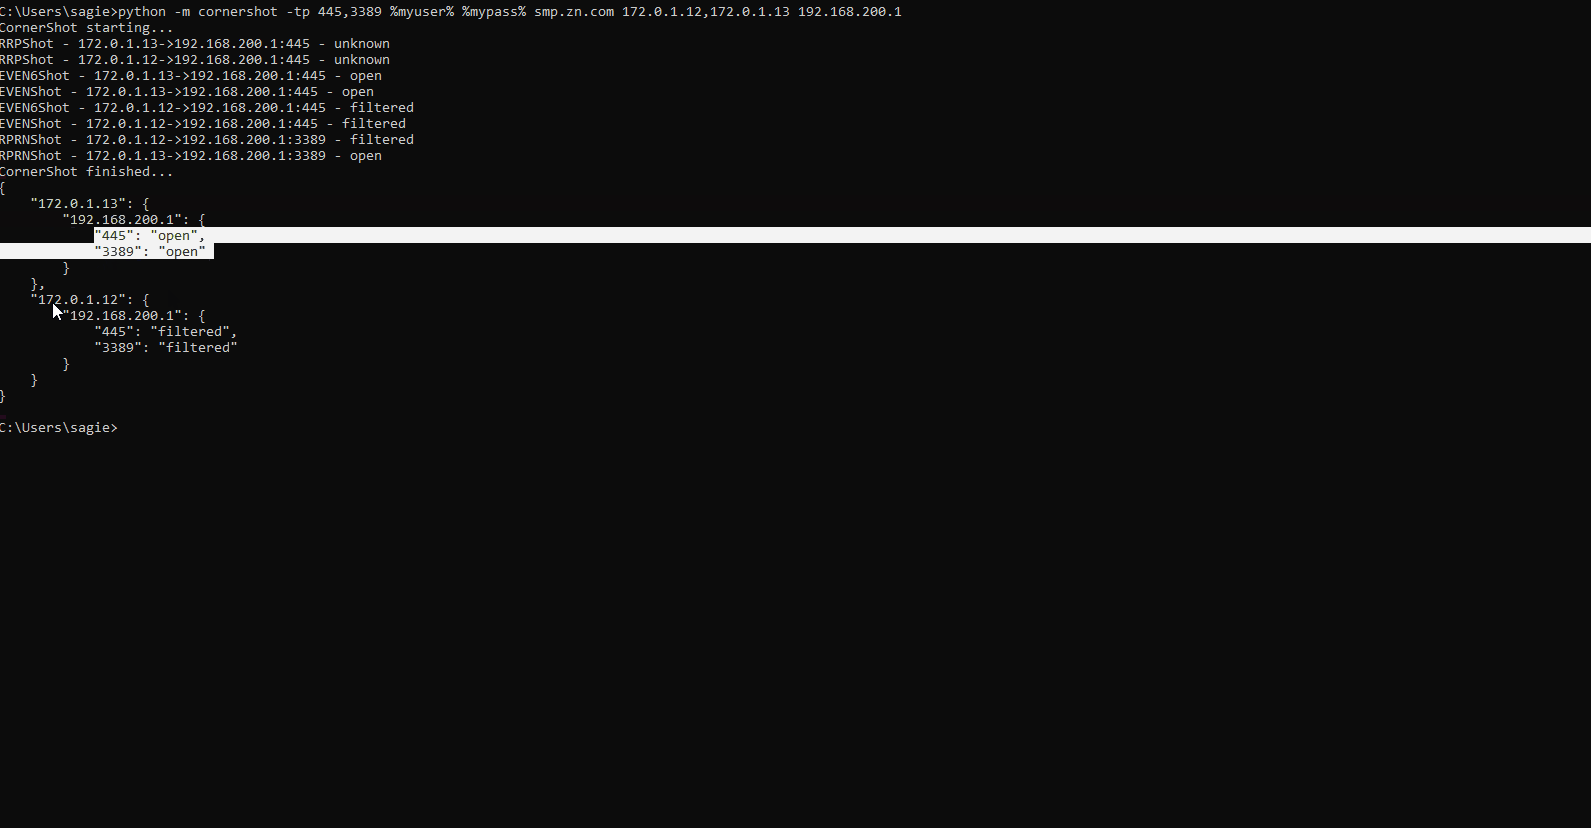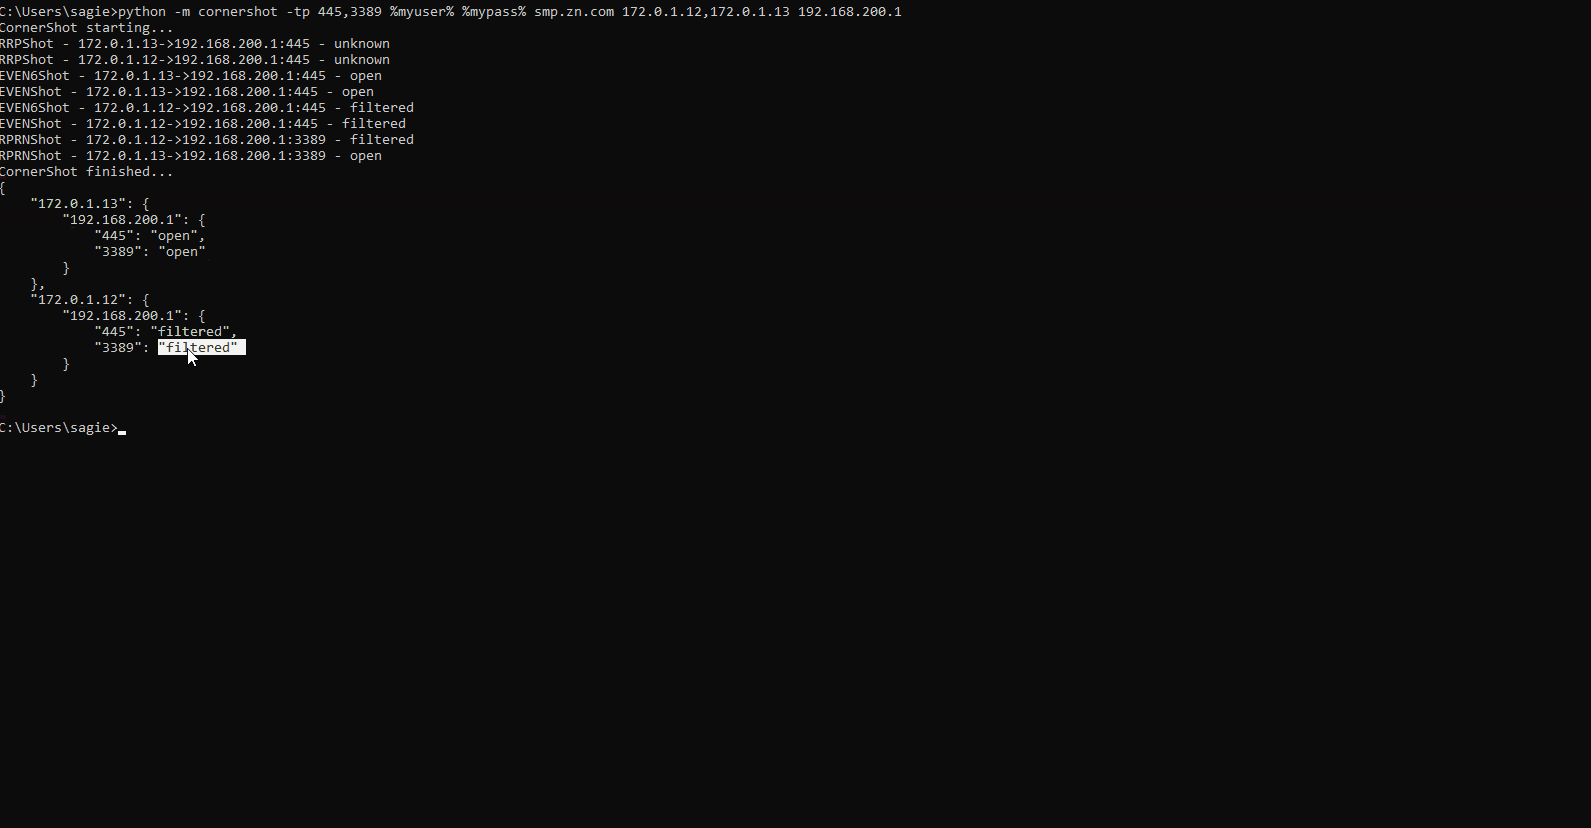 zeronetworks/cornershot
Amplify network visibility from multiple POV of other hosts
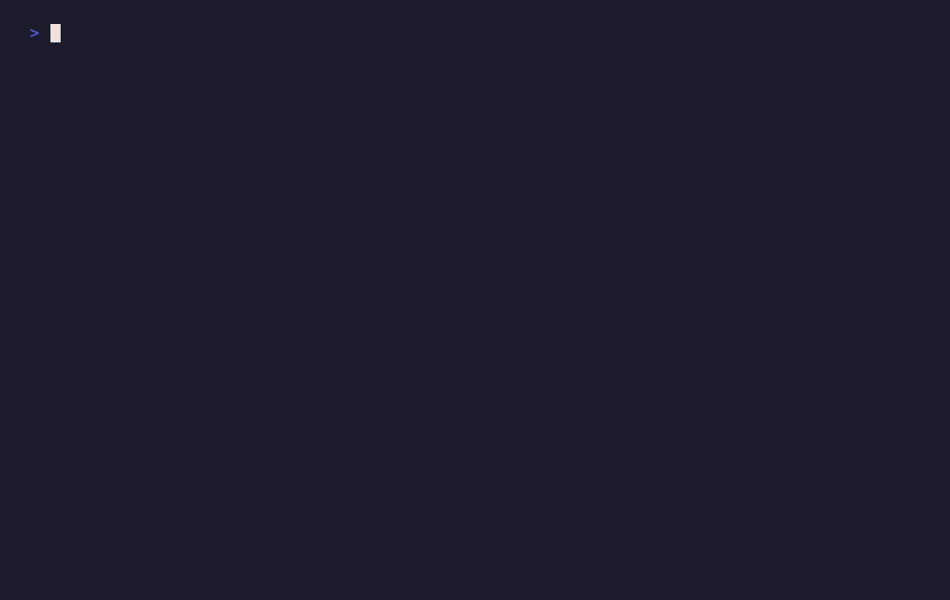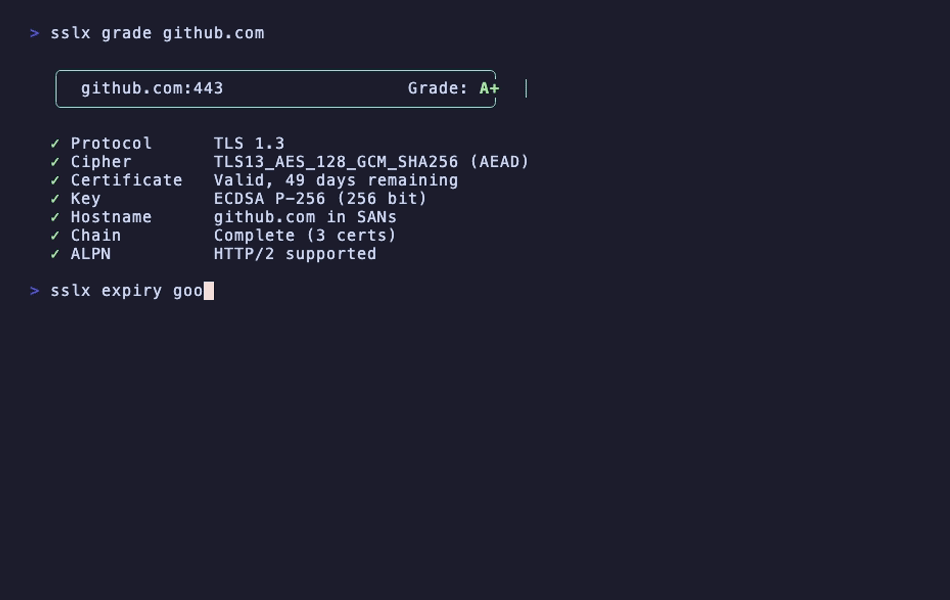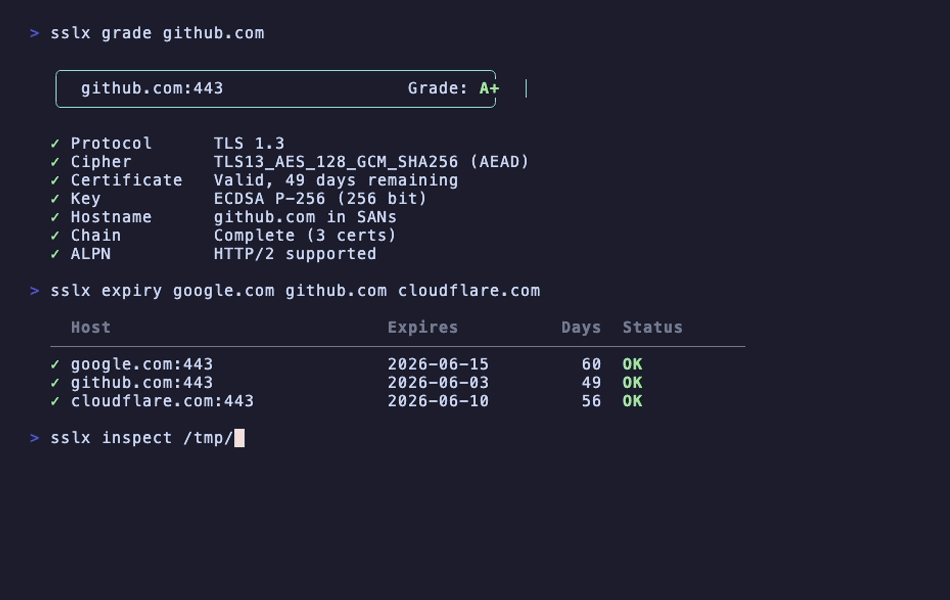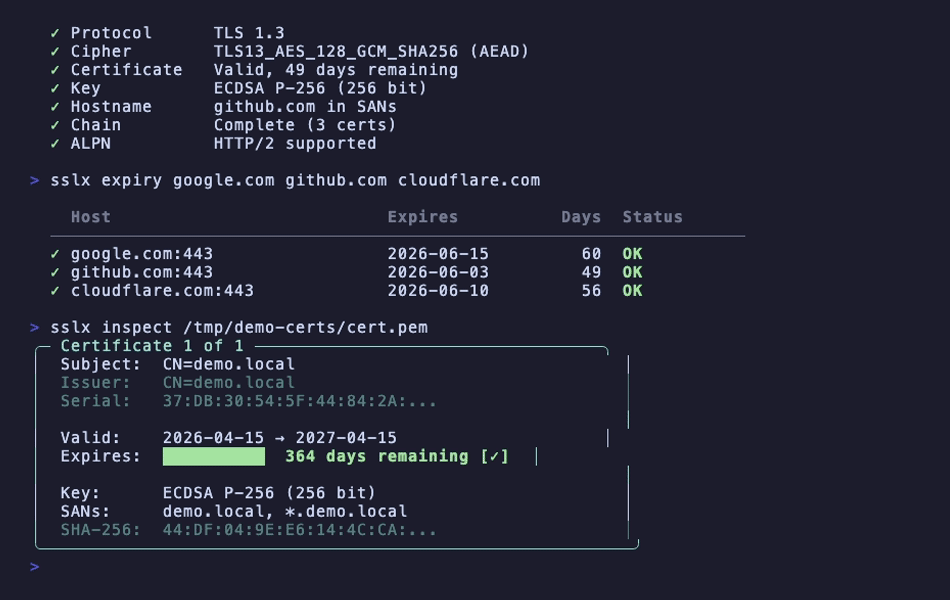 glincker/sslx
A fast, modern alternative to OpenSSL's CLI - inspect, grade, and manage certificates from the terminal
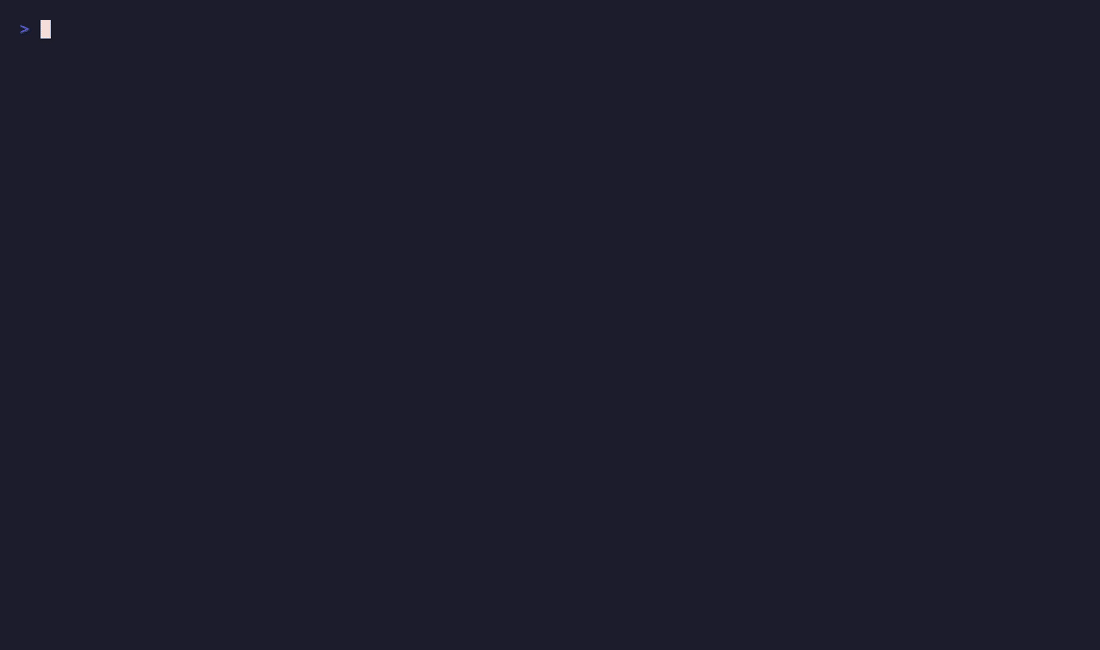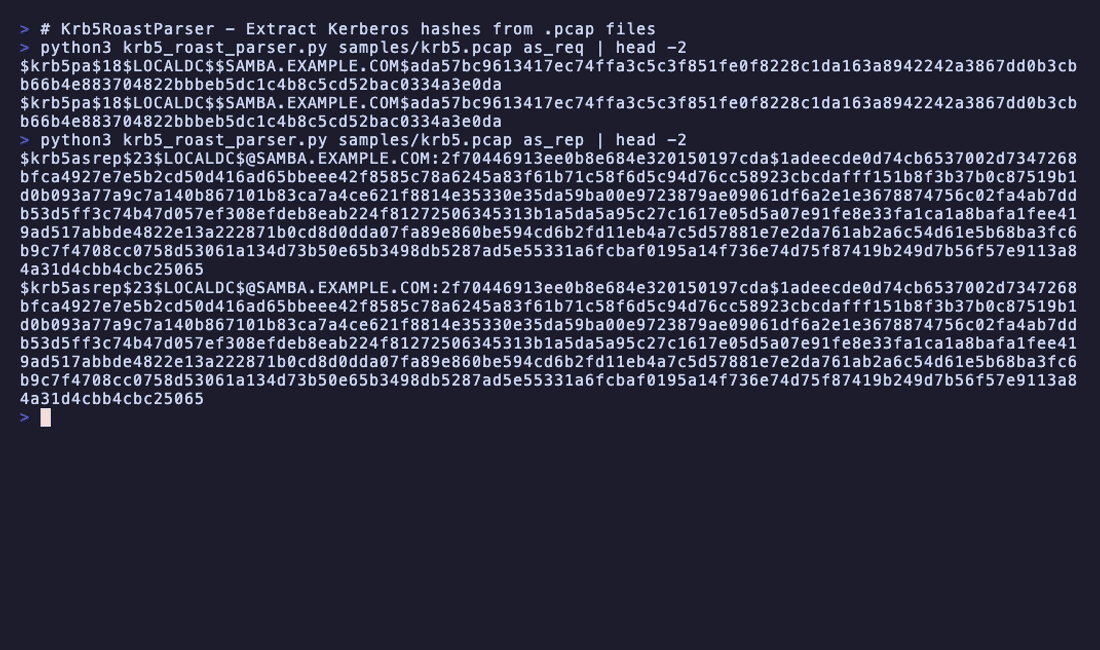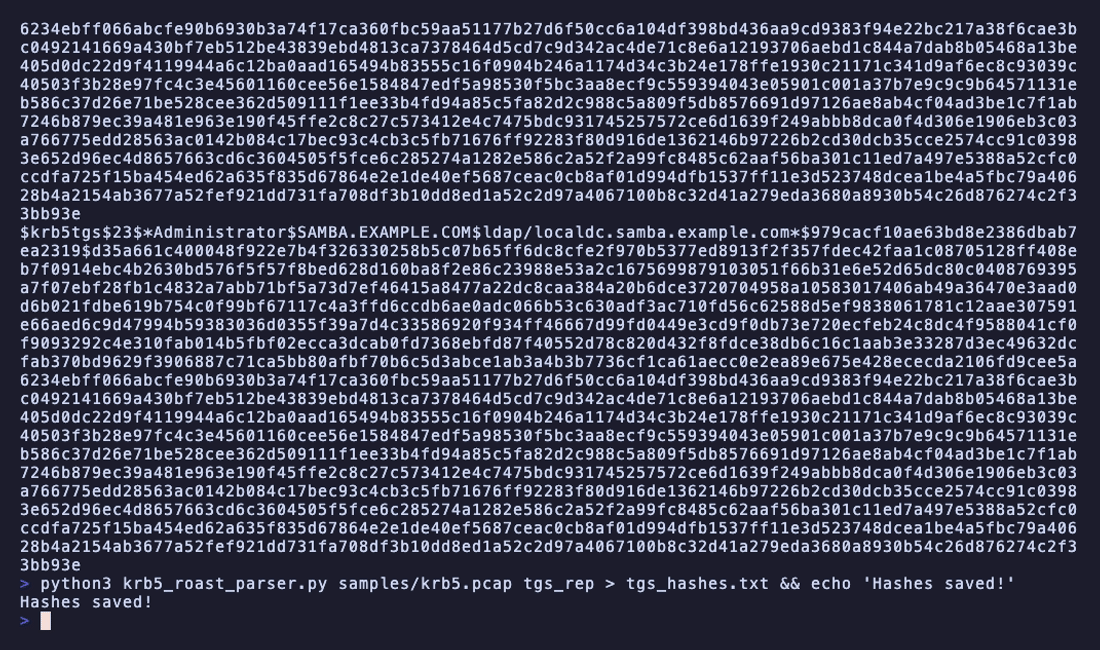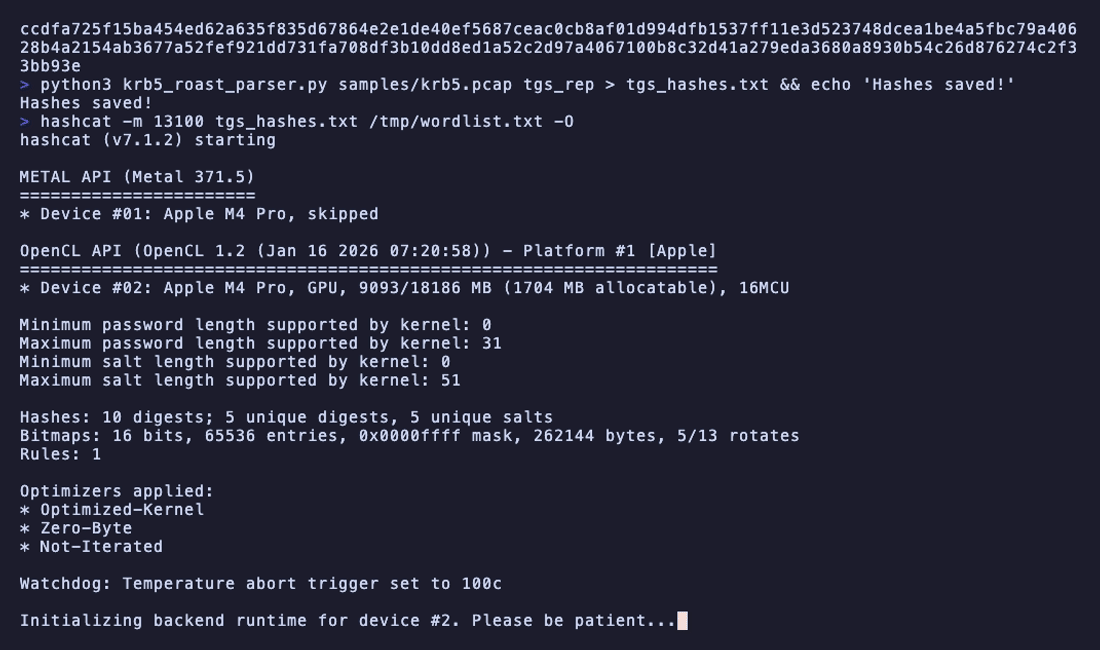 jalvarezz13/krb5roastparser
KrbRoastParser is a tool for parsing Kerberos packets from pcap files to extract AS-REQ, AS-REP and TGS-REP hashes