external_curl_AOSP10_r33_CVE-2021-22924

Command-line tool and library for transferring data using URL syntax, supporting various protocols including HTTP, FTP, and more.

Command-line tool and library for transferring data using URL syntax, supporting various protocols including HTTP, FTP, and more.

Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…

Hackable HTTP proxy for resiliency testing and simulated network conditions

A secure low code deception runtime framework, leveraging AI for System Virtualization.

Open-source MITM proxy to intercept, inspect, and mock network traffic.

HTTP/HTTPS proxy over SSH

Mallet is an intercepting proxy for arbitrary protocols

Set of tools for security testing of Internet of Things devices using specific network IoT protocols

CVE-2024-38200 & CVE-2024-43609 - Microsoft Office NTLMv2 Disclosure Vulnerability

Open Source Implementation of Cobalt Strike's Malleable C2

Knocker, a knock based access control service for your homelab

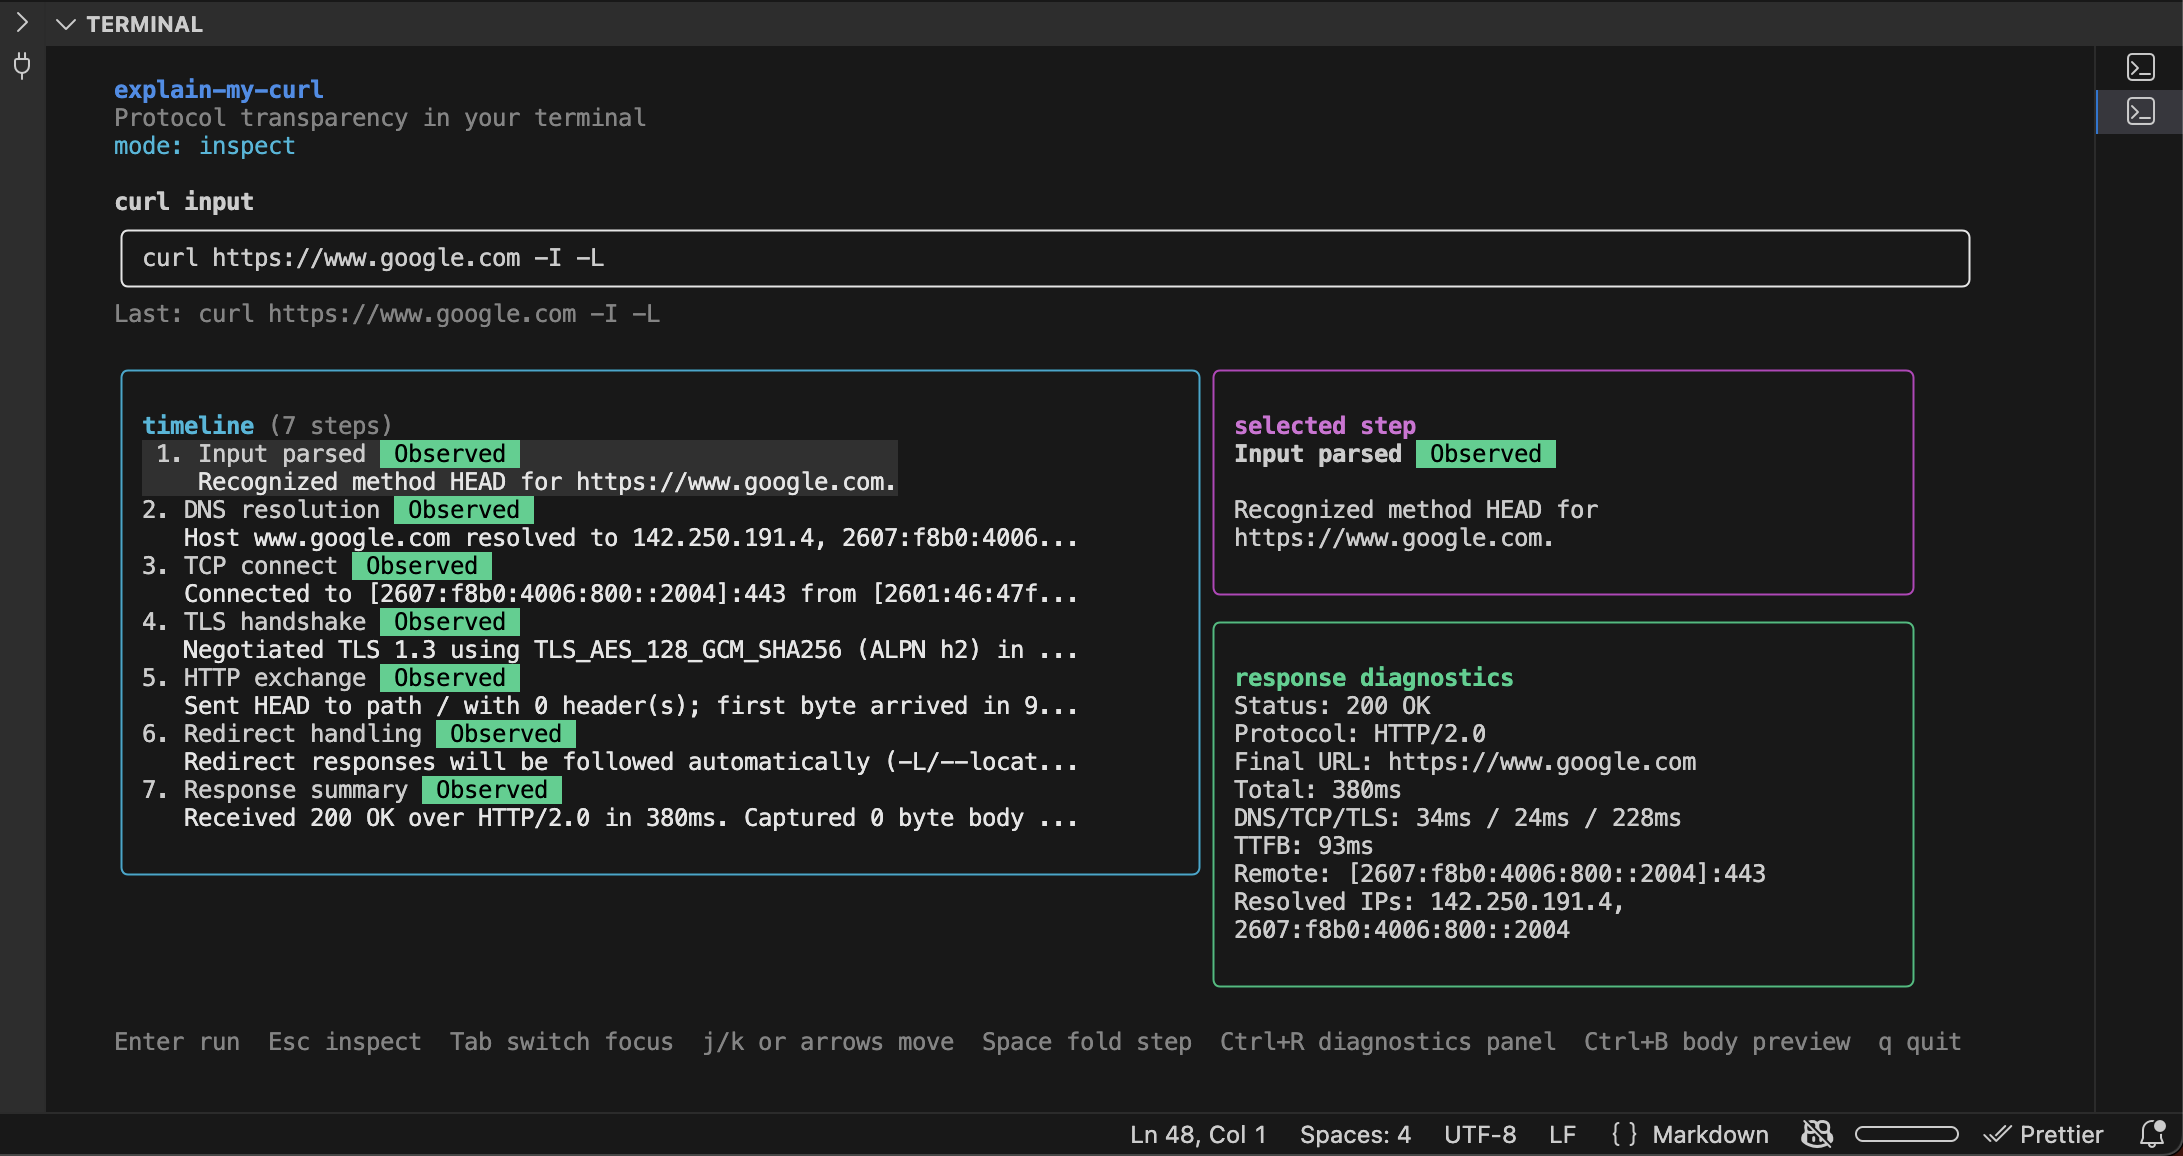
Takes a curl command and explains DNS/TLS/HTTP details step-by-step

Cisco RV110w UPnP stack overflow

CVE-2018-13379 Script for Nmap NSE.

✨ HAProxy ve Keepalived konusunu load balancer ve cluster'a ek olarak güvenlik(zayıf SSL/Kripto Kullanımı (LOGJAM) (CVE-2015-4000) zafiyeti önlemi)…


Behavioral detection script for CVE-2026-42945 (NGINX Rift) — heap overflow in ngx_http_rewrite_module. No RCE, crash-based detection only.