Exploiting-a-vulnerability-using-reverse-shell

This project simulates a real-world attack-and-defend scenario across two virtual machines. You will exploit a critical pre-authentication RCE…

This project simulates a real-world attack-and-defend scenario across two virtual machines. You will exploit a critical pre-authentication RCE…

Python scanner to identify systems vulnerable to CVE-2020-0796 (SMBv3 RCE) by sending crafted negotiate requests and checking for the flaw.

Exploit for CVE-2024-47176 targeting CUPS printing service vulnerability. Enables remote code execution and privilege escalation on affected…

Analysis of network scan results, service vulnerabilities, OS fingerprinting, and critical Nessus findings including Ghostcat (CVE-2020-1938).

regreSSHion is a security tool designed to test for vulnerabilities related to CVE-2024-6387, specifically focusing on SSH and remote access…

A critical flaw has been discovered in Erlang/OTP's SSH server allows unauthenticated attackers to gain remote code execution. One malformed SSH…

Command-line tool and library for transferring data using URL syntax, supporting various protocols including HTTP, FTP, and more.

libpcap-based TCP packet sniffer that decodes HTTP traffic, reassembles streams, and emits customizable access-log style output with request/response…

Portable OpenSSH

HTTP(S)/WS(S)/TCP Tunnels to localhost using only SSH.


Remote Desktop Protocol in Twisted Python

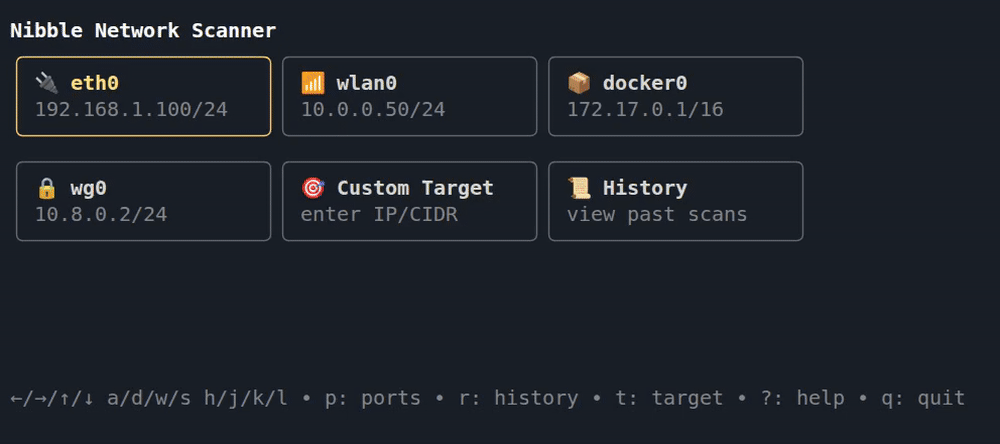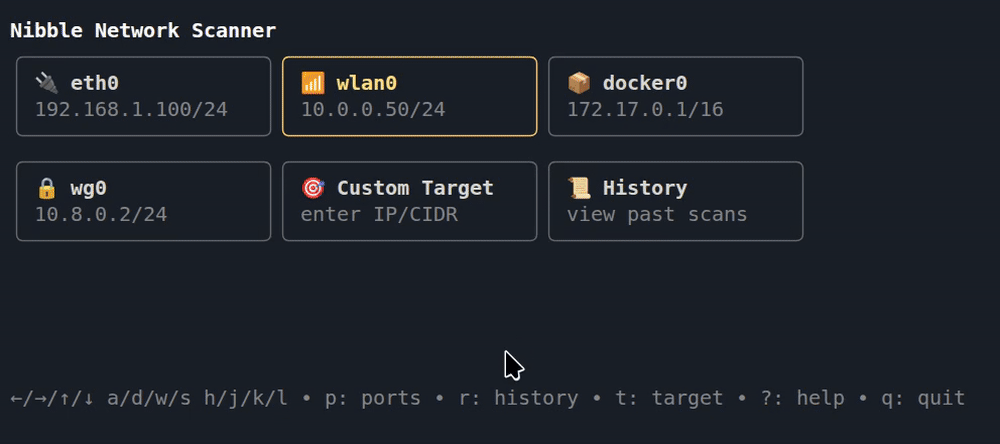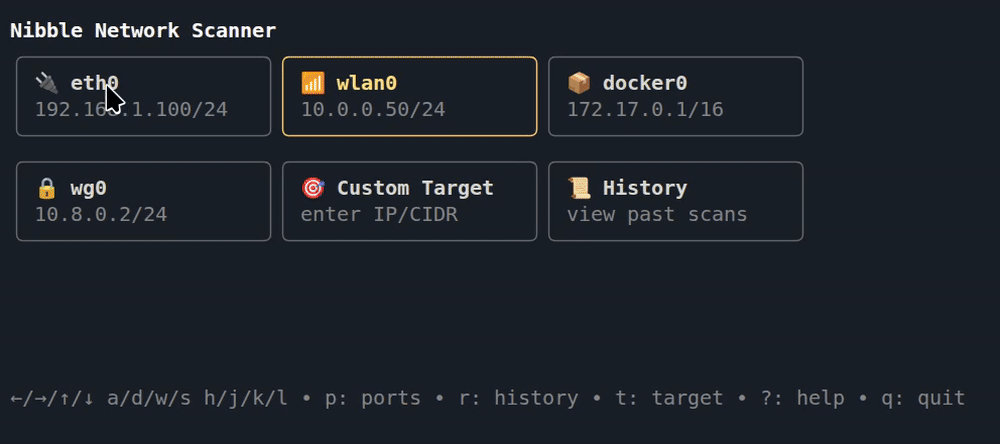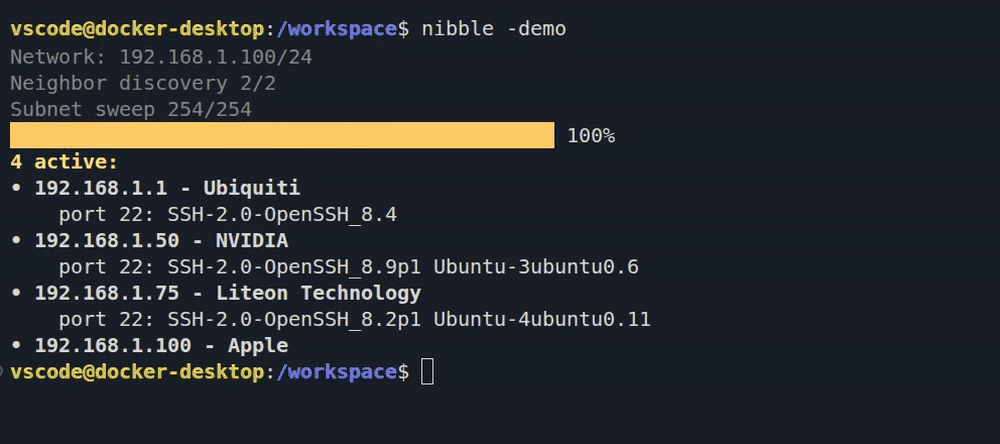
easy to use network scanner, with a clickable tui interface

Virtual machines manipulation framework

A swiss-knife MCP server for analysing PCAP files

Check vuln CVE 2019-0708

CVE-2004-2687 (Distcc 3.2.1) exploitation, methodology & remediation — Metasploitable2 lab

Challange CVE-2020-13777