

GPEWebDefender
 gopasteverything/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
defensive-toolsincident-responseinformation-gathering+8
2
gopasteverything/gpewebdefenderLightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.

 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
 gcla/termshark
A terminal UI for tshark, inspired by Wireshark
 google/gopacket
Provides packet processing capabilities for Go

 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
 netsniff-ng/netsniff-ng
A Swiss army knife for your daily Linux network plumbing.
 cyb3r-monk/rita-j
Implementation of RITA (Real Intelligence Threat Analytics) in Jupyter Notebook with improved scoring algorithm.
 leonward/openfpc
OpenFPC, Open Source Full Packet Capture
 halildeniz/networkassessment
NetworkAssessment: Network Compromise Assessment Tool
 corelight/zeek-community-id
Zeek support for Community ID flow hashing.
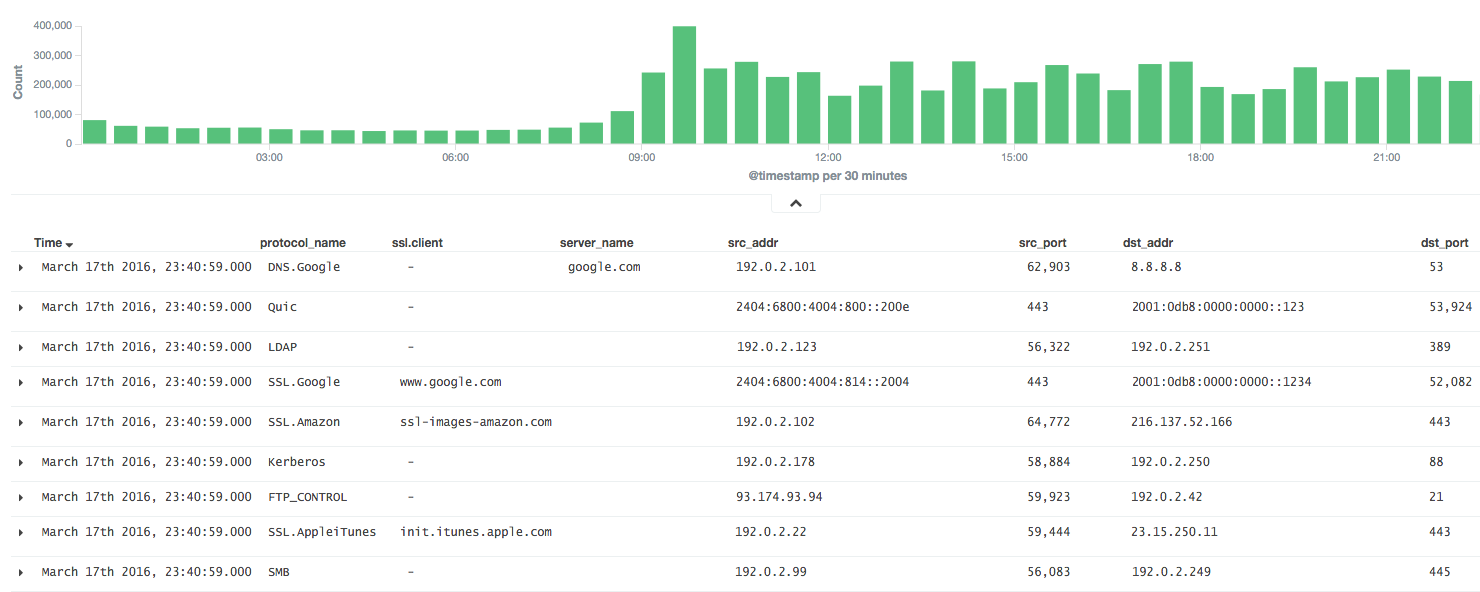 knqyf263/ndff
A flow-based network monitor with Deep Packet Inspection
 corelight/zeek-spicy-ipsec
A Zeek IPSec protocol analyzer based on Spicy.
 corelight/zeek-spicy-wireguard
A Zeek Wireguard protocol analyzer based on Spicy.
 corelight/zeek-quic
Bro analyzer that detects Google's QUIC protocol
 corelight/zeek-spicy-ospf
A Zeek OSPF packet analyzer based on Spicy.
 nccgroup/baskerville
Selective protocol extractor from PCAPs or interfaces
 corelight/corelightforsplunk
Splunk app for integrating and analyzing Corelight network detection data, enabling real-time threat hunting and incident response.