

CVE-2024-3596-Detector
 alperenugurlu/cve-2024-3596-detector
Detects CVE-2024-3596 in RADIUS/UDP traffic by analyzing MD5 collisions in Access-Request packets, helping administrators identify vulnerable…
authenticationcryptographynetwork-security+3
7
alperenugurlu/cve-2024-3596-detectorDetects CVE-2024-3596 in RADIUS/UDP traffic by analyzing MD5 collisions in Access-Request packets, helping administrators identify vulnerable…
 corelight/cve-2022-21907
Zeek package to detect CVE-2022-21907 HTTP exploit attempts by analyzing packet captures for malformed requests and triggering alerts.
 thack1/cve-2022-21449
Zeek script to detect exploitation attempts of CVE-2022-21449 targeting TLS clients
 lakshmirnr/cve-2024-51179
Proof-of-concept exploit for CVE-2024-51179: crafted PFCP packet flooding causes denial of service in Open5GS UPF/SMF, disrupting 5G core PDU session…
 corelight/zeek-mercury-npf
Zeek plugin generating Mercury NPF fingerprints for TCP, TLS/DTLS, QUIC, HTTP, SSH, OpenVPN, and STUN to support network security monitoring.
 themson/shellshock
scripts associate with bourne shell EVN function parsing vulnerability CVE-2014-6271
 lixiang957/cve-2021-33959
Proof-of-concept exploit for CVE-2021-33959 demonstrating UDP reflection amplification attack against Plex Media Server via crafted M-SEARCH packets…
 wrong-commit/cve-2010-4669
Python-based exploit for CVE-2010-4669 using Scapy to send crafted packets for network vulnerability testing. Requires root and Python 2.
 freddierice/cve-2020-35498-flag
C-based exploit tool to detect and trigger CVE-2020-35498 via raw socket injection with BPF filter, targeting wireless interfaces for vulnerability…
 dlee35/curveball_lua
Repo containing lua scripts and PCAP to find CVE-2020-0601 exploit attempts via network traffic
 bl4ck5un/cve-2013-4348
DOS (infinite loop) attack via a small value in the IHL field of a packet with IPIP encapsulation
 evilsocket/bettercap
DEPRECATED, bettercap developement moved here: https://github.com/bettercap/bettercap
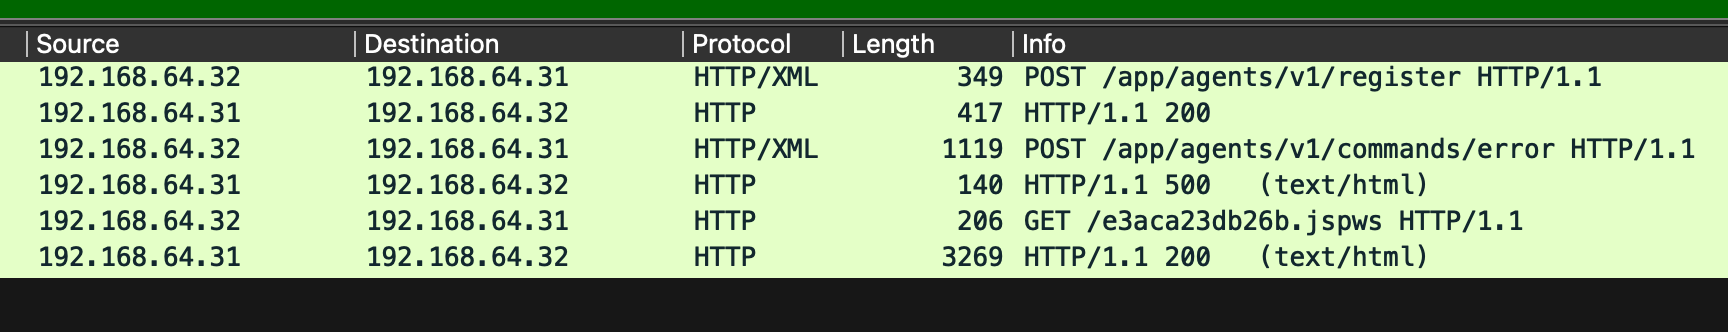 boredhackerblog/teamcity-cve-2026-63077-pcap
teamcity teamcity-CVE-2026-63077 exploitation pcap
 oisf/libhtp
Security-aware HTTP protocol parser library used by IDS/IPS engines to inspect and normalize HTTP traffic for threat detection.
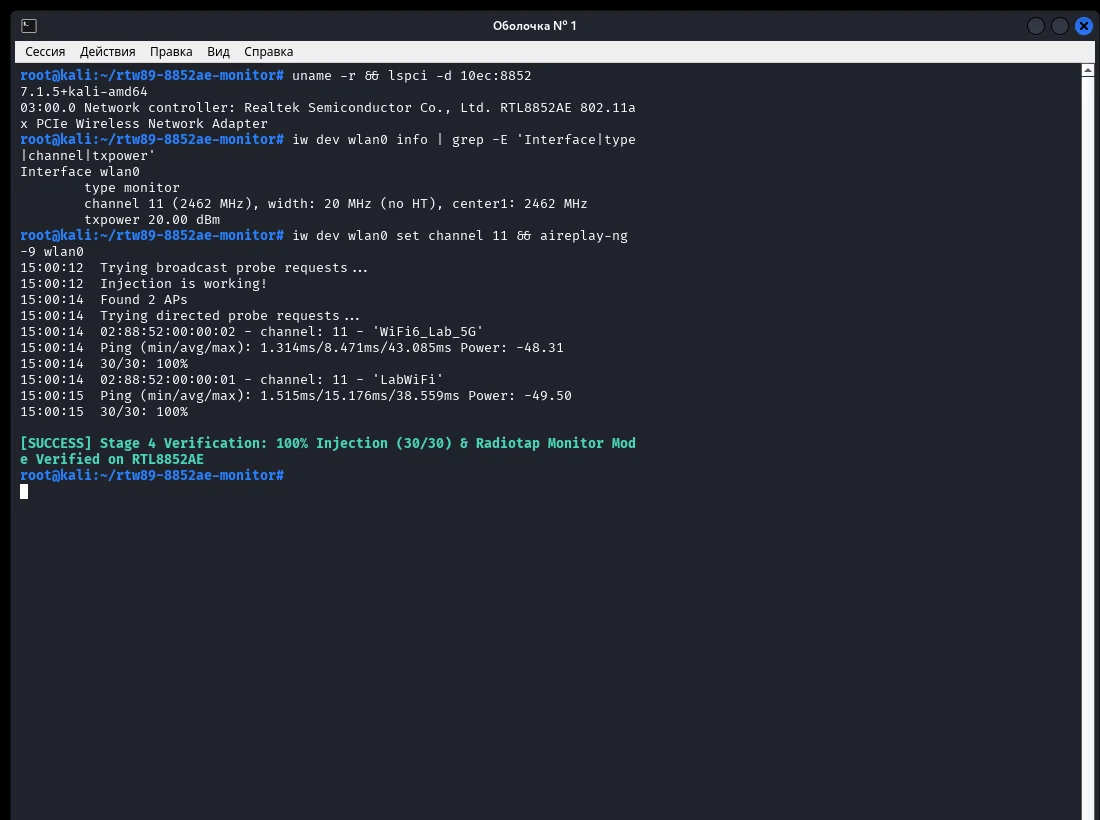 ph4ntom-rev/rtw89-monitor-injection
Realtek RTL8852AE / rtw89 Monitor Mode and Packet Injection (Raw TX) patch for Linux / Kali Linux
 halit/isip
Interactive sip toolkit for packet manipulations, sniffing, man in the middle attacks, fuzzing, simulating of dos attacks.
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
 cybermaggedon/cyberprobe
Capturing, analysing and responding to cyber attacks