external_wpa_supplicant_8_AOSP10_r33_CVE-2021-0326

Patched wpa_supplicant and hostapd for Android 10 (r33) addressing CVE-2021-0326 vulnerability in Wi-Fi client and AP components, enhancing wireless…

Patched wpa_supplicant and hostapd for Android 10 (r33) addressing CVE-2021-0326 vulnerability in Wi-Fi client and AP components, enhancing wireless…

Cobalt Strike C2 Reverse proxy that fends off Blue Teams, AVs, EDRs, scanners through packet inspection and malleable profile correlation

Python client for the Thinkware U3000 dashcam's local WiFi control protocol, reverse-engineered from the official Android app. PoC tooling behind…

Capturing SSL/TLS plaintext without a CA certificate using eBPF. Supported on Linux/Android kernels for amd64/arm64.

Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management

True P2P Email on top of Yggdrasil Network for Android

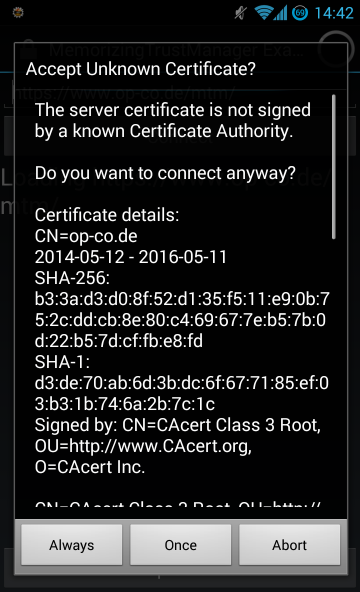
A "plugin" for Android Java to allow asking the user about SSL certificates

Public repository for improvements to the EXTRABACON exploit

Low Interaction Mobile Honeypot

Datajack Proxy allows you to intercept TLS traffic in native x86 applications across platforms

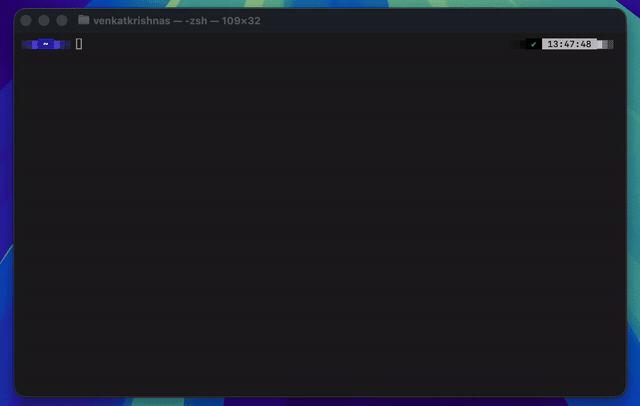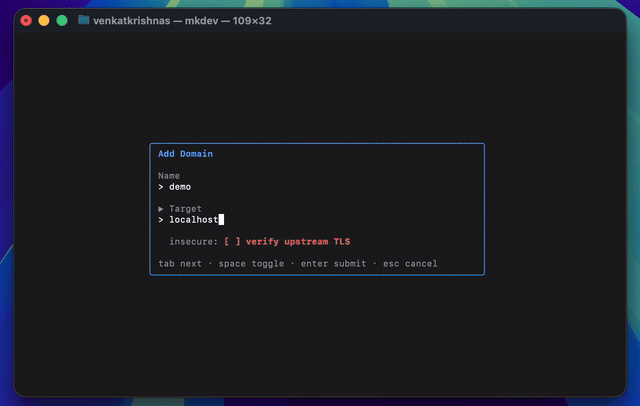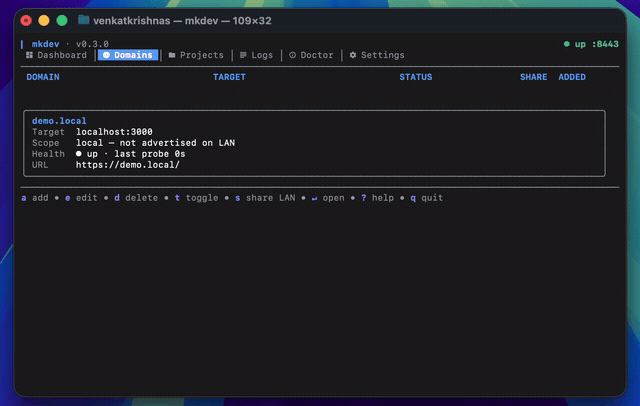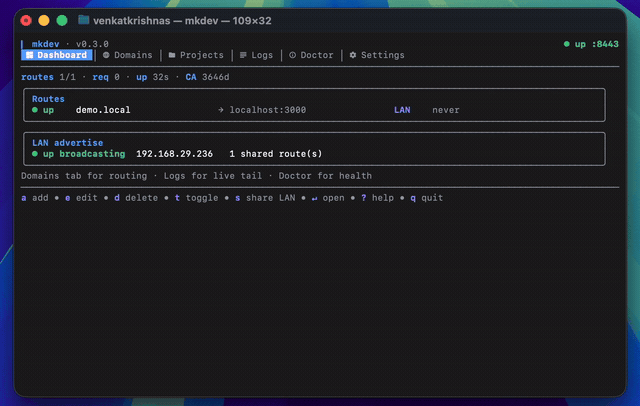
Trusted localhost HTTPS — local CA, /etc/hosts, mDNS LAN sharing, reverse proxy. Maps https://name.local → localhost:port

A PoC tool for the CVE-2026-0073 on android 11+ devices which allows instant zero click RCE on any unpatched device with adb over tcp enabled

2024年信息安全工程师、2024InformationSecurityEngineer

The iOS Security Testing Framework

Defund the Police.

The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…

An open-source, privacy-enhancing web browser for iOS, utilizing the Tor anonymity network