
Pulsar
 jacopodl/pulsar
Data exfiltration and covert communication tool
command-and-controlcryptographydata-exfiltration+2
jacopodl/pulsarData exfiltration and covert communication tool
 arrhenius975/cve-2024-38063-exploit-refactoring
Python-based exploit for CVE-2024-38063 targeting Windows IPv6 vulnerability. Automates network interface detection, packet crafting, and…
 trinadh465/external_curl_aosp10_r33_cve-2021-22924
Command-line tool and library for transferring data using URL syntax, supporting various protocols including HTTP, FTP, and more.

 haruu77g/phantomprint
Passive hybrid fingerprinting engine — identify hosts without sending a single packet
 aniruddh-bhandarkar/cups-script-final-project
Custom script to showcase the novel contribution to CVE-2025-58060
 mysara2022/cve-2025-8671-vulnerability-poc-
CVE-2025-8671 vulnerability POC
 firefart/stunner
Test and exploit STUN/TURN servers for misconfigurations, enabling internal network pivoting via SOCKS proxy, memory leak attacks, and internal port…
 brompwnie/cve-2020-9283
Exploit for CVE-2020-9283 based on Go

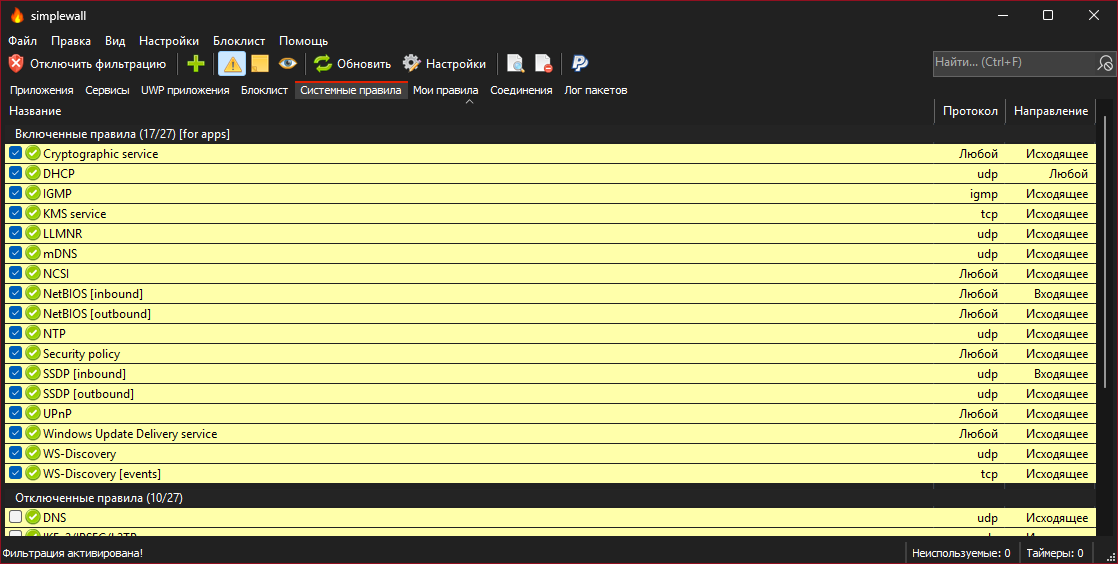 henrypp/simplewall
Simple tool to configure Windows Filtering Platform (WFP) which can configure network activity on your computer.
 elazarl/goproxy
A customizable HTTP/HTTPS proxy library for Go supporting regular forwarding, CONNECT tunneling, MITM TLS interception, and programmatic…
 rathole-org/rathole
A lightweight and high-performance reverse proxy for NAT traversal, written in Rust. An alternative to frp and ngrok.
 mobile-shell/mosh
Remote terminal application supporting intermittent connectivity, IP roaming, and speculative local echo for high-latency links. Uses AES-128…
 haad/proxychains
proxychains - a tool that forces any TCP connection made by any given application to follow through proxy like TOR or any other SOCKS4, SOCKS5 or…
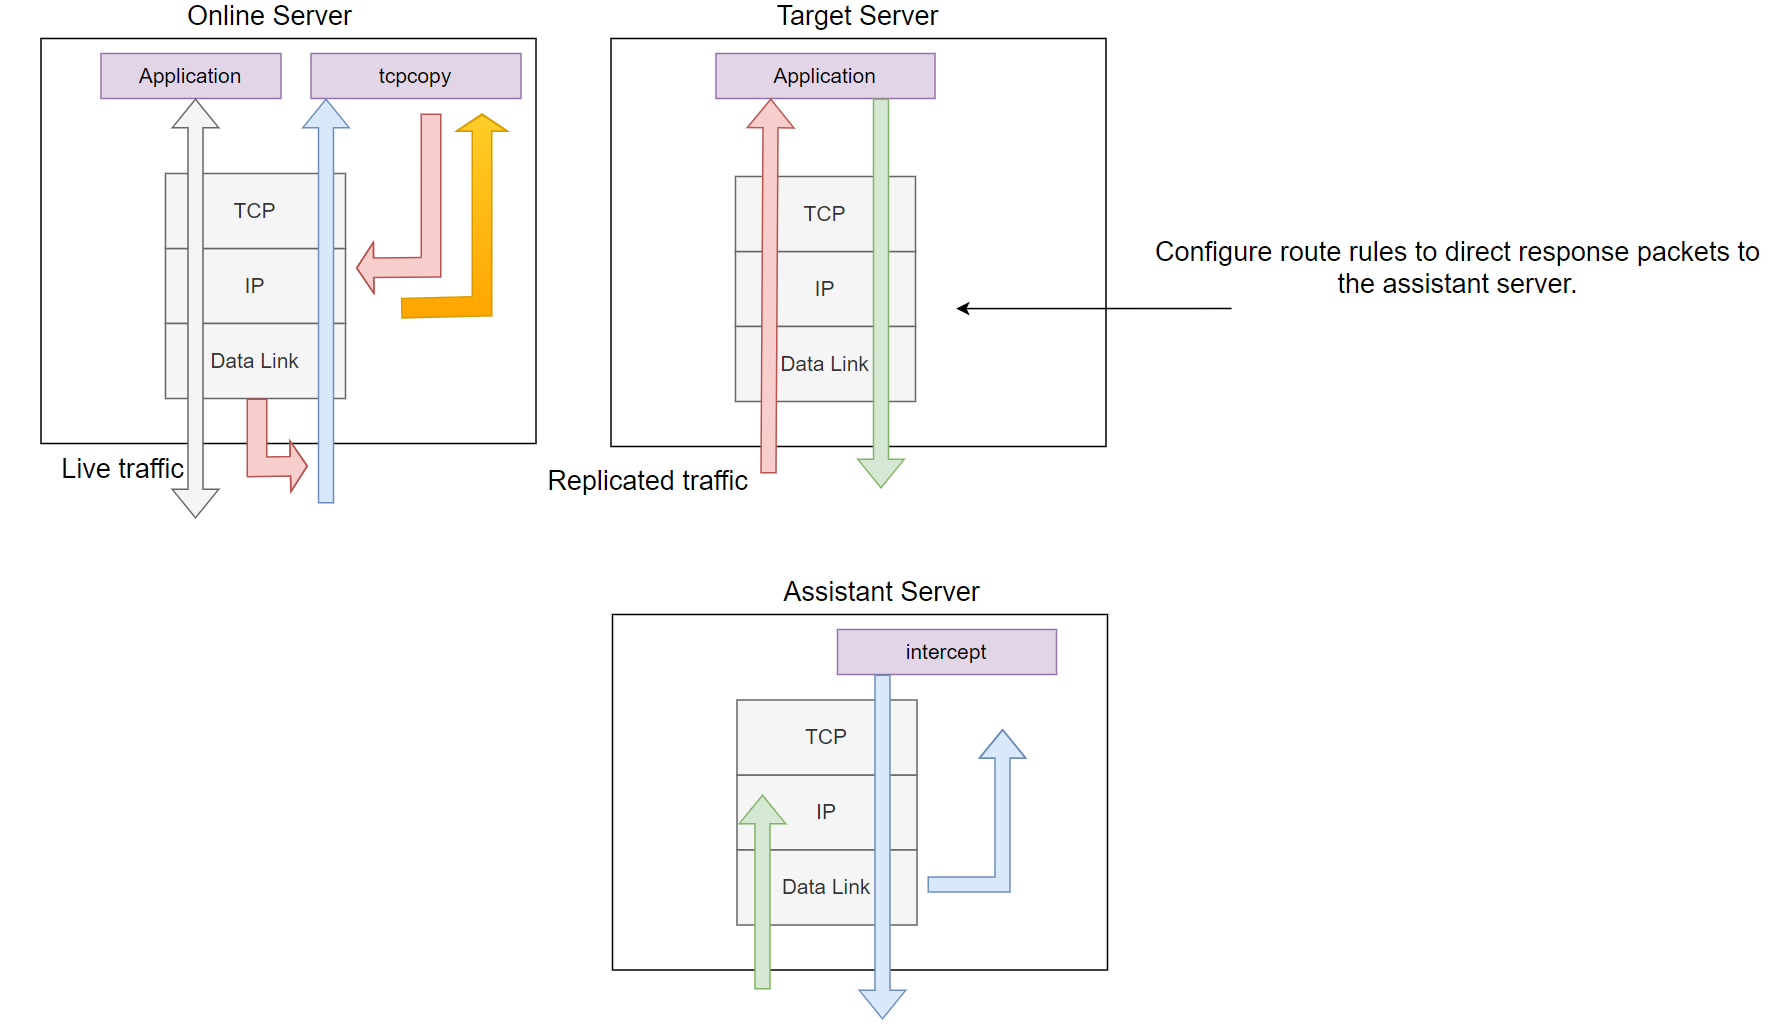 session-replay-tools/tcpcopy
An online request replication and TCP stream replay tool, ideal for real testing, performance testing, stability testing, stress testing, load…