

CVE-2026-19490-check
 bishopfox/cve-2026-19490-check
Safely detect Citrix NetScaler SAML auth bypass CVE-2026-19490
authenticationdefensive-toolsinformation-gathering+6
1
bishopfox/cve-2026-19490-checkSafely detect Citrix NetScaler SAML auth bypass CVE-2026-19490
 keraattin/cve-2026-34197
Detects Apache ActiveMQ Classic RCE (CVE-2026-34197) via Jolokia API with Python and Nmap NSE scripts, checking unauthenticated access and version…
 gh0st0ne/http-vuln-cve2020-3452.nse
CVE-2020-3452 : Cisco ASA and FTD Unauthorized Remote File Reading Nmap NSE Script
 huzaifahussain98/cve-2020-23593
INFORMATION DISCLOSURE :CSRF to enable syslog mode and send to remote syslog server IP and Port.
 spiderlabs/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 google/nogotofail
An on-path blackbox network traffic security testing tool
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 interceptsuite/interceptsuite
MITM proxy for TCP/TLS/DTLS/UDP traffic, with STARTTLS, IoT, Thick Client and more.
 varangamin/cve-2017-6206
The DGS-1510 Websmart switch series firmware has been found to have security vulneratiblies. The vulnerabilities include unauthenticated command…
 cedrico03/cve-2025-45422---bbox
CVE-2025-45422: Proximus b-box UPnP Persistence & Access Control Bypass
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 brainbob/cve-2026-24061
Python-based exploit for CVE-2026-24061, targeting a network service with customizable port and debug mode for security testing.
 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 synacktiv/bbs
bbs is a router for SOCKS and HTTP proxies. It exposes a SOCKS5 (or HTTP CONNECT) service and forwards incoming requests to proxies or chains of…
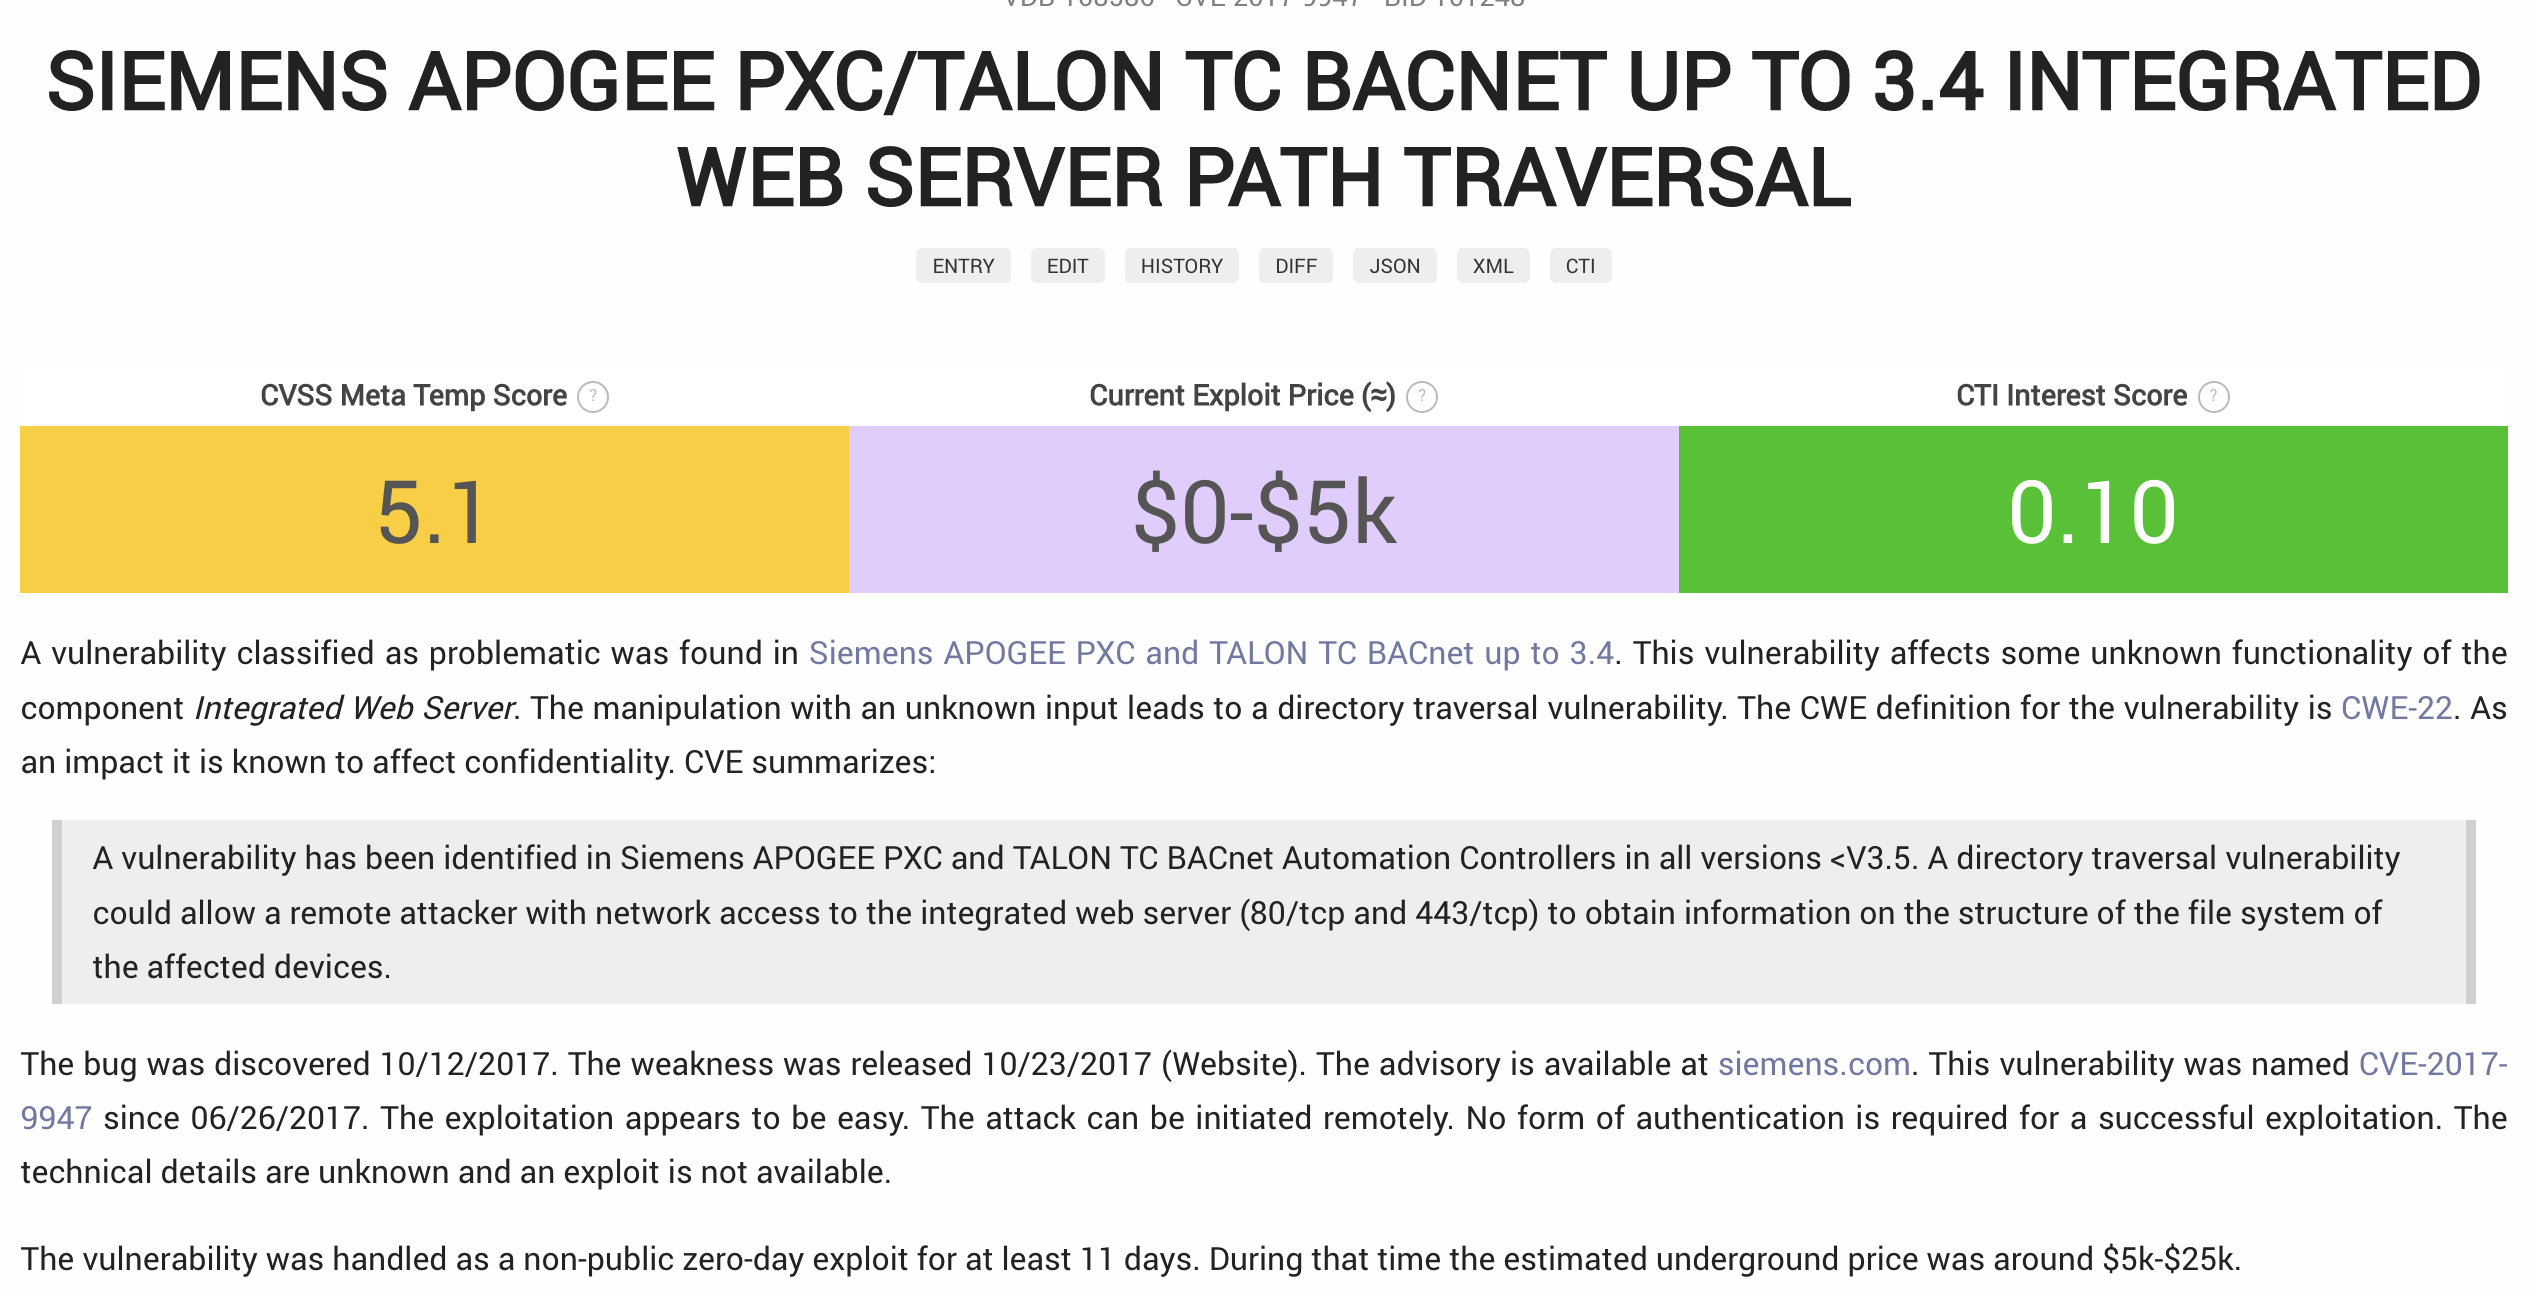 rosesecurity/apologee
APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…
 geniuszly/cve-2020-15916
Proof-of-concept exploit for CVE-2020-15916, enabling unauthorized LAN configuration changes via weak authentication bypass and payload injection.
 jsongmax/fortinet-cve-2022-40684
Go-based exploit tool for CVE-2022-40684 (Fortinet authentication bypass). Automates SSH key injection for authorized penetration testing and…