Bryobio
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
forensicsinformation-gatheringnetwork-forensics+3
emrekybs/bryobioIt was developed to speed up the processes of SOC Analysts during analysis
 karitamw/printnightmare-detection-mitigation-lab
Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.
 ilk-toolkit/ilk-toolkit
A ToolKit that automatically installs & configures all the Tools needed to turn your Daily Driver Linux Distro into a Pentesting Machine
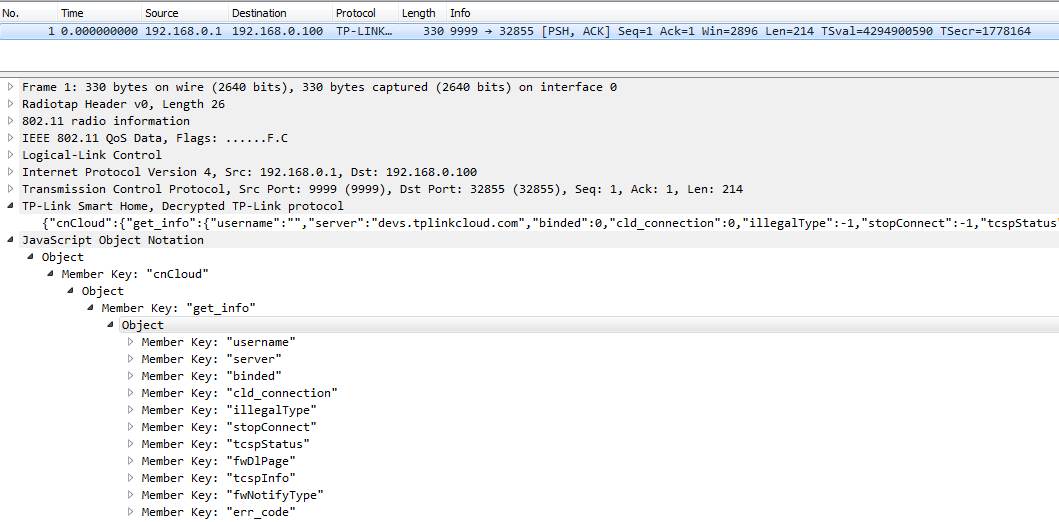 softscheck/tplink-smartplug
TP-Link WiFi SmartPlug Client and Wireshark Dissector
 awakecoding/wireshark-rdp
Wireshark RDP resources
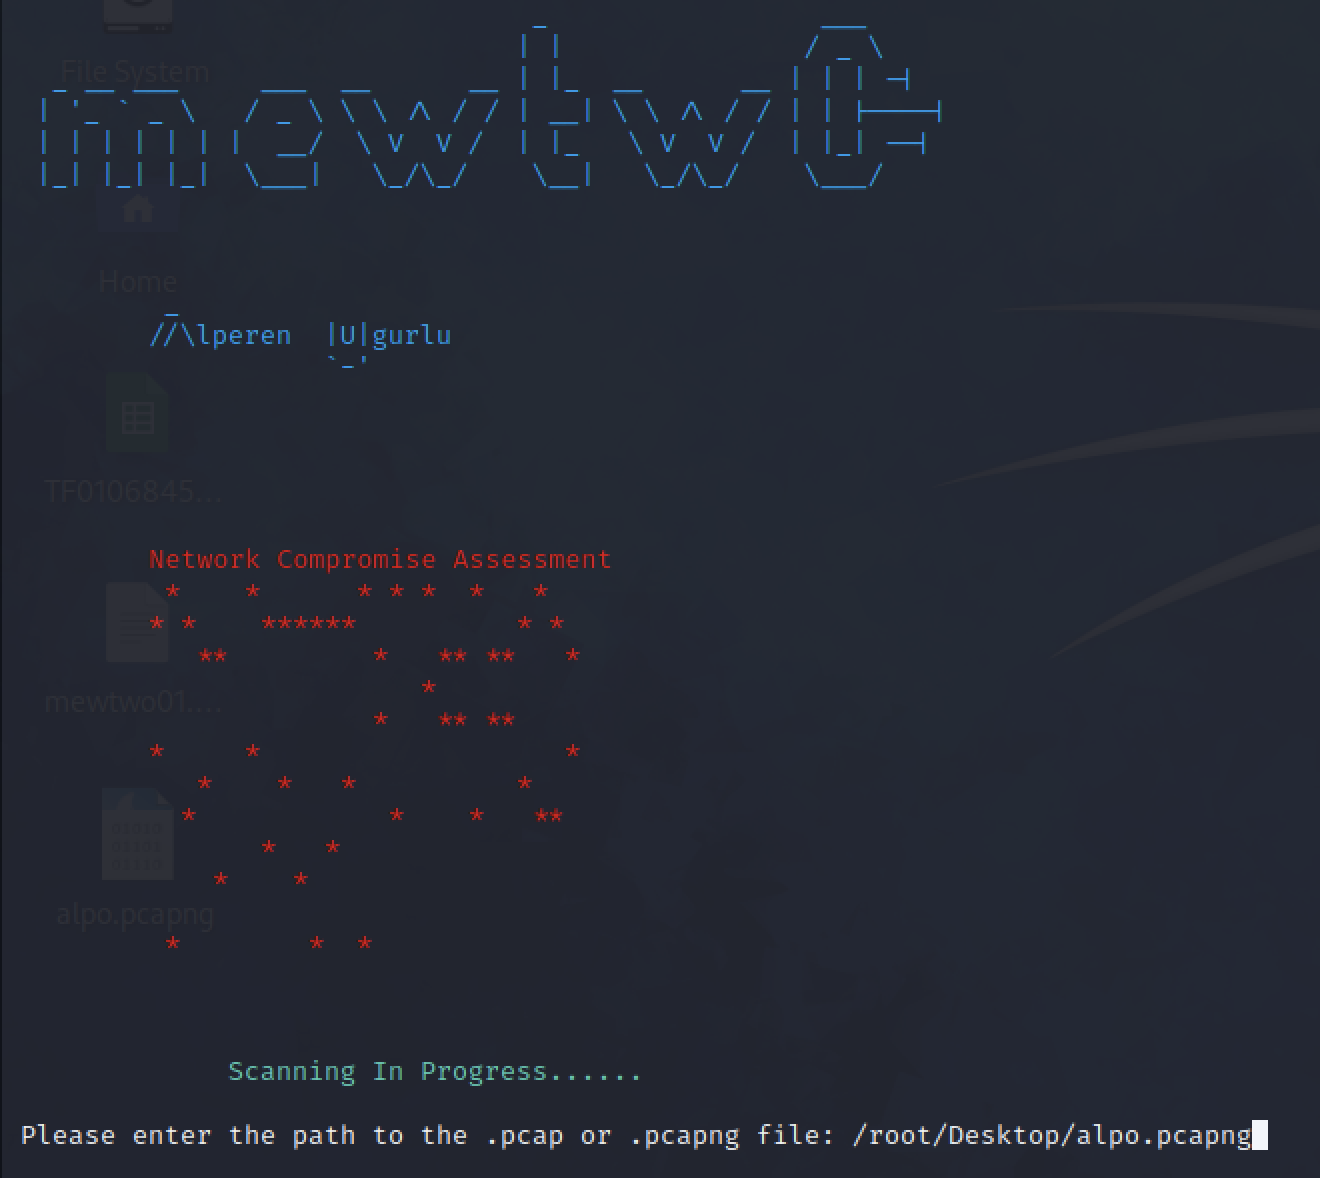 alperenugurlu/network_assessment
With Wireshark or TCPdump, you can determine whether there is harmful activity on your network traffic that you have recorded on the network you…
 infobyte/wiremax
Lua-based Wireshark postdissector that decrypts and parses Ubiquiti AirMAX/RouterBoard 802.11 vendor IEs into filterable fields.
 kiminewt/pyshark-legacy
Python wrapper for tshark, allowing python packet parsing using wireshark dissectors (Python2 legacy version)
 yili-soc/vm-homelab-log4shell-assessment
Full-lifecycle vulnerability management on a live Log4Shell (CVE-2021-44228) target — scan, manual exploitation, network detection, and remediation…
 ivoalbacete/kali-metasploitable
Escaneo de vulnerabilidades, análisis de tráfico con Wireshark y explotación controlada del CVE-2011-2523 (vsftpd 2.3.4) en entorno de red segura.
 b4ntgrim/vuln_remediation_megaquagga
Remediation report for MegaQuagga Publishing validating the mitigation of CVE-2019-9978 through progressive defensive layering. Documents reverse…
 klairmanraj/multi-vlan-enterprise-network-vulnerability-assessment
Multi-VLAN enterprise network vulnerability assessment using Nessus, OWASP ZAP, and Wireshark. Confirms Stored XSS on WebGoat and EternalBlue…
 klairmanraj/multi-vlan-enterprise-network-security-infrastructure
Multi-VM virtual network lab with GRE tunneling, nftables firewall, Active Directory, BIND9 DNS, and Docker services. Includes vulnerability…
 klairmanraj/vulnerability-risk-assessment-tvra-enterprise-network
Qualitative TVRA for multi-VLAN enterprise lab scoring stored XSS and EternalBlue via CVSS v3.0 with ZAP, Nessus, and Wireshark evidence.
 appneta/tcpreplay
Edit and replay captured network traffic at arbitrary speeds — a suite of pcap tools for *NIX and Windows.
 pentesteracademy/patoolkit
PA Toolkit is a collection of traffic analysis plugins focused on security