
CVE-2025-32433-LAB
 damnkrishna/cve-2025-32433-lab
A Flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without…
container-securityeducationexploitation+6
damnkrishna/cve-2025-32433-labA Flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without…
 stealthcopter/deepce
Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
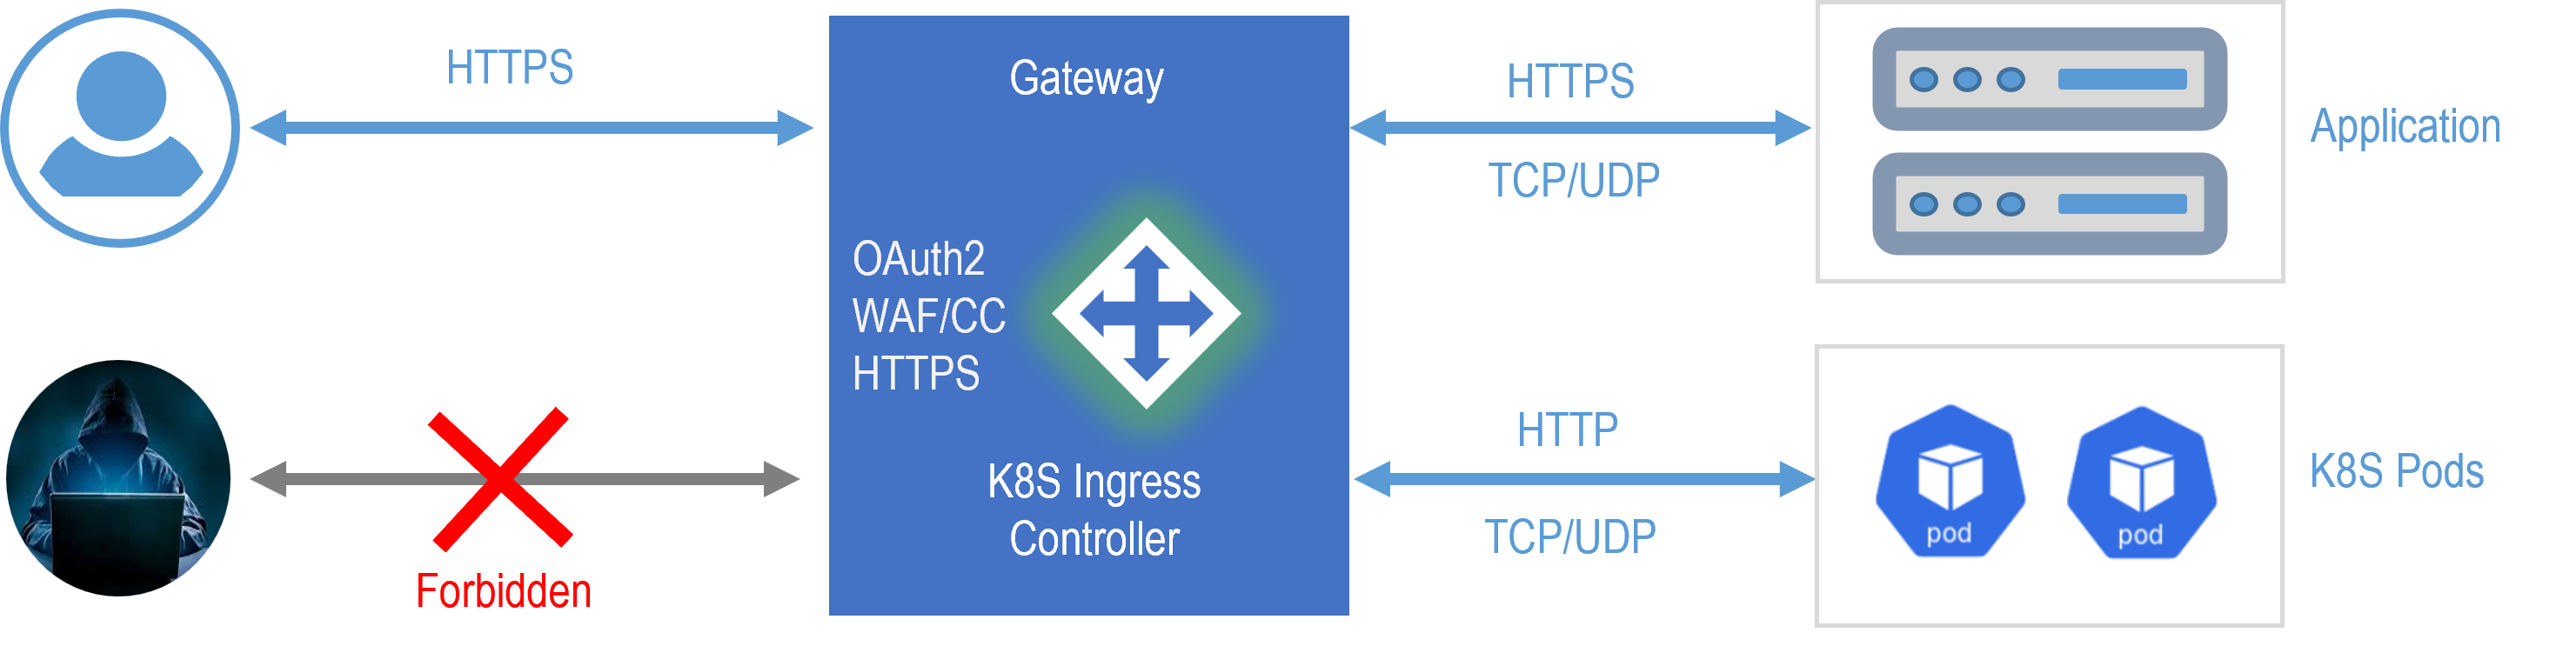 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 milesrichardson/docker-onion-nmap
Scan .onion hidden services with nmap using Tor, proxychains and dnsmasq in a minimal alpine Docker container.
 paradigmxyz/iron-proxy
An egress firewall for untrusted workloads.
 hackerhouse-opensource/cve-2018-10933
Docker-based CVE-2018-10933 libssh authentication bypass exploit with patched client for testing SSH server vulnerabilities and unauthorized access…
 cozystack/copy-fail-blocker
BPF-LSM mitigation for CVE-2026-31431 (Copy Fail) — denies AF_ALG socket creation cluster-wide
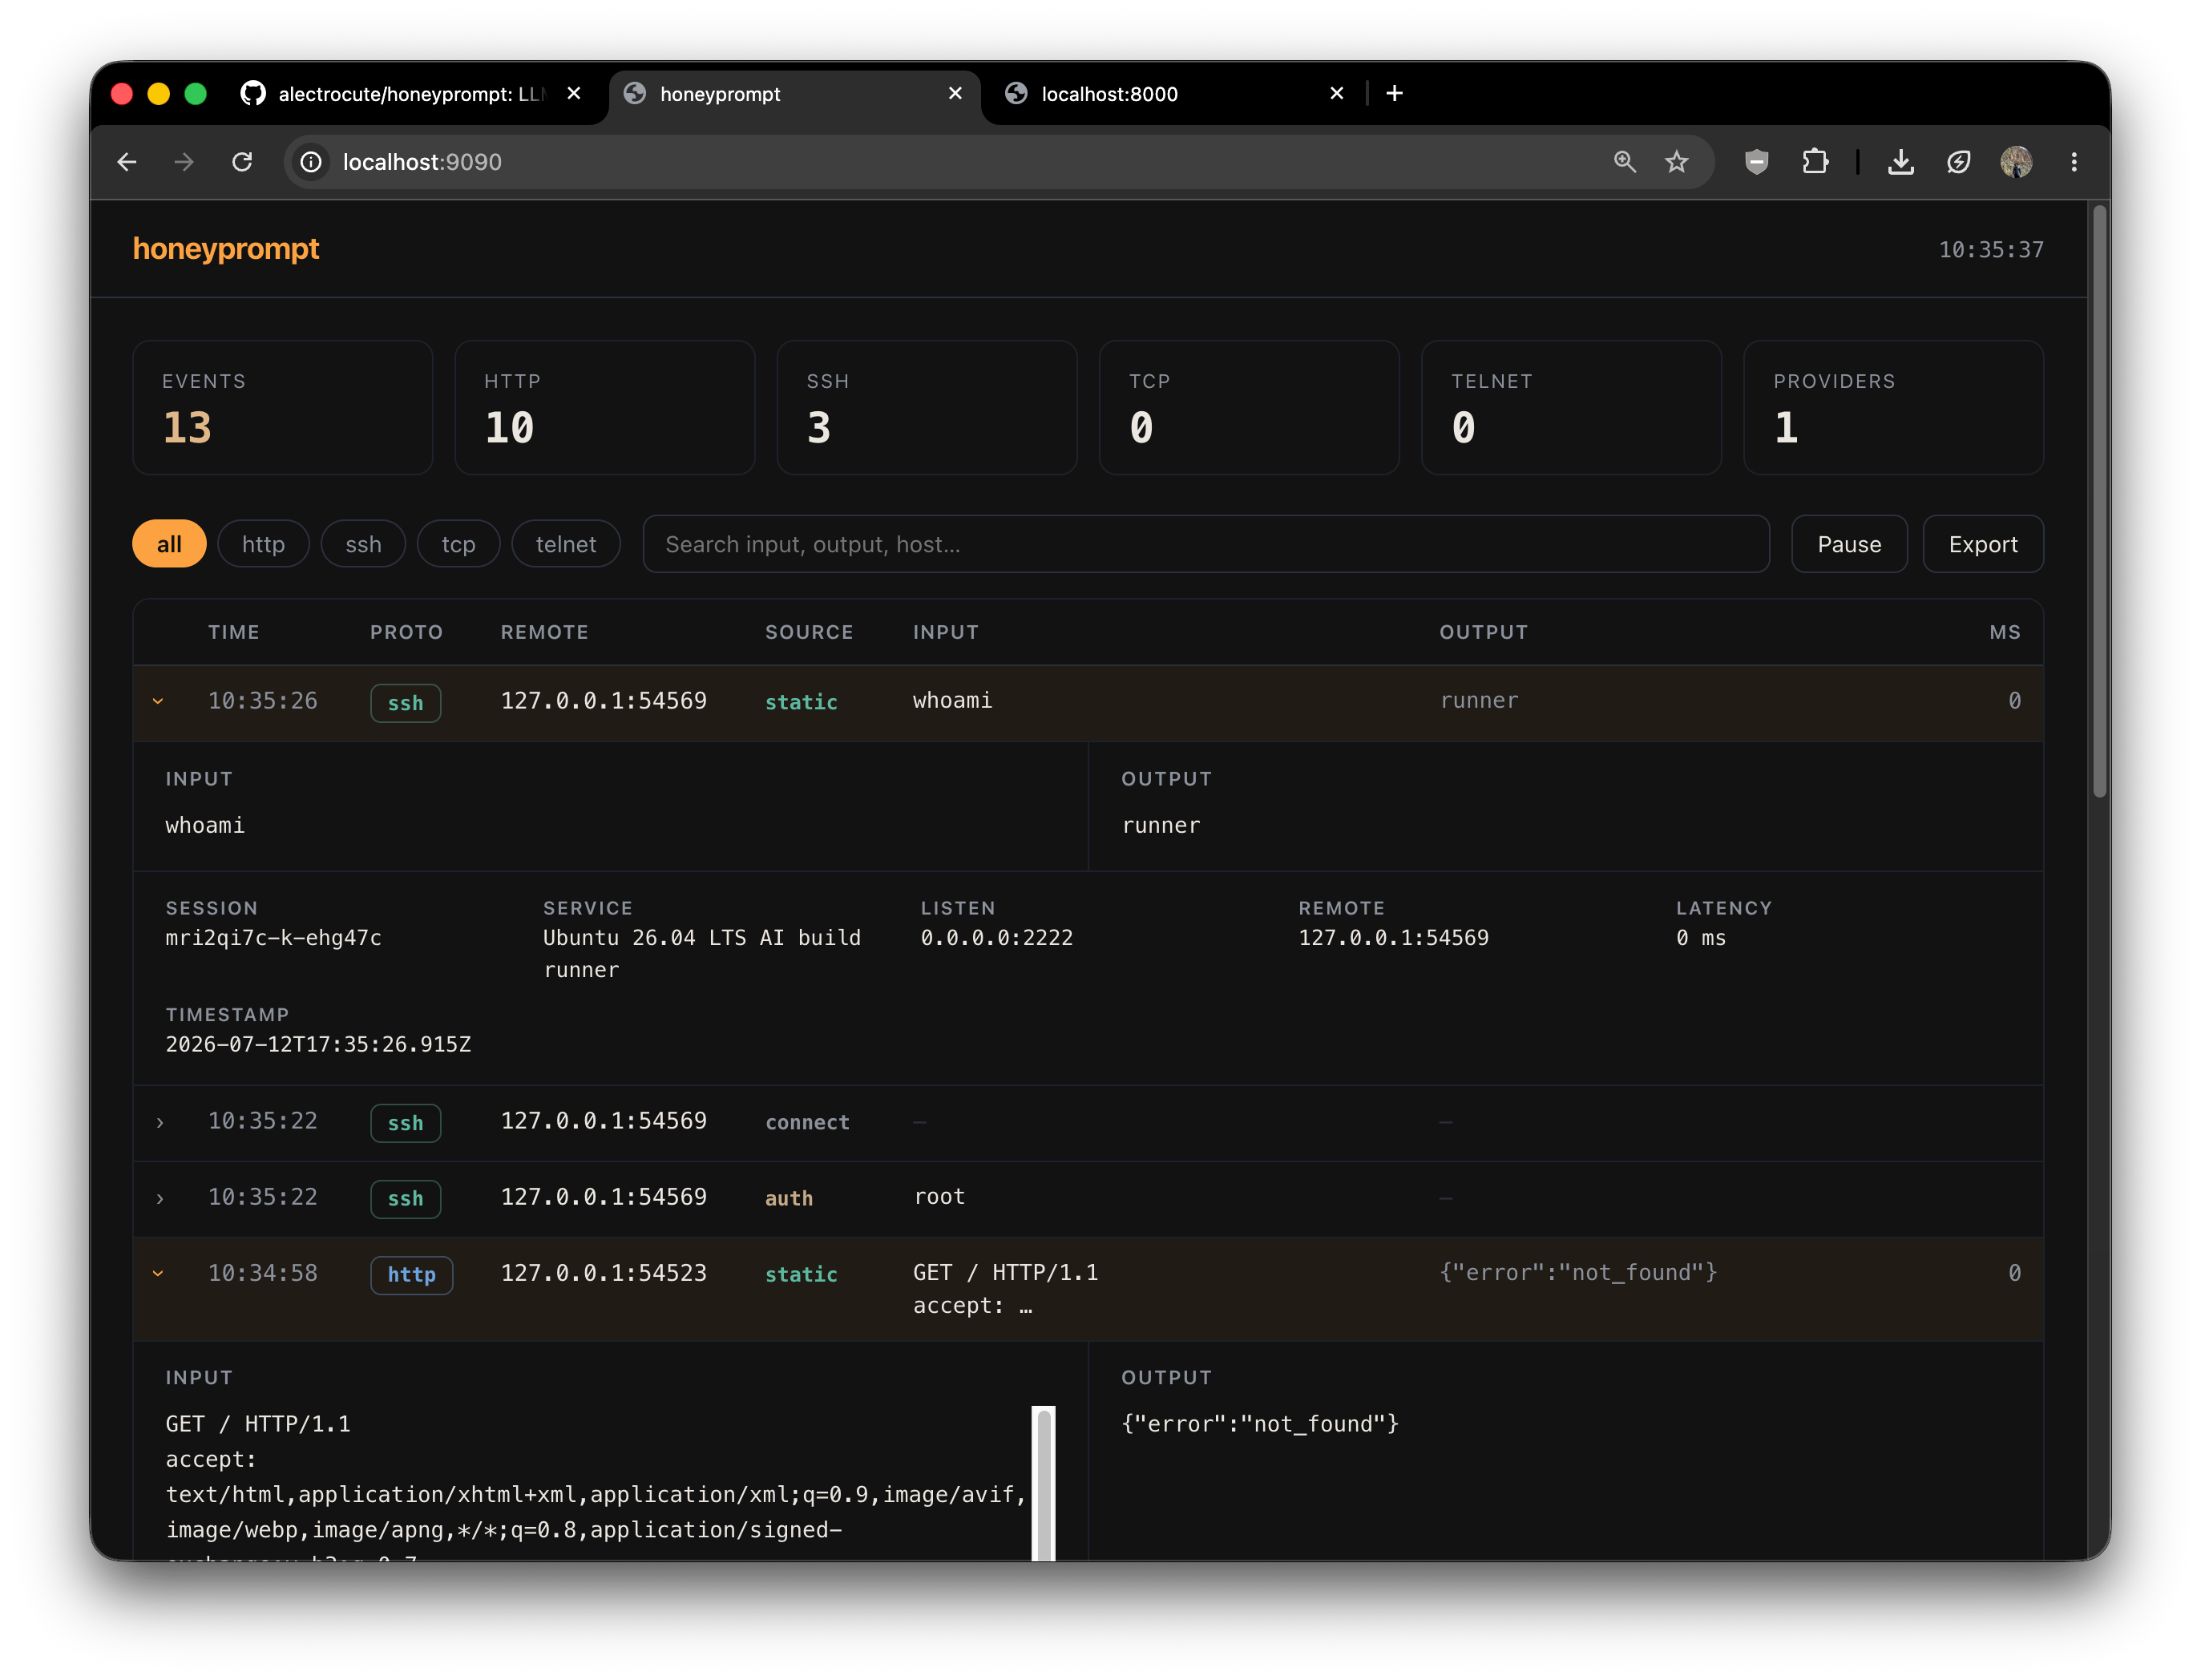 alectrocute/honeyprompt
LLM-first deception framework: "The honeypot that talks back!™"
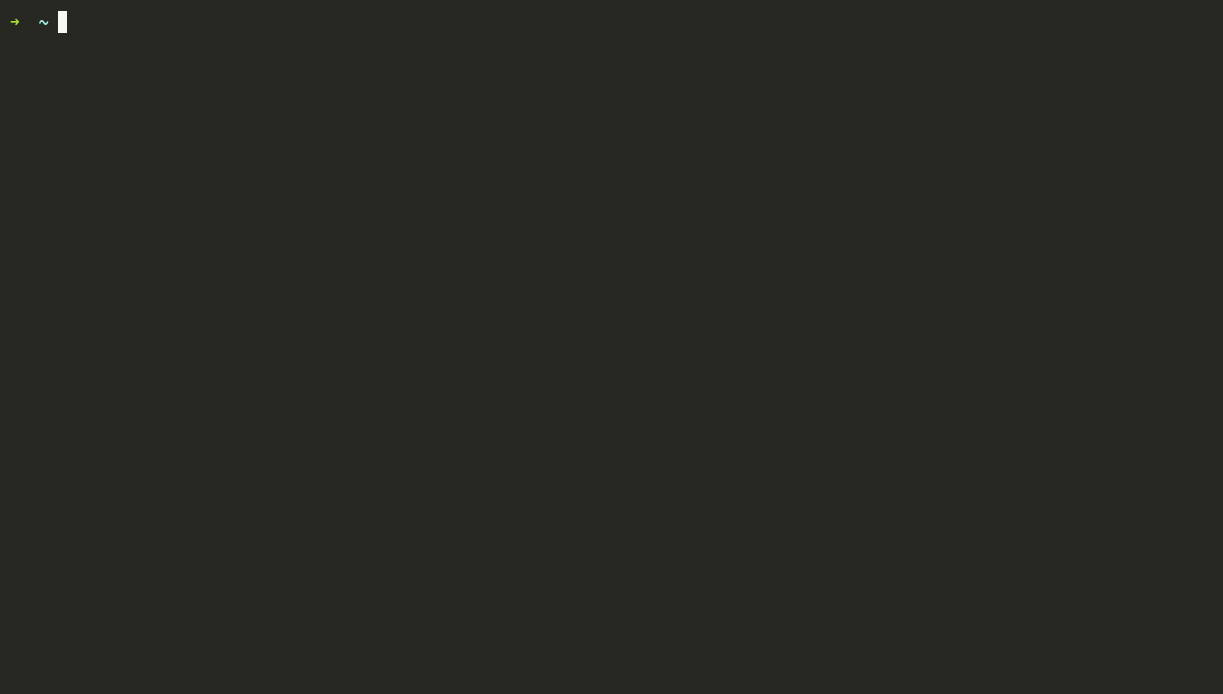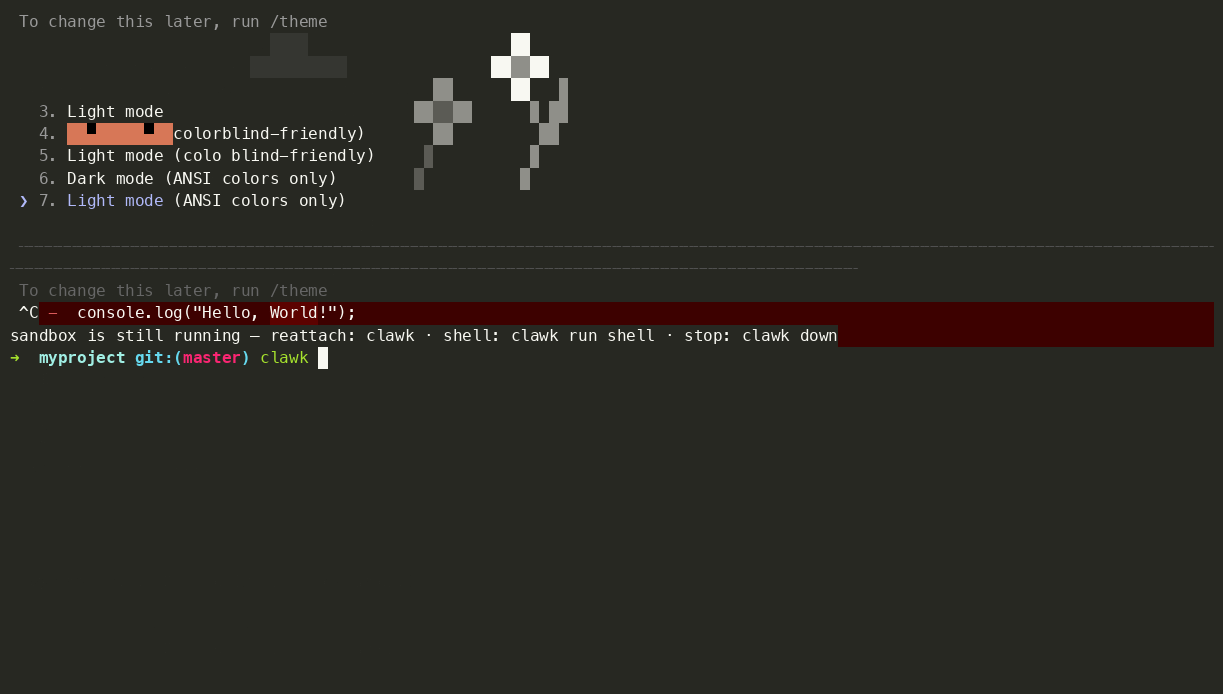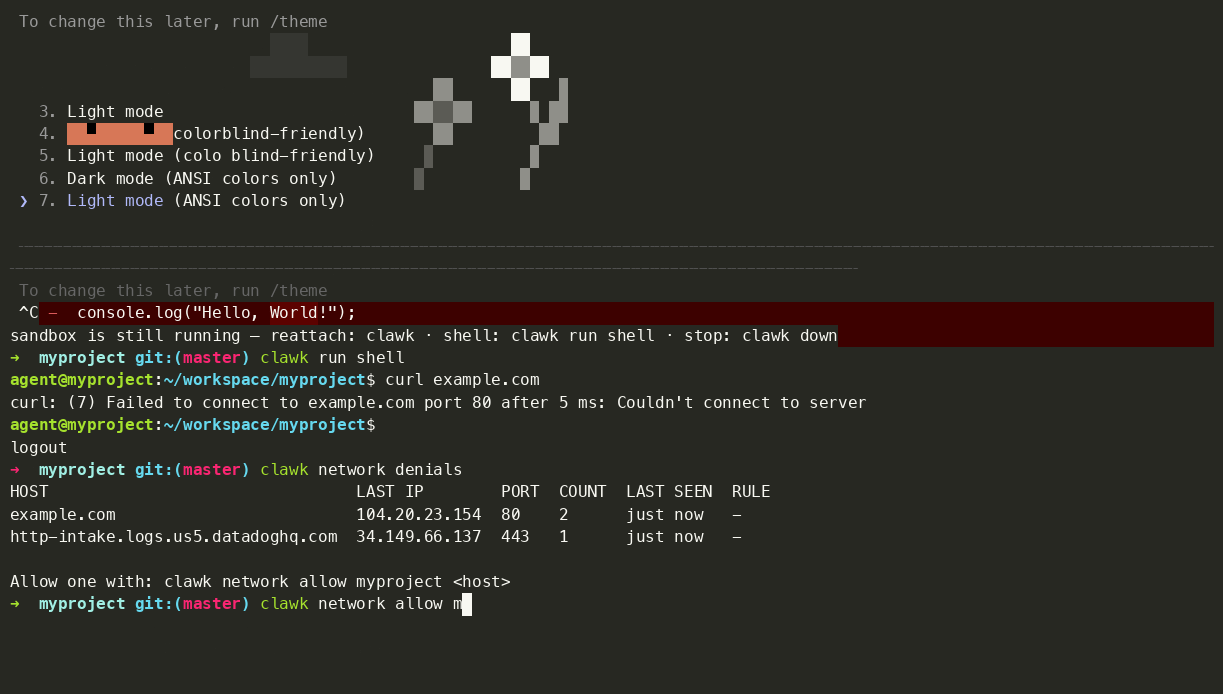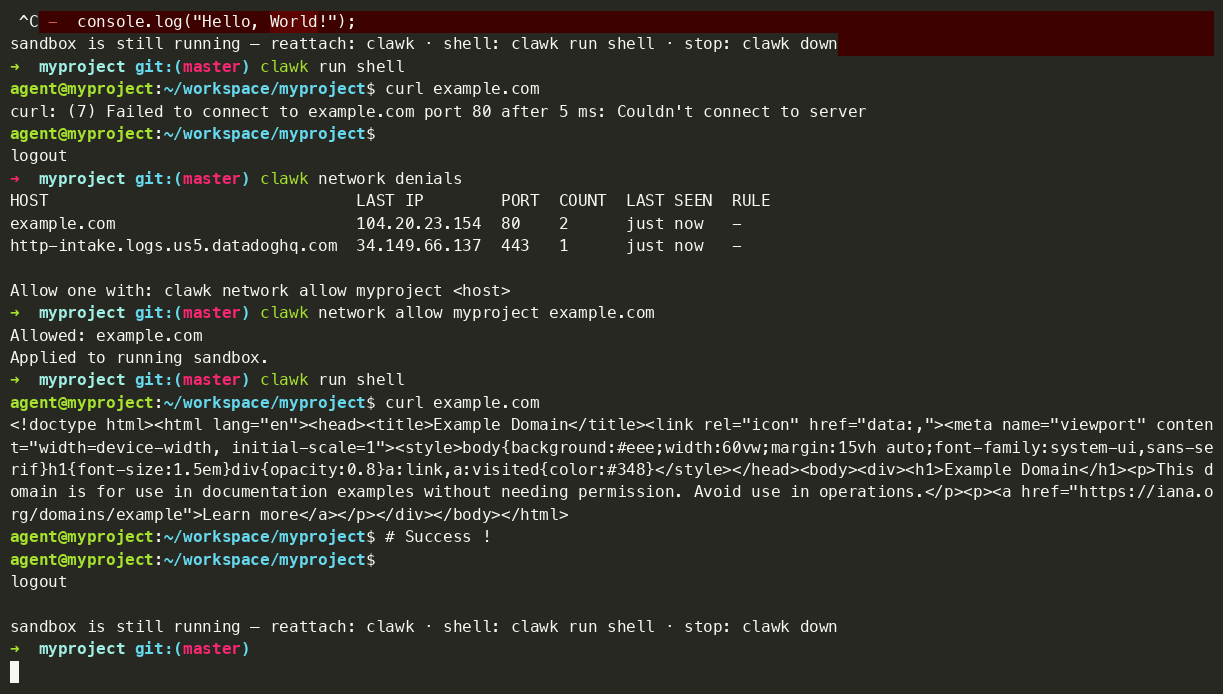 clawkwork/clawk
Give coding agents a disposable Linux VM, not your laptop
 tabbysable/poc-2020-8558
Information about Kubernetes CVE-2020-8558, including proof of concept exploit.
 knqyf263/cve-2023-50387
Educational proof-of-concept for the DNSSEC KeyTrap vulnerability (CVE-2023-50387) with a Docker-based lab environment to demonstrate algorithmic…
 andripwn/cve-2019-0708
Scanner PoC for CVE-2019-0708 RDP RCE vuln
 testssl/testssl.sh
Testing TLS/SSL encryption anywhere on any port
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency.
 greenbone/openvas-scanner
This repository contains the scanner component for Greenbone Community Edition.
 anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.