openssl-ccs-cve-2014-0224

Go-based tool for testing servers against the OpenSSL CCS injection vulnerability (CVE-2014-0224), using a patched TLS library to detect weak…

Go-based tool for testing servers against the OpenSSL CCS injection vulnerability (CVE-2014-0224), using a patched TLS library to detect weak…

Desktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…

Testing tool for the Mikrotrick exploit (CVE-2026-67276)

A comprehensive Python testing tool for CVE-2023-44487, the HTTP/2 Rapid Reset vulnerability. This enhanced version provides granular control over…

Go-based exploit tool for CVE-2022-40684 (Fortinet authentication bypass). Automates SSH key injection for authorized penetration testing and…

Exploit tool for CVE-2018-10933 libSSH authentication bypass, enabling remote shell access without credentials using Python scripts and optional fake…

Concurrent Go-based detection and Python exploitation tool for CVE-2026-41940, enabling rapid vulnerability assessment and targeted exploitation.

Python-based testing tool for CVE-2023-44487 (HTTP/2 Rapid Reset) with multiple attack patterns, granular configuration, and monitoring for…

General-purpose cryptography library and SSL/TLS toolkit implementing ciphers, digests, public key algorithms, X.509 certificates, and a command-line…

Robust open-source toolkit implementing TLS, DTLS, and QUIC protocols with a full-strength cryptographic library, command-line tool for key…

Test tool for CVE-2020-1472

A Multi-vector DoS tool for Cybersecurity Red Teamers' .

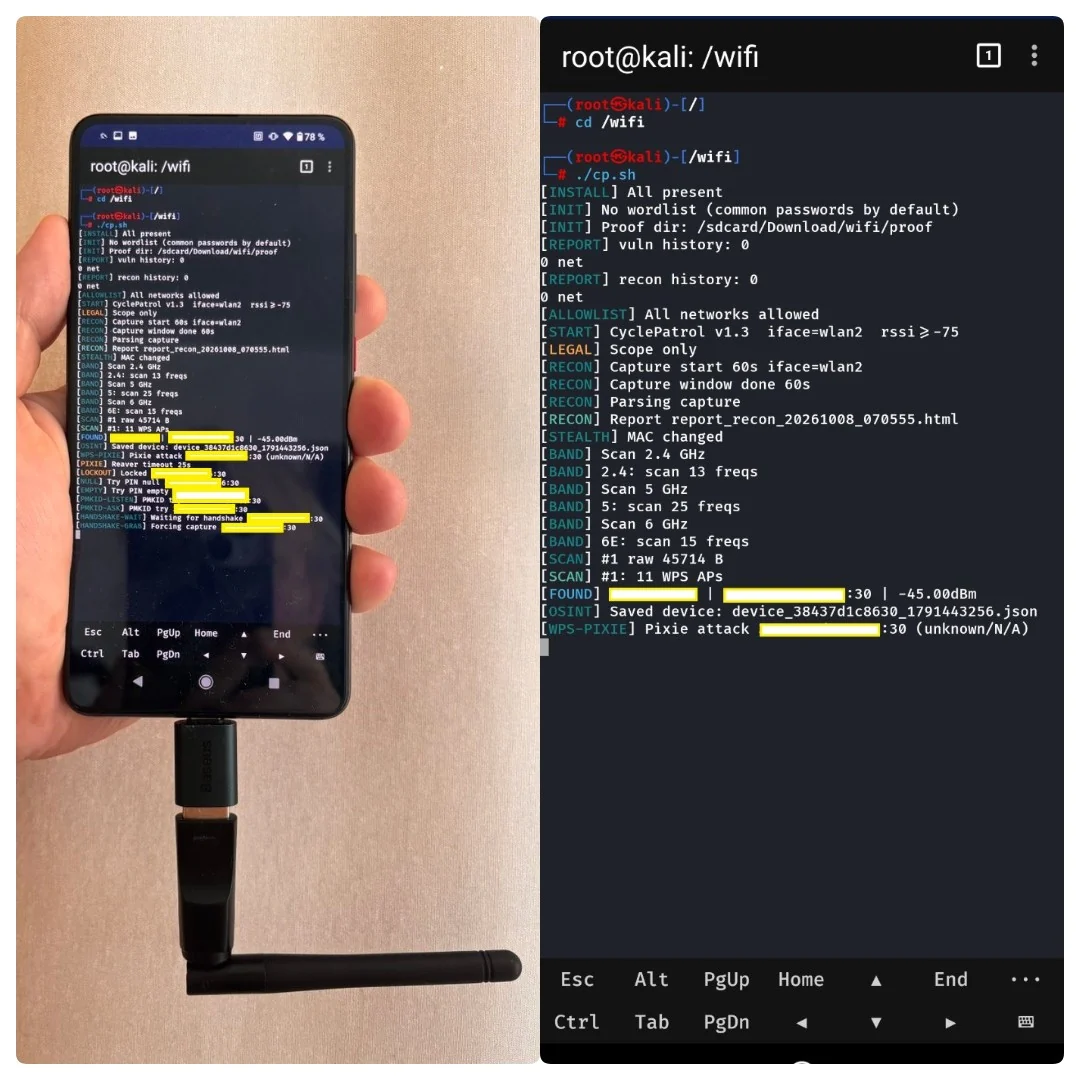
Bash tool for on-foot Wi-Fi security checks in a loop, with evidence reports.

A network stress testing tool for simulating high traffic loads.

Transparent man-in-the-middle proxy that terminates SSL/TLS connections, forges certificates on-the-fly, and logs decrypted traffic for network…

Tool to analyze and test security in IPv4 and IPv6 data networks

Parses and decrypts MS-CHAPv2 handshakes from PPTP VPN and WPA2 Enterprise captures, extracting credentials for offline cracking via CloudCracker.

PolarDNS is a specialized authoritative DNS server suitable for penetration testing and vulnerability research.