
netgear-to-CVE-2022-29383
 cxaqhq/netgear-to-cve-2022-29383
Exploit for CVE-2022-29383 SQL injection in NETGEAR ProSafe SSL VPN (FVS318Gv2/FVS318N) via scgi-bin/platform.cgi.
exploitationnetwork-securitypenetration-testing+2
cxaqhq/netgear-to-cve-2022-29383Exploit for CVE-2022-29383 SQL injection in NETGEAR ProSafe SSL VPN (FVS318Gv2/FVS318N) via scgi-bin/platform.cgi.
 reverseclabs/needle
The iOS Security Testing Framework
 oblique/create_ap
[NOT MAINTAINED] This script creates a NATed or Bridged WiFi Access Point.
 t13nn3s/cve-2020-0796
Powershell SMBv3 Compression checker
 google/tsunami-security-scanner
Tsunami is a general purpose network security scanner with an extensible plugin system for detecting high severity vulnerabilities with high…
 haad/proxychains
proxychains - a tool that forces any TCP connection made by any given application to follow through proxy like TOR or any other SOCKS4, SOCKS5 or…
 samyk/slipstream
NAT Slipstreaming allows an attacker to remotely access any TCP/UDP services bound to a victim machine, bypassing the victim’s NAT/firewall, just by…

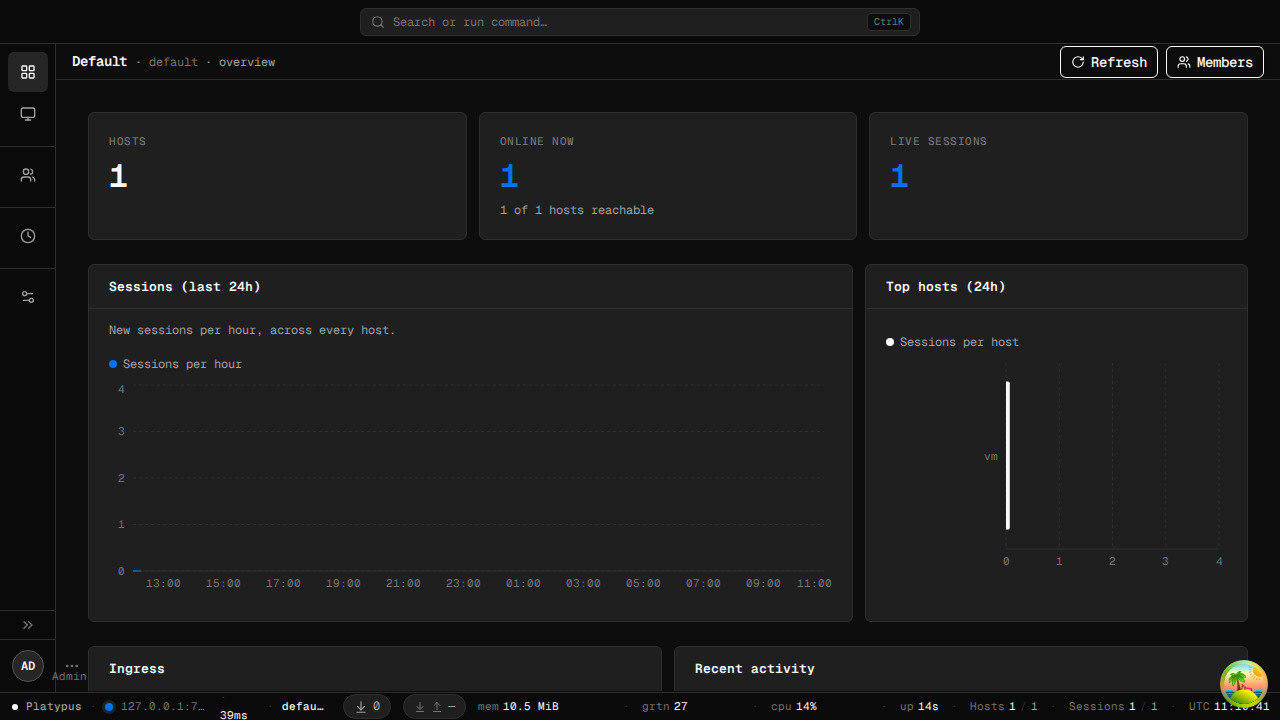 wangyihang/platypus
:hammer: A modern, cross-platform machine manager
 mverschu/cve-2025-33073
PoC Exploit for the NTLM reflection SMB flaw.
 jamesmcm/vopono
Run applications through VPN tunnels with temporary network namespaces
 p0dalirius/coercer
A python script to automatically coerce a Windows server to authenticate on an arbitrary machine through 12 methods.
 ztgrace/changeme
A default credential scanner.
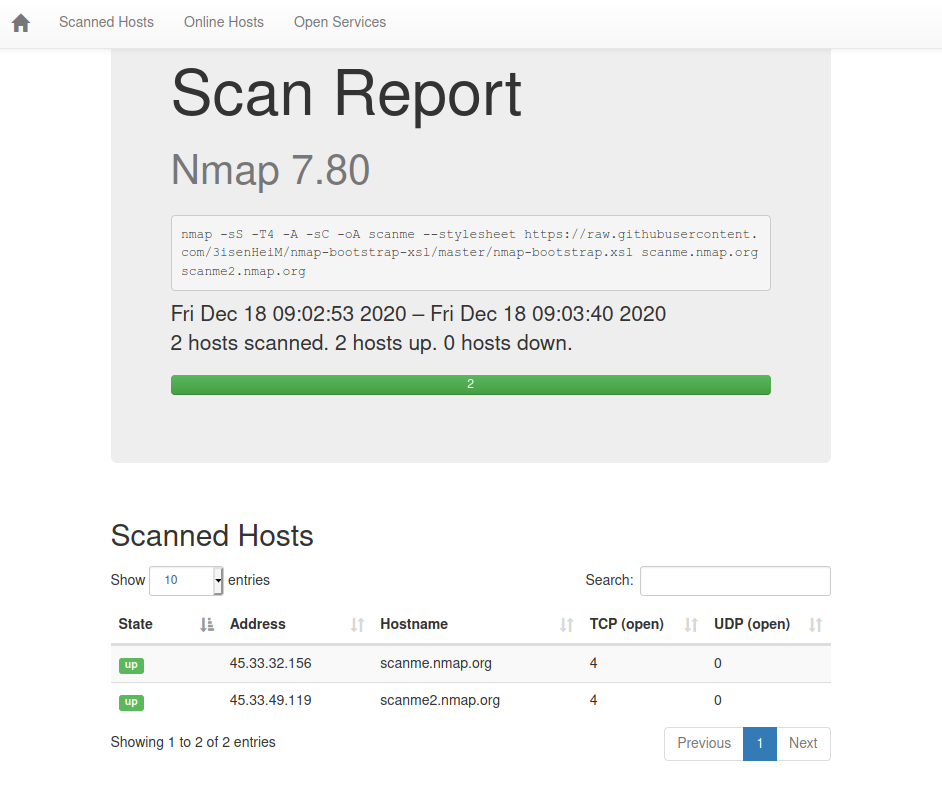 honze-net/nmap-bootstrap-xsl
A Nmap XSL implementation with Bootstrap.
 nccgroup/fuzzowski
the Network Protocol Fuzzer that we will want to use.
 aploium/shootback
a reverse TCP tunnel let you access target behind NAT or firewall
 byt3bl33d3r/itwasalladream
A PrintNightmare (CVE-2021-34527) Python Scanner. Scan entire subnets for hosts vulnerable to the PrintNightmare RCE
 owasp/o-saft
O-Saft - OWASP SSL advanced forensic tool