
zeek-spicy-facefish
 corelight/zeek-spicy-facefish
A Zeek protocol analyzer for the Facefish rootkit, based on Spicy.
command-and-controlintrusion-detectionmalware-analysis+1
1
corelight/zeek-spicy-facefishA Zeek protocol analyzer for the Facefish rootkit, based on Spicy.
 srozb/reditrap
Minimal Redis honeypot detecting RediShell (CVE-2025-49844) exploits.
 bitsalv/toolshell-honeypot
Honeypot for CVE-2025-53770 aka ToolShell
 murrayr0123/cve-2024-3400-compromise-checker
A simple bash script to check for evidence of compromise related to CVE-2024-3400
 abousteif/cve-2021-38647
https://github.com/corelight/CVE-2021-38647 without the bloat
 corelight/cve-2021-38647-noimages
Zeek package detecting CVE-2021-38647 (OMIGOD) exploit attempts by monitoring OMI/WMI traffic for missing Authorization headers and malicious SOAP…
 corelight/petitpotam-notest
Zeek package for detecting PetitPotam NTLM relay attacks via EFS DCERPC over unencrypted SMB, distinguishing successful and unsuccessful exploit…
 corelight/emudhra-weak-keys
A Zeek package that detects when compromised eMudhra intermediate certificates are used in TLS 1.2 and below.
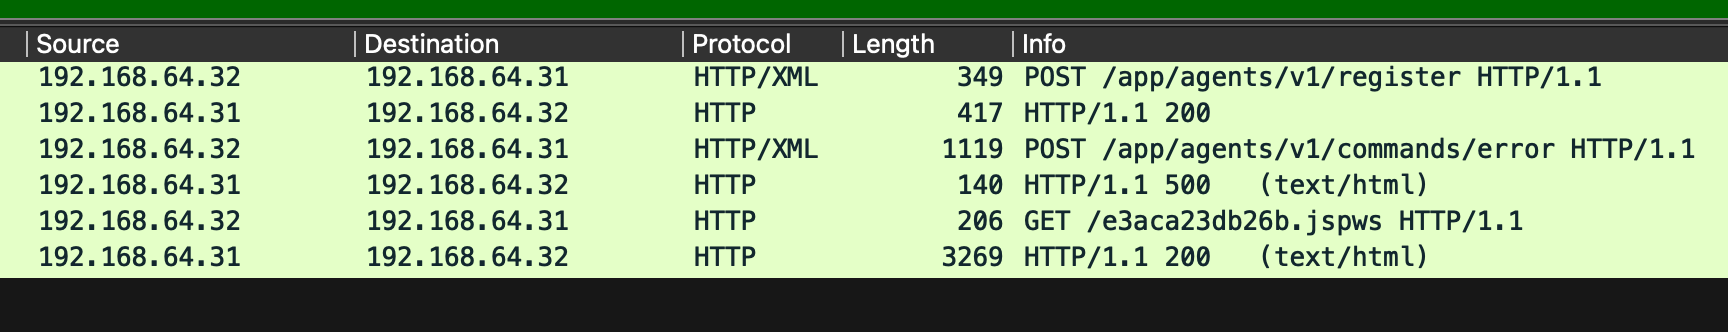 boredhackerblog/teamcity-cve-2026-63077-pcap
teamcity teamcity-CVE-2026-63077 exploitation pcap
 google/stenographer
Stenographer is a packet capture solution which aims to quickly spool all packets to disk, then provide simple, fast access to subsets of those…
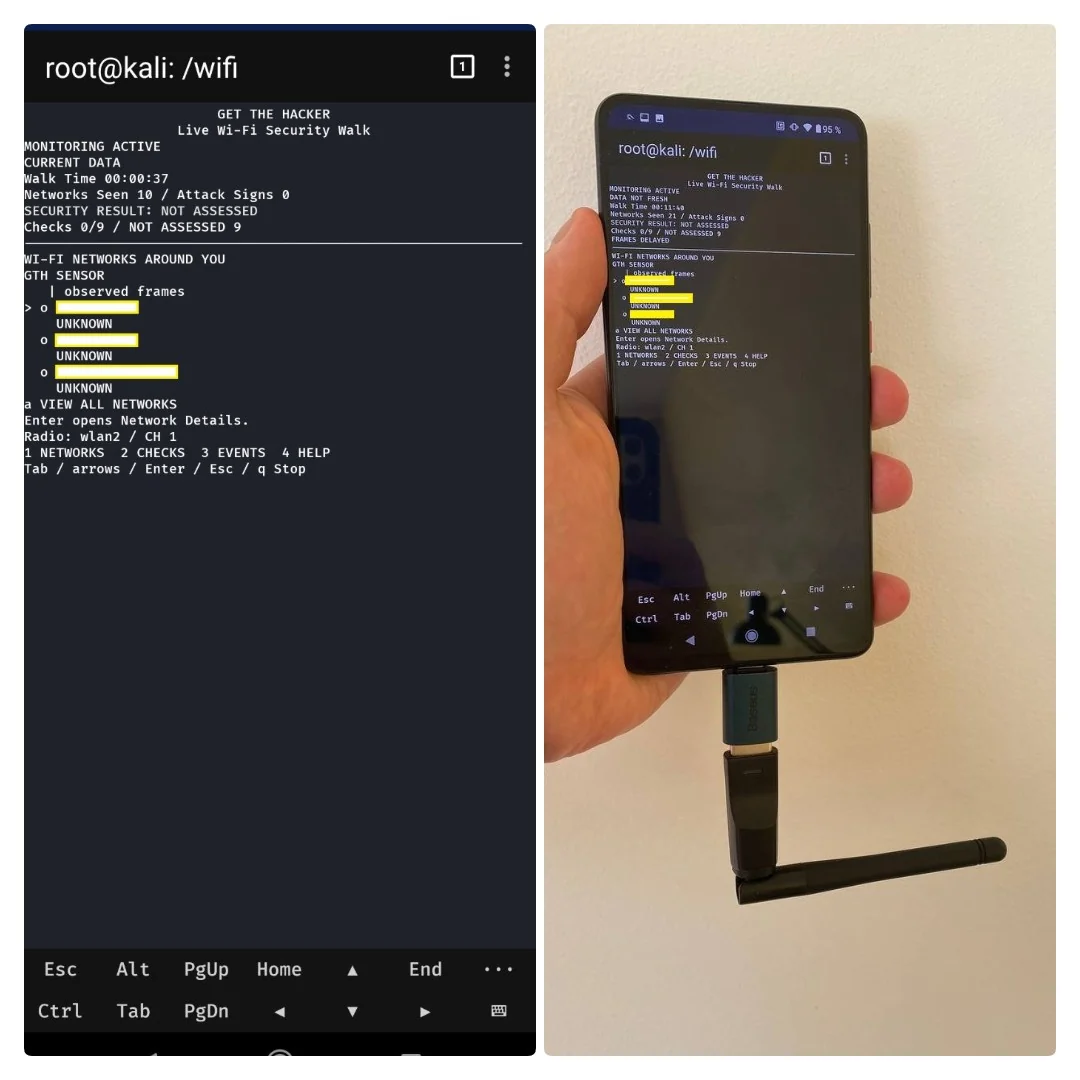 buybitart/get-the-hacker
Hunt WiFi threats silently. Catch the hackers.
 mellow-hype/c2finder
Look for un-sinkholed C&C IPs in your Bro logs (from Bambanek Consulting C&C master list)
 below0day/honeypot-logs-cve-2025-5777
CitrixBleed 2 NetScaler honeypot logs
 corelight/php2shell-detect
Zeek and Suricata Detections for "php2shell" CVE-2026-109618 and CVE-2026-109619
 imthenachoman/how-to-secure-a-linux-server
Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 treussart/probemanager
Centralize Management of Intrusion Detection System like Suricata Bro Ossec ...
 taisa456/network-security-snort
Snort 3 IDS → IPS lab on Kali. Custom detection rules + iptables enforcement against ICMP recon, Nmap SYN scans, Hydra FTP brute force, and vsftpd…