

OpenShell
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
ai-securityauthentication-authorizationcloud-security+7
20.4k
nvidia/openshellSandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 t0xodile-swig/http3-adapter
Burp Suite extension that intercepts requests and sends them over HTTP/3, converting responses back for Burp, with support for kettled requests and…
 anuththara2007-w/cve-2026-20127-exploit-extension
Offline browser extension providing defensive analysis and detection guidance for CVE-2026-20127, with packet visualization, IOC extraction, and…
 thuname/ted
Research artifact from USENIX Security 2026 demonstrating DDoS attacks by abusing tunnel nodes and IPv6 extension headers, with accompanying analysis…
 indrajeetmp11/heartbleed-poc-exploit-script
This Python PoC script detects the Heartbleed vulnerability (CVE-2014-0160) by performing a TLS handshake with heartbeat extension and sending a…
 ctabango/cve-2025-24071_pocextra
Proof-of-concept exploit for CVE-2025-24071 that creates a .searchconnector-ms file to trigger SMB authentication when copied, enabling credential…
 furkankayapinar/ecs_checker
EDNS Client Subnet (ECS) Remote Detection Tool - CVE-2025-40766
 chaostoolkit/chaostoolkit-kubernetes
Kubernetes driver extension of the Chaos Toolkit probes and actions API
 nomis/eero-zero-length-ipv6-options-header-dos
eeroOS Ethernet Interface Denial of Service Vulnerability (CVE-2023-5324)
 zu1k/good-mitm
Rule-based MITM engine. Rewriting, redirecting and rejecting on HTTP(S) requests and responses, supports JavaScript rule.
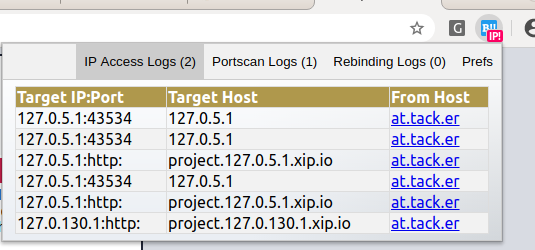 mindedsecurity/behave
Behave! A monitoring browser extension for pages acting as "bad boi"