
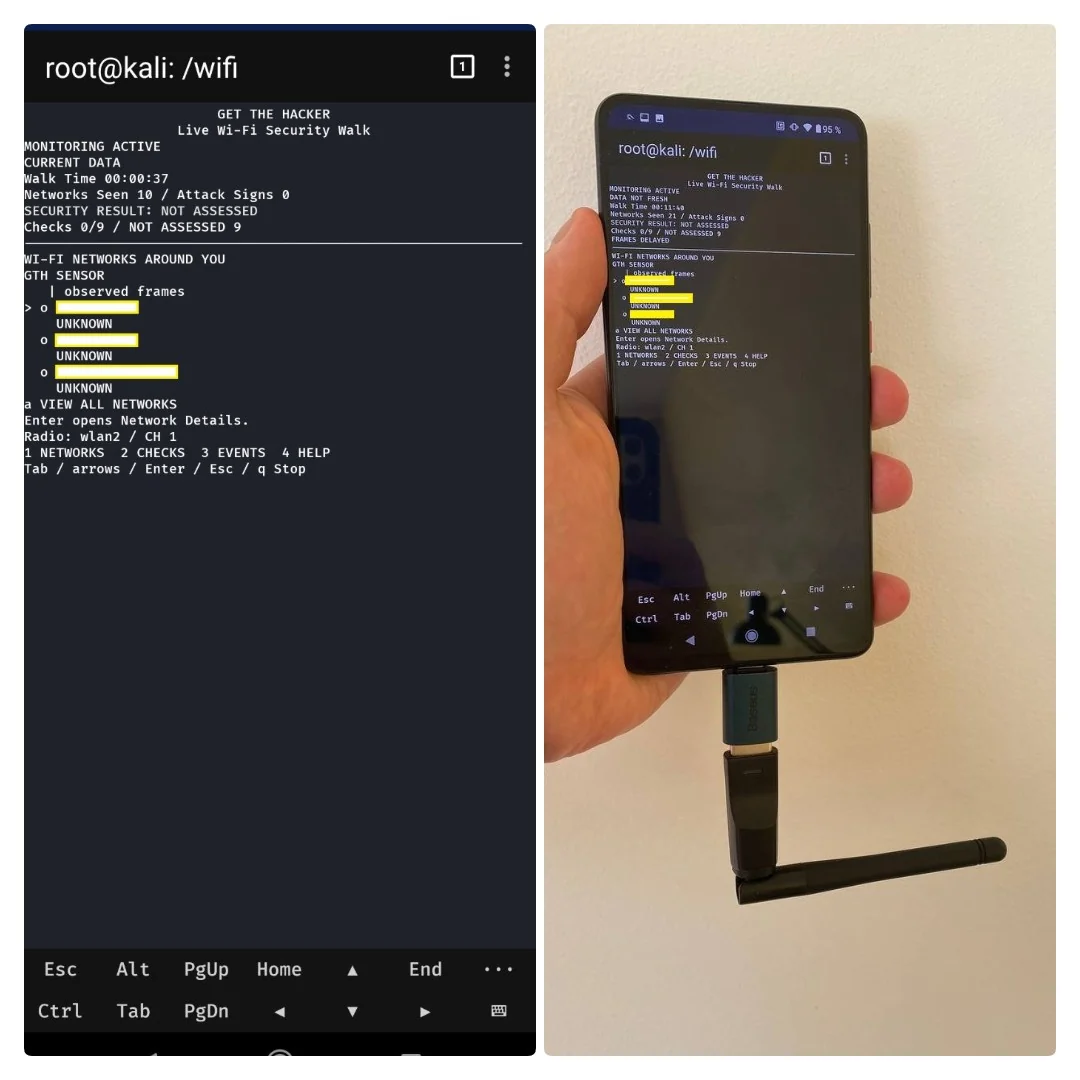
get-the-hacker
 buybitart/get-the-hacker
Hunt WiFi threats silently. Catch the hackers.
defensive-toolsincident-responseintrusion-detection+5
buybitart/get-the-hackerHunt WiFi threats silently. Catch the hackers.
 amibhai/spoofed
A professional-grade, fully async Python network spoofing suite for authorized security auditing. Features full IPv4/IPv6 interception, 802.11…

 yashubitra/mobile-intrusion-detection-system
Unsupervised deep autoencoder that flags anomalous mobile traffic: 25,000+ HTTP/HTTPS flows intercepted from a live iOS device with mitmproxy,…
 corelight/emudhra-weak-keys
A Zeek package that detects when compromised eMudhra intermediate certificates are used in TLS 1.2 and below.
 corelight/php2shell-detect
Zeek and Suricata Detections for "php2shell" CVE-2026-109618 and CVE-2026-109619
 nawaralseelawi/pvbrf-id
Simulation code and results for a private, verifiable, Byzantine-robust federated intrusion detection protocol using secret sharing, Merkle audits…
 jev-sec/jev-ids
Blazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.
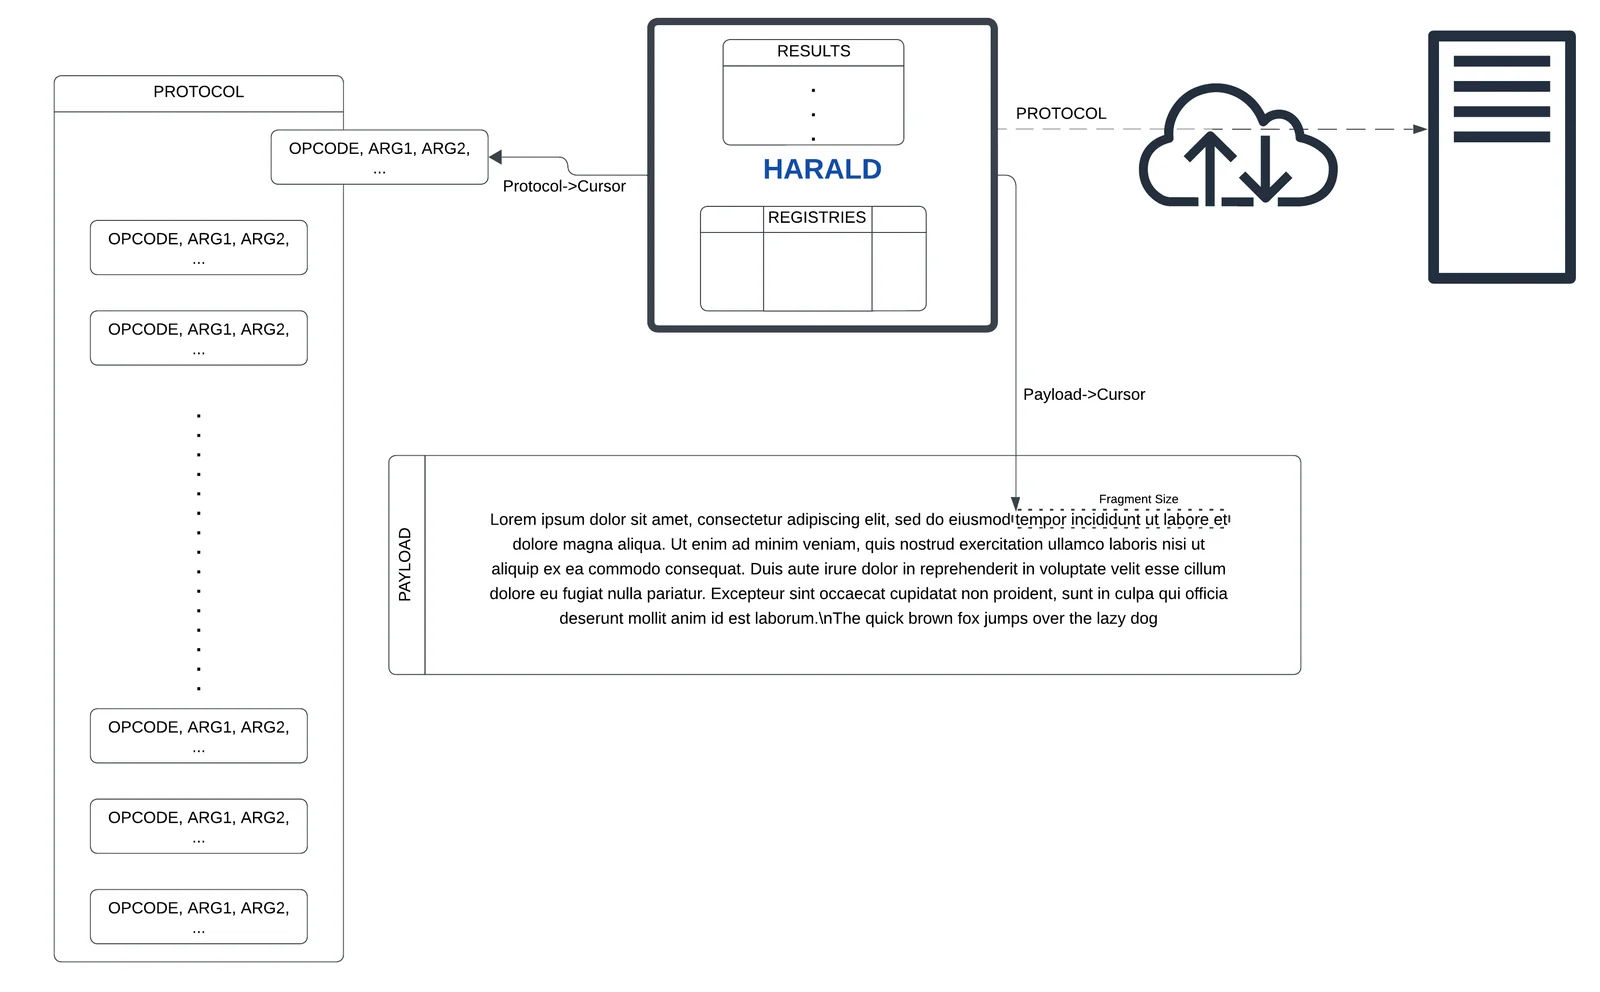 gmh5225/harald
An in-memory minimal CPU for agnostic on-the-fly protocols creation
 gmh5225/f31
Tool for hiding Kali Linux on the network
 devinblack001/ddos-reduction-system
Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
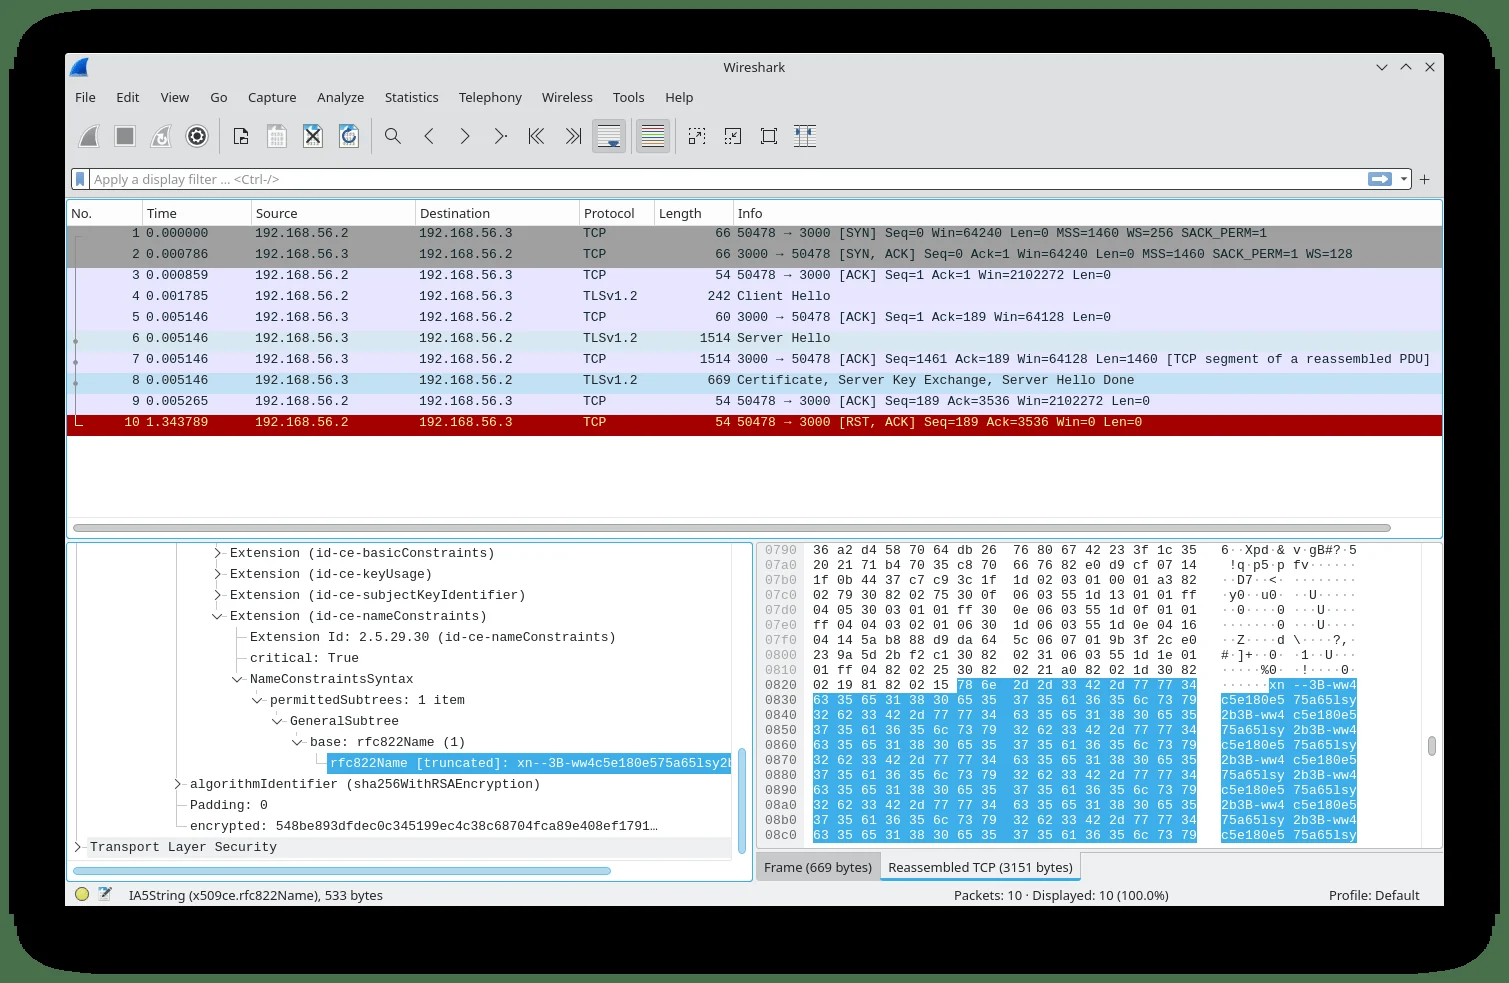 fox-it/spookyssl-pcaps
PCAPs and Suricata signatures for detecting OpenSSL CVE-2022-3602 exploitation attempts, including malicious client/server traffic and legitimate…
 davidsonrafaelk/evillimiter
Tool that monitors, analyzes and limits the bandwidth of devices on the local network without administrative access
 kismetwireless/kismet-docs
Documentation repository for Kismet, a wireless network detector, sniffer, and intrusion detection system. Includes guides, configuration references,…
 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
 4n4s4zi/tfo-connect-bypass
Using TCP Fast Open to bypass syscall-based networking rules (CVE-2026-63828/CVE-2026-72243 PoC)
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
 rohithronanki/cve-2026-34159-vulnerability-research-analysis-detection
Critical buffer validation bypass in deserialize_tensor() (llama.cpp < b8492). Null tensor buffer skips bounds check, enabling unauthenticated…