

sshesame
 jaksi/sshesame
An easy to set up and use SSH honeypot, a fake SSH server that lets anyone in and logs their activity
defensive-toolsincident-responseinformation-gathering+4
1.8k
jaksi/sshesameAn easy to set up and use SSH honeypot, a fake SSH server that lets anyone in and logs their activity
 wolfssl/wolfssh
Small, portable embeddable SSHv2 client and server library in C with SCP, SFTP, port forwarding, and post-quantum key exchange for embedded and IoT…
 haidang-infosec/phantom-grid
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…
 damnkrishna/cve-2025-32433-lab
A Flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without…
 dev-sec/chef-ssh-hardening
This chef cookbook provides secure ssh-client and ssh-server configurations.
 dev-sec/puppet-ssh-hardening
This puppet module provides secure ssh-client and ssh-server configurations.
 gagaltotal/cve-2026-31431-copy-fail
Automated scanner and patch helper for CVE-2026-31431, detecting vulnerable Linux hosts via SSH, verifying kernel versions, and applying kernel…
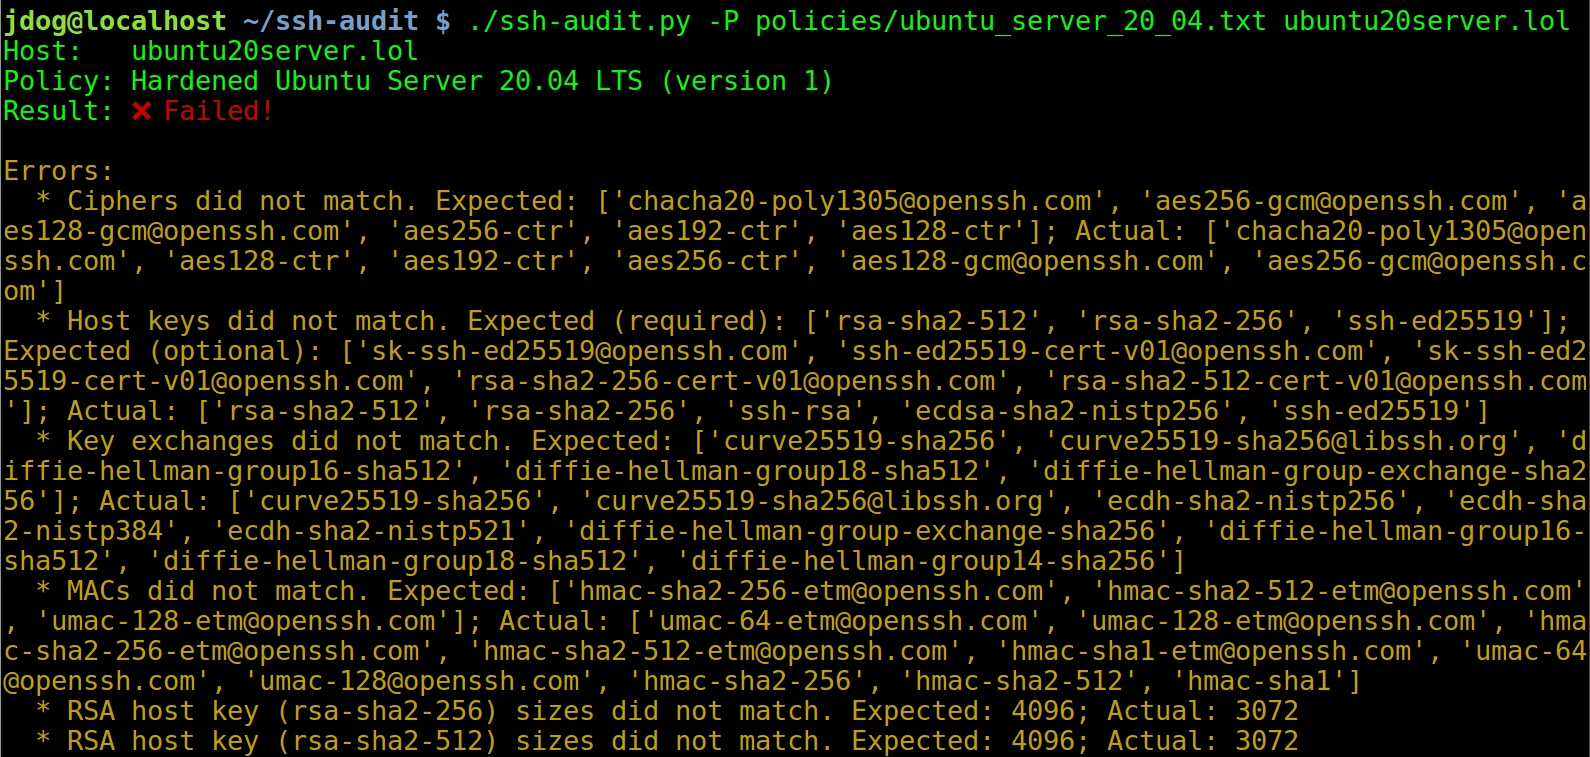 jtesta/ssh-audit
SSH server & client security auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc)
 liam-worsley/cve-2025-32433-poc-analysis
This is an analysis for CVE-2025-32433 (Erlang OTP SSH Vulnerability). I did not write any of the code, I only wrote comments describing what the…
 t3l3machus/pentest-pivoting
A compact guide to network pivoting for penetration testings / CTF challenges.
 shoucheng3/apache__mina-sshd_cve-2023-35887_2-9-2
Pure Java SSH client/server library implementing SSH-2 protocol with support for multiple ciphers, key exchanges, authentication methods, SFTP, SCP,…
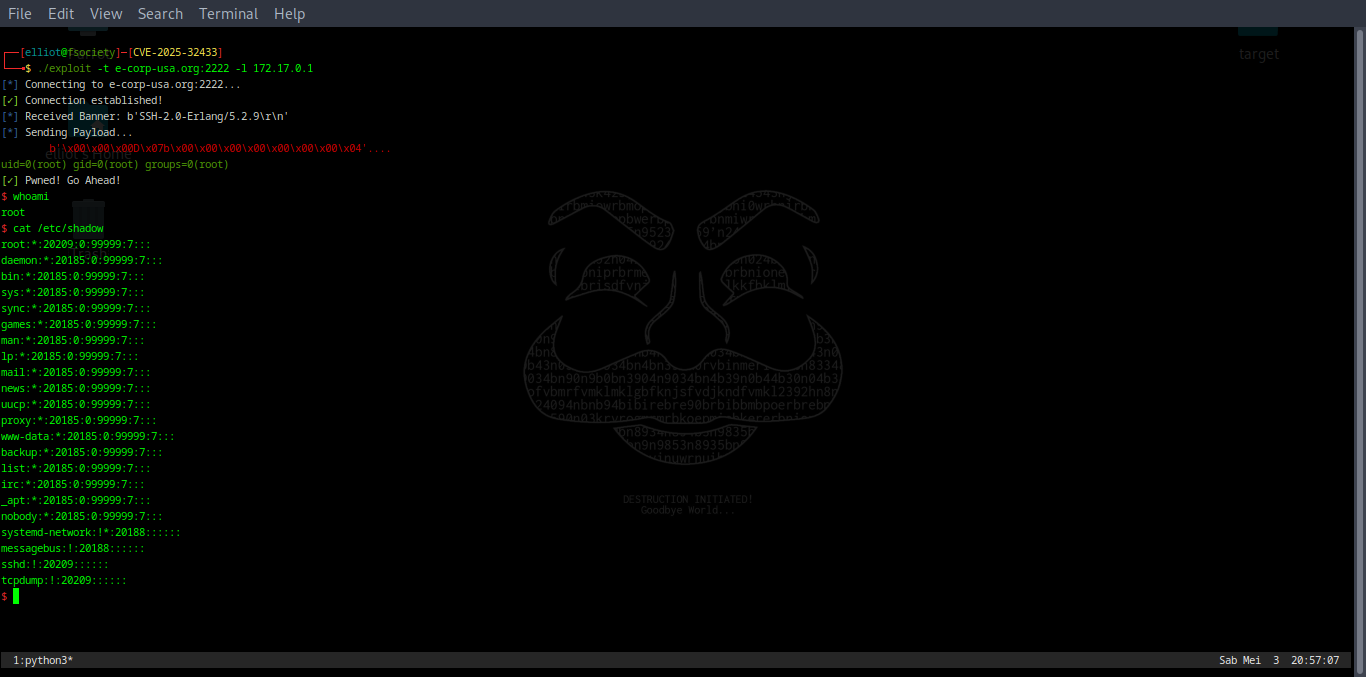 vigilante-1337/cve-2025-32433
A critical flaw has been discovered in Erlang/OTP's SSH server allows unauthenticated attackers to gain remote code execution. One malformed SSH…
 omer-efe-curkus/cve-2025-32433-erlang-otp-ssh-rce-poc
The vulnerability allows an attacker with network access to an Erlang/OTP SSH server to execute arbitrary code without prior authentication.
 rxerium/cve-2025-26466
The OpenSSH client and server are vulnerable to a pre-authentication DoS attack between versions 9.5p1 to 9.9p1 (inclusive) that causes memory and…
 rxerium/cve-2025-26465
MitM attack allowing a malicious interloper to impersonate a legitimate server when a client attempts to connect to it
 shamo0/cve-2024-6387_poc
Script for checking CVE-2024-6387 (regreSSHion)
 dheatattack/dheater
Proof-of-concept denial-of-service tool that enforces Diffie-Hellman ephemeral key exchange over TLS and SSH to saturate server CPU, implementing…
 jayanaxhf/filessh
A fast and convenient TUI file browser for remote servers