
shadowhammer
 withsecurelabs/shadowhammer
Batch-mode checker for Shadowhammer malware indicators, scanning local or provided MAC addresses against known malicious hashes, with offline support…
defensive-toolsincident-responsemalware-analysis+2
8
withsecurelabs/shadowhammerBatch-mode checker for Shadowhammer malware indicators, scanning local or provided MAC addresses against known malicious hashes, with offline support…
 cyberdudebivash/cyberdudebivash-5g-core-key-rotation-ghost-admin-auditor
Production-grade tool for detecting & remediating CVE-2026-0622 (Ghost Admin privilege escalation & master key exposure in 5G core software).
 dinotools/dionaea
Low-interaction honeypot that emulates vulnerable network services to capture malware, shellcode, and exploit attempts, with IPv6 and TLS support.
 yarrick/iodine
Tunnel IPv4 data through DNS servers to bypass firewall restrictions and provide covert network access for penetration testing.
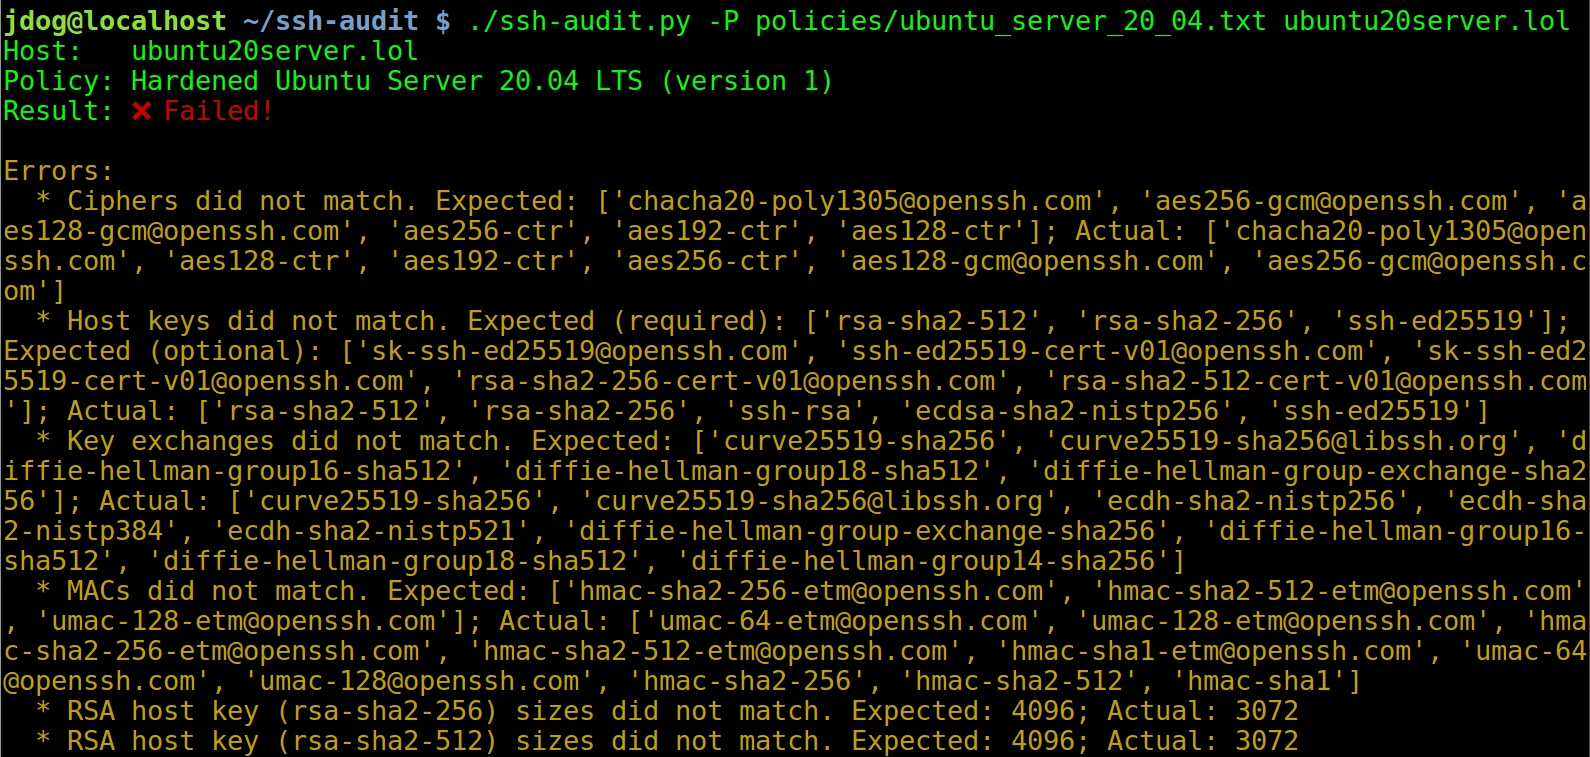 jtesta/ssh-audit
SSH server & client security auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc)
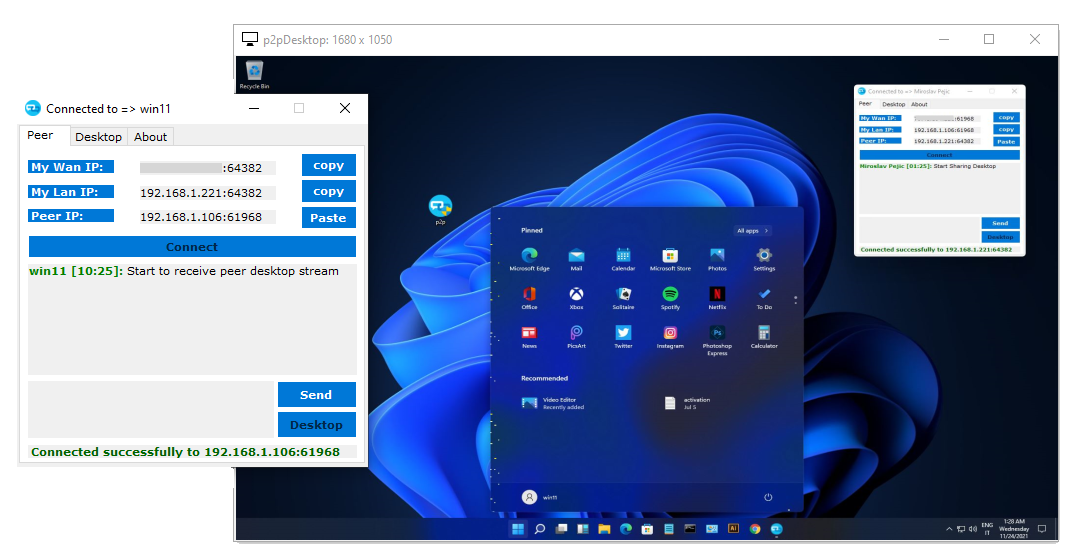 miroslavpejic85/p2p
🖥️ P2P Remote Desktop - Portable peer-to-peer remote desktop with no installation required.
 warp-tech/warpgate
Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit
 baram01/webui
WebUI for AAA
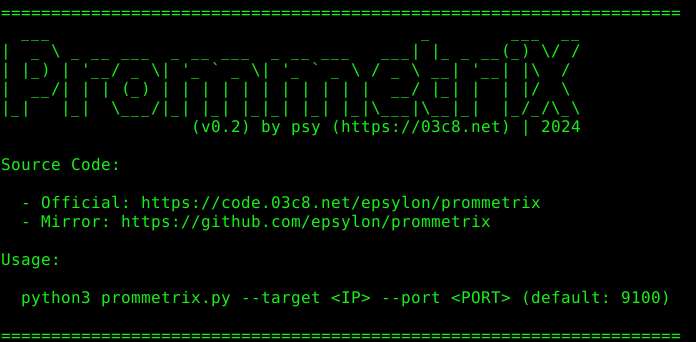 epsylon/prommetrix
Prommetrix can obtain relevant information from the instances of 'Node Exporter' executed by 'Prometheus'.
 bishopfox/bigip-scanner
Determine the running software version of a remote F5 BIG-IP management interface.
 corelight/detect-ransomware-filenames
Zeek script that monitors SMB traffic and alerts on known ransomware filenames using the Anti-Ransomware File System Resource Manager list.
 corelight/pingback
A Zeek package to detect the Pingback malware ICMP tunnel command and control (C2) network traffic.
 corelight/raspi-corelight
Corelight@Home script
 corelight/zeek-agenttesla-detector
A Zeek based Agent Tesla malware C2 detector.
 corelight/zeek-asyncrat-detector
A Zeek based AsyncRAT malware detector.
 corelight/zeek-elf
A Zeek ELF File Analyzer
 corelight/zeek-gozi-detector
A Zeek based Gozi banking malware detector.