

gopacket
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
command-and-controlexploit-frameworkslateral-movement+7
724
mandiant/gopacketA complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
 cognis-digital/c2detect
C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 mgeeky/redwarden
Cobalt Strike C2 Reverse proxy that fends off Blue Teams, AVs, EDRs, scanners through packet inspection and malleable profile correlation
 byt3bl33d3r/mitmf
Framework for Man-In-The-Middle attacks
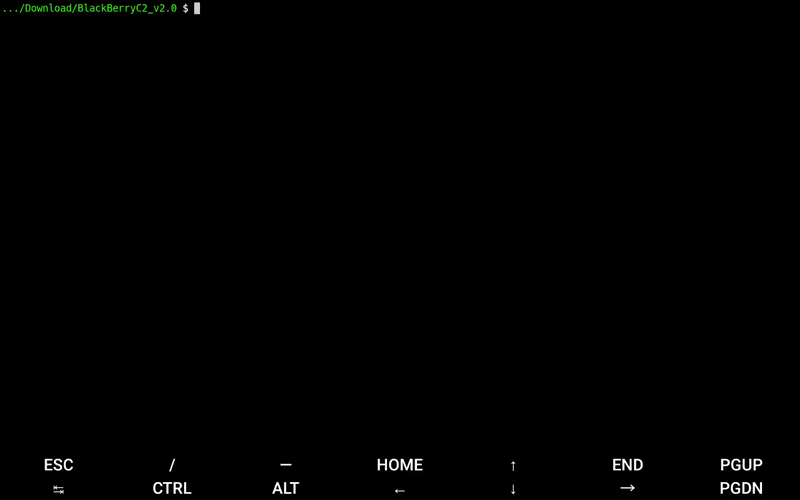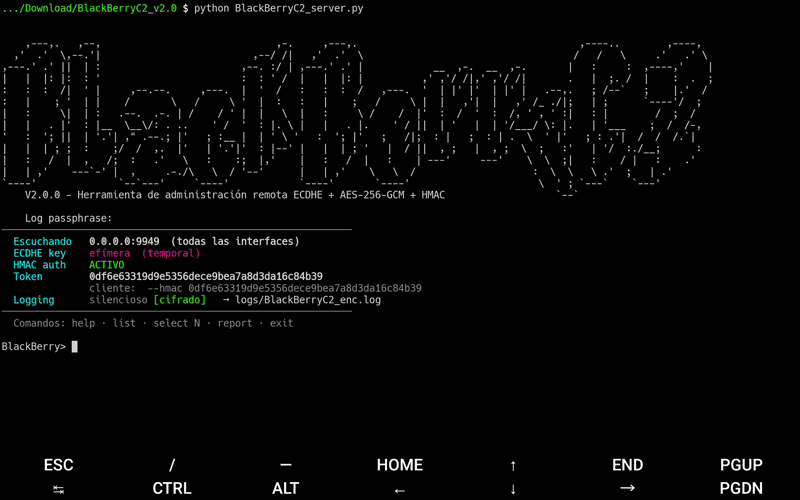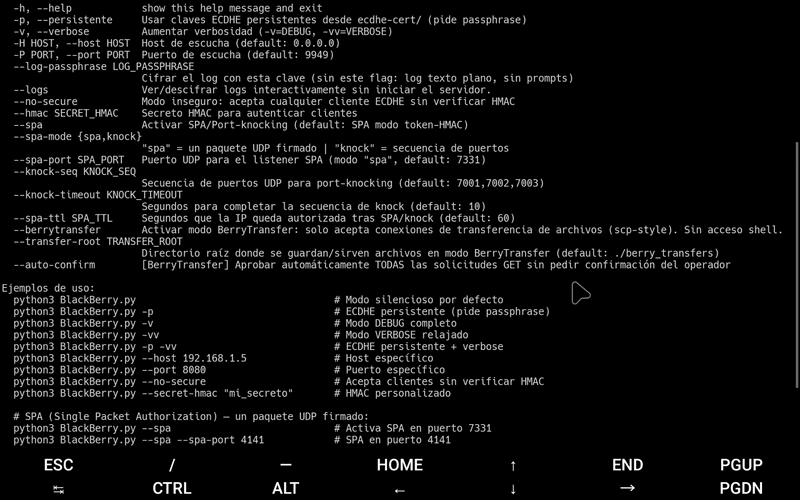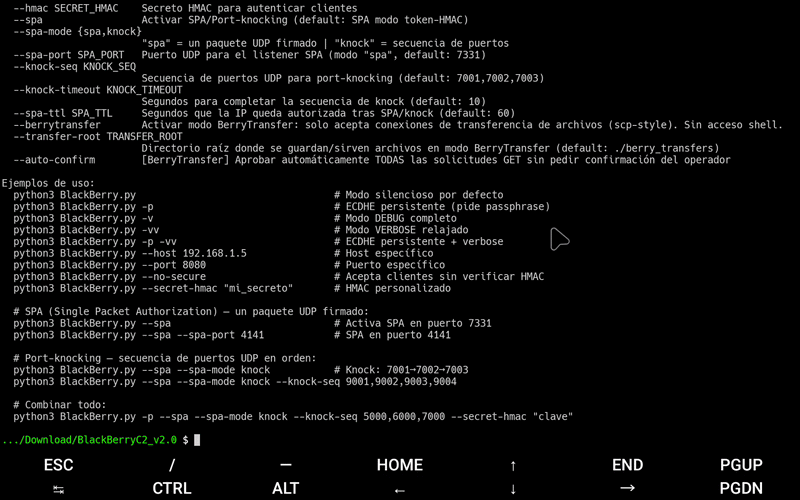 dereeqw/blackberryc2
Encrypted command‑and‑control (C2) research framework for cybersecurity education, red team labs, and secure client‑server communication experiments.
 cisc0-gif/kitt-lite
Python-Based Pentesting CLI Tool
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
 reverseclabs/c3
Custom Command and Control (C3). A framework for rapid prototyping of custom C2 channels, while still providing integration with existing offensive…
 codextf2/openmalleablec2
Open Source Implementation of Cobalt Strike's Malleable C2
 bluscreenofjeff/malleablec2profiles
Malleable C2 profiles for Cobalt Strike
 degenerat3/meteor
A cross-platform C2/teamserver supporting multiple transport protocols, written in Go.
 corelight/c2-detection-manjusaka
Detection of Manjusaka C2 framework
 averagesecurityguy/c2
A simple, extensible C&C beaconing system.