CVE-2023-4596-OpenSSH-Multi-Checker

CVE-2024-6387-checker is a tool or script designed to detect the security vulnerability known as CVE-2024-6387 OpenSSH. CVE-2024-6387 OpenSSH is an…

CVE-2024-6387-checker is a tool or script designed to detect the security vulnerability known as CVE-2024-6387 OpenSSH. CVE-2024-6387 OpenSSH is an…

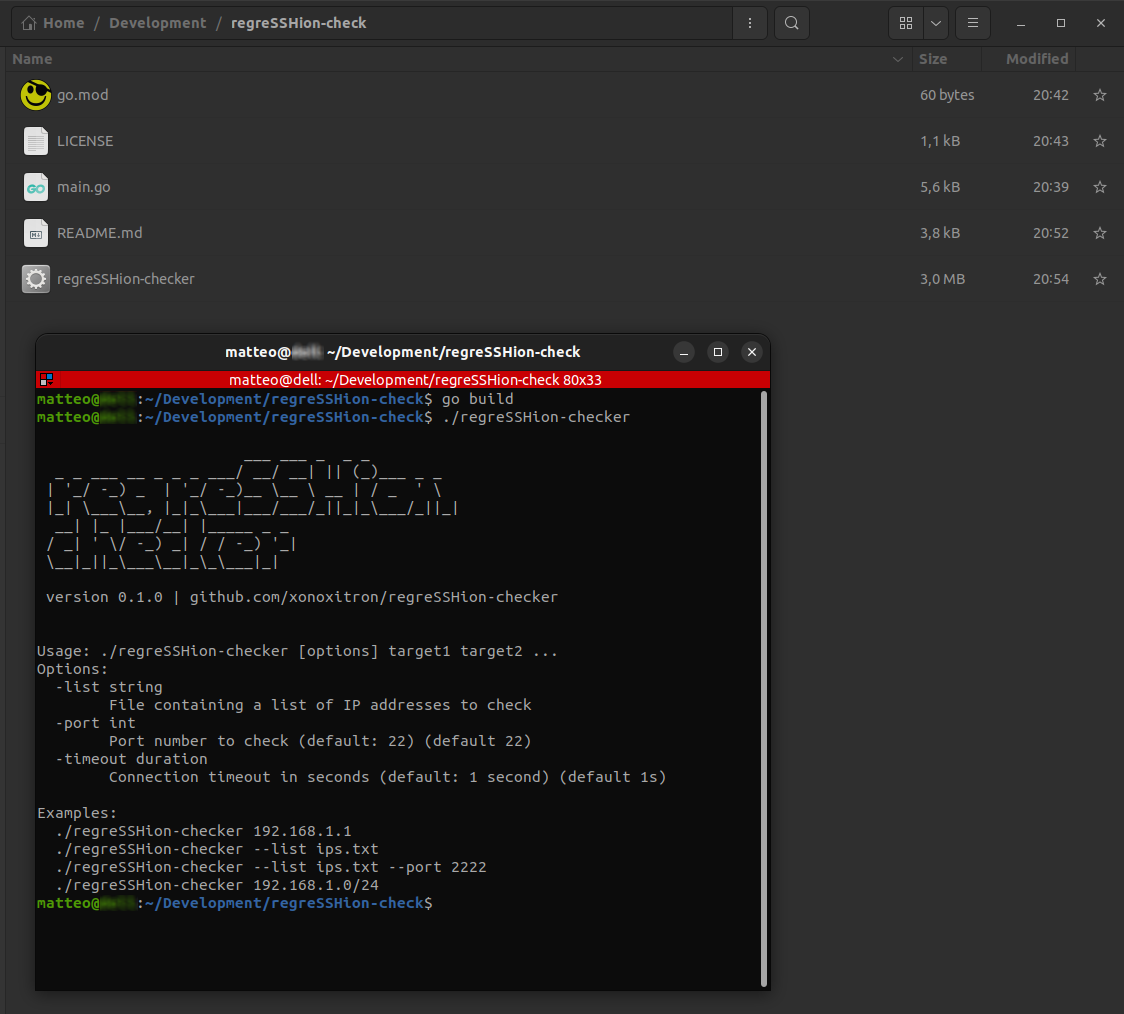
Fast, efficient, and reliable detection for the regreSSHion exploit. Scan multiple targets in seconds with zero dependencies.

Security analysis and report of CVE-2024-6387 OpenSSH vulnerability, including vulnerability details, CVSS evaluation, and mitigation recommendations.

regreSSHion is a security tool designed to test for vulnerabilities related to CVE-2024-6387, specifically focusing on SSH and remote access…

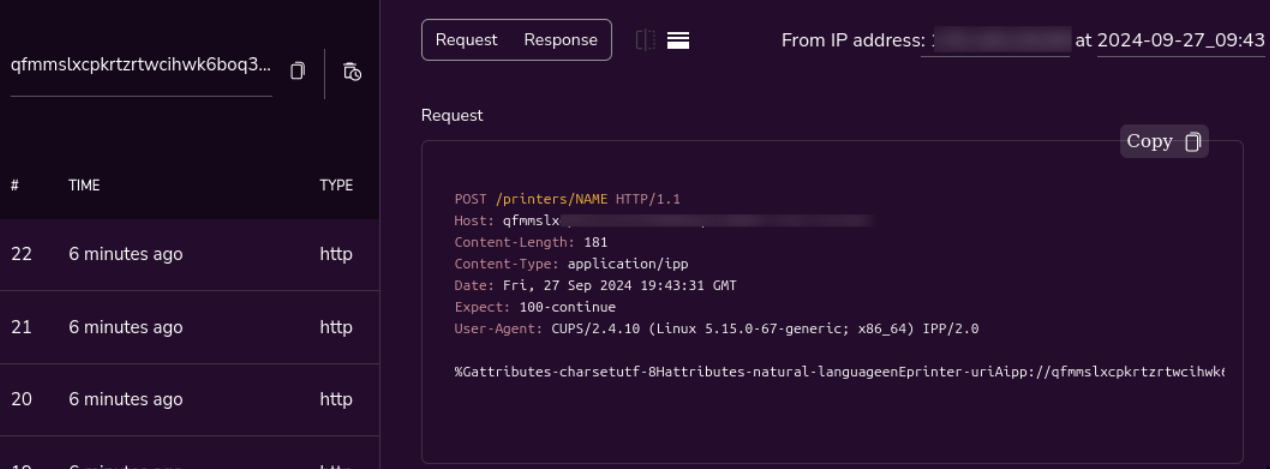
Scanner for the CUPS vulnerability CVE-2024-47176

Python script to detect CVE-2024-23113, a format string vulnerability in FortiGate FGFM service on TCP/541, using SSL connection and crafted payload…

Mitigation Guide for CVE-2024-6387 in OpenSSH

Found 200+ vulnerabilities on scanme.nmap.org including CVE-2023-38408 (9.8 critical)

Lightweight Python scanner that identifies servers vulnerable to OpenSSH regreSSHion (CVE-2024-6387) via rapid banner retrieval across IPs, domains,…

An ssh honeypot with the XZ backdoor. CVE-2024-3094

Quickly identifies servers vulnerable to OpenSSH 'regreSSHion' (CVE-2024-6387).

Laboratorio criado para PenTest da Vuln CVE 2024-214113(MONIKER LINK).

CVE-2024-6387, also known as RegreSSHion, is a high-severity vulnerability found in OpenSSH servers (sshd) running on glibc-based Linux systems. It…

Python-based exploit for CVE-2024-54772 enabling username enumeration on MikroTik RouterOS versions v6.43 through v7.17.2 using wordlist or…

PowerShell audit script to detect missing patches for CVE-2024-38063, an IPv6 vulnerability in Windows systems, enabling rapid remediation…

CVE-2024-6387 OpenSSH 信号竞争漏洞(regreSSHion)分析报告及检测脚本

Check to see if your Palo Alto firewall has been compromised by running script againt support bundle.

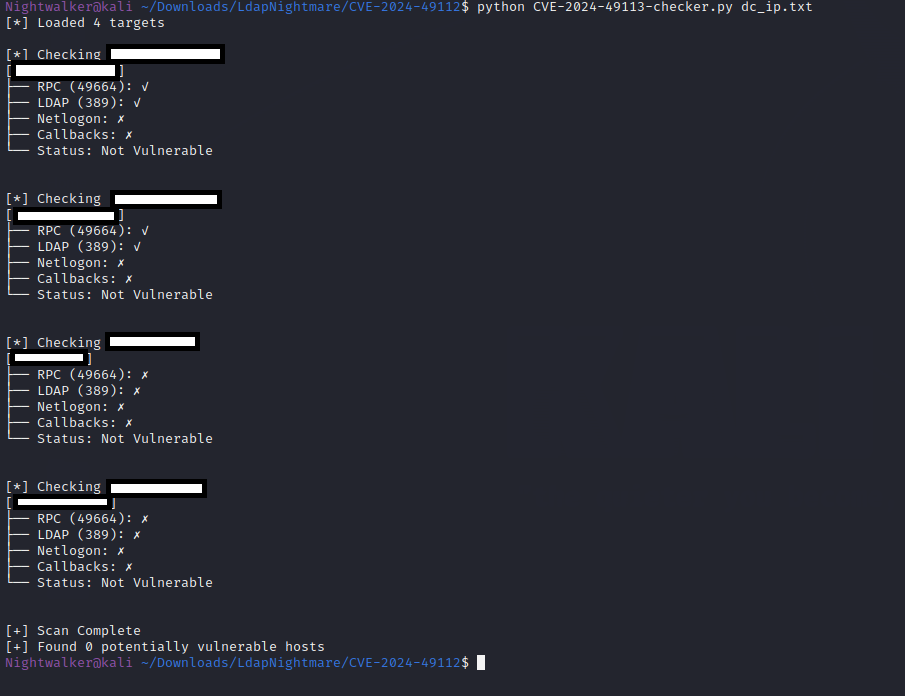
Checks if a system is potentially vulnerable to CVE-2024-49113 (LDAP Nightmare) by testing RPC connectivity, LDAP ports, Netlogon service, and LDAP…