
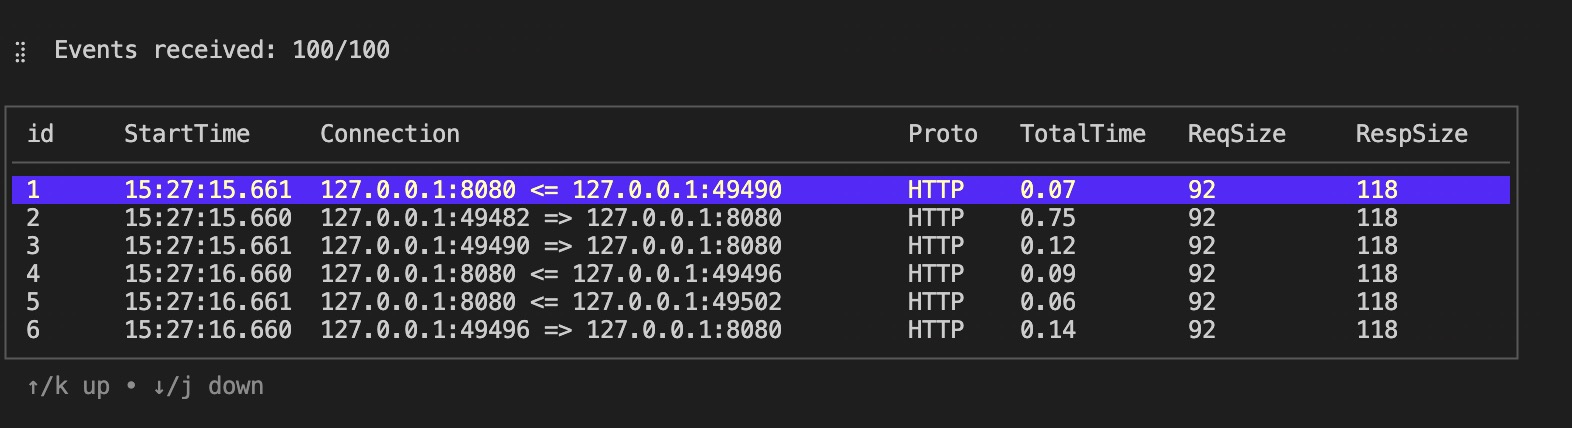
kyanos
 hengyoush/kyanos
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…
dns-analysisdynamic-analysis-sandboxinglog-analysis+3
5.1k
hengyoush/kyanosKyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
 calebmadrigal/trackerjacker
Like nmap for mapping wifi networks you're not connected to, plus device tracking
 robertdavidgraham/masscan
TCP port scanner, spews SYN packets asynchronously, scanning entire Internet in under 5 minutes.
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 jpr5/ngrep
ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…
 danmcinerney/wifi-monitor
Prints the IPs on your local network that're sending the most packets
 zapotek/cdpsnarf
CDPSnarf is a network sniffer exclusively written to extract information from CDP (Cisco Discovery Protocol) packets.
 securityanalysts/cve-2021-37152
Exploit Accsess network clients by sending packets in wirless TP-LINK and preparing for a mitm attack
 ntop/pf_ring
High-speed packet processing framework
 pfq/pfq
Functional Network Framework for Multi-Core Architectures
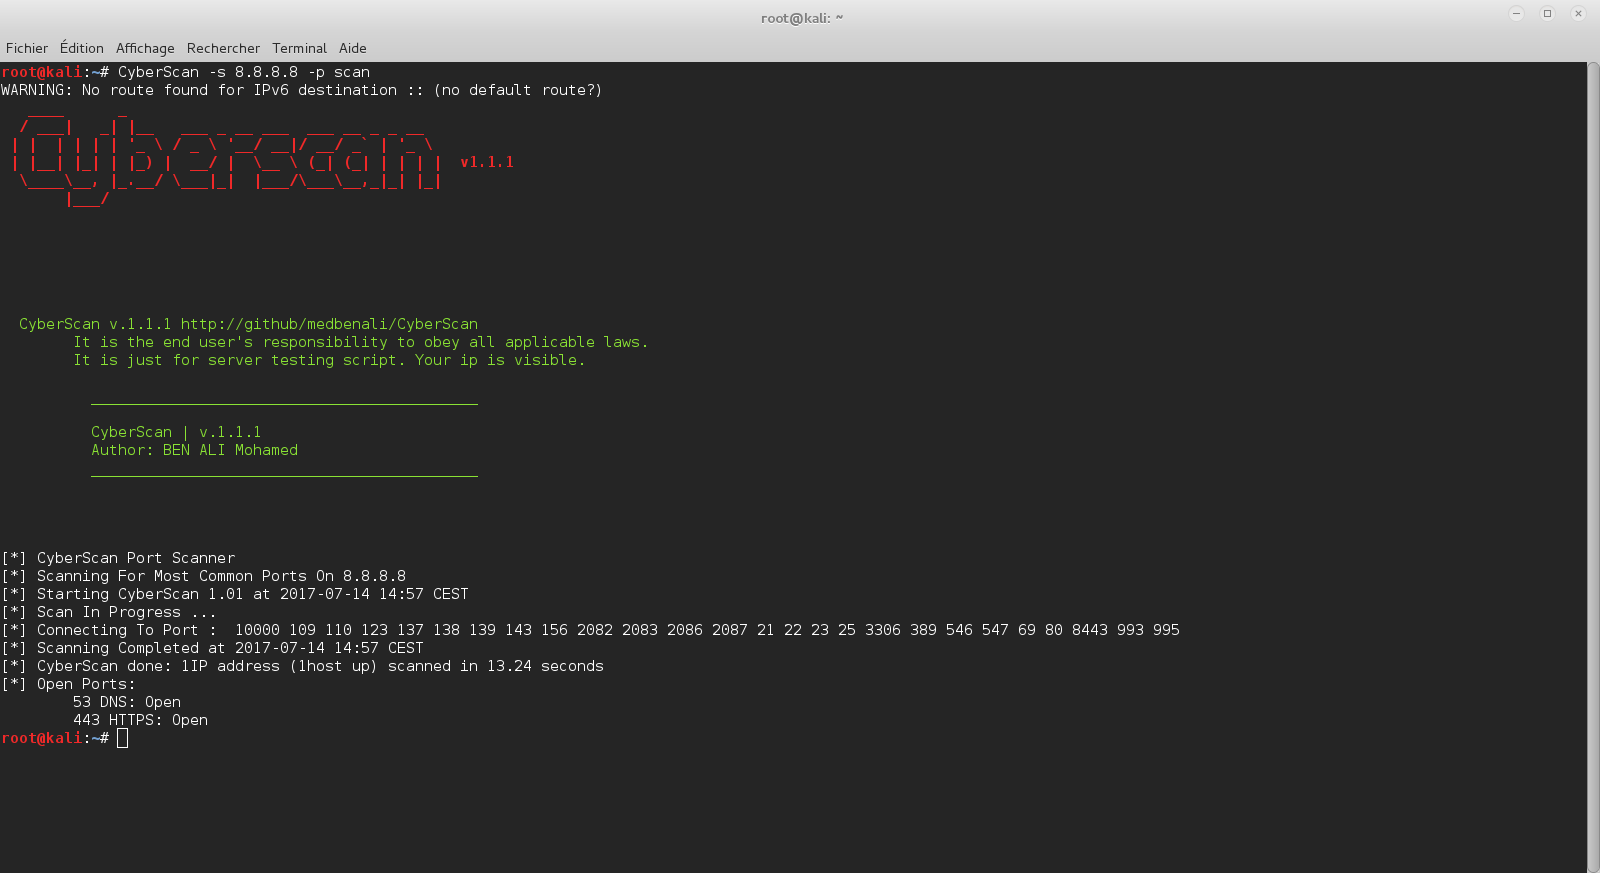 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
 evilsocket/spycast
A crossplatform mDNS enumeration tool.
 90n45-d3v/dbmonster
A Multitool For Tracking And Locating Nearby Devices Via Their RF Activities.
 takeshixx/ip-https-tools
Tools for the IP over HTTPS (IP-HTTPS) Tunneling Protocol